

CVE-2019-5010
 jonathanwilbur/cve-2019-5010
CVE-2019-5010 Exploit PoC - Python Denial of Service via Malformed X.509v3 Extension
cryptographyexploitationpenetration-testing+1
jonathanwilbur/cve-2019-5010CVE-2019-5010 Exploit PoC - Python Denial of Service via Malformed X.509v3 Extension
 morpheuslord/winfihack
A windows Wifi Brute forcing utility which is an extremely old method but still works without the requirement of external dependencies.
 t43wiu6/cve-2019-0887
exp for CVE-2019-0887
 dougburks/so-crates
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!
 ngothienan/cve-2023-38831
Python-based exploit generator for CVE-2023-38831 (WinRAR remote code execution). Creates malicious RAR archives with bait files and payload scripts…
 fa1c0n35/cve-2023-38831-winrar-exploit
Python-based exploit generator for CVE-2023-38831 WinRAR vulnerability. Creates malicious RAR archives with bait files (PDF, images) and payload…
 b1tg/cve-2023-38831-winrar-exploit
CVE-2023-38831 winrar exploit generator
 crowsec-edtech/cve-2022-22947
Spring Cloud Gateway < 3.0.7 & < 3.1.1 Code Injection (RCE)
 haitam-lazaar/libextractor-privesc
Proof-of-concept for CVE-2026-100310, a local privilege escalation in GNU libextractor ≤1.15 via the LIBEXTRACTOR_PREFIX untrusted search path, with…
 wifiphisher/wifiphisher
Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…
 kienhosd/wp-file-manager-exploit-cve-2020-25213-with-zerologon
Exploit Windows server 2019 vulnerable to Zerologon with Garble, Chisel, wp-file-manager vulnerability (have video demo)
 fancysauce/pwnkit-cve-2021-4034
 c3rrberu5/zerologon-to-shell
Automated exploit script combining CVE-2020-1472 (ZeroLogon) with evil-winrm to gain a remote shell on vulnerable Windows Domain Controllers.
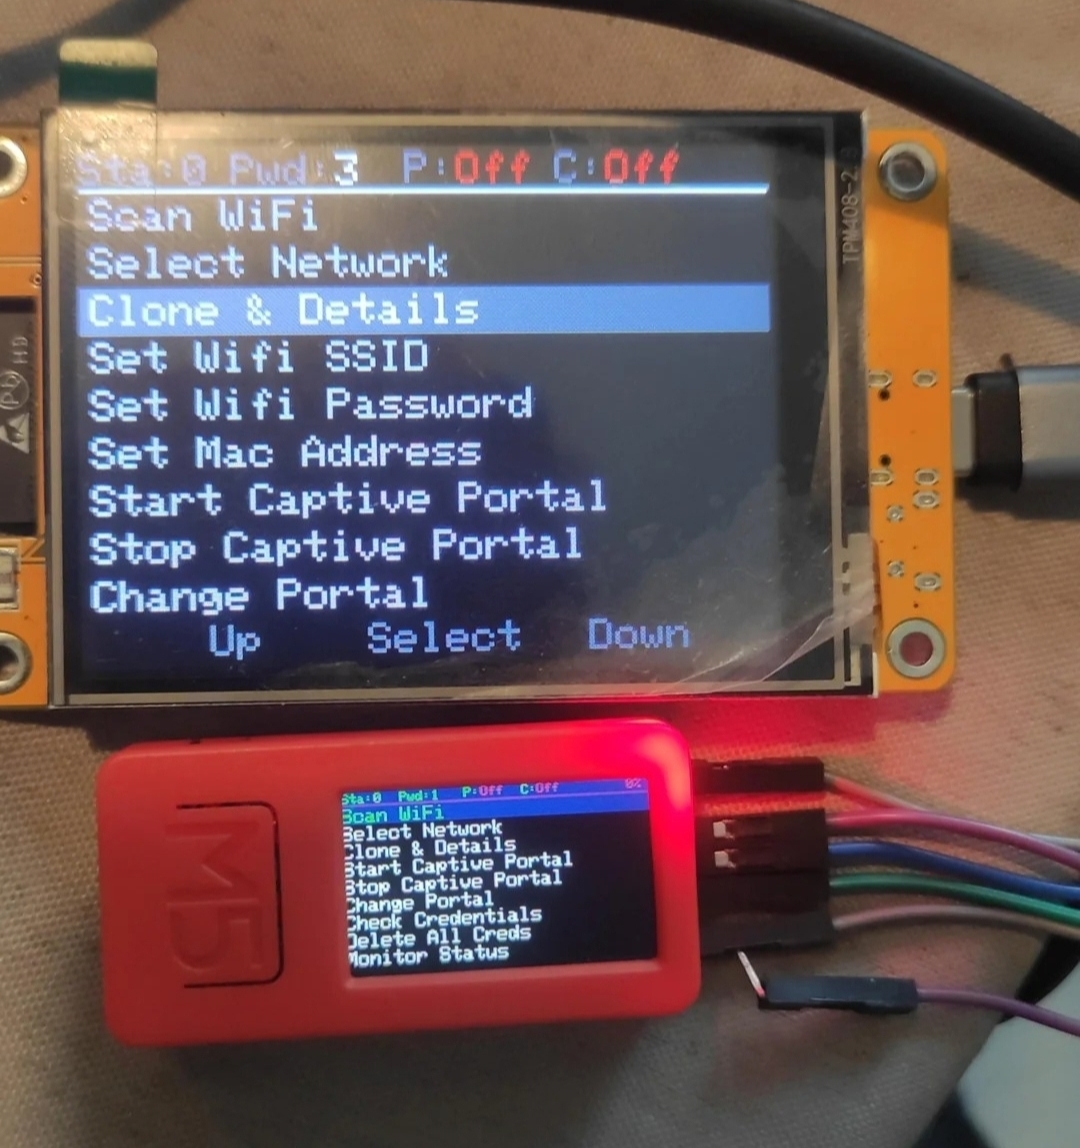 7h30th3r0n3/evil-m5project
Multi-purpose WiFi penetration testing toolkit for M5Stack devices. Performs network scanning, evil-twin attacks, deauthentication, captive portal…
 elevenpaths/evilfoca
Tool to analyze and test security in IPv4 and IPv6 data networks
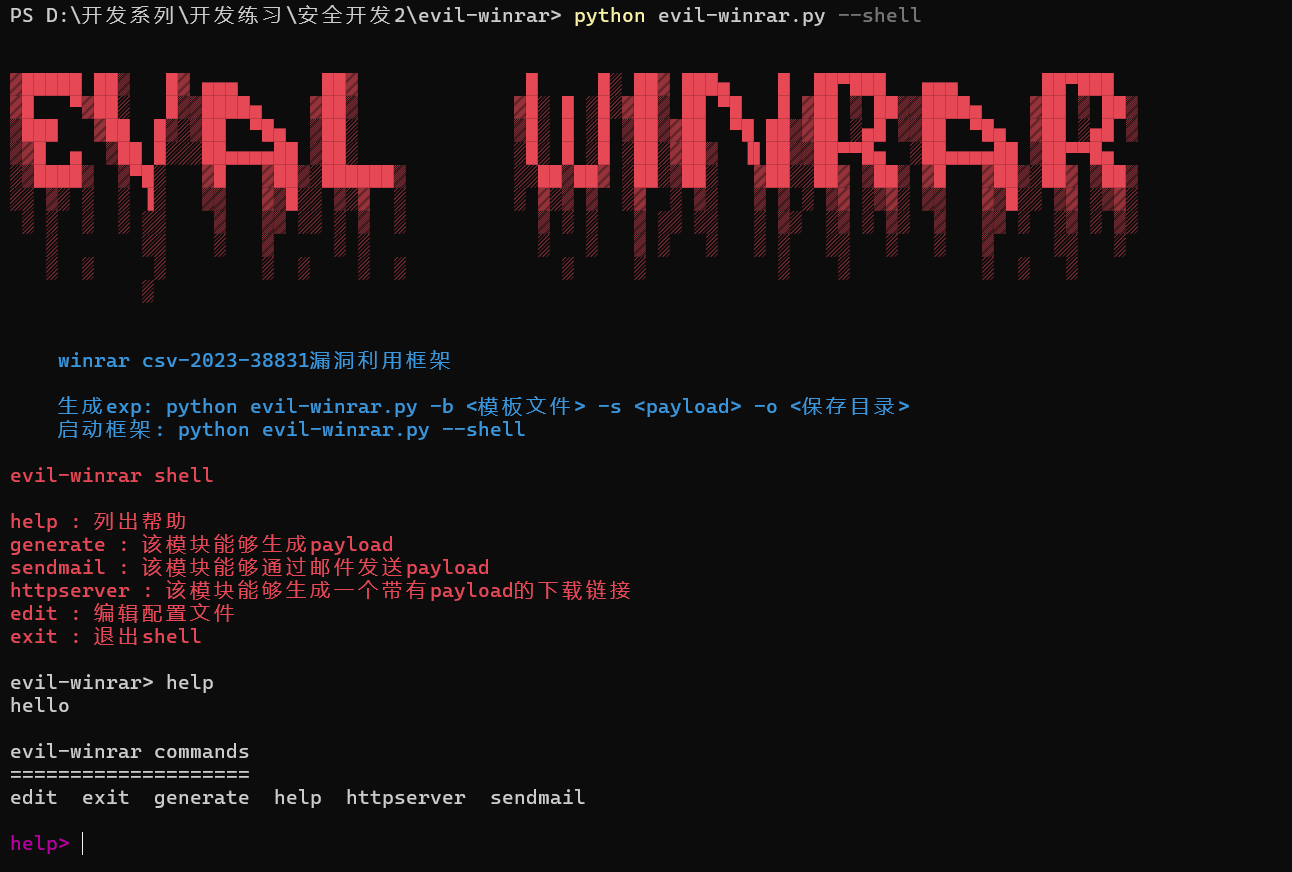 youmulijiang/evil-winrar
evil-winrar,CVE-2023-38831漏洞利用和社会工程学攻击框架 (evil-winrar, CVE-2023-38831 Vulnerability Exploitation and Social Engineering Attack Framework)
 flamingspork/iptable_evil
Kernel-level iptables backdoor that accepts all packets with the RFC 3514 evil bit set, bypassing firewall rules. Includes in-tree and out-of-tree…
 tw-d/wifi-pineapple-mk7_evil-portal
Rogue access point toolkit for WiFi penetration testing, deploying evil portal phishing payloads to capture credentials and perform social…