hopline
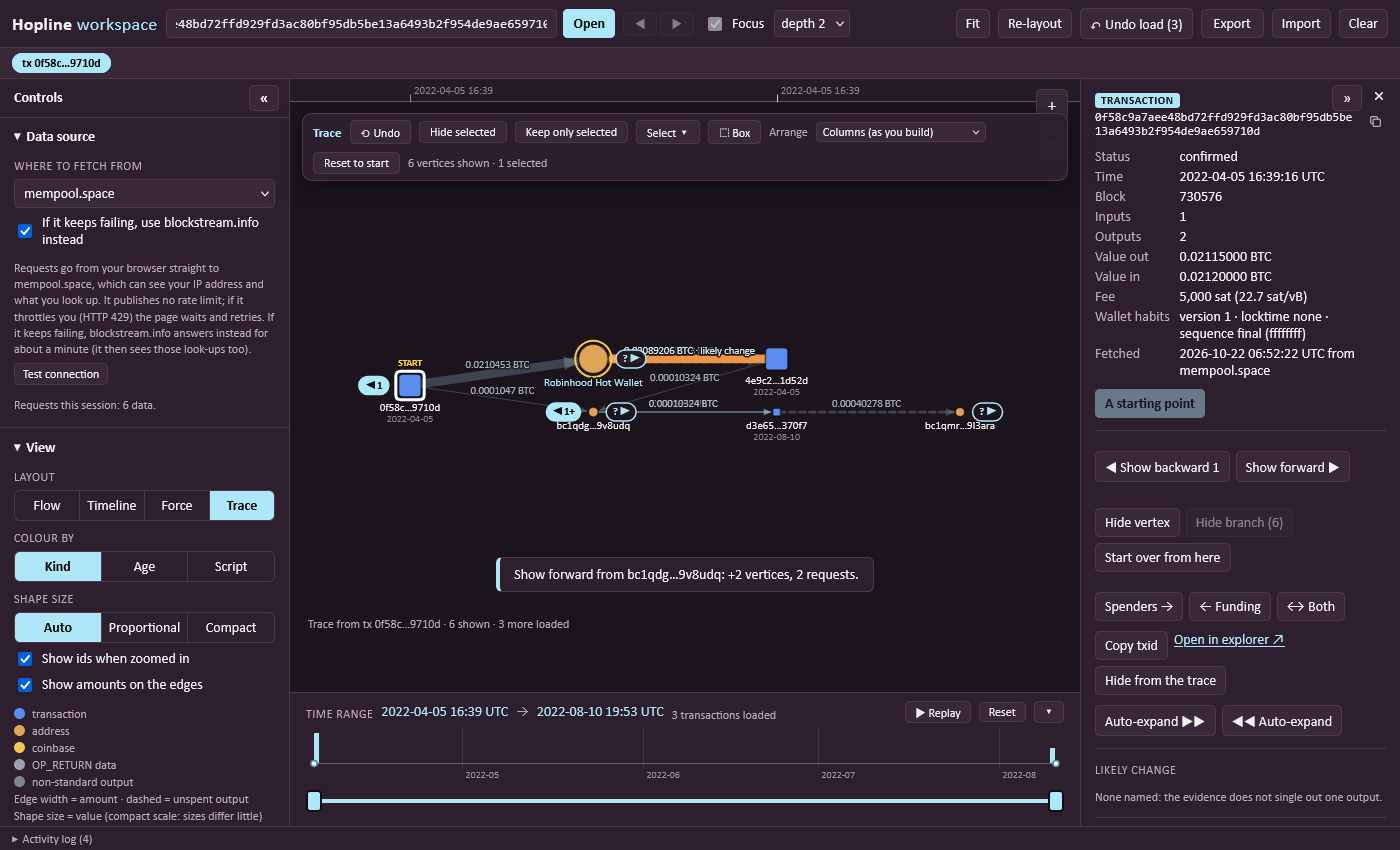
Bitcoin investigation tools in your browser: follow the money, label wallets, flag patterns with reasons and write a verifiable report. Nothing to…

Bitcoin investigation tools in your browser: follow the money, label wallets, flag patterns with reasons and write a verifiable report. Nothing to…

Reverse Engineer any USB gadget: capture vendor-app traffic, infer the protocol with evidence, generate an open Python/libusb driver. CLI + MCP…

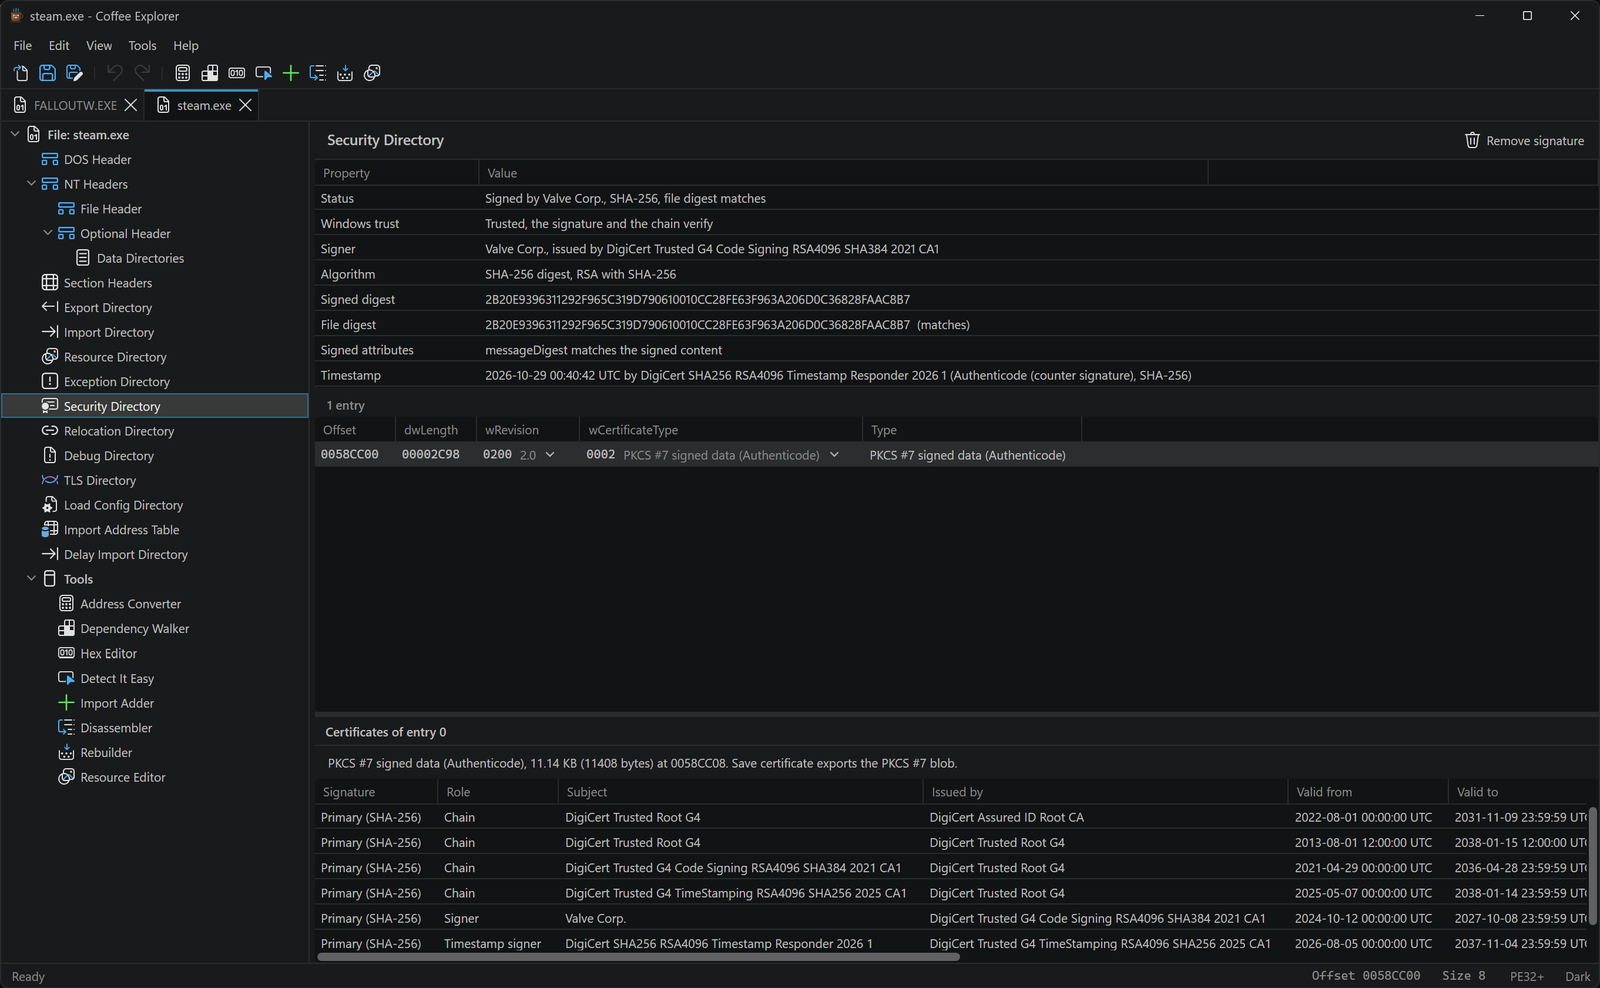
The familiar PE editor, redesigned with a Visual Studio aesthetic, high DPI support and more.

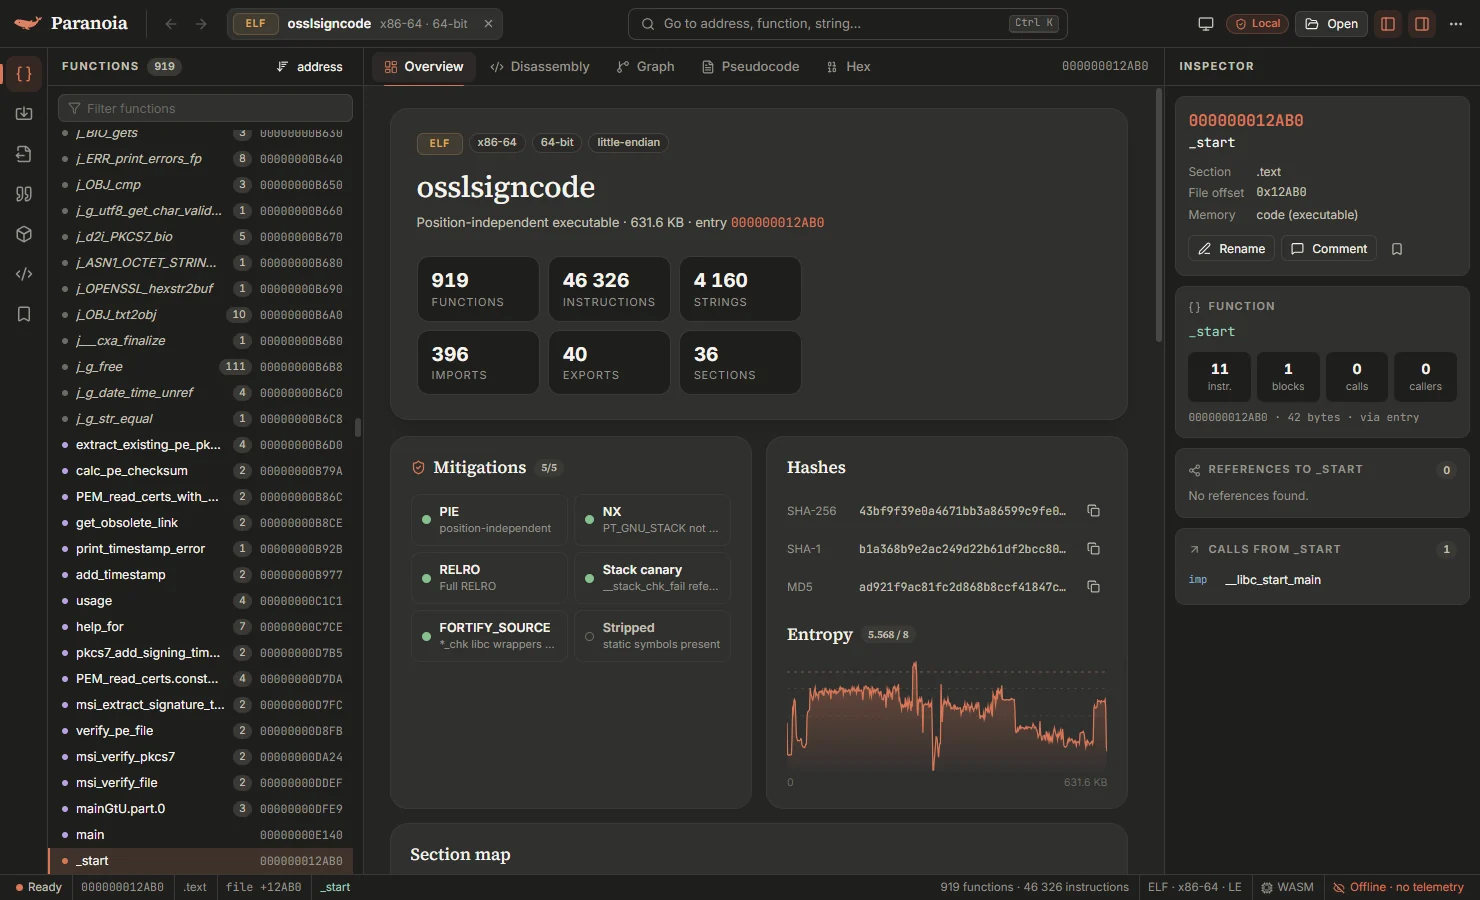
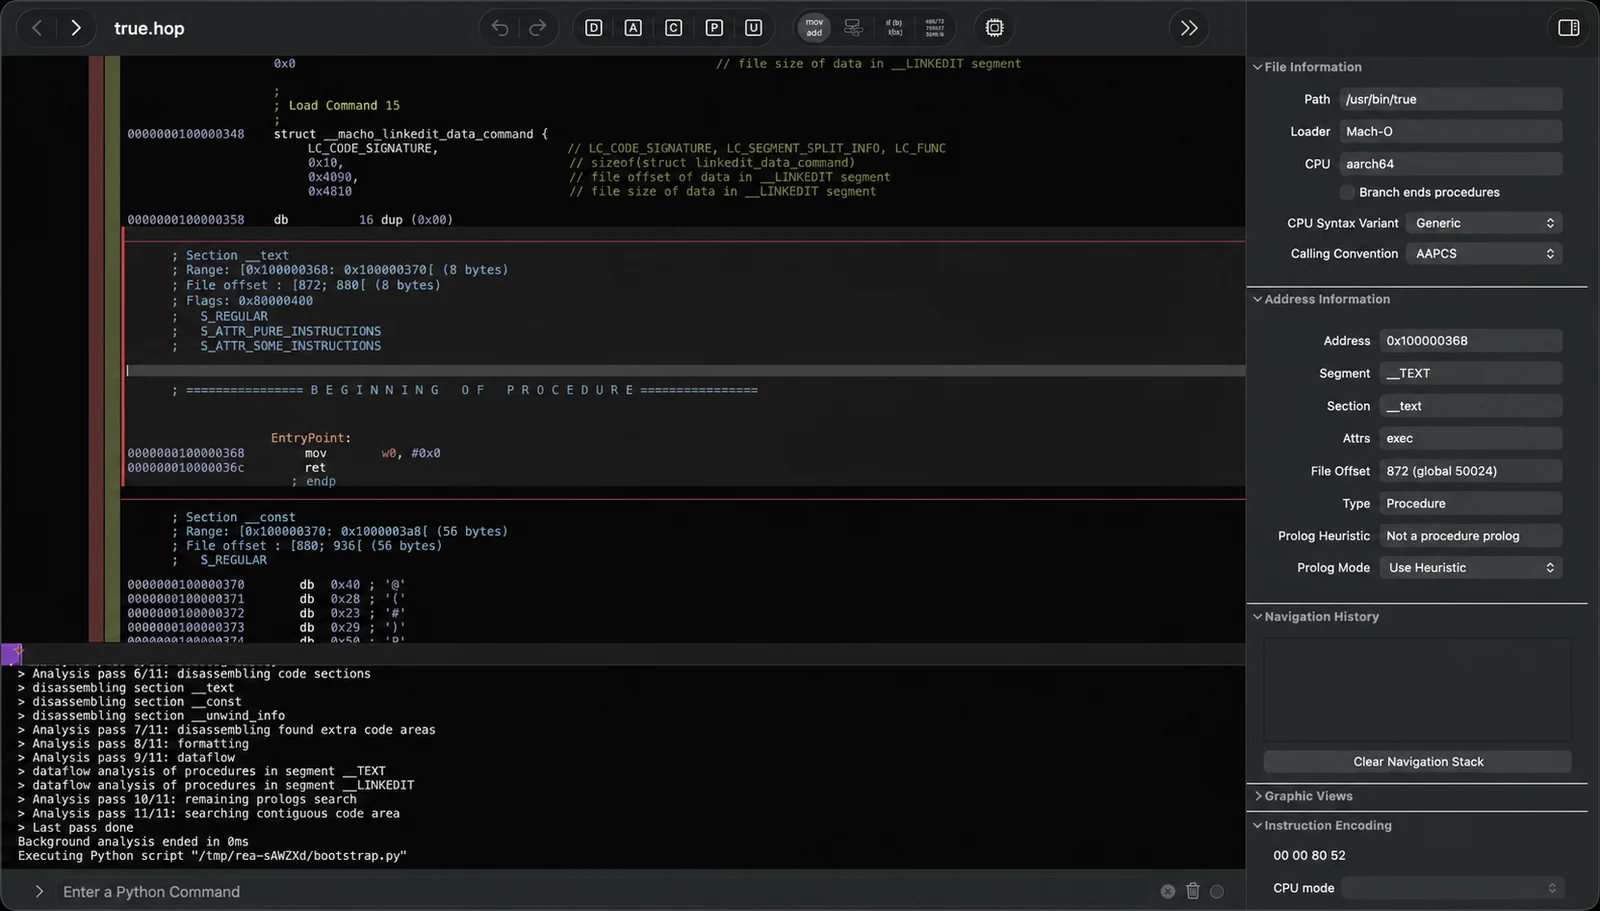
Open reverse engineering — PE/ELF/Mach-O, x86/x64/AArch64, graphs, pseudocode. Rust engine, no network. Desktop · CLI · browser.

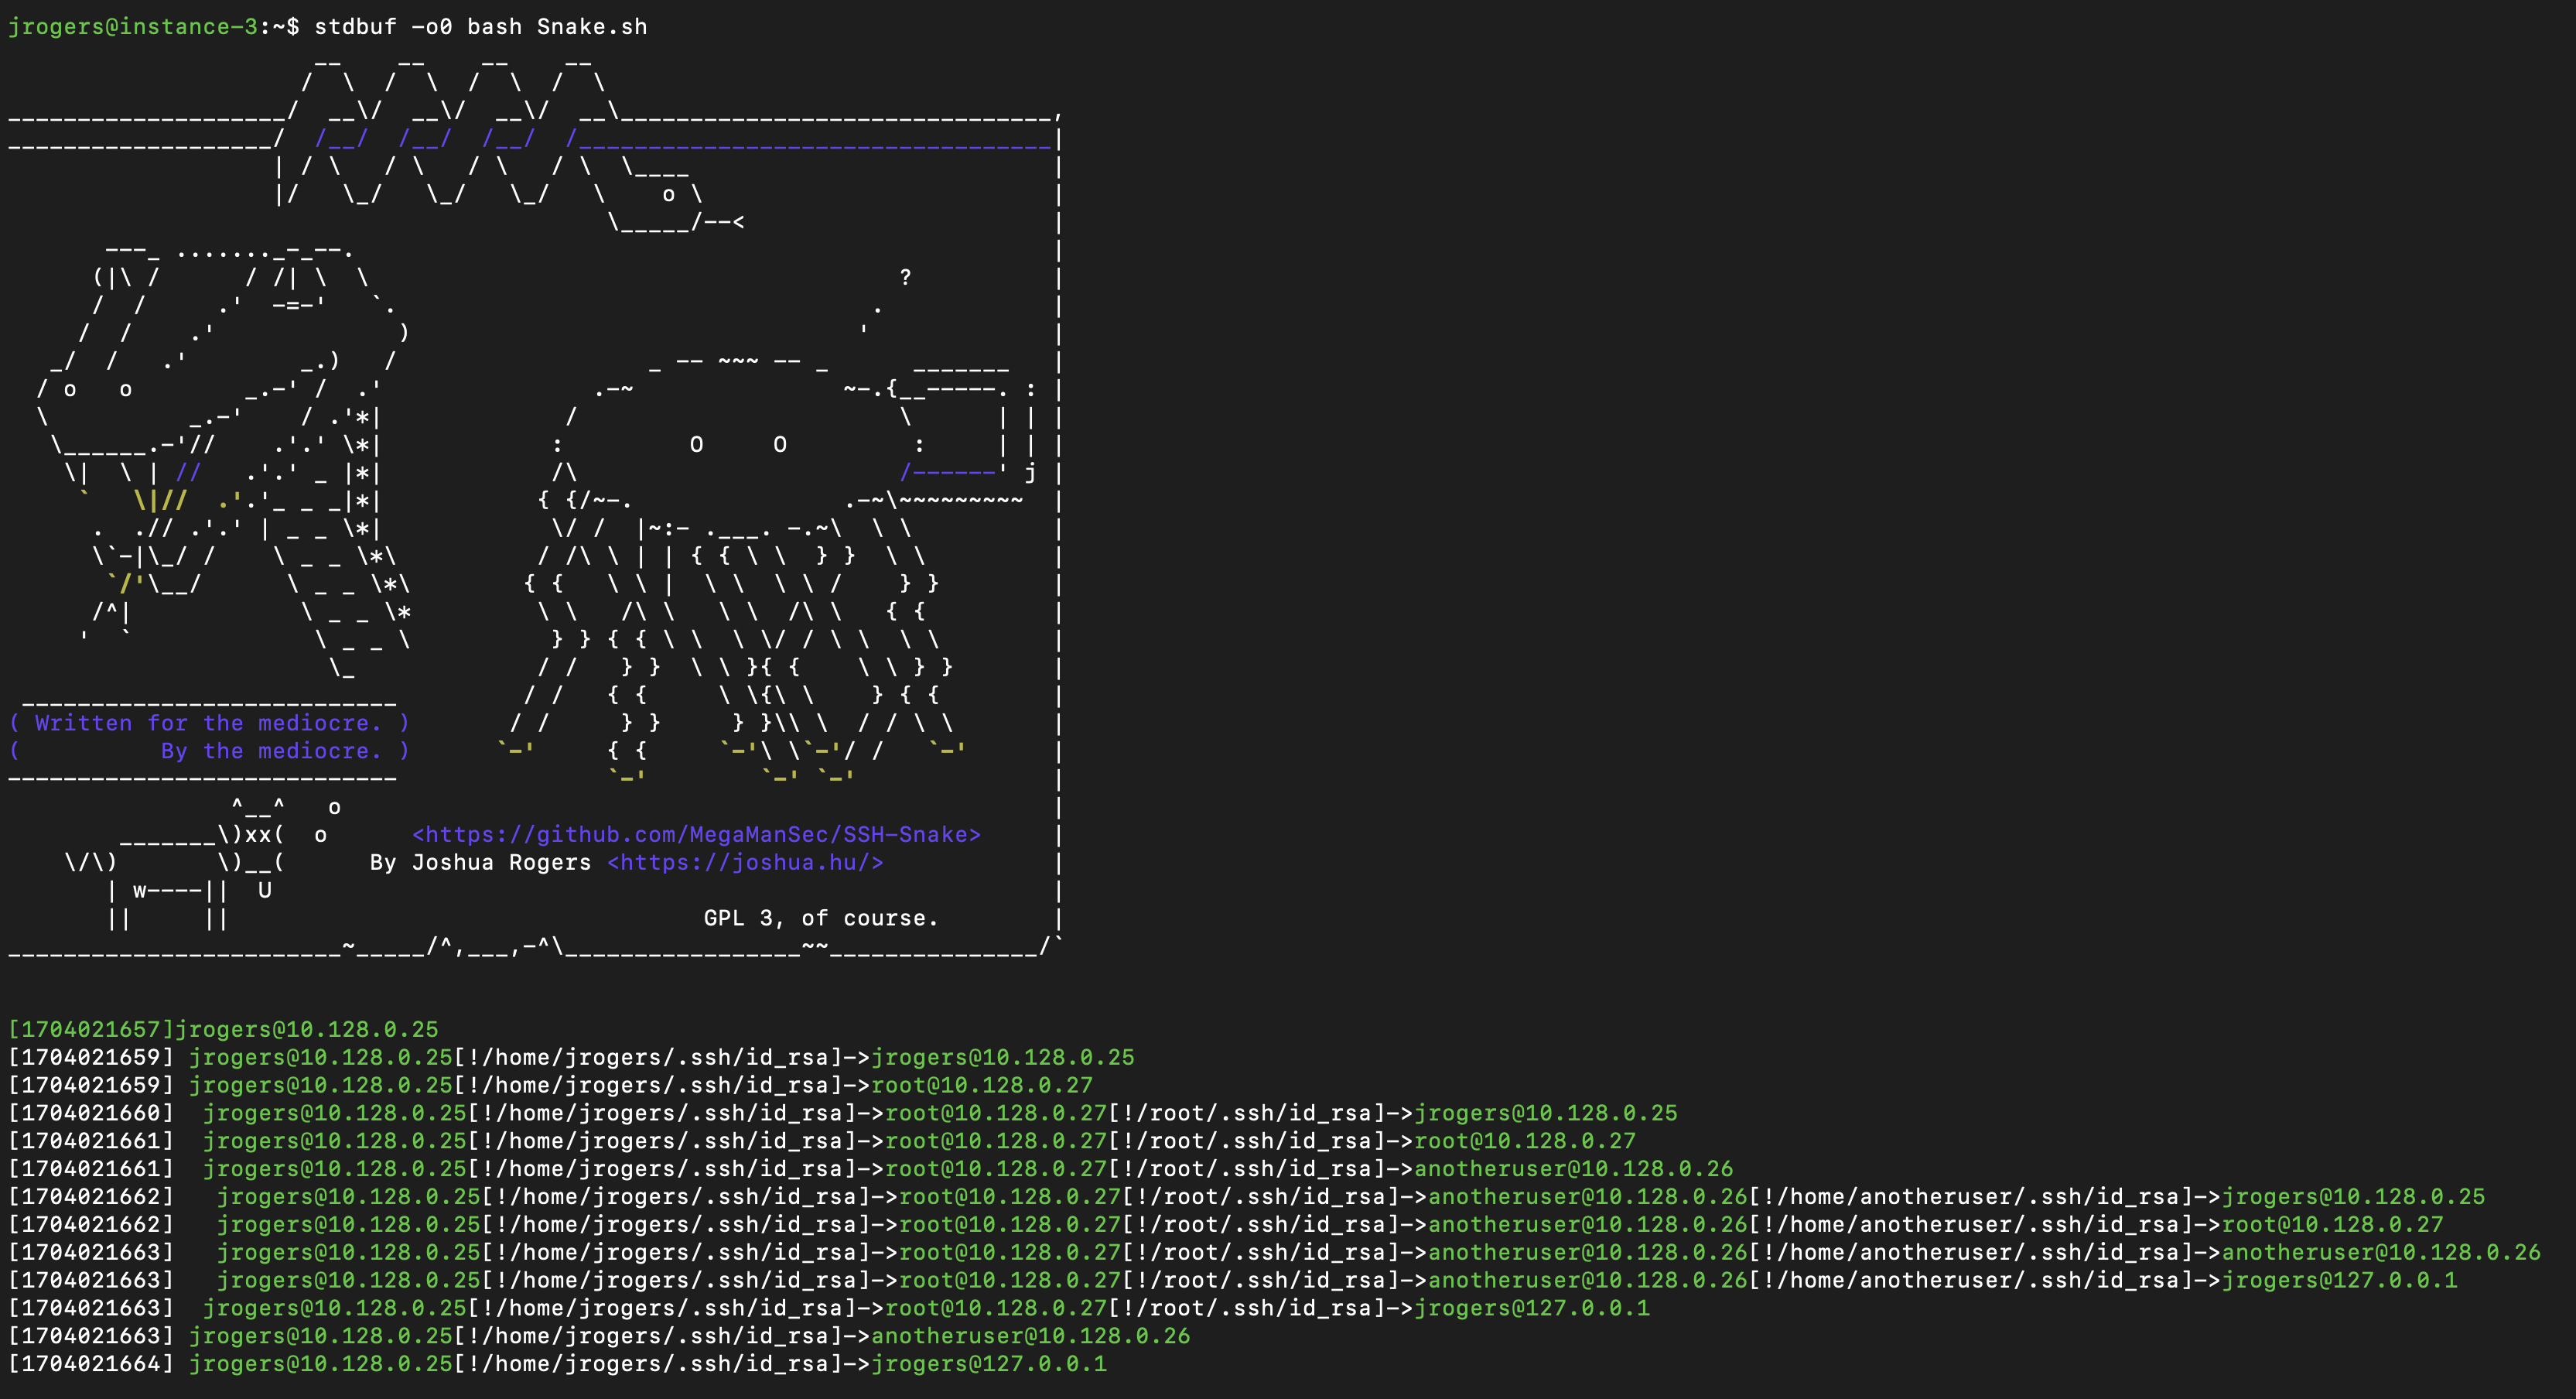
Fileless, self-propagating Bash script that recursively discovers SSH private keys and reachable hosts, then traverses the network via SSH to map…

Multi-agent LLM system that autonomously assesses web application security, orchestrating tool-grounded execution and validating exploits end to end.

Helping Ethical Hackers use LLMs in 50 Lines of Code or less..

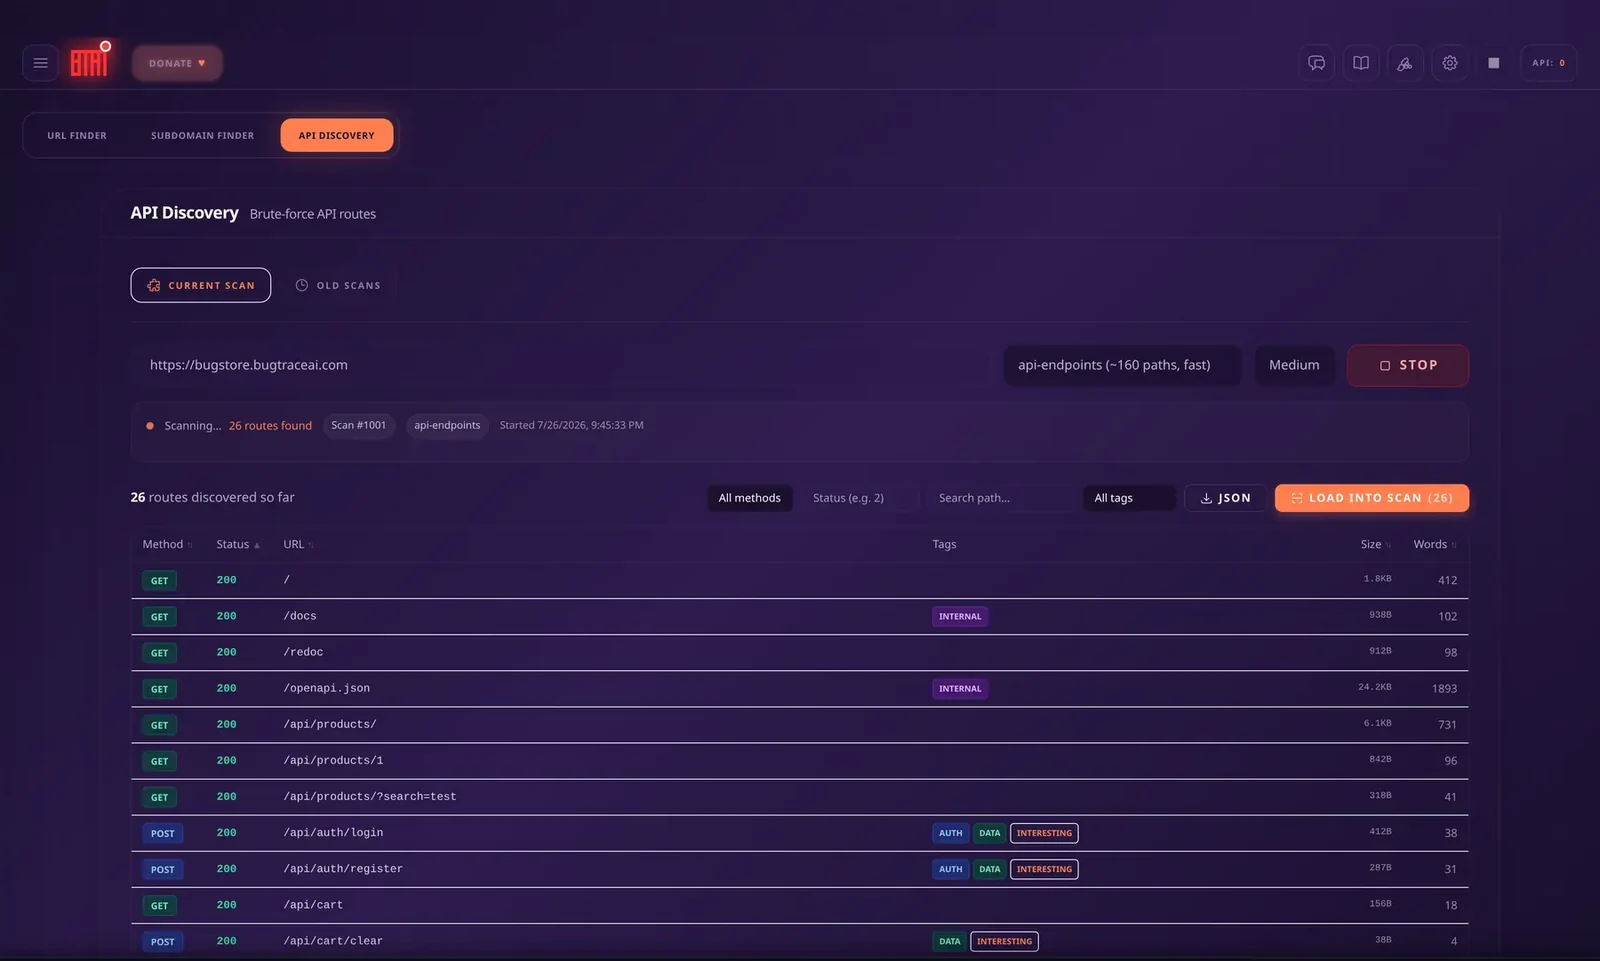
Open-source, self-hosted web pentesting suite with agentic scanning, analyst tools, API testing, model checkpoints and MCP integrations.

This repository contains a tool that can be used for automated pentesting tasks.

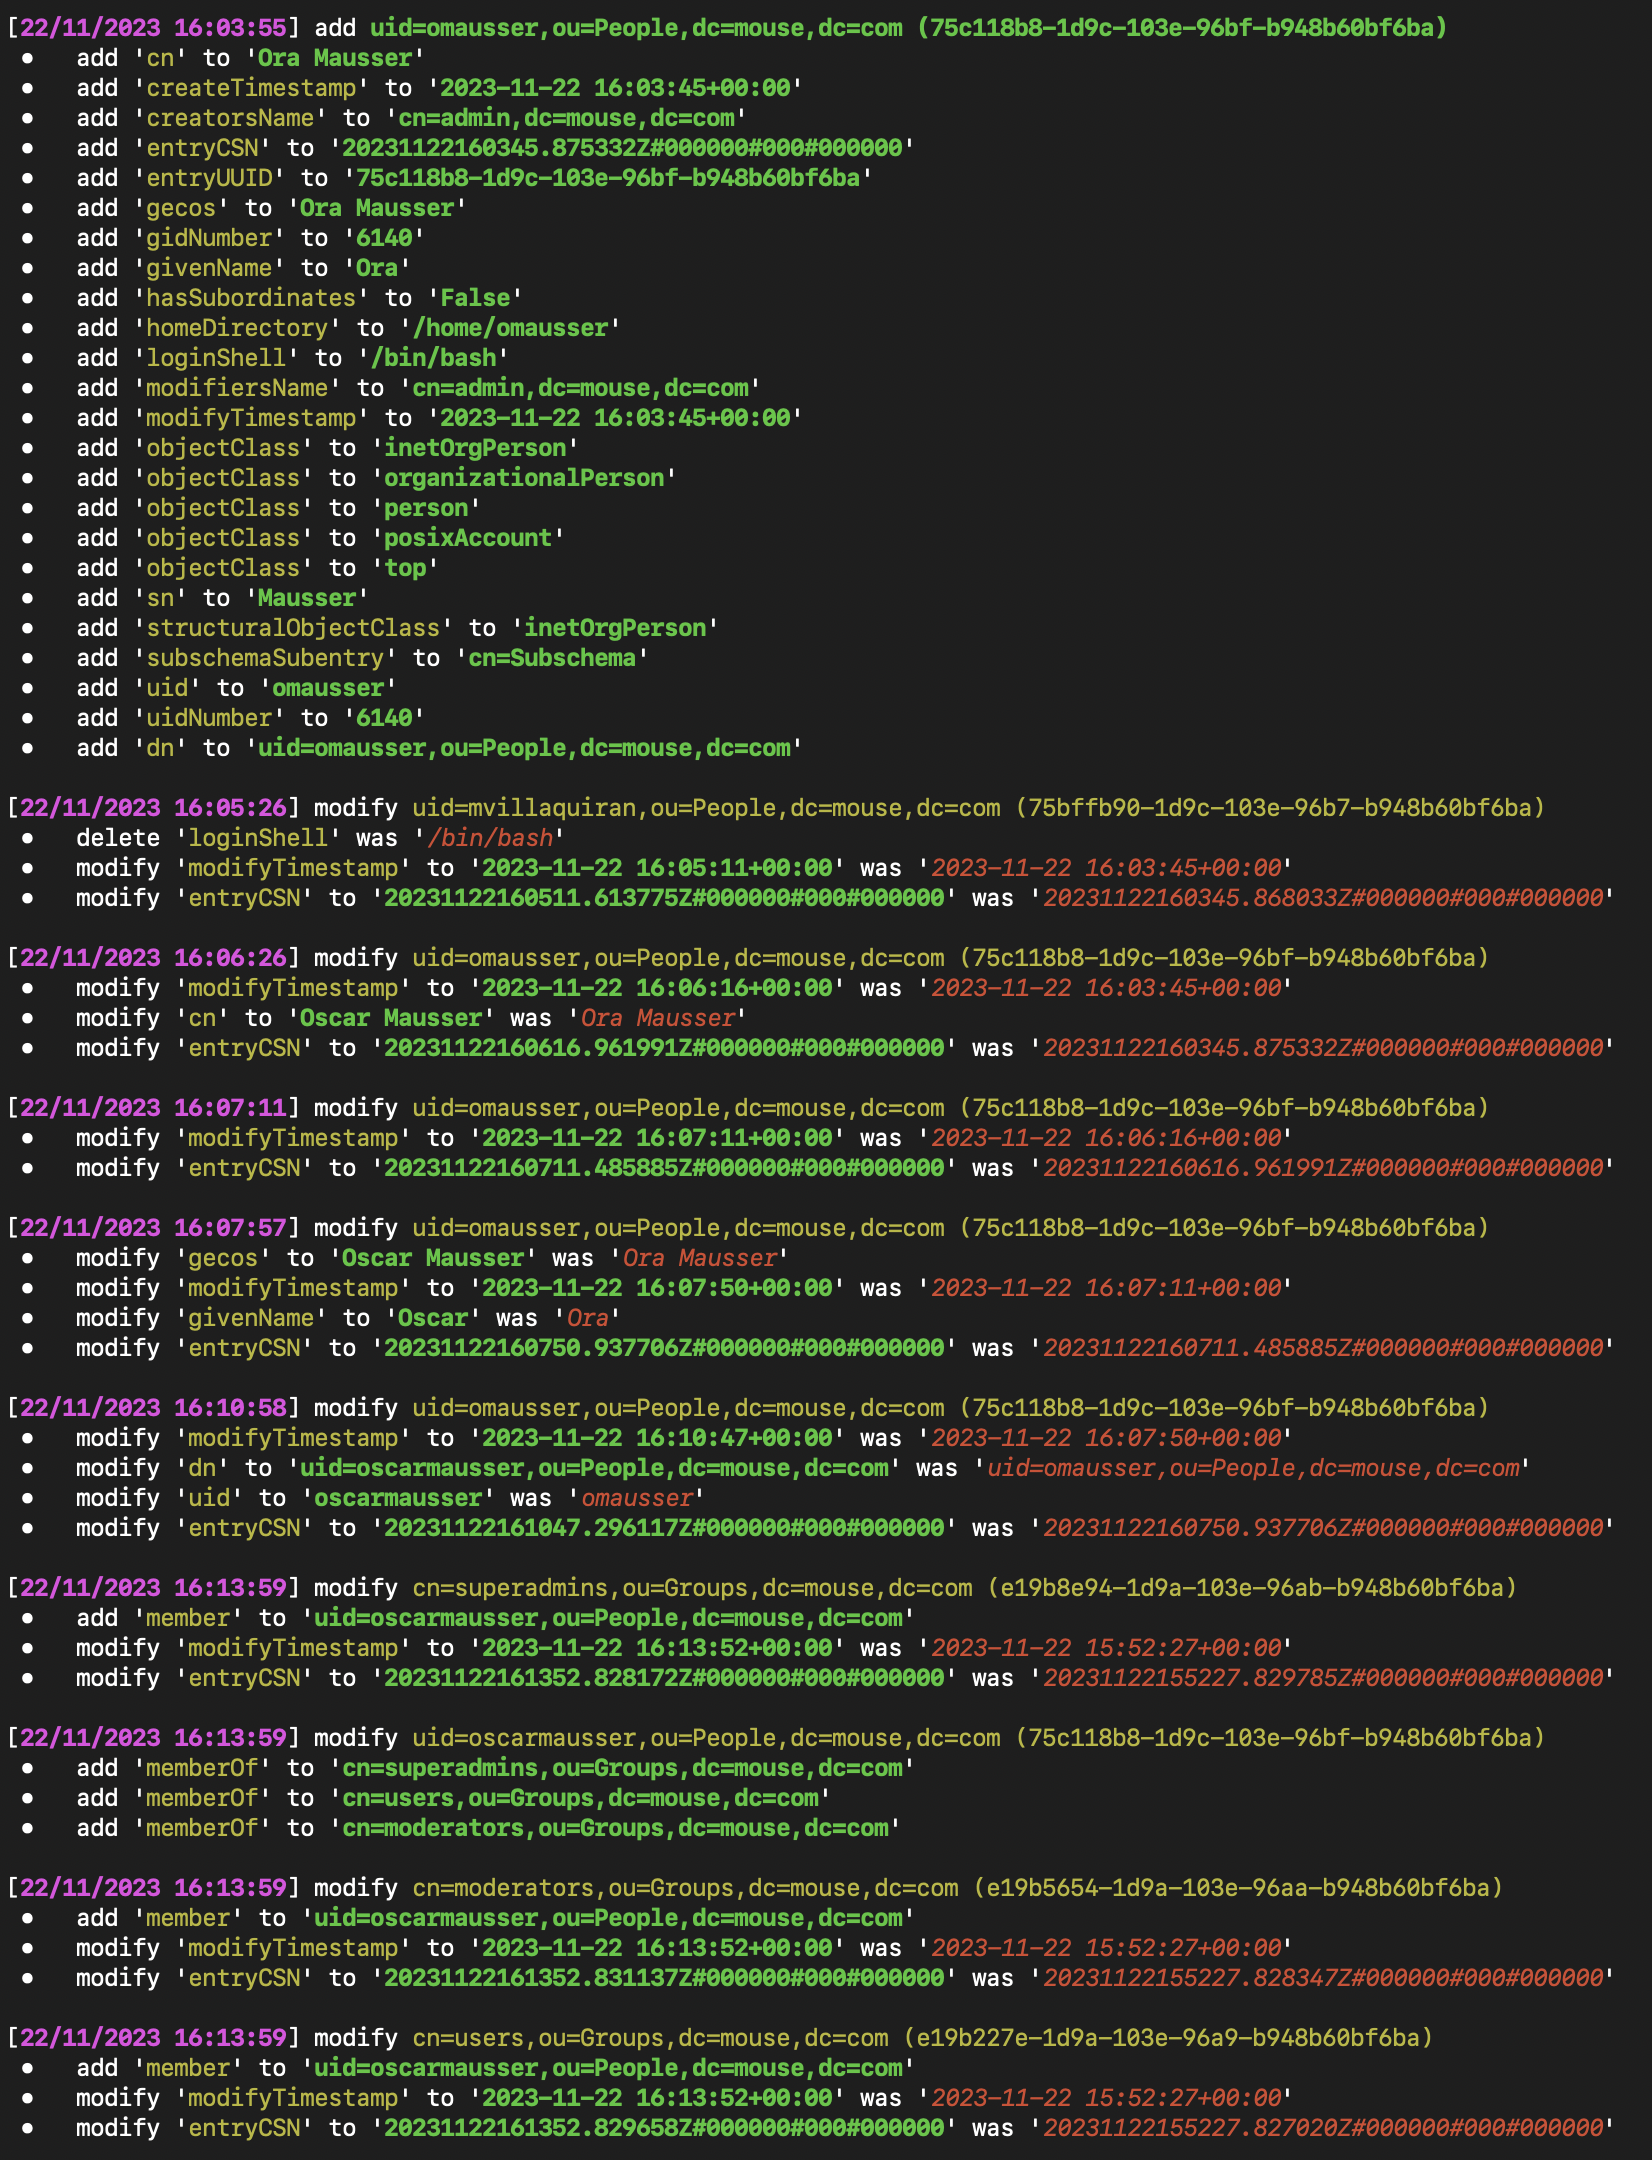
LDAP Watchdog: A real-time linux-compatible LDAP monitoring tool for detecting directory changes, providing visibility into additions, modifications,…

Offline security-report converter to SARIF 2.1.0 and NDJSON with schema validation and preserved evidence provenance. No scanning or uploads.

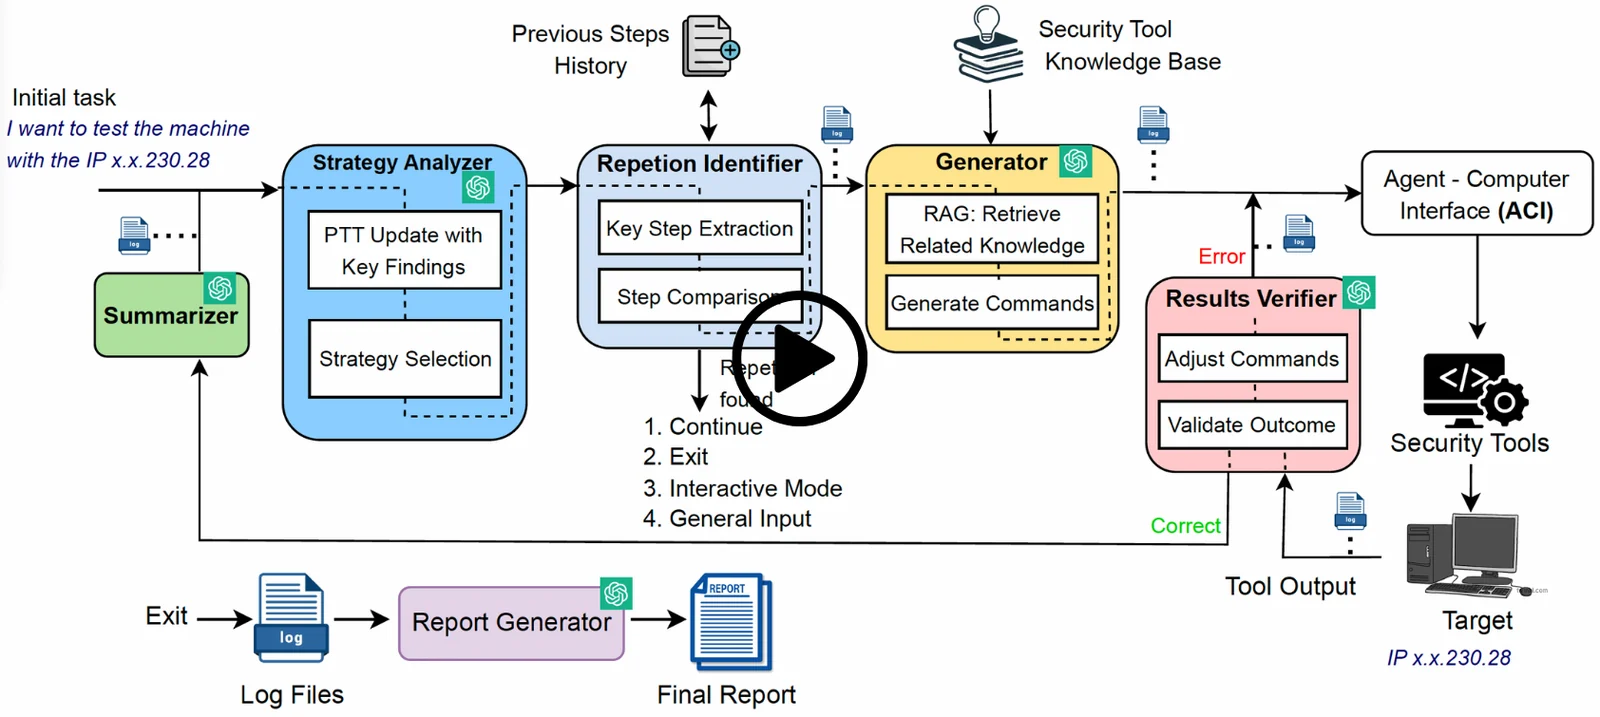
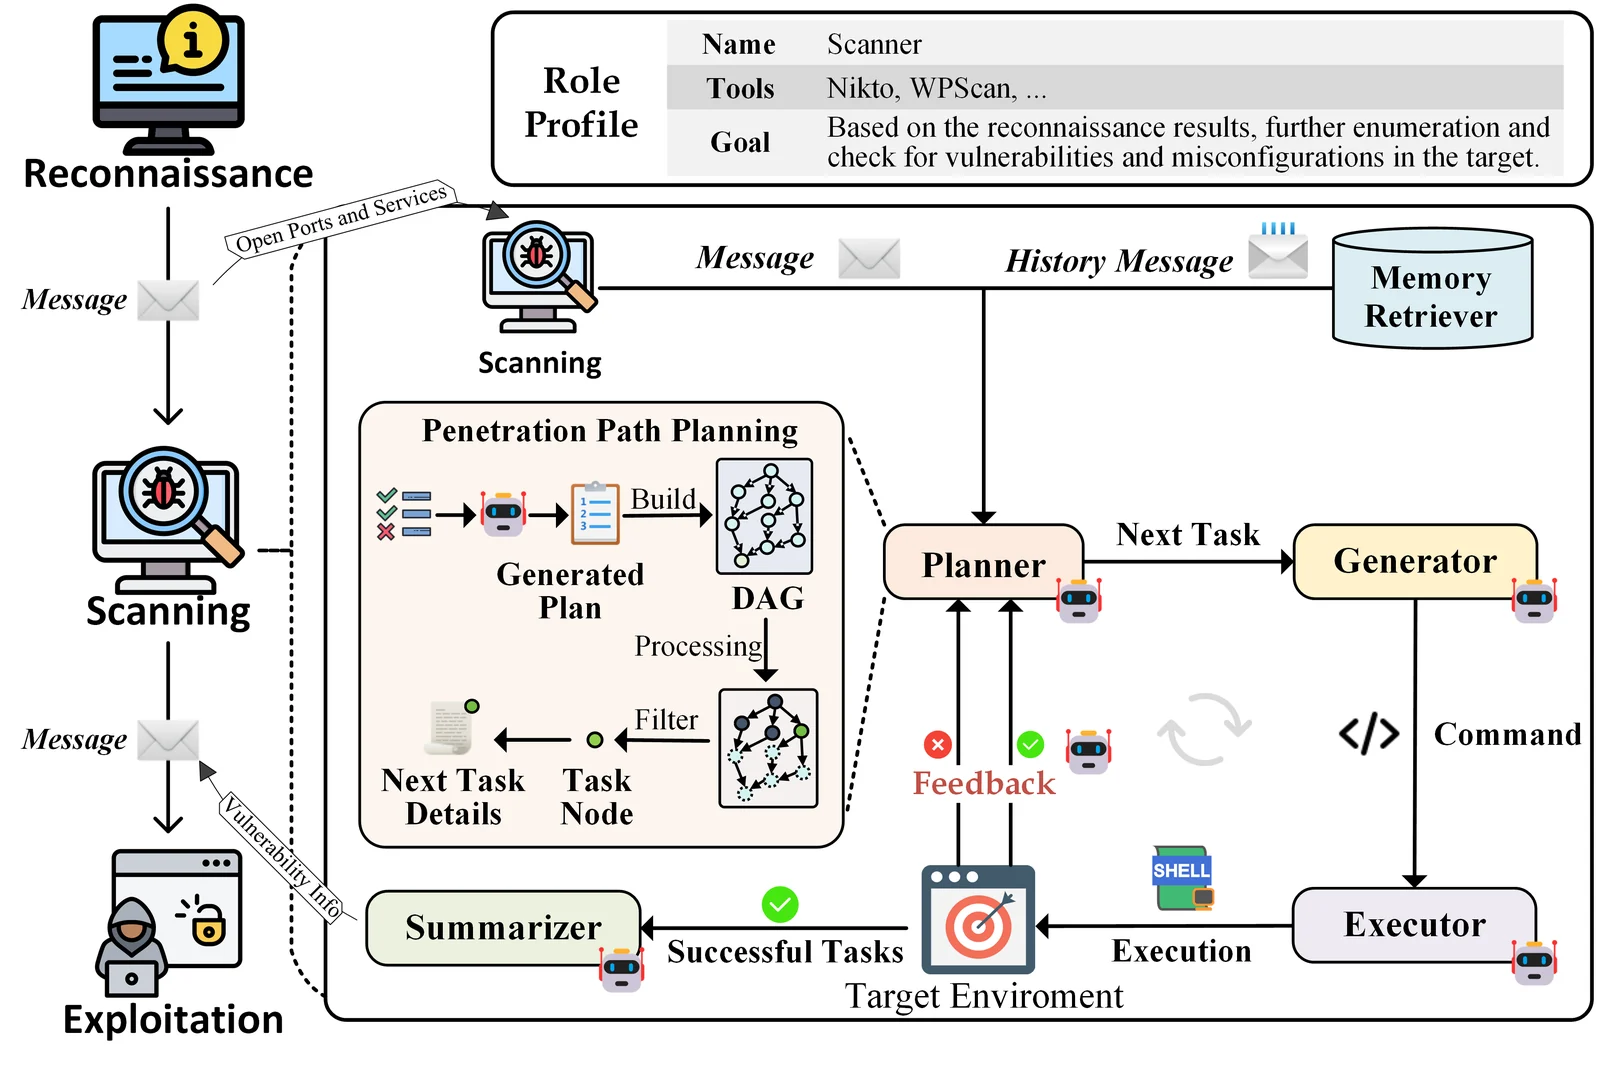
LLM-driven multi-agent framework that autonomously replicates human penetration testing workflows, orchestrating Kali Linux tooling and RAG knowledge…
Evidence Aug 25, 2026
1 Repository evidence · Evidence observed: Oct 18, 2026
Evidence Aug 19, 2026
1 Repository evidence · Evidence observed: Sep 26, 2026
Evidence May 4, 2026
1 Repository evidence · Evidence observed: Sep 26, 2026


7.45M-document cyber threat intelligence corpus and benchmark linking hacker-forum, exploit and advisory text to 340K NVD CVEs, with temporal splits…

LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and…

CVE-2026-109618/109619 — 5 RCE chains + detection rules (Suricata, Sigma, ModSecurity). PHP session.upload_progress pre-auth exploit research.

MCP server exposing 180+ reverse-engineering tools that aggregate Ghidra, IDA, x64dbg, Frida and 56 other backends with native binary parsers and a…

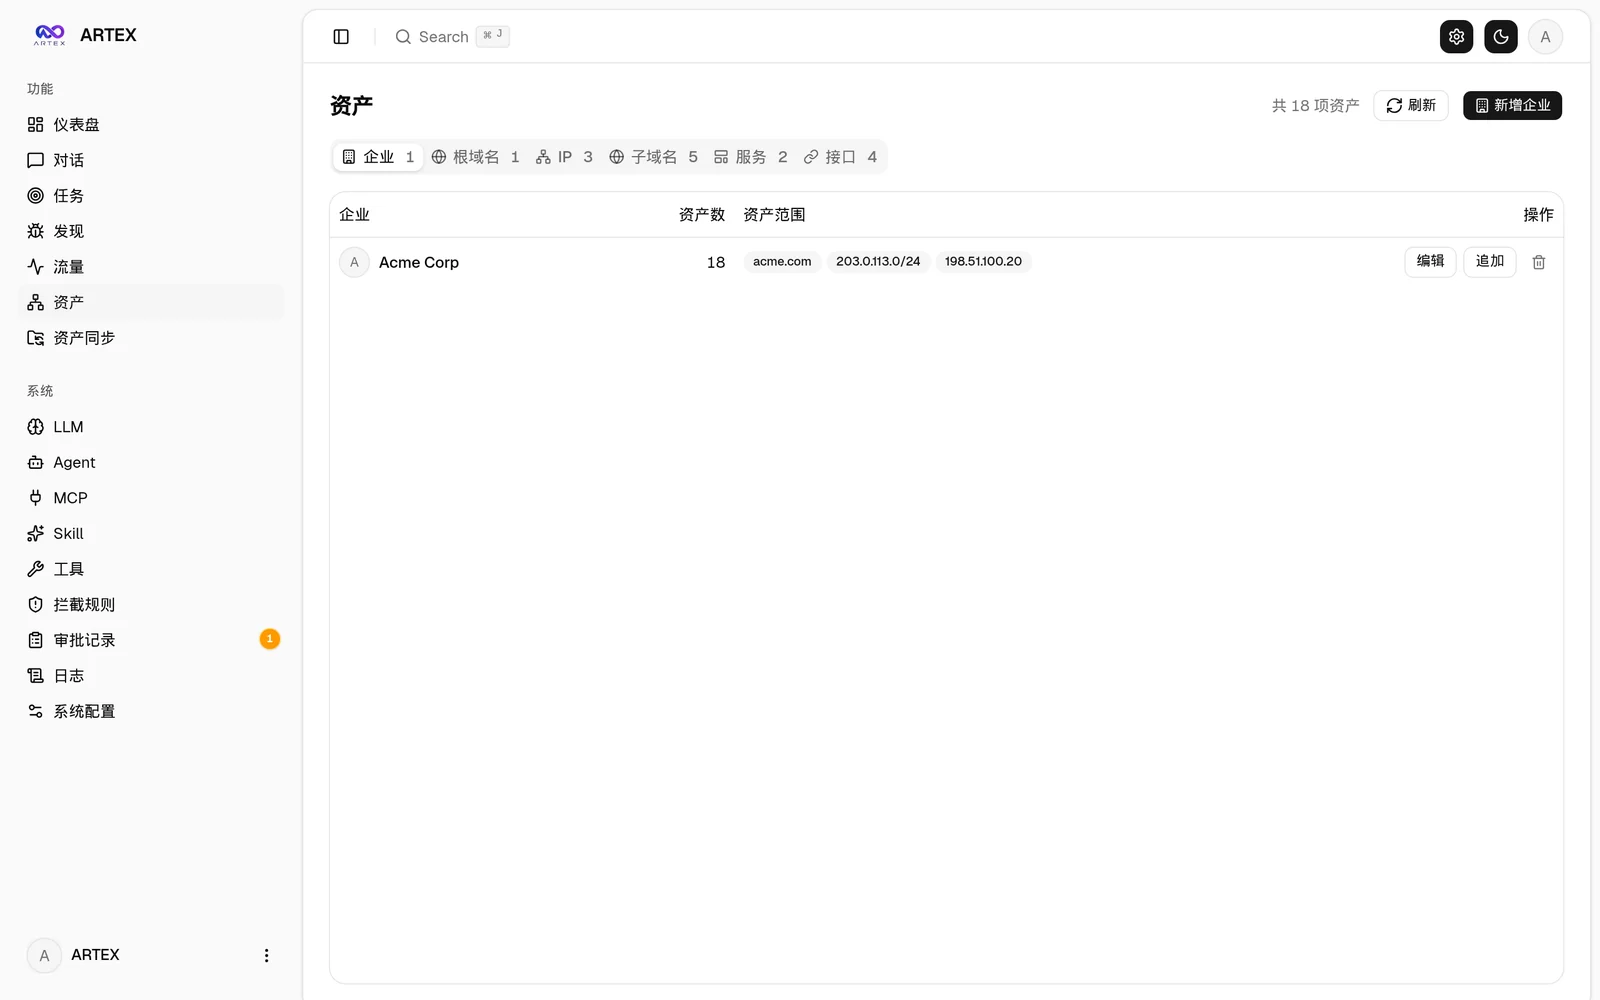
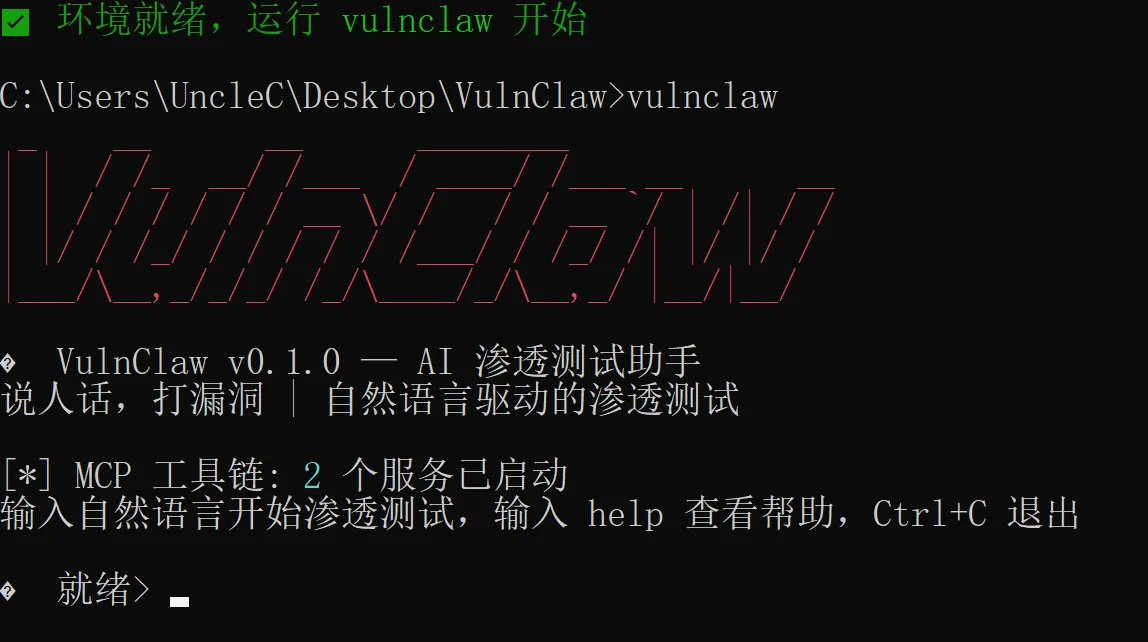
基于 AI Agent + MCP 工具链 + 渗透 Skill 编排, 配合大语言模型, 自然语言输入 → 自动完成「信息收集 → 漏洞发现 → 漏洞利用 → 报告生成」全流程。

Curated collection of LLM jailbreak prompts and bypass techniques, documenting adversarial inputs that circumvent AI model safety guardrails.

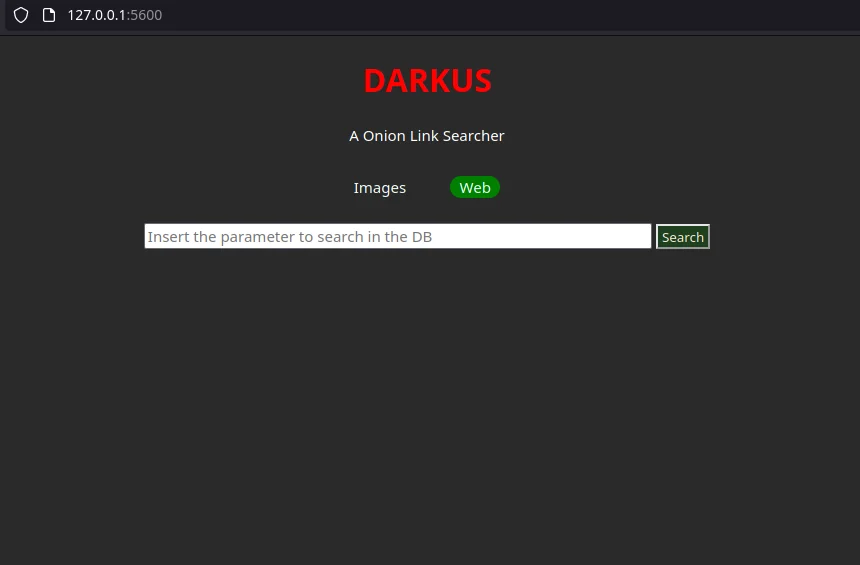
Searches dark web and onion search engines for keywords and returns matching onion links, with optional local database storage and Ahmia blacklist…


7.45M-document cyber threat intelligence corpus and benchmark linking hacker-forum, exploit and advisory text to 340K NVD CVEs, with temporal splits…

LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and…

CVE-2026-109618/109619 — 5 RCE chains + detection rules (Suricata, Sigma, ModSecurity). PHP session.upload_progress pre-auth exploit research.

MCP server exposing 180+ reverse-engineering tools that aggregate Ghidra, IDA, x64dbg, Frida and 56 other backends with native binary parsers and a…

基于 AI Agent + MCP 工具链 + 渗透 Skill 编排, 配合大语言模型, 自然语言输入 → 自动完成「信息收集 → 漏洞发现 → 漏洞利用 → 报告生成」全流程。

Curated collection of LLM jailbreak prompts and bypass techniques, documenting adversarial inputs that circumvent AI model safety guardrails.

Searches dark web and onion search engines for keywords and returns matching onion links, with optional local database storage and Ahmia blacklist…