Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
sarenka — OSINT tool - gets data from services like shodan, censys etc. in one app | Kitploit
Tools/GitHubGitHub/ktzgraph/sarenka
OSINT (Open Source Intelligence)ReconnaissanceVulnerability AnalysisHash AnalysisInformation GatheringCrawlerDNS Analysis
GitHubktzgraph/sarenka

sarenka

OSINT tool - gets data from services like shodan, censys etc. in one app
View Repository
67485484 years agoReviewed by Kitploit
Share
Website

sarenka-logo

Release release CircleCi release CircleCi release Platform release Platform release Python version CWE feed CVE feed license

♥ Free Software, requires only free accounts to third part services ♥

Lack of knowledge ... that is the problem.

[William Edwards Deming]

SARENKA is an Open Source Intelligence (OSINT) tool that helps you in obtaining and understanding Attack Surface.

The main goal is gathering information from search engines for Internet-connected devices (https://censys.io/, https://www.shodan.io/, https://www.criminalip.io/ko). It scrapes data about Common Vulnerabilities and Exposures (CVE), Common Weakness Enumeration (CWE) and also has a database where CVEs are mapped to CWE.

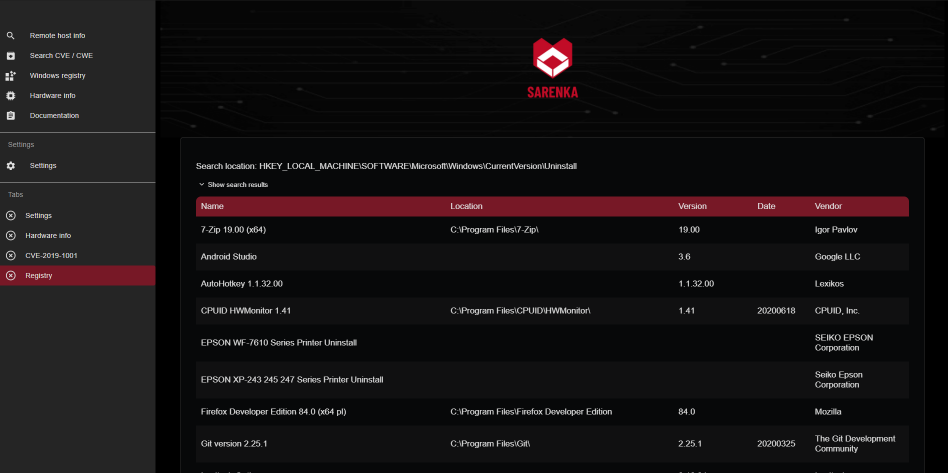
It returns data about the local machine - local installed software (from Windows Registry), local network information (python libraries, popular cmd commads).

For now, the application also has simple tools like a hash calculator, shannon entropy calculator and very simple port scanner. More cryptography-math tools and reconnaissance scripts are planned.

The app is alive and has been rewritten from scratch on branch develop.

Contributors

Author Author Author

SARENKA was mentioned here:

  • ncybersec
  • llllap3xllll
  • securityonline.info
  • haxf4rall.com
  • hackdig.com
  • findglocal.com
  • 台灣數位國土安全部 - DDHS
  • laptrinhx.com
  • kitploit.com
  • attackware.com
  • hacking.land
  • cyberfishnews.com
  • modernnetsec.io
  • spywarenews.com
  • cert.europa.eu
  • dfir.pro
  • iransec.net
  • hacker-gadgets.com
  • vulners.com
  • redpacketsecurity.com
  • kali-linuxtr.net
  • anonymousmedia.org
  • pentesttools.net
  • wangshit.xyz
  • geekychild.com
  • hacker.observer
  • nuomiphp.com
  • danielonsecurity.com
  • haktechs
  • cybeseclabs.com
  • vk.com
  • hacking.reviews
  • thehacker.co
  • iguru.gr
  • en.iguru.gr
  • rucore.net
  • hackerzzz.com
  • my.oschina.net
  • kalilinuxtutorials.com
  • pintait.com
  • osintbrasil.blogspot.com
  • wenyanet.com
  • federatica.space
  • giters.com
  • redhotcyber.com
  • haktechs.com
  • hakin9.org
  • www.libhunt.com
  • cybersec365.org
  • reddit.com user mikeis075
  • blackhatethicalhacking.com
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    786
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    506
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    429
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    345
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    262
  • 6

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    256

Explore all tools

Browse our collection of tools

View all tools →





