

HoneypotBuster
 javelinnetworks/honeypotbuster
PowerShell module for red teams to detect honeypots, honeytokens, and deception techniques in Active Directory environments, including fake accounts,…
penetration-testingred-teaming
javelinnetworks/honeypotbusterPowerShell module for red teams to detect honeypots, honeytokens, and deception techniques in Active Directory environments, including fake accounts,…
 owasp/openshield
Open source CSPM for Azure - scan for misconfigurations and quantum-unsafe cryptography, map findings to CIS/NIST/ISO27001/SOC2, and fix them with…
 silverpoision/rock-on
Rock-On is a all in one Recon tool that will just get a single entry of the Domain name and do all of the work alone.
 divinelabio/argus
The Ultimate Information Gathering Toolkit
 makefu/dnsmap
fork of http://code.google.com/p/dnsmap/source/checkout
 fricciolosa-red-team/evildork
Automated Google dorking tool for extracting leaked secrets, personal information, and subdomains from a target domain or individual, outputting…
 a3h1nt/sububy
Modular subdomain enumeration suite with certificate transparency, DNS brute-force, and API-based discovery. Includes post-enumeration modules for…
 wattocyber/vegadns
Rust-based DNS enumeration and subdomain discovery tool for reconnaissance and penetration testing security assessments.
 kira2040k/php_code_analysis
Static PHP code scanner that detects SQL injection, XSS, SSRF, LFI, command injection, insecure deserialization, and other web vulnerabilities in…
 imbas007/poc_cve-2026-41940
Proof-of-concept exploit for CVE-2026-41940 targeting cPanel, enabling account enumeration, command execution, and interactive shell access on…
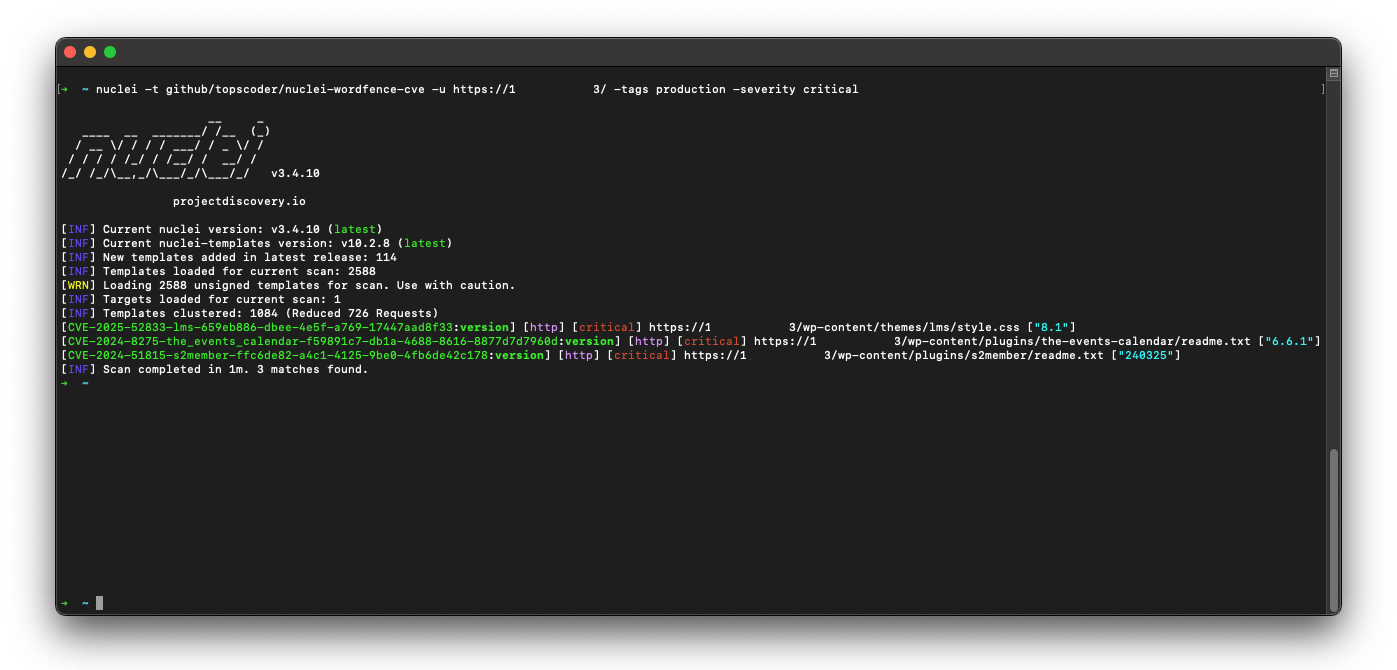 topscoder/nuclei-wordfence-cve
80k+ WordPress Nuclei templates, updated daily from Wordfence intel—filter by severity/tags/CVE and scan in one line. 🚀🔒
 m0usem0use/erl_mouse
python script to find vulnerable targets of CVE-2025-32433
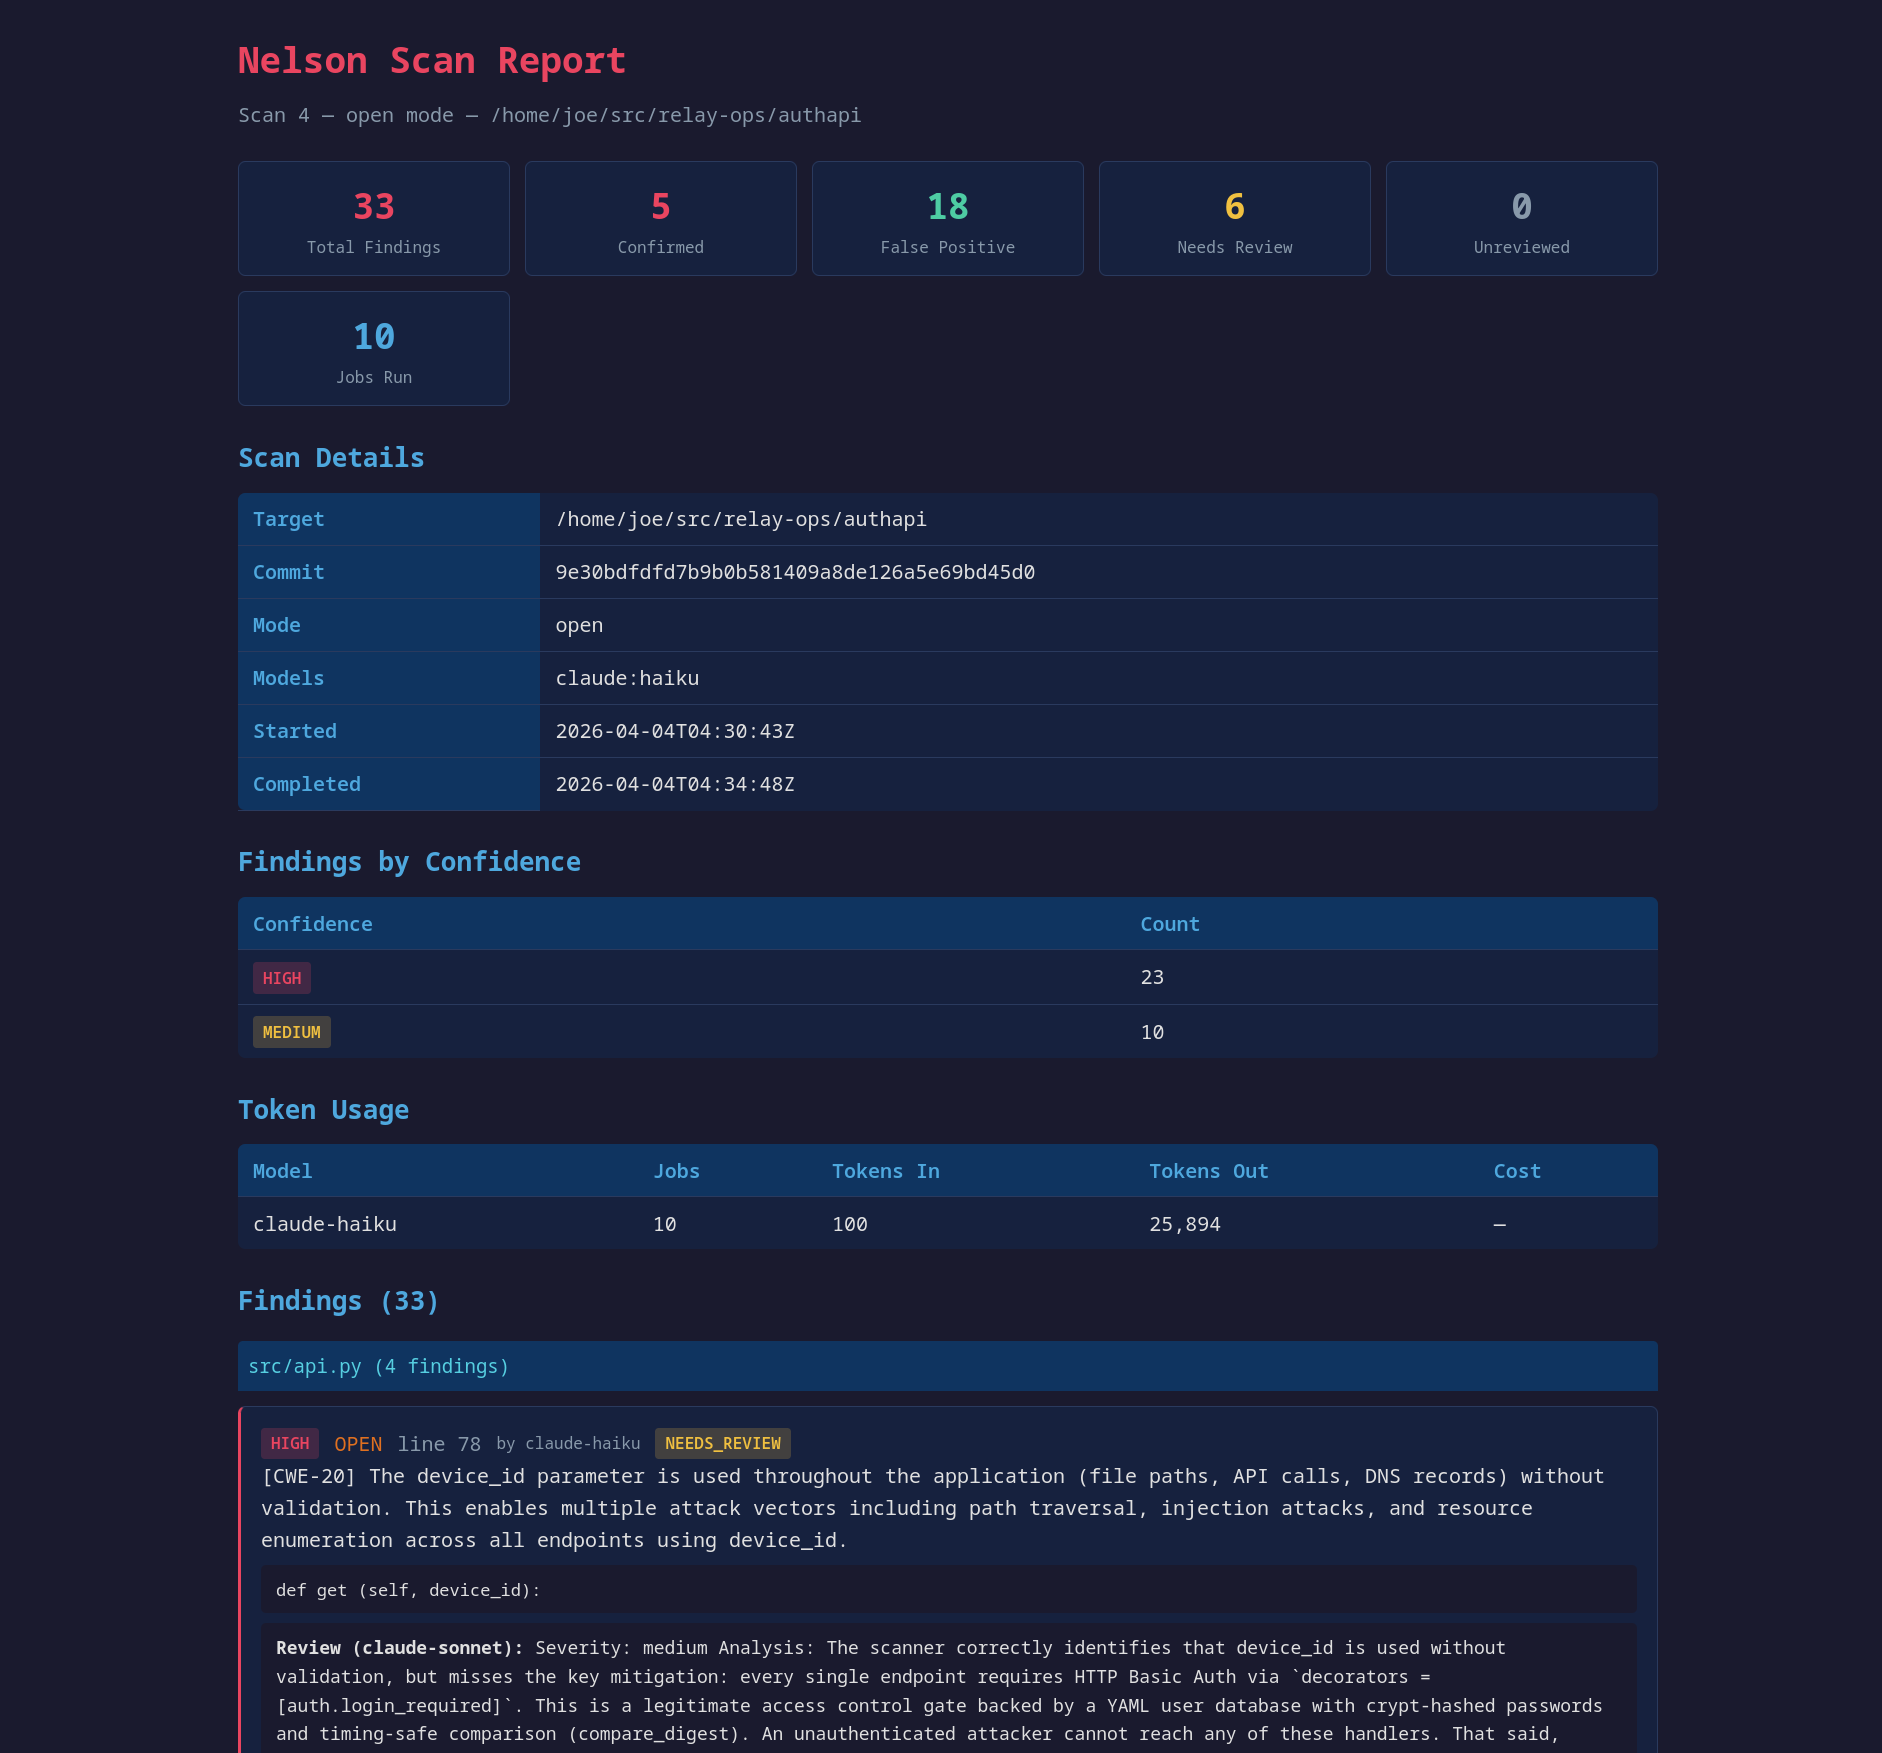 swelljoe/nelson
Finding vulnerabilities through dumb brute force
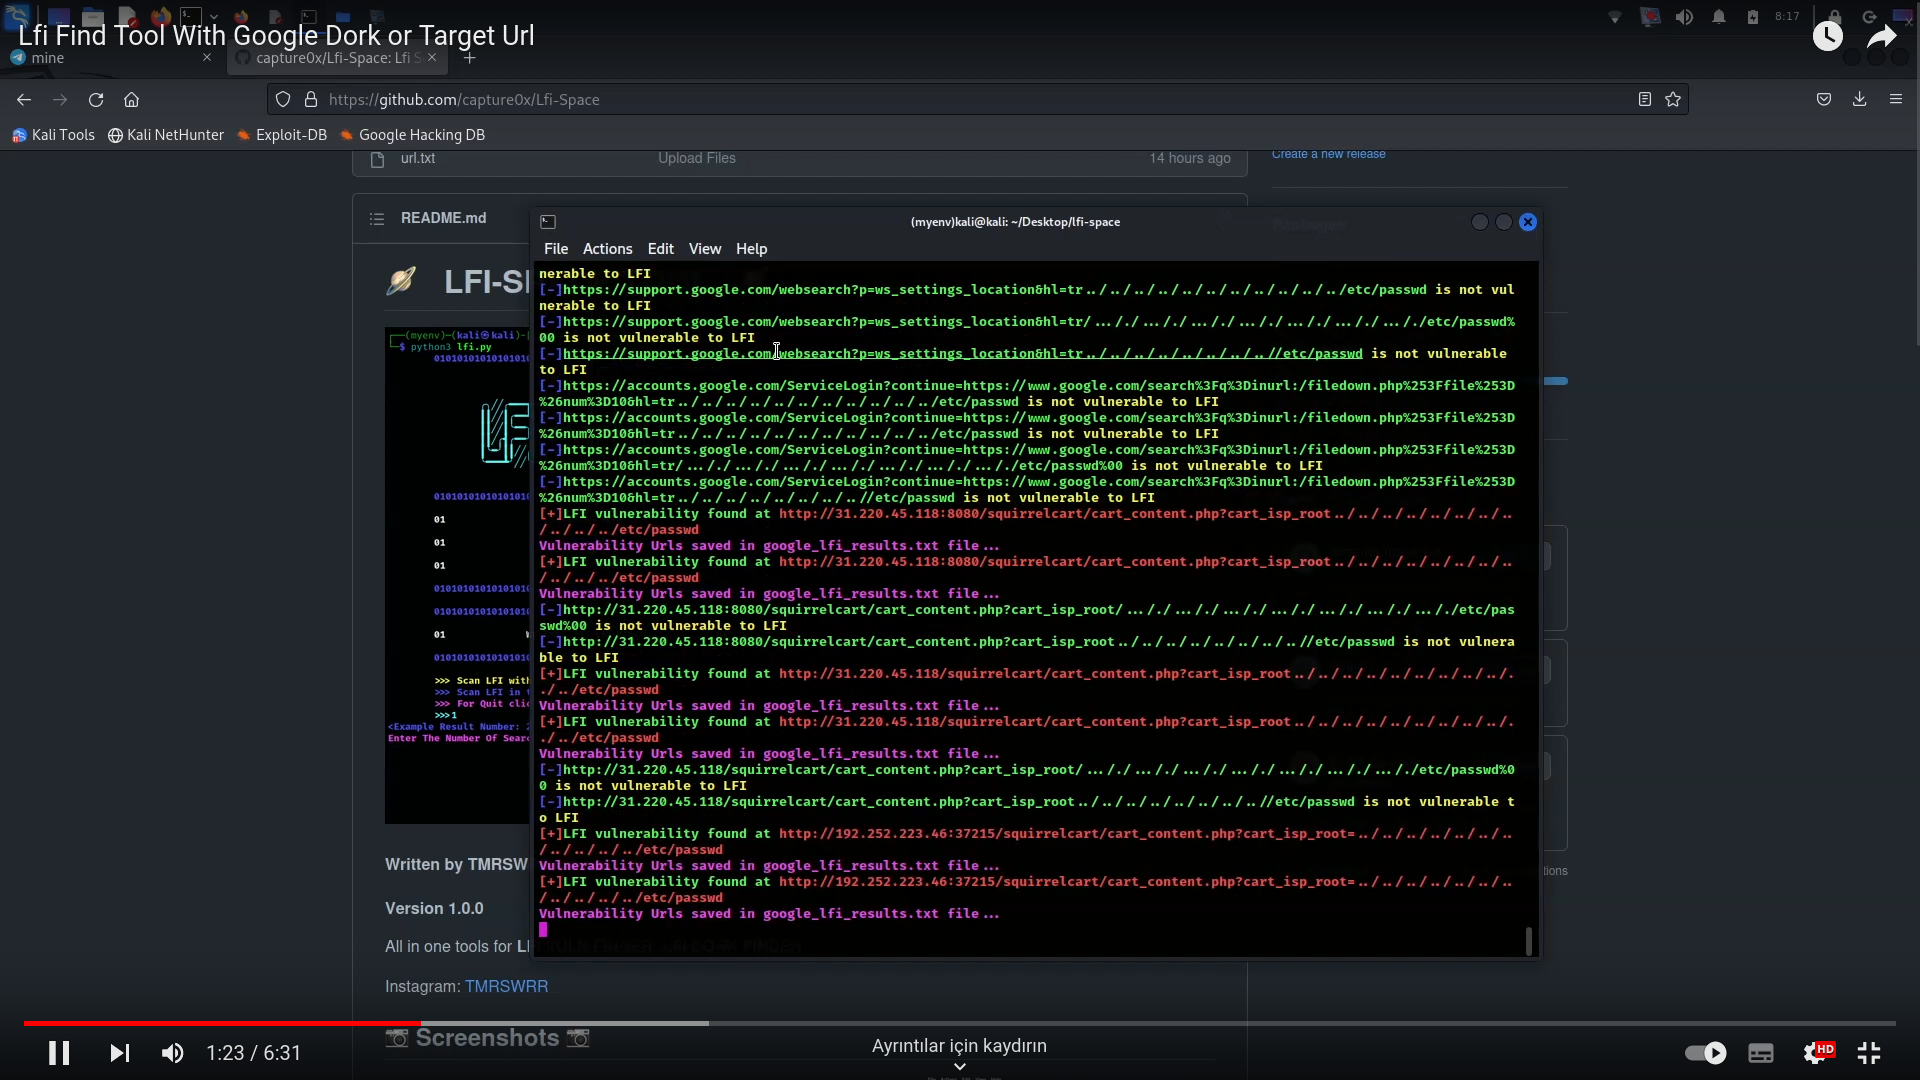 capture0x/lfi-space
Automated Local File Inclusion (LFI) vulnerability scanner with Google Dork search and targeted URL scan modes for web application security testing.
 andrysqui/cve-2024-9166
A vulnerability scanner that searches for the CVE-2024-9166 vulnerability on websites, more info about this vulnerability here:…
 pavanw3b/sh00t
Security Testing is not as simple as right click > Scan. It's messy, a tough game. What if you had missed to test just that one thing and had to…
 tencent/ai-infra-guard
A full-stack AI Red Teaming platform securing AI ecosystems via Agent Scan, Skills Scan, MCP scan, AI Infra scan and LLM jailbreak evaluation.
 tuhinshubhra/red_hawk
All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers