Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
RedditC2 — Abusing Reddit API to host the C2 traffic. | Kitploit
Tools/GitHubGitHub/kleiton0x00/redditc2
ExploitationCommand and ControlRed TeamingPayload Development
GitHubkleiton0x00/redditc2

RedditC2

Abusing Reddit API to host the C2 traffic.

View Repository
277471423 years agoReviewed by Kitploit
Share

RedditC2

Abusing Reddit API to host the C2 traffic, since most of the blue-team members use Reddit, it might be a great way to make the traffic look legit.

🚫 [Disclaimer]: Use of this project is for Educational/ Testing purposes only. Using it on unauthorised machines is strictly forbidden. If somebody is found to use it for illegal/ malicious intent, author of the repo will not be held responsible.


Requirements

Install PRAW library in python3:

pip3 install praw

Quickstart

See the Quickstart guide on how to get going right away!

Demo

https://user-images.githubusercontent.com/37262788/206015879-589614d5-1a7a-4c21-a342-75bdfc677a61.mp4

Workflow

Teamserver

  1. Go to the specific Reddit Post & post a new comment with the command ("in: ")
  2. Read for new comment which includes the word "out:"
  3. If no such comment is found, go back to step 2
  4. Parse the comment, decrypt it and read it's output
  5. Edit the existing comment to "executed", to avoid reexecuting it

Client

  1. Go to the specific Reddit Post & read the latest comment which includes "in:"
  2. If no new comment is detected, go back to step 1
  3. Parse the command out of the comment, decrypt it and execute it locally
  4. Encrypt the command's output and reply it to the respective comment ("out:" )

Below is a demonstration of the XOR-encrypted C2 traffic for understanding purposes:
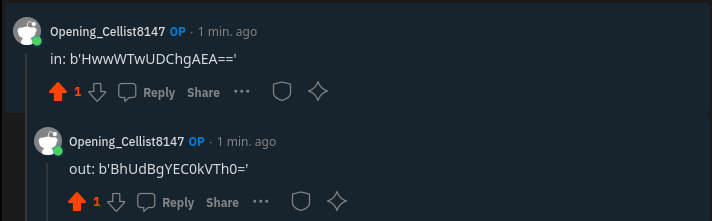
Screenshot from 2022-12-15 10-58-34

Scanning results

Since it is a custom C2 Implant, it doesn't get detected by any AV as the bevahiour is completely legit.

TO-DO

  • Teamserver and agent compatible in Windows/Linux
  • Make the traffic encrypted
  • Add upload/download feature
  • Add persistence feature
  • Generate the agents dynamically (from the TeamServer)
  • Tab autocompletion

Credits

Special thanks to @T4TCH3R for working with me and contributing to this project.

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    1.0k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    593
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    371
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    336
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    326
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    322

Explore all tools

Browse our collection of tools

View all tools →





