

Windows-PE-Packer
 czs108/windows-pe-packer
🗜️ A packer for Windows x86 executable files written in C and Intel x86 Assembly. The new file after packing can obstruct reverse…
binary-analysisexploitationpayload-generation+1
367
czs108/windows-pe-packer🗜️ A packer for Windows x86 executable files written in C and Intel x86 Assembly. The new file after packing can obstruct reverse…
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
 hessandrew/cve-2020-0568_intel-sa-00344
Proof-of-concept or exploit code for Intel CVE-2020-0568 (INTEL-SA-00344), targeting a specific security vulnerability in Intel hardware or firmware.
 soldier0x0/briefr
Open Vulnerability Intelligence platform, aggregated intel in one dashboard, with correlation and IOC lookups, completely self hosted. All resources…
 yohanes/poc-cve-2025-31931
Proof-of-concept exploit for CVE-2025-31931 demonstrating arbitrary shared library loading in Intel ITT API on Android, affecting OpenCV 4.10.
 v1d1an/s1em
This project is a SIEM with SIRP and Threat Intel, all in one.
 gmh5225/cve-2015-2291
(1) IQVW32.sys before 1.3.1.0 and (2) IQVW64.sys before 1.3.1.0 in the Intel Ethernet diagnostics driver for Windows allows local users to cause a…
 zedocun/sharepoint-cve-2023-29375-incident-response
End-to-end SOC incident analysis and threat hunting playbook targeting Microsoft SharePoint privilege escalation (CVE-2023-29375) using SIEM logs,…
 thisistfs/rogue-framework
Desktop workbench for AFL++ fuzzing, cross-architecture QEMU emulation, harness development, Ghidra headless analysis, custom mutators, and patch…
 intel/intel-linux-processor-microcode-data-files
Official Intel microcode data files for updating processor firmware to mitigate security vulnerabilities and address functional issues on Linux…
 fundacion-sadosky/vbox_cve_2017_10235
[CVE-2017-10235] Description and PoC of VirtualBox E1000 device Buffer Overflow
 microsoft/igvm
Rust library and format specification for creating and loading Independent Guest Virtual Machine (IGVM) files, supporting hardware-isolated VMs with…
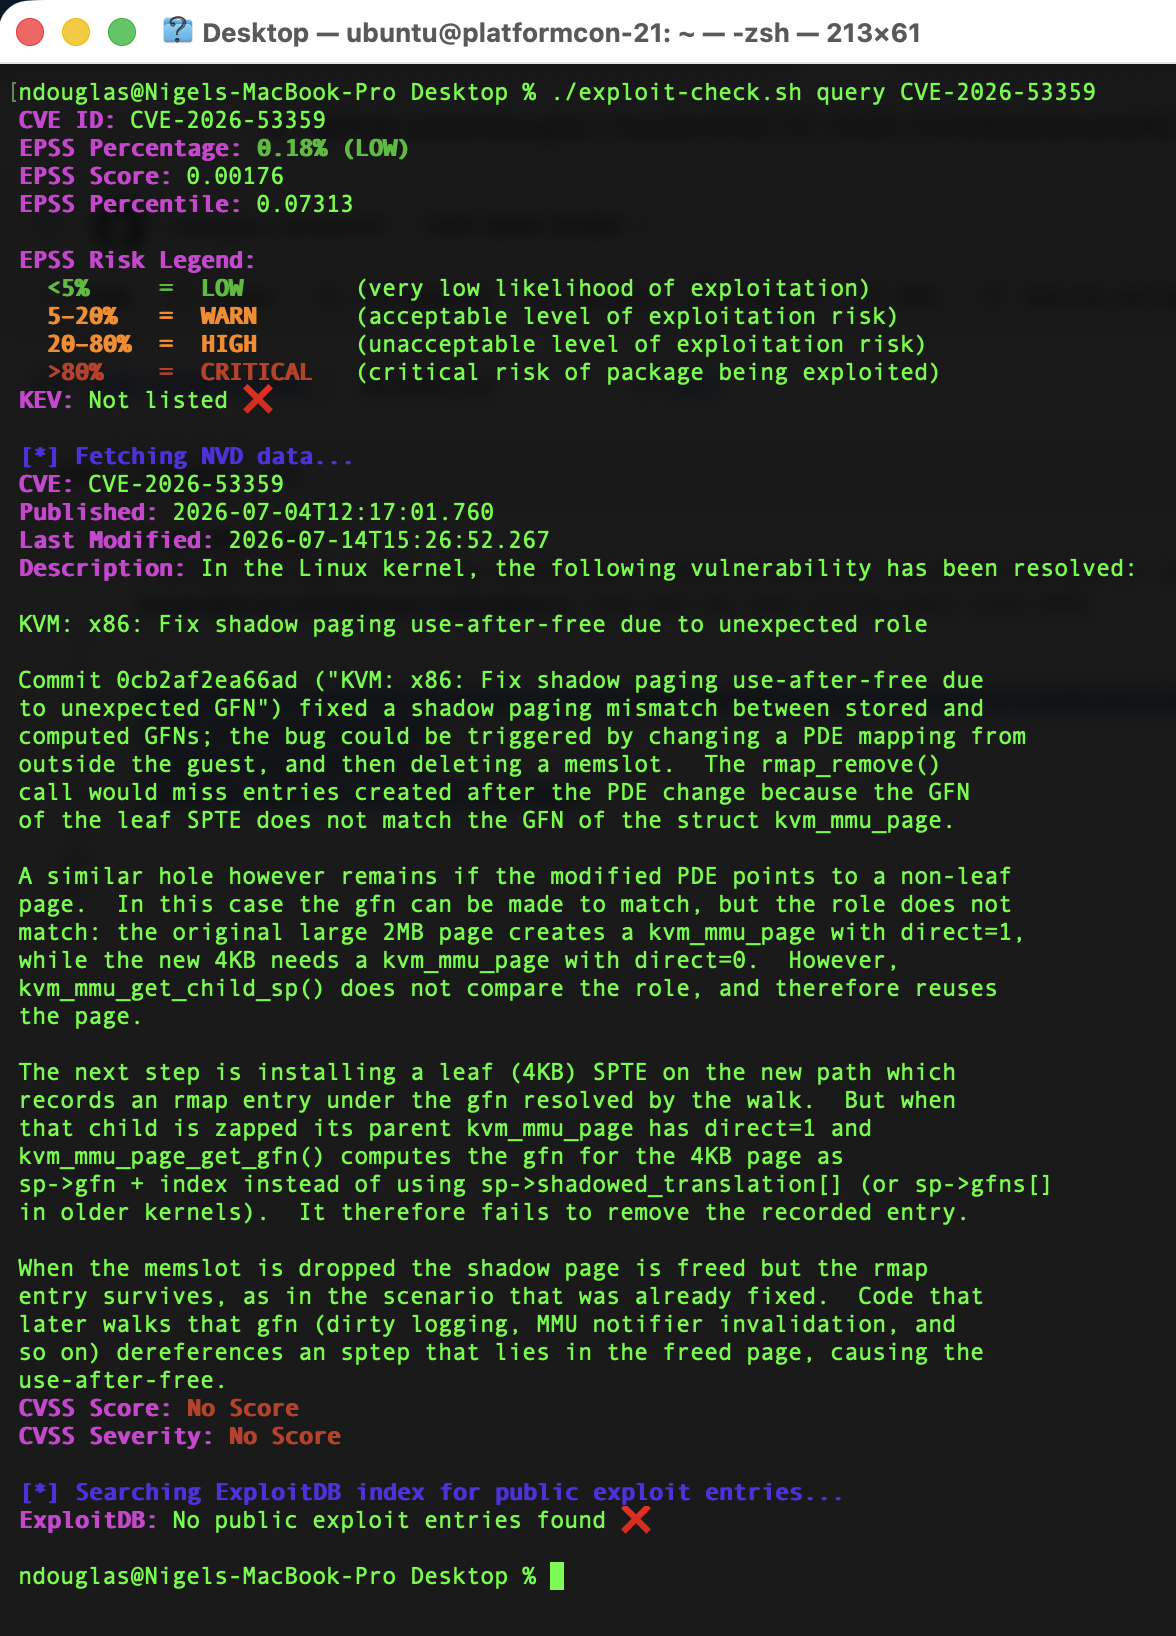 ndouglas-cloudsmith/cve-2026-53359
A 16-year-old bug in the Linux kernel lets a rented VM break out and attack the host it runs on. Intel and AMD alike. Januscape is a use-after-free…
 talyx66/webfang
WEBFANG, is my first CLI, a modular OSINT & Reconnaissance toolkit curated for Ethical Hackers and Red-Teamers. Sink fangs into web targets using a…
 theway-hue/cve-2017-5689-checker
Automated checker-exploit for CVE-2017-5689, scanning Intel AMT panels for authentication bypass and reporting vulnerable IPs.
 expel-io/expel-intel
This is the home of the Expel Intel Team. Here, we will share IOCs and other information that is either not suitable for fitting into other mediums…
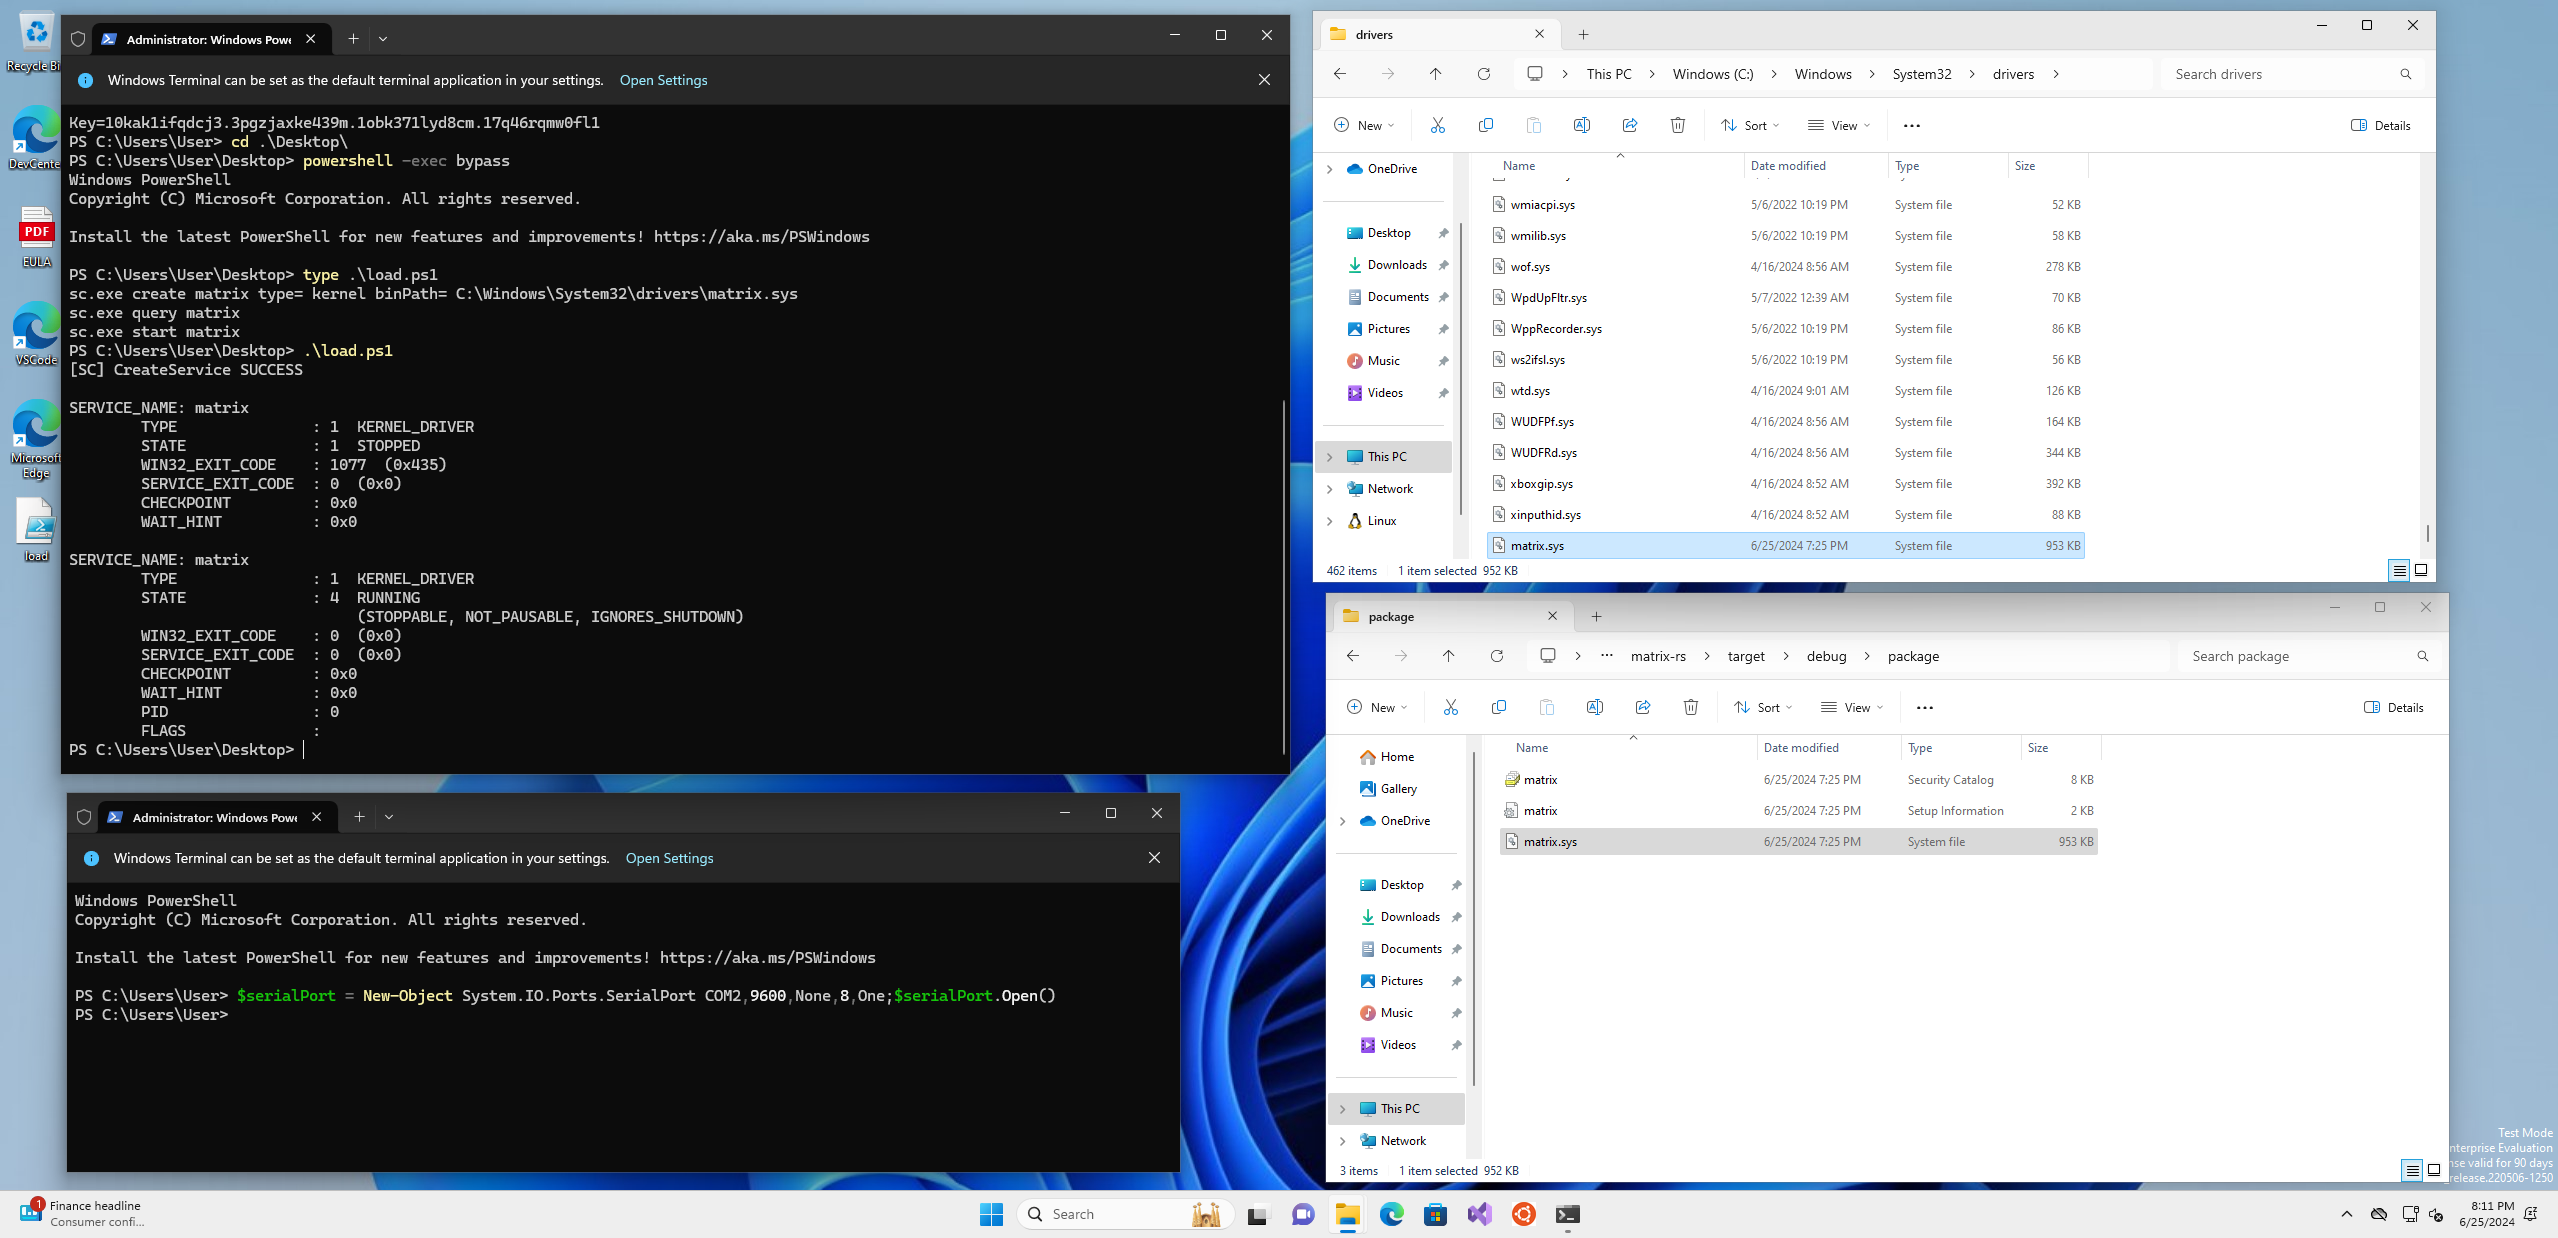 memn0ps/matrix-rs
Rusty Hypervisor - Windows Kernel Blue Pill Type-2 Hypervisor in Rust (Codename: Matrix)
 emirpolatt/cve-2022-31188
Proof-of-concept exploit for CVE-2022-31188, an SSRF vulnerability in OpenCV CVAT that allows authenticated users with Task Create permissions to…