Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
fastnetmon — Very fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support | Kitploit
Tools/GitHubGitHub/pavel-odintsov/fastnetmon
Packet Sniffing & AnalysisNetwork MappingNetwork SecurityUtilities & FrameworksThreat IntelligenceIncident ResponseAnomaly DetectionLog Analysis
GitHubpavel-odintsov/fastnetmon

fastnetmon

Very fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support

View Repository
3.7k5871254 days agoReviewed by Kitploit

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    985
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    571
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    354
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    341
  • 5

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    324
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    309

Explore all tools

Browse our collection of tools

View all tools →
Share

logo

Community Edition

FastNetMon - A high-performance DDoS detector/sensor built on top of multiple packet capture engines: NetFlow, IPFIX, sFlow, AF_PACKET (port mirror).

What do we do?

We detect hosts in the deployed network sending or receiving large volumes of traffic, packets/bytes/flows per second and perform a configurable action to handle that event. These configurable actions include notifying you, calling script or making BGP announcements.

Project

🌏️ Official site
⭐️ FastNetMon Advanced, Commercial Edition
🌟️ FastNetMon Advanced, free one-month trial
📜️ FastNetMon Advanced and Community difference table
📘️ Detailed reference

Legal

📖 FastNetMon Community Edition Terms and Conditions
🔏️ FastNetMon Community Edition Privacy Notice

FastNetMon is a product of FastNetMon LTD, UK. FastNetMon ® is a registered trademark in the UK and EU.

By installing or using this software, you confirm that you have read and agree to the FastNetMon Community Edition T&Cs and Privacy Notice, which will apply to your installation and use of the software

Installation

  • Linux install instructions
  • macOS install instructions
  • FreeBSD port

Supported packet capture engines

  • NetFlow v5, v9, v9 Lite
  • IPFIX
  • sFlow v5
  • PCAP
  • AF_PACKET (recommended)
  • AF_XDP (XDP based capture)
  • Netmap (deprecated, still supported only for FreeBSD)
  • PF_RING / PF_RING ZC (deprecated, available only for CentOS 6 in 1.2.0)

You can check out the comparison table for all available packet capture engines.

Features

  • Detects DoS/DDoS in as little as 1-2 seconds
  • Scales up to terabits on single server (sFlow, Netflow, IPFIX) or to 40G + in mirror mode
  • Trigger block/notify script if an IP exceeds defined thresholds for packets/bytes/flows per second
  • Thresholds can be configured per-subnet basis with the hostgroups feature
  • Email notifications about detected attack
  • Complete IPv6 support
  • Prometheus support: system metrics and total traffic counters
  • Flow and packet export to Kafka in JSON and Protobuf format
  • Announce blocked IPs via BGP to routers with ExaBGP or GoBGP (recommended)
  • Announce blocked IPs through rustbgpd gRPC API
  • Full integration with Clickhouse InfluxDB and Graphite
  • API
  • Redis integration
  • MongoDB protocol support compatible with native MongoDB and FerretDB
  • VLAN untagging in mirror and sFlow modes
  • Capture attack fingerprints in PCAP format

We track multiple platform and environment-specific metrics to understand ways how our product is being used and prioritise development accordingly.

Official support groups:

  • Mailing list
  • Slack
  • IRC: #fastnetmon at irc.libera.chat:6697 (TLS) web client
  • Telegram: fastnetmon
  • Discord: fastnetmon

Follow us at social media:

  • Twitter
  • LinkedIn
  • Facebook

Router integration instructions

  • Juniper MX Routers

Complete integration with the following vendors

  • Juniper integration
  • A10 Networks Thunder TPS Appliance integration
  • MikroTik RouterOS

Screenshots

Command line interface Main screen image


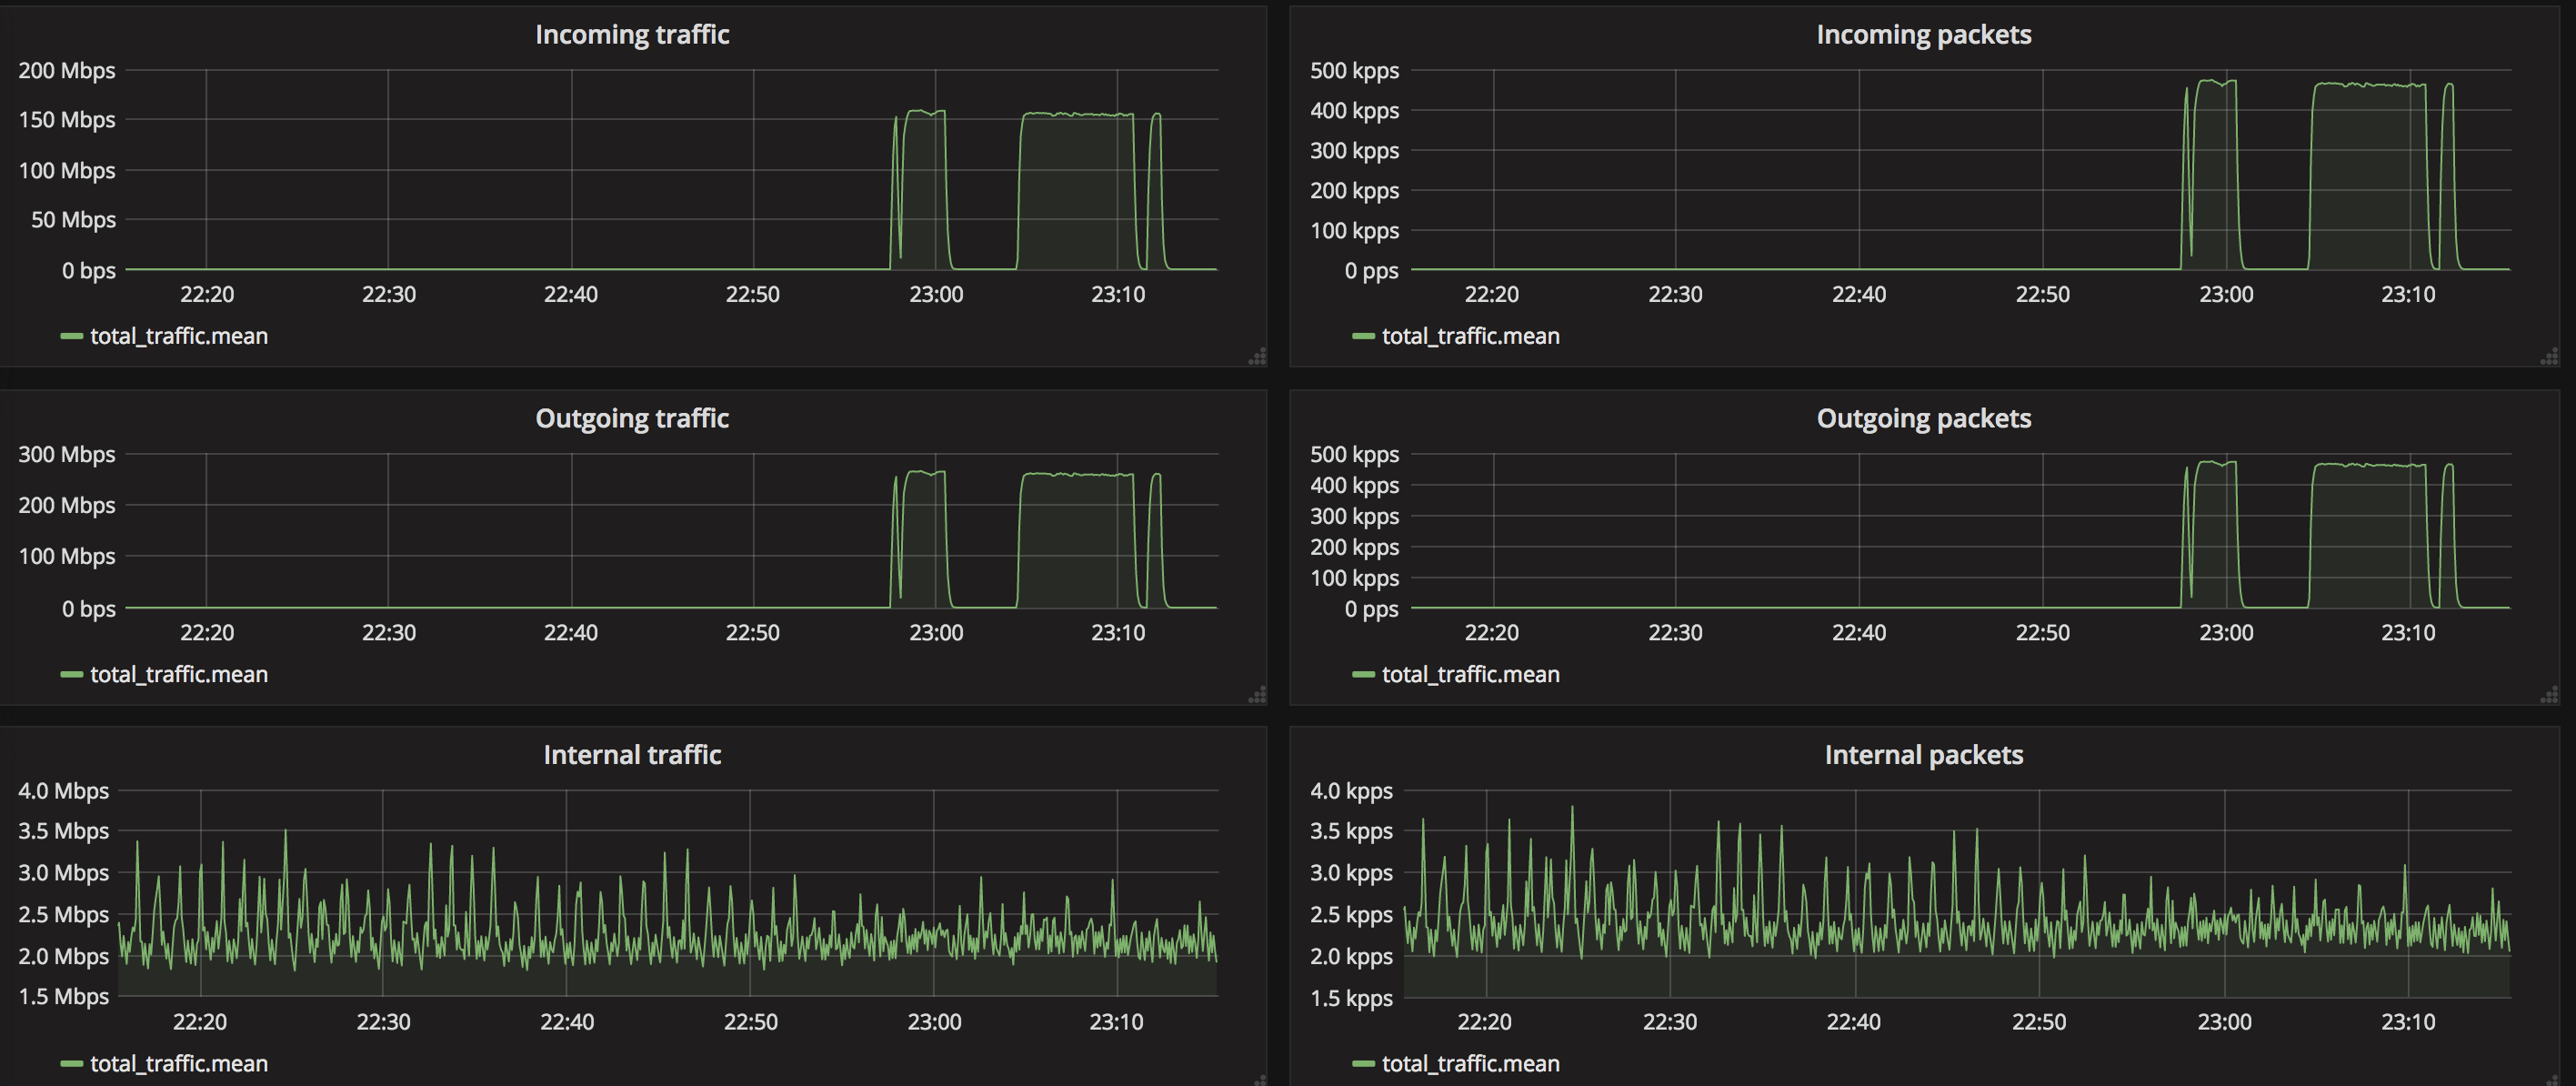
Standard Grafana dashboard Grafana total traffic

Example deployment scheme

Network diagramm

Upstream versions in different distributions

FastNetMon upstream distro packaging status

Snap: fastnetmon-community

Download Tool