Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
oss-fuzz — OSS-Fuzz - continuous fuzzing for open source software. | Kitploit
Tools/GitHubGitHub/google/oss-fuzz
Dynamic Analysis (Sandboxing)Vulnerability AnalysisFuzzingLearning & EducationTop in Fuzzing #2
GitHubgoogle/oss-fuzz

oss-fuzz

OSS-Fuzz - continuous fuzzing for open source software.

View Repository
12.5k2.9k1052h 31m agoReviewed by Kitploit
Share
Website

OSS-Fuzz: Continuous Fuzzing for Open Source Software

Fuzz testing is a well-known technique for uncovering programming errors in software. Many of these detectable errors, like buffer overflow, can have serious security implications. Google has found thousands of security vulnerabilities and stability bugs by deploying guided in-process fuzzing of Chrome components, and we now want to share that service with the open source community.

In cooperation with the Core Infrastructure Initiative and the OpenSSF, OSS-Fuzz aims to make common open source software more secure and stable by combining modern fuzzing techniques with scalable, distributed execution. Projects that do not qualify for OSS-Fuzz (e.g. closed source) can run their own instances of ClusterFuzz or ClusterFuzzLite.

We support the libFuzzer, AFL++, and Honggfuzz fuzzing engines in combination with Sanitizers, as well as ClusterFuzz, a distributed fuzzer execution environment and reporting tool.

Currently, OSS-Fuzz supports C/C++, Rust, Go, Python, Java/JVM, JavaScript and Lua code. Other languages supported by LLVM may work too. OSS-Fuzz supports fuzzing x86_64 and i386 builds.
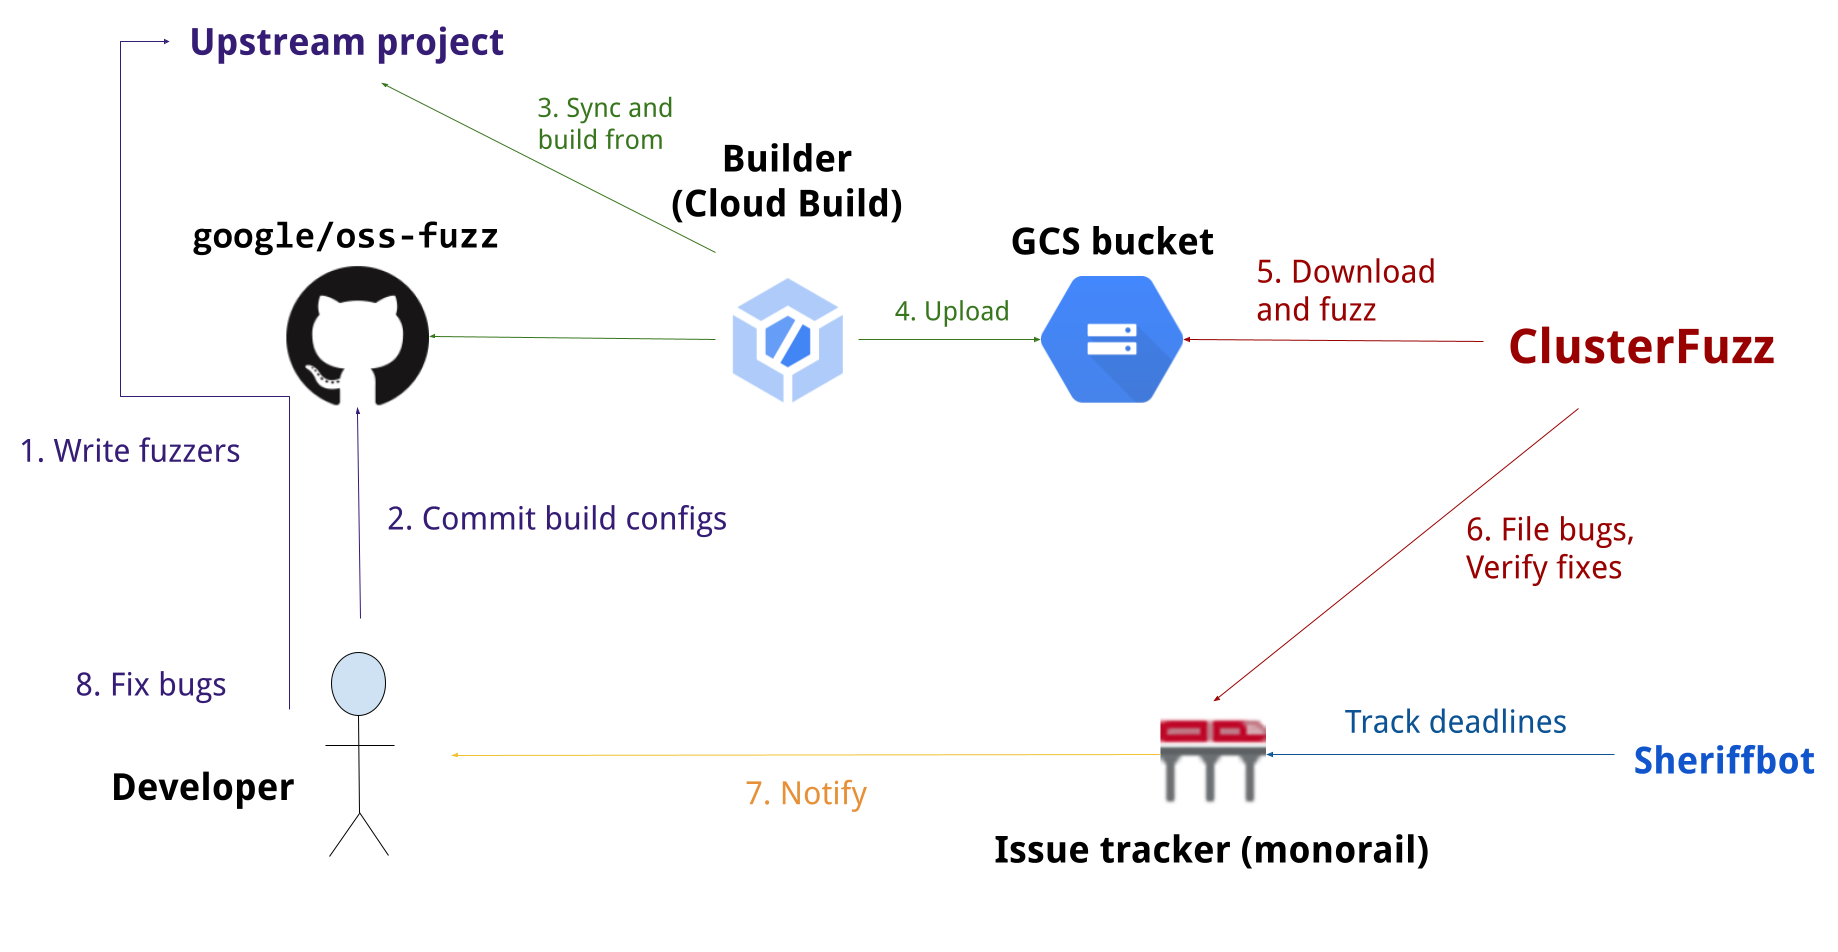
Overview

OSS-Fuzz process diagram

Documentation

Read our detailed documentation to learn how to use OSS-Fuzz.

Trophies

As of May 2025, OSS-Fuzz has helped identify and fix over 13,000 vulnerabilities and 50,000 bugs across 1,000 projects.


Blog posts

  • 2024-11-20 - Leveling Up Fuzzing: Finding more vulnerabilities with AI
  • 2023-08-16 - AI-Powered Fuzzing: Breaking the Bug Hunting Barrier
  • 2023-02-01 - Taking the next step: OSS-Fuzz in 2023
  • 2022-09-08 - Fuzzing beyond memory corruption: Finding broader classes of vulnerabilities automatically
  • 2021-12-16 - Improving OSS-Fuzz and Jazzer to catch Log4Shell
  • 2021-03-10 - Fuzzing Java in OSS-Fuzz
  • 2020-12-07 - Improving open source security during the Google summer internship program
  • 2020-10-09 - Fuzzing internships for Open Source Software
  • 2018-11-06 - A New Chapter for OSS-Fuzz
  • 2017-05-08 - OSS-Fuzz: Five months later, and rewarding projects
  • 2016-12-01 - Announcing OSS-Fuzz: Continuous fuzzing for open source software
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    1.1k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    600
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    391
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    321
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    292
  • 6

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    257

Explore all tools

Browse our collection of tools

View all tools →




