

owtf
 owtf/owtf
Modular penetration testing framework integrating multiple tools for automated web application security assessment, aligned with OWASP Testing Guide,…
exploit-frameworkspenetration-testingpenetration-testing-frameworks+2
2.0k
owtf/owtfModular penetration testing framework integrating multiple tools for automated web application security assessment, aligned with OWASP Testing Guide,…
 bahaabdelwahed/killshot
A Penetration Testing Framework, Information gathering tool & Website Vulnerability Scanner
 rek7/fireelf
fireELF - Fileless Linux Malware Framework
 arpsyndicate/puncia
Panthera(P.)uncia - Official CLI utility for Subdomain Center & Exploit Observer.
 justakazh/sicat
Multi-source vulnerability and exploit aggregator with auto-discovery via Nmap and Wappalyzer, searching Exploit-DB, NVD, CVE.org, GitHub, Nuclei,…
 entysec/hatsploit
Modular penetration testing platform that enables you to write, test, and execute exploit code.
 msd0pe-1/cve-maker
CLI tool to search CVEs and exploits from NIST, ExploitDB, and GitHub databases. Supports exploit compilation detection and lists latest critical…
 stevenaldinger/decker
Declarative penetration testing orchestration framework
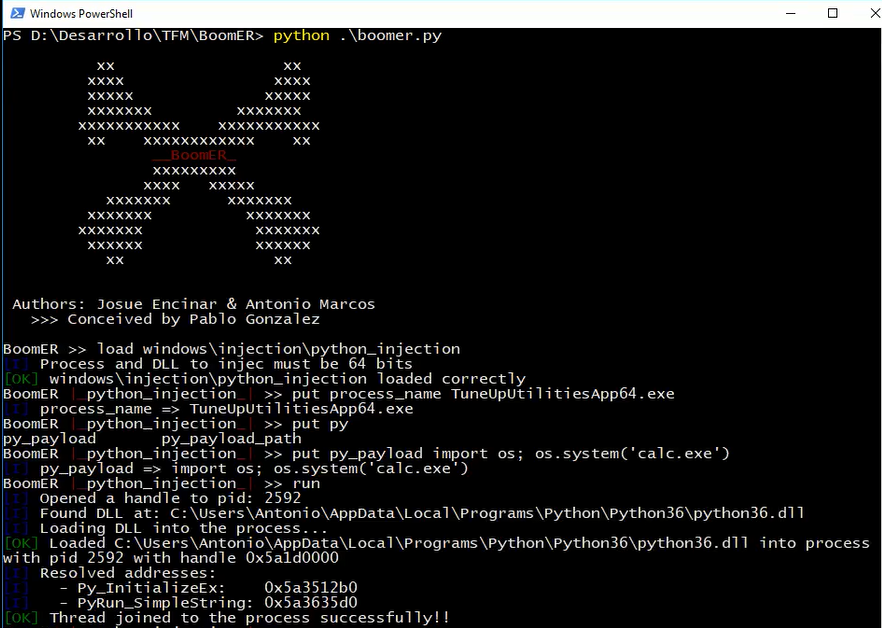 josue87/boomer
Framework for exploiting local vulnerabilities
 joelgmsec/thunderstorm
Modular framework to exploit UPS devices
 wilfred-wulbou/hg532d-rce-exploit
A Remote Code Execution (RCE) exploit for Huawei HG532d based on CVE-2017-17215 vulnerability. Modded from original PoC code from exploit-db.com
 oxdbxkxo/ez-pwnkit
Go implementation of the PwnKit Linux Local Privilege Escalation exploit (CVE-2021-4034)

 d0ubl3g/industrial-security-auditing-framework
ISAF aims to be a framework that provides the necessary tools for the correct security audit of industrial (OT) environments.
 shinthink/pbck-exploit
📤 Mass exploitation framework for CVE-2026-56290 — Page Builder CK Joomla unauthenticated file upload to RCE
 khadafigans/react2shell
React2Shell - CVE-2025-66478 RCE Exploit
 bolivarj/cve-2011-2523
Python exploit for vsftpd 2.3.4 - Backdoor Command Execution
 mauricelambert/cve-2022-47986
CVE-2022-47986: Python, Ruby, NMAP and Metasploit modules to exploit the vulnerability.
 joaoaugustom/wordpress_backup_migration-rce_unauthenticated
This exploit is based on CVE-2023-6553 and was built upon the original exploit by Chocapik, it was added that a direct reverse shell can be obtained.