Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
sandmap — Nmap on steroids. Simple CLI with the ability to run pure Nmap engine, 31 modules with 459 scan profiles. | Kitploit
Tools/GitHubGitHub/trimstray/sandmap
ReconnaissanceVulnerability ScannersNetwork MappingPort ScanningDNS & Subdomain EnumerationInformation GatheringNetwork SecurityPenetration TestingUtilities & Frameworks
GitHubtrimstray/sandmap

sandmap

1.9k246501 year agoReviewed by Kitploit
Share

Nmap on steroids. Simple CLI with the ability to run pure Nmap engine, 31 modules with 459 scan profiles.

View Repository

sandmap

Travis-CI Version Rawsec's CyberSecurity Inventory BlackArch Repository License

Description • How To Use • Command Line • Configuration • Requirements • Other • Contributing • License • Wiki

Master


Description

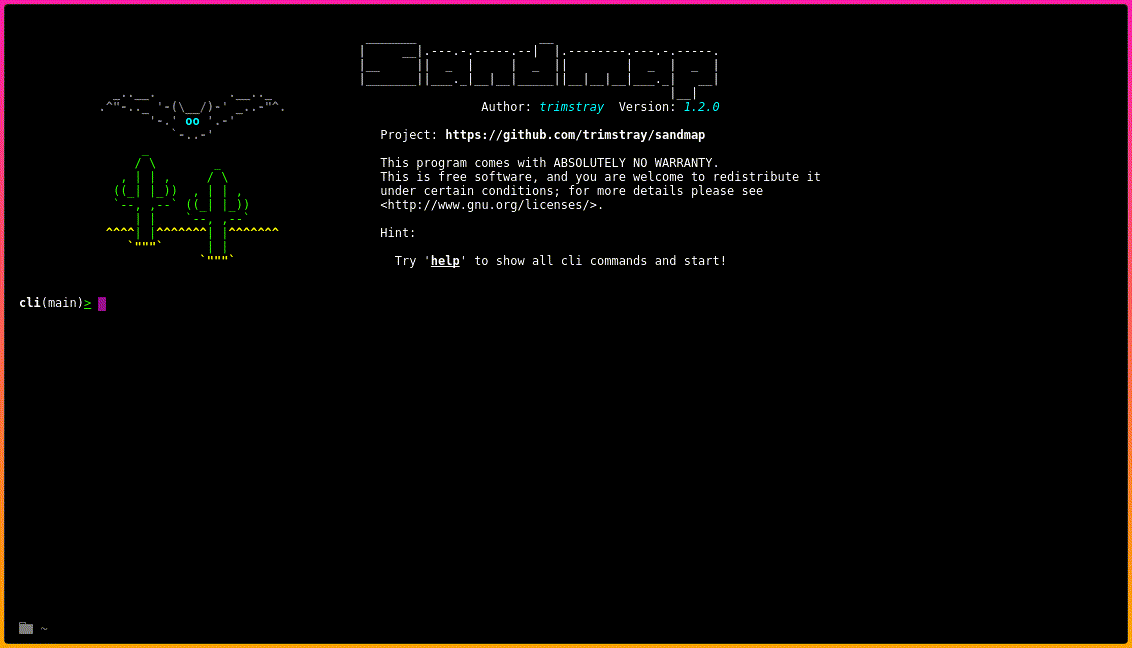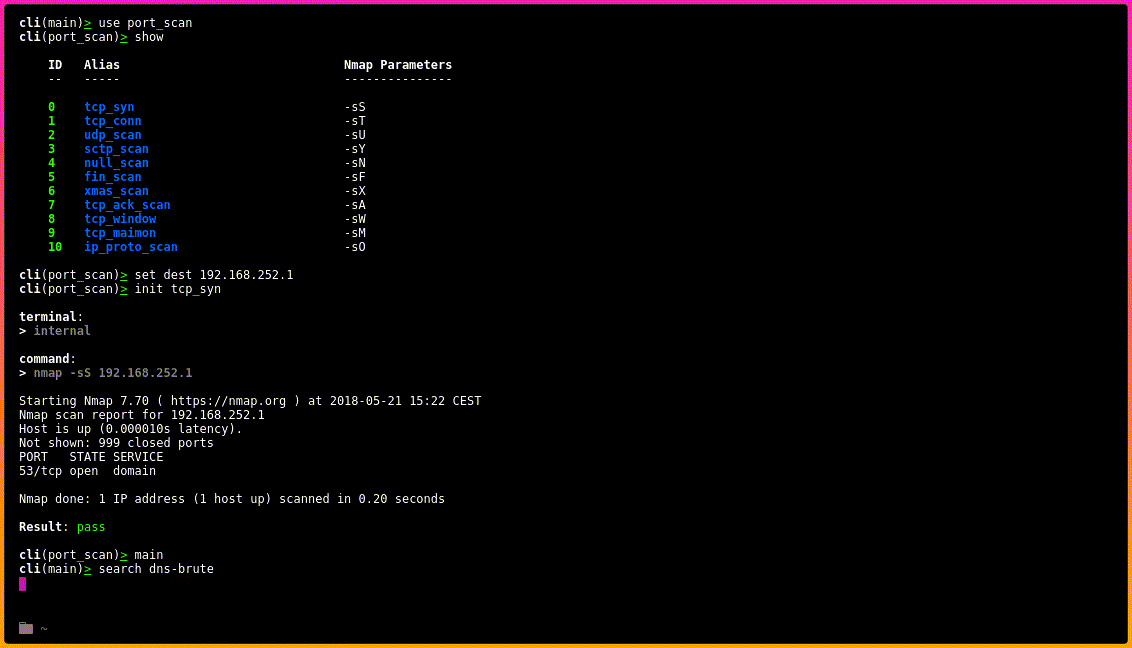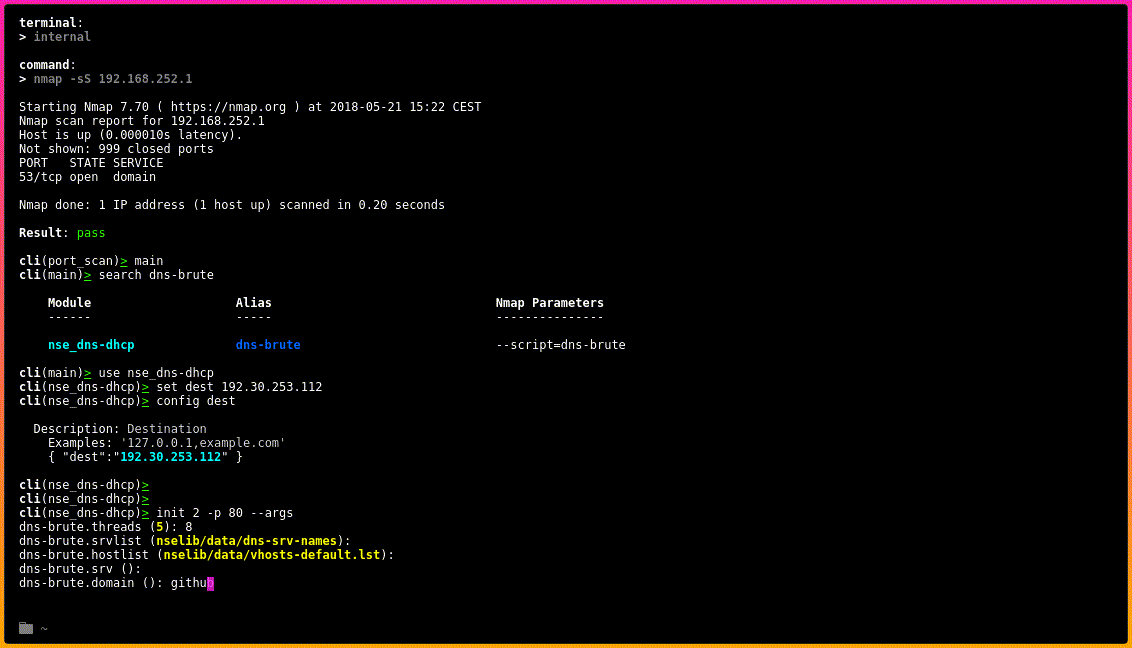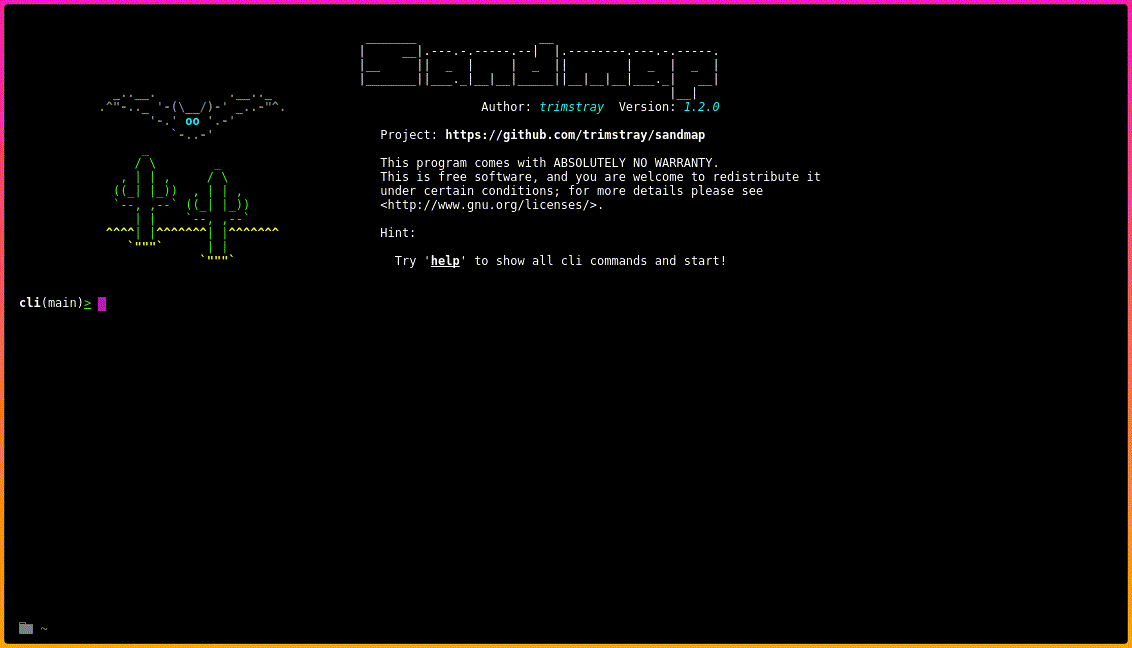
sandmap is a tool supporting network and system reconnaissance using the massive Nmap engine. It provides a user-friendly interface, automates and speeds up scanning and allows you to easily use many advanced scanning techniques.

Key Features

  • simple CLI with the ability to run pure Nmap engine
  • predefined scans included in the modules
  • support Nmap Scripting Engine (NSE) with scripts arguments
  • TOR support (with proxychains)
  • multiple scans at one time
  • at this point: 31 modules with 459 scan profiles

How To Use

It's simple:

# Clone this repository
git clone --recursive https://github.com/trimstray/sandmap

# Go into the repository
cd sandmap

# Install
./setup.sh install

# Run the app
sandmap
  • symlink to bin/sandmap is placed in /usr/local/bin
  • man page is placed in /usr/local/man/man8

Command Line

Before using the sandmap read the Command Line introduction.

Configuration

The etc/main.cfg configuration file has the following structure:

# shellcheck shell=bash

# Specifies the default destination.
# Examples:
#   - dest="127.0.0.1,8.8.8.8"
dest="127.0.0.1"

# Specifies the extended Nmap parameters.
# Examples:
#   - params="--script ssl-ccs-injection -p 443"
params=""

# Specifies the default output type and path.
# Examples:
#   - report="xml"
report=""

# Specifies the TOR connection.
# Examples:
#   - tor="true"
tor=""

# Specifies the terminal type.
# Examples:
#   - terminal="internal"
terminal="internal"

Requirements

sandmap uses external utilities to be installed before running:

  • nmap
  • xterm
  • proxychains

This tool working with:

  • GNU/Linux (testing on Debian and CentOS)
  • Bash (testing on 4.4.19)
  • Nmap (testing on 7.70)

Also you will need root access.

Other

Modules

Available modules: 31 Available scan profiles: 459

If you want to create your own modules, take a look this.

Project architecture

See this.

Contributing

See this.

License

GPLv3 : http://www.gnu.org/licenses/

Free software, Yeah!

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    415
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    343
  • 5

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258

Explore all tools

Browse our collection of tools

View all tools →