Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Winpayloads — Undetectable Windows Payload Generation | Kitploit
Tools/GitHubGitHub/nccgroup/winpayloads
Privilege EscalationExploit FrameworksPayload GenerationPersistence MechanismsLateral MovementShellcodePost-ExploitationPenetration TestingCommand and ControlRed TeamingShellcode GenerationPayload Development
1.6k328597 years agoReviewed by Kitploit
Share
GitHubnccgroup/winpayloads

Winpayloads

Undetectable Windows Payload Generation

View Repository

Winpayloads - Python2.7

Undetectable Windows Payload Generation with extras Running on Python2.7

As usual, Don't upload payloads to any online virus checkers

  • Virus Total Detection - Updated 25/01/2019 - 16/68 Detections
    https://www.virustotal.com/#/file/a921ac7540c93bf03a8ed76158b445b5f8780d8f112405811ebbe820c0e3d5c3/detection

For Fully Undetectable Payloads please use the stager functionality Youtube Video

Docker!

Normal installation is deprecated, Please use docker now.
docker pull charliedean07/winpayloads:latest
docker run -e LANG=C.UTF-8 --net=host -it charliedean07/winpayloads

Features

  • UACBypass - PowerShellEmpire https://github.com/PowerShellEmpire/Empire/raw/master/data/module_source/privesc/Invoke-BypassUAC.ps1 Copyright (c) 2015, Will Schroeder and Justin Warner. All rights reserved.
  • PowerUp - PowerShellEmpire https://raw.githubusercontent.com/PowerShellEmpire/PowerTools/master/PowerUp/PowerUp.ps1 Copyright (c) 2015, Will Schroeder and Justin Warner. All rights reserved.
  • Invoke-Shellcode https://github.com/PowerShellMafia/PowerSploit/blob/master/CodeExecution/Invoke-Shellcode.ps1 Copyright (c) 2012, Matthew Graeber. All rights reserved.
  • Invoke-Mimikatz https://github.com/PowerShellMafia/PowerSploit/blob/master/Exfiltration/Invoke-Mimikatz.ps1 Copyright (c) 2012, Matthew Graeber. All rights reserved.
  • Invoke-EventVwrBypass https://github.com/enigma0x3/Misc-PowerShell-Stuff/blob/master/Invoke-EventVwrBypass.ps1 Matt Nelson (@enigma0x3)
  • Persistence - Adds payload persistence on reboot
  • Psexec Spray - Spray hashes until successful connection and psexec payload on target
  • Upload to local webserver - Easy deployment
  • Powershell stager - allows invoking payloads in memory & more
  • Anti sandboxing techniques
  • Custom shellcode

Check out the Wiki for installation and more!

https://github.com/nccgroup/Winpayloads/wiki
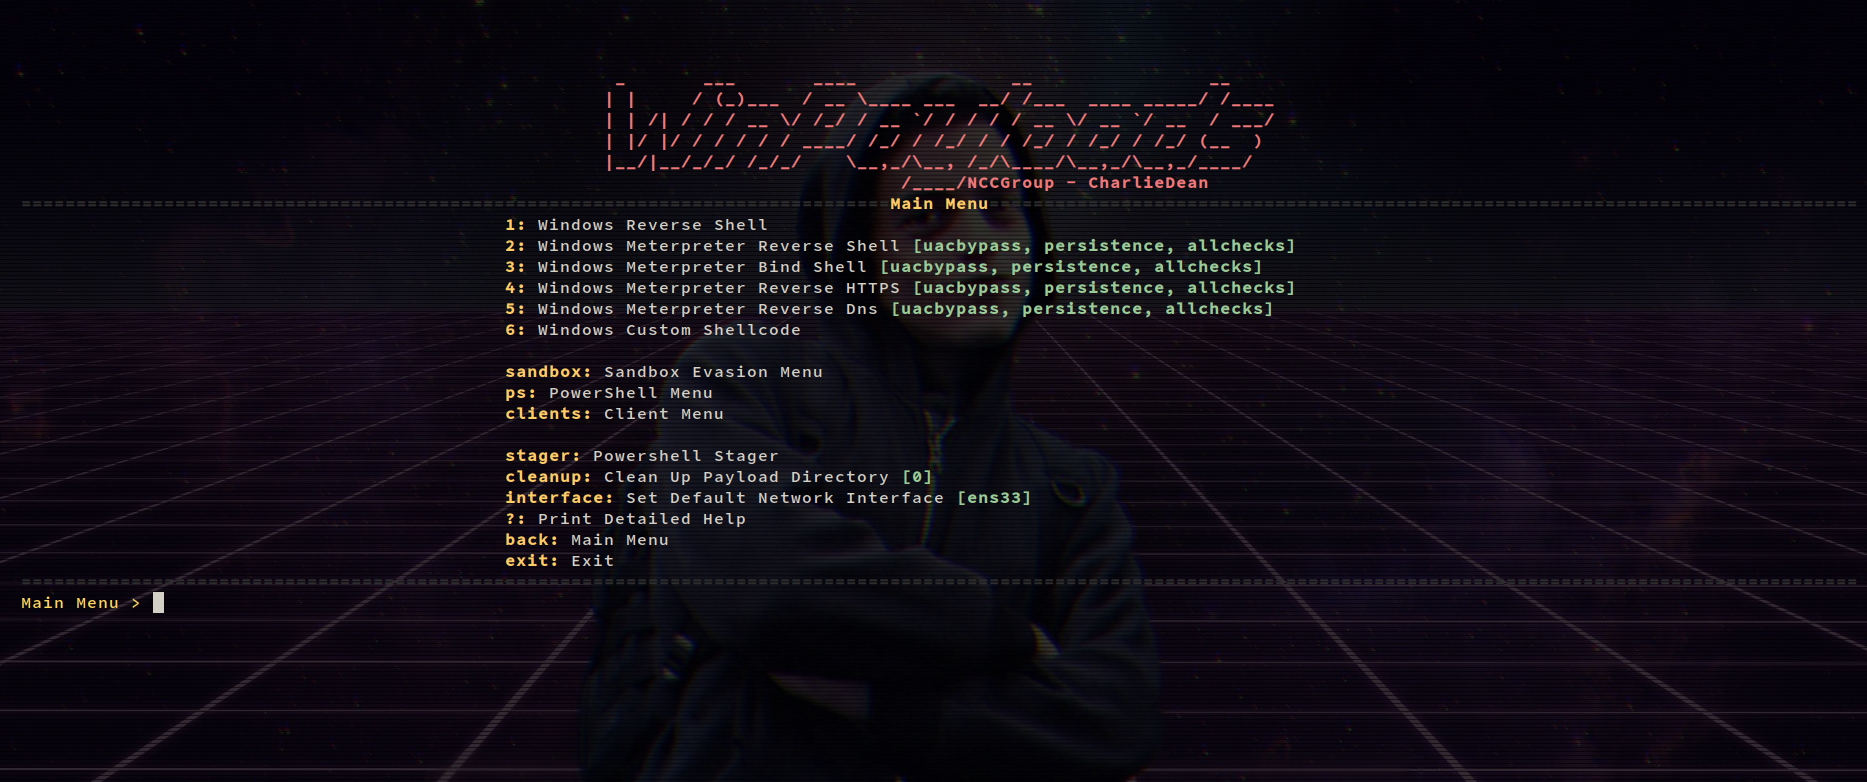
alt tag

Video and Information on Blog (OUTDATED)

https://charliedean.github.io

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    891
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    547
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    369
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    366
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    309
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    282

Explore all tools

Browse our collection of tools

View all tools →





