
 0xkayala/nucleifuzzer
Automated web vulnerability scanner combining URL discovery tools (ParamSpider, waybackurls, gauplus, hakrawler, katana) with Nuclei fuzzing templates to detect XSS, SQLi, SSRF, and Open Redirects.


NucleiFuzzer is an advanced automation tool designed to streamline and optimize web application security testing by integrating a suite of powerful URL discovery and vulnerability scanning tools. It combines ParamSpider, Waybackurls, Katana, Gauplus, and Hakrawler to comprehensively gather and enumerate potential entry points for web applications. Leveraging the power of Nuclei, it scans these endpoints using fuzzing-templates to effectively uncover a wide range of vulnerabilities.
The enhanced NucleiFuzzer is built for speed and accuracy, utilizing advanced URL validation, deduplication with uro, and precise HTTP filtering using httpx. This tool provides security professionals, bug bounty hunters, and web developers with a seamless workflow to detect and address security risks, ensuring robust web application protection.
ParamSpider, Waybackurls, Katana, Gauplus, and Hakrawler) to ensure exhaustive coverage of URLs and parameters.Nuclei with fuzzing-templates to identify critical security issues with precision.uro and httpx for cleaner and more focused scanning.Take advantage of NucleiFuzzer to safeguard your web applications against vulnerabilities and attacks with an enhanced, efficient, and reliable security testing solution!
Note: Nuclei + Paramspider + waybackurls + gauplus + hakrawler + katana + Fuzzing Templates = NucleiFuzzer
Important: Make sure the tools Nuclei, Paramspider, waybackurls, gauplus, hakrawler, katana, httpx & uro are installed on your machine and executing correctly to use the NucleiFuzzer without any issues.
git clone https://github.com/projectdiscovery/nuclei.gitgit clone https://github.com/0xKayala/ParamSpider.gitgit clone https://github.com/tomnomnom/waybackurls.gitgit clone https://github.com/bp0lr/gauplus.gitgit clone https://github.com/hakluke/hakrawler.gitgit clone https://github.com/projectdiscovery/katana.gitgit clone https://github.com/projectdiscovery/httpx.githttps://github.com/s0md3v/uro.gitFuzzing Templates git clone https://github.com/projectdiscovery/nuclei-templates.git

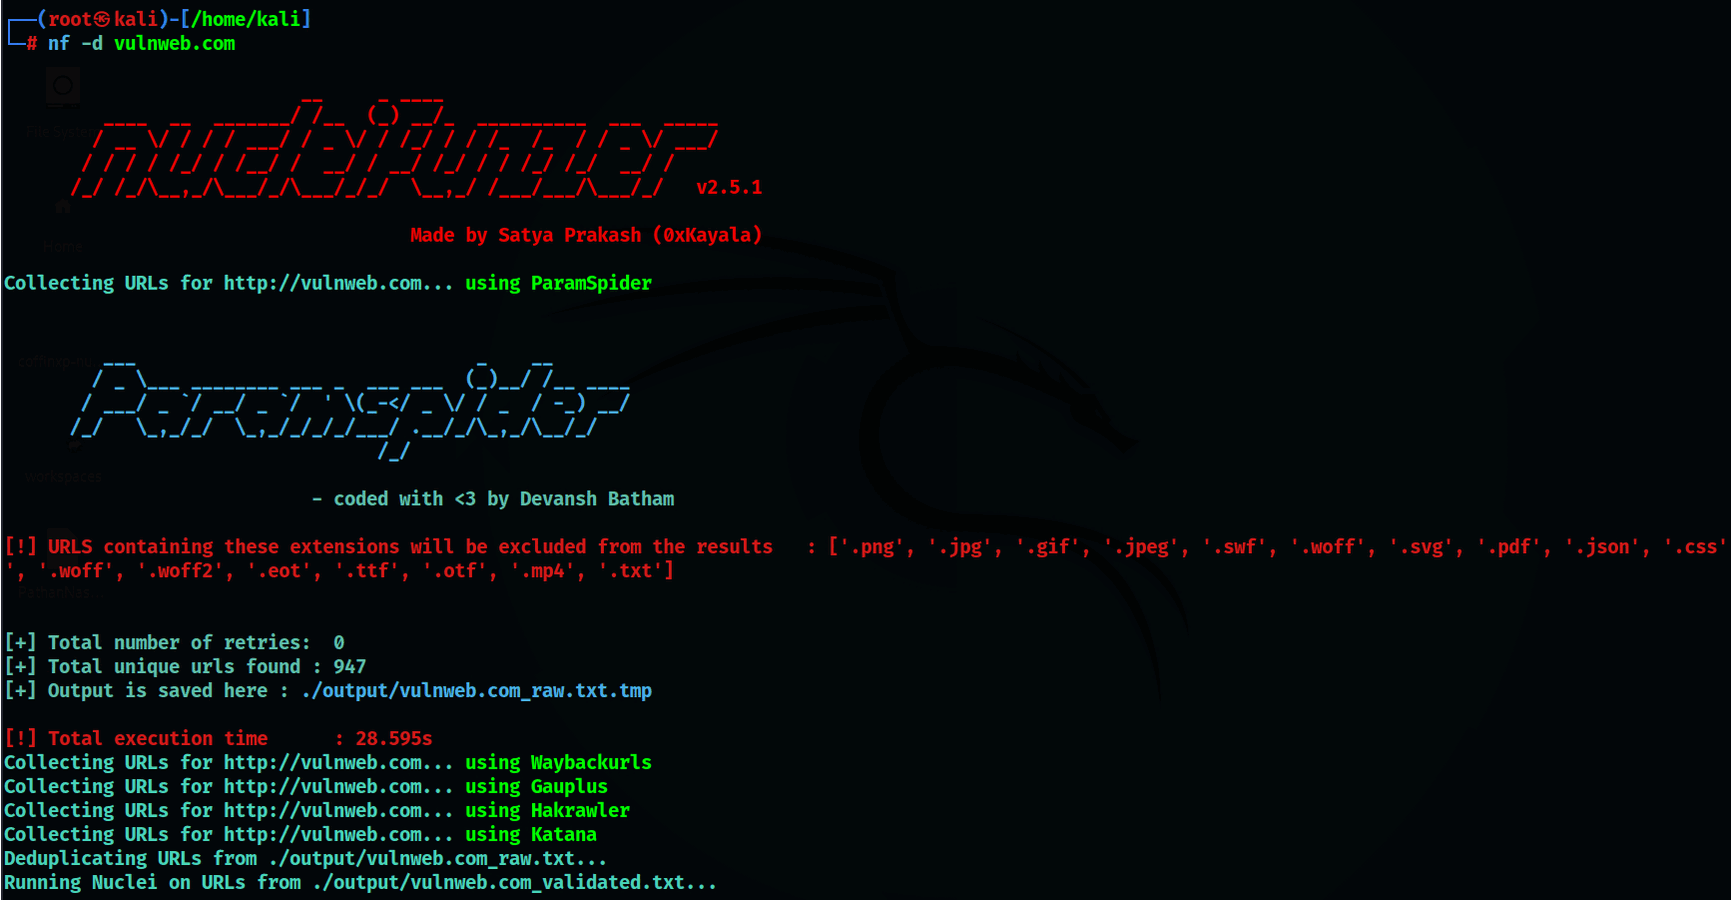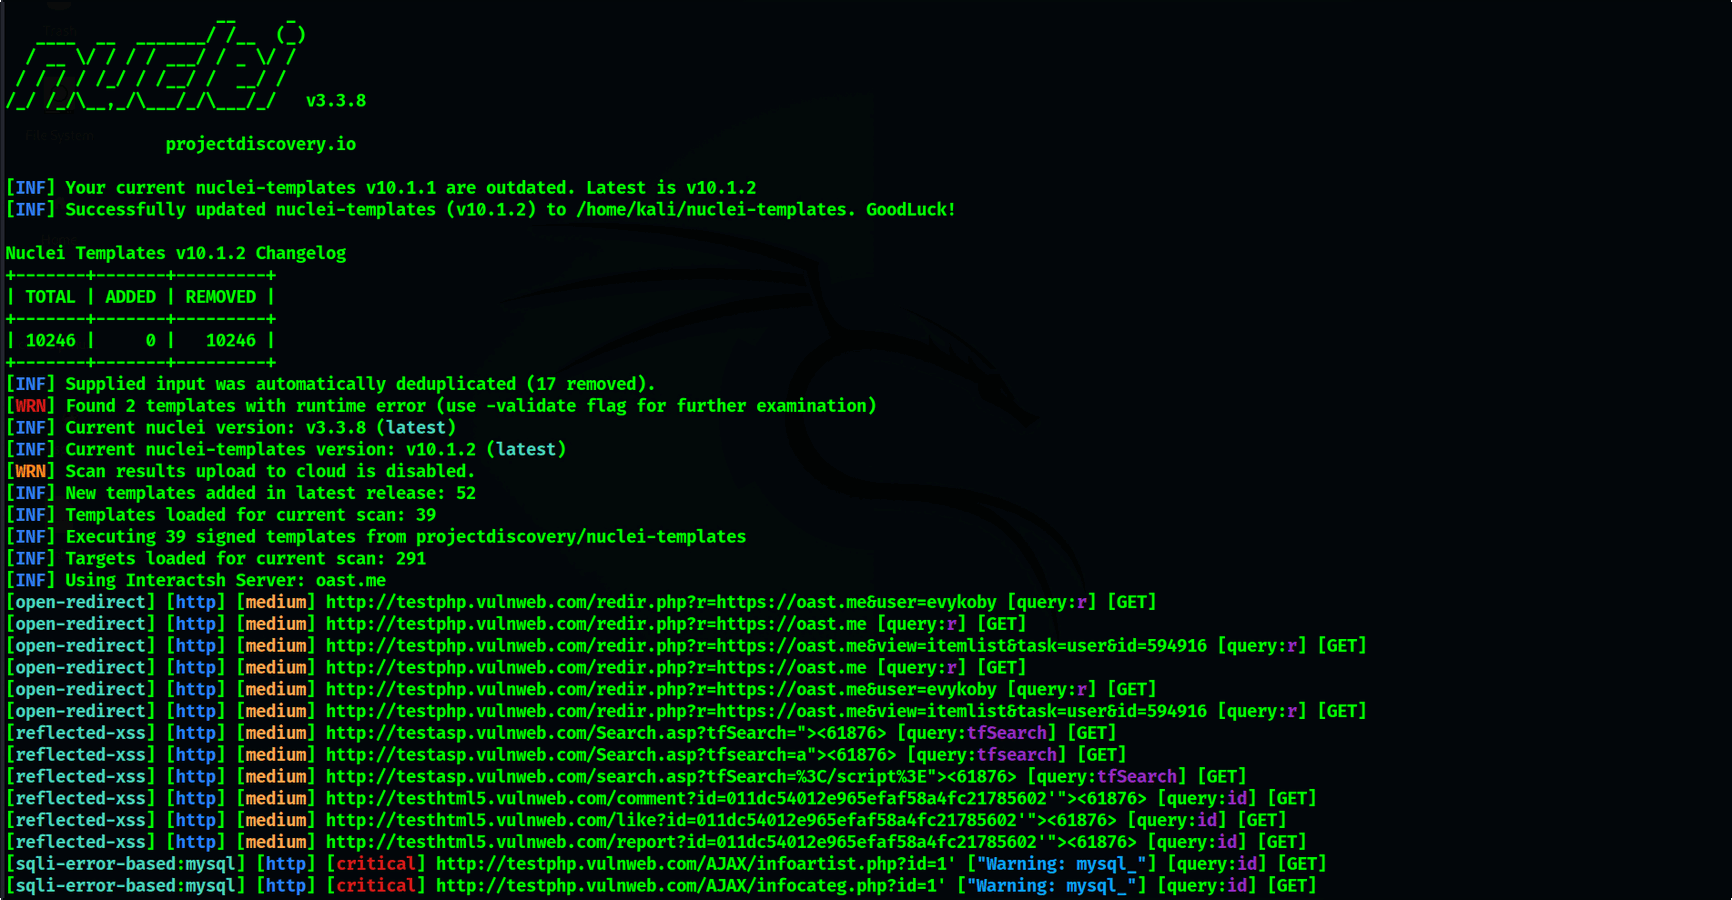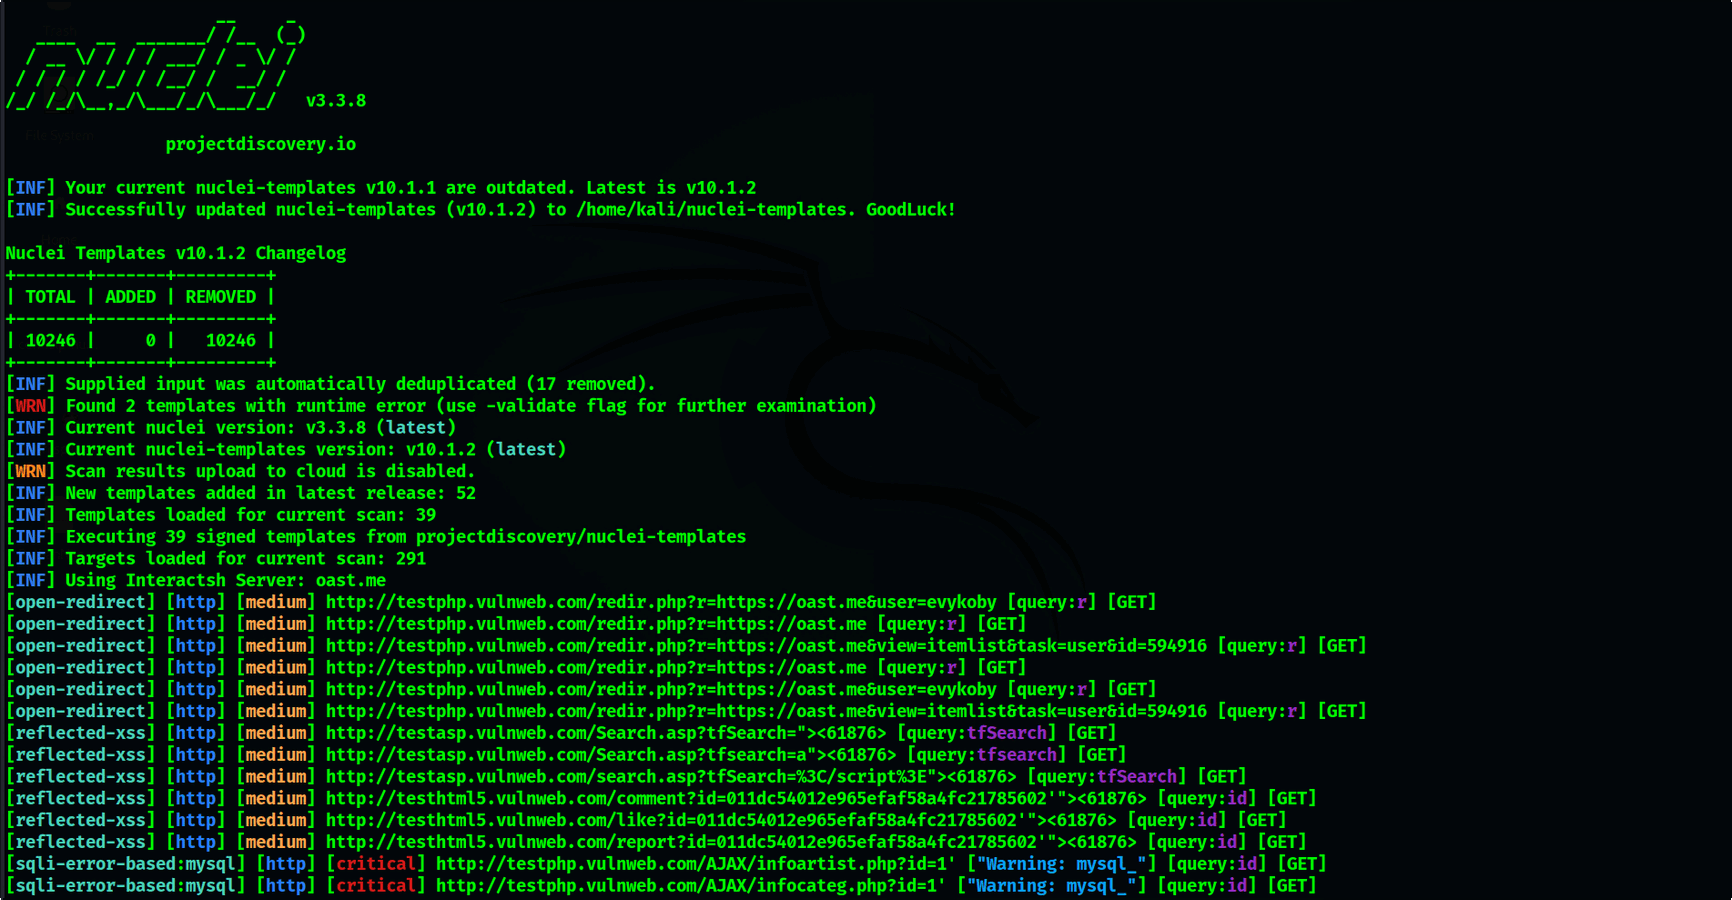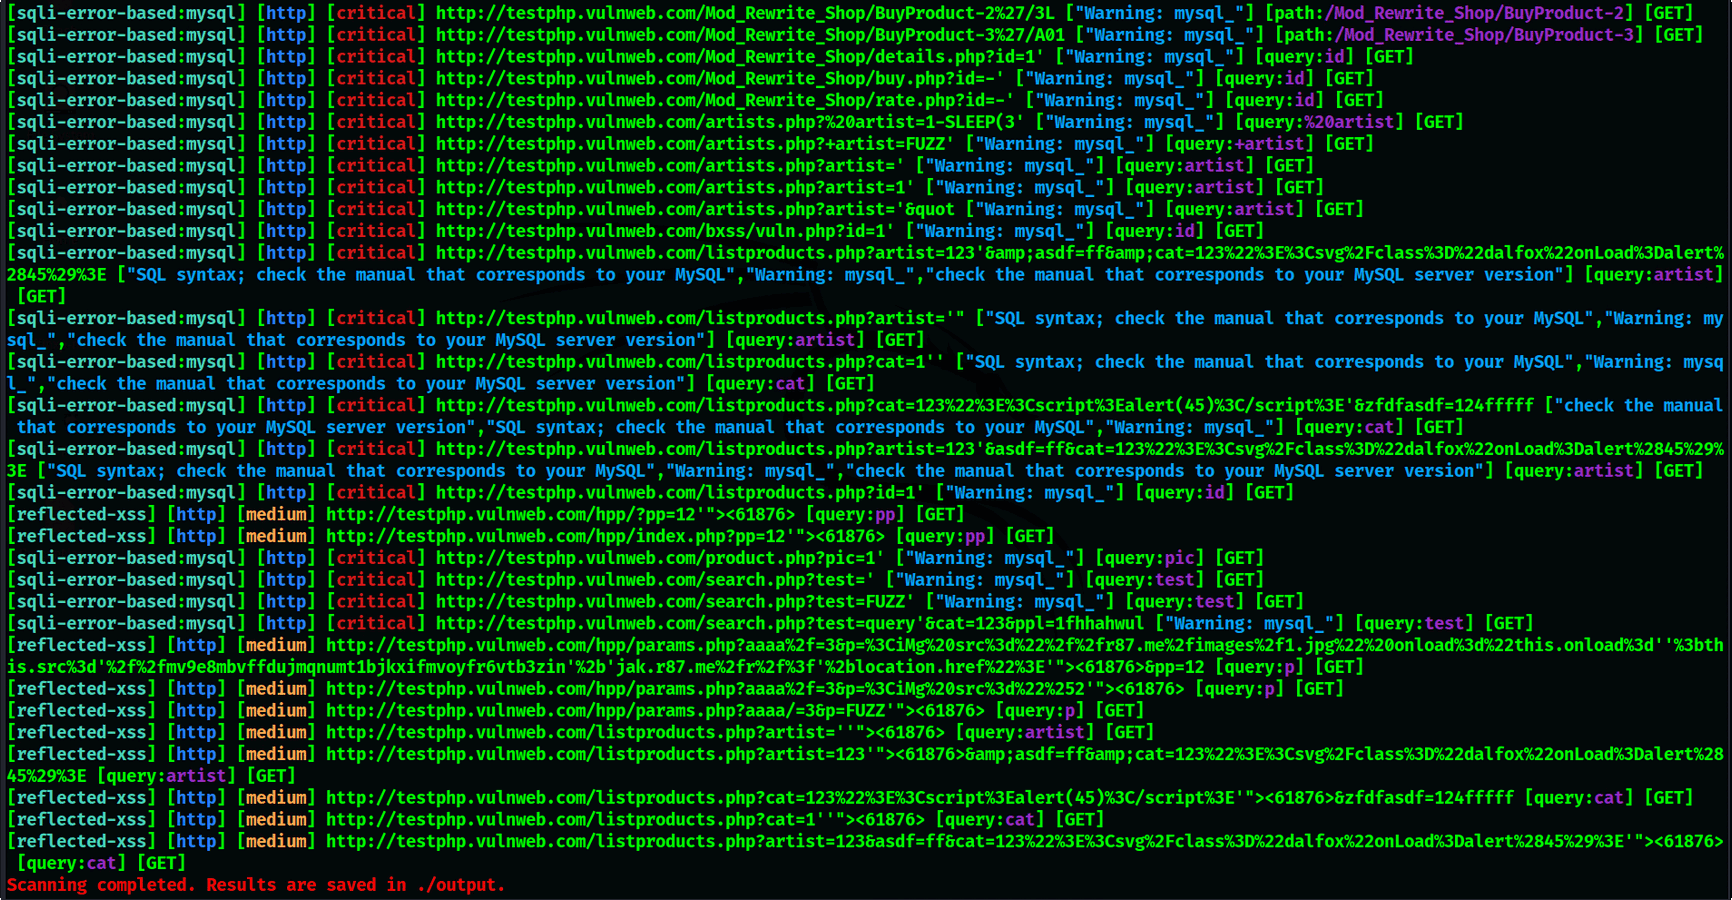
nf -h
This will display help for the tool. Here are the options it supports.
NucleiFuzzer: A Powerful Automation Tool for Web Vulnerability Scanning

Usage: /usr/bin/nf [options]

Options:
  -h, --help              Display help information
  -d, --domain <domain>   Single domain to scan for vulnerabilities
  -f, --file <filename>   File containing multiple domains/URLs to scan
  -o, --output <folder>   Specify output folder for scan results (default: ./output)
To install NucleiFuzzer, follow these steps:
git clone https://github.com/0xKayala/NucleiFuzzer.git && cd NucleiFuzzer && sudo chmod +x install.sh && ./install.sh && (command -v nf &> /dev/null && nf -h || echo "Installation failed: Command 'nf' not found. Please check for errors during installation.") && cd .. || echo "Failed to clone or navigate to NucleiFuzzer repository. Please check your setup."
Here are a few examples of how to use NucleiFuzzer:
Run NucleiFuzzer on a single domain:
nf -d example.com
Run NucleiFuzzer on multiple domains from a file:
nf -f file.txt
For a Practical Demonstration of the NucleiFuzzer tool see the below video 👇

Contributions are welcome! If you'd like to contribute to NucleiFuzzer, please follow these steps:
Made by
Satya Prakash | 0xKayala \
A Security Researcher and Bug Hunter \






