Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
45 results
TrollDump preview

TrollDump

GitHubcybersectroll/trolldump

Injects x64 managed DLLs into GUI processes via SetWindowsHook, with a modular C# payload runner and LSASS dump POC for red-team/offensive Windows…

payload-developmentpost-exploitationprivilege-escalation+1
84
2 years ago
ExtensionHijack preview

ExtensionHijack

GitHubal1ex/extensionhijack

ExtensionHijack

persistence-mechanismspost-exploitationred-teaming
25 years ago
NTDLLReflection preview

NTDLLReflection

GitHubsaadahla/ntdllreflection

Bypass Userland EDR hooks by Loading Reflective Ntdll in memory from a remote server based on Windows ReleaseID to avoid opening a handle to ntdll ,…
adversarial-attackids-ips-evasionpost-exploitation+1
3063 years ago
CVE-2026-2636_PoC preview

CVE-2026-2636_PoC

GitHuboxfemale/cve-2026-2636_poc

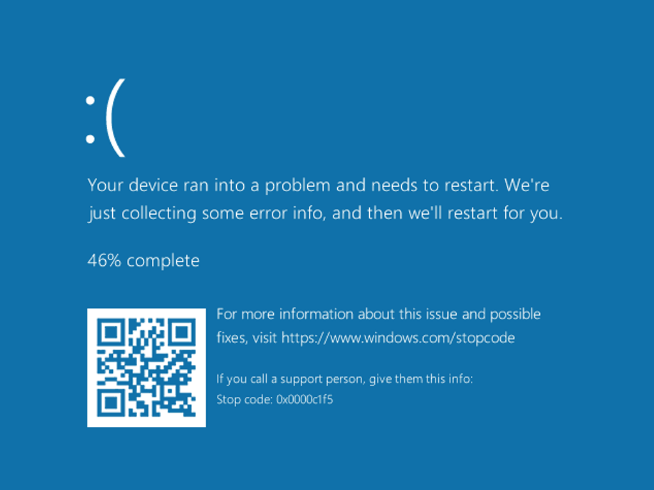
Proof-of-concept for CVE-2026-2636, a Windows CLFS.sys vulnerability causing BSoD via ReadFile on CreateLogFile handle, enabling unprivileged denial…

exploitationexploit-frameworksvulnerability-analysis
156 months ago
CVE-2025-62215_Windows_Kernel_PE preview

CVE-2025-62215_Windows_Kernel_PE

GitHubabrewer251/cve-2025-62215_windows_kernel_pe

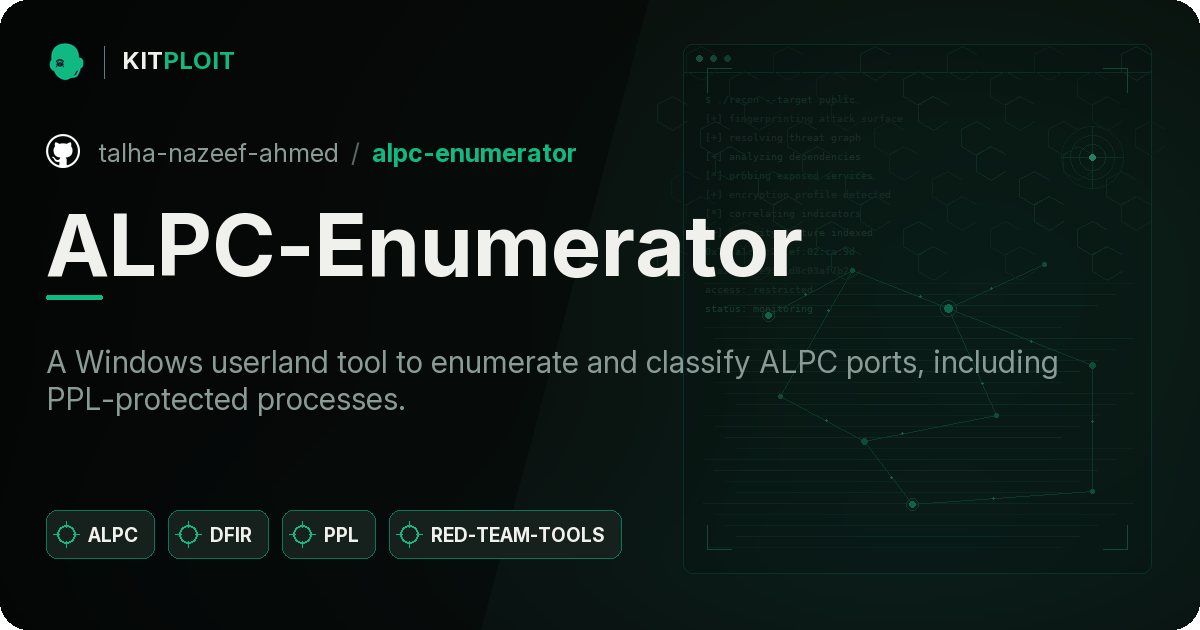
This PoC demonstrates a race condition in the Windows kernel leading to a double-free vulnerability, allowing local privilege escalation to SYSTEM.…
binary-exploitationctfeducation+3
2010 months ago
ALPC-Enumerator preview

ALPC-Enumerator

GitHubtalha-nazeef-ahmed/alpc-enumerator

A Windows userland tool to enumerate and classify ALPC ports, including PPL-protected processes.
digital-forensicsinformation-gatheringmalware-analysis+4
291 month ago
LogMeInPoCHandleDup preview

LogMeInPoCHandleDup

GitHubalfarom256/logmeinpochandledup

Exploit for a LogMeIn/GoTo Windows kernel driver race condition that duplicates SYSTEM handles, enabling thread-token impersonation and local…

binary-exploitationexploitationprivilege-escalation+2
642 years ago
Villain preview

Villain

GitHubt3l3machus/villain

Villain is a high level stage 0/1 C2 framework that can handle multiple reverse TCP & HoaxShell-based shells, enhance their functionality with…
command-and-controlexploit-frameworkspayload-generation+4
4.5k1 year ago
DuplicateDump preview

DuplicateDump

GitHubhagrid29/duplicatedump

Dumping LSASS with a duplicated handle from custom LSA plugin
post-exploitationprivilege-escalationred-teaming
2064 years ago
CVE-2025-2783 preview

CVE-2025-2783

GitHubbytereaper77/cve-2025-2783

This project is a research-oriented and educational simulation designed to demonstrate the concept of a sandbox escape vulnerability within Google…
binary-exploitationeducationexploitation+1
81 year ago
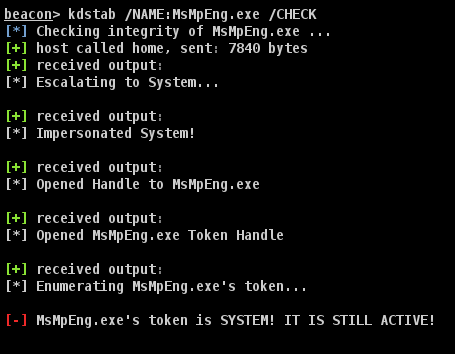
KDStab preview

KDStab

GitHuboctoberfest7/kdstab

BOF combination of KillDefender and Backstab
defensive-toolsexploit-frameworkspayload-development+3
1703 years ago
cookie-monster preview

cookie-monster

GitHubkingofthenops/cookie-monster

BOF-based tool to extract browser cookies and credentials from Chrome, Edge, and Firefox via handle duplication and fileless download, with offline…
data-exfiltrationpenetration-testingpost-exploitation+1
5742 months ago
Docker-Security preview

Docker-Security

GitHubowasp/docker-security

Getting a handle on container security
cloud-infrastructure-securitycloud-securityconfiguration-auditing+6
6902 years ago
CallStackSpoofer preview

CallStackSpoofer

GitHubwithsecurelabs/callstackspoofer

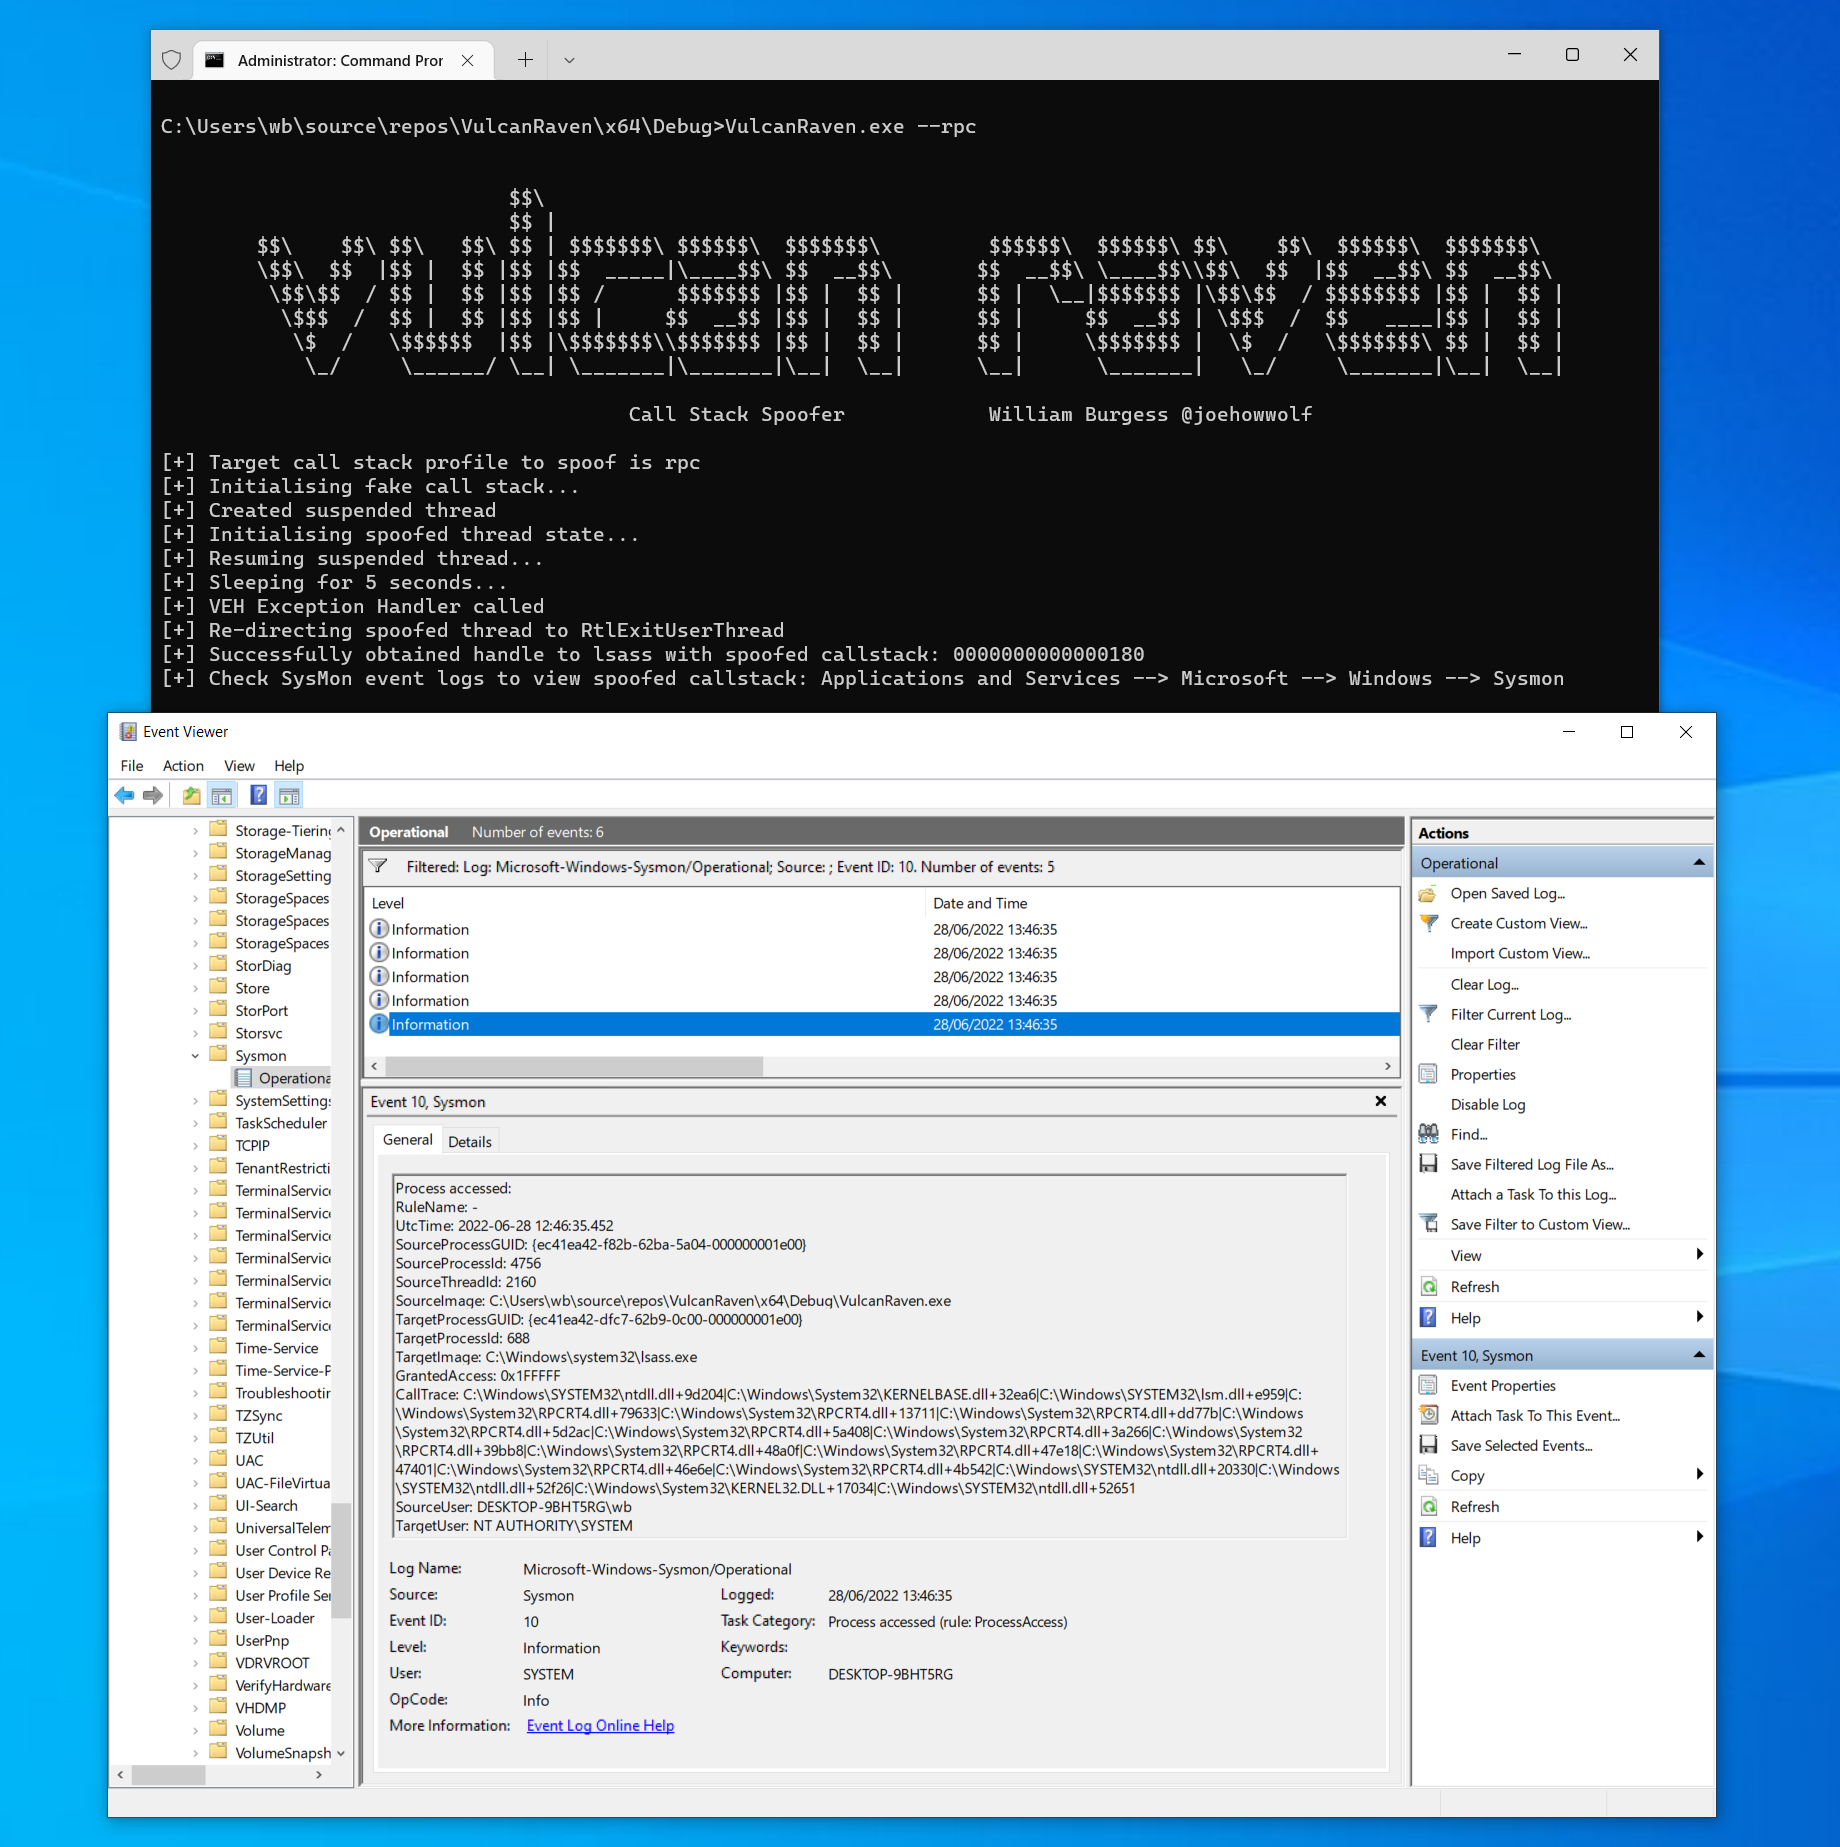
A PoC implementation for spoofing arbitrary call stacks when making sys calls (e.g. grabbing a handle via NtOpenProcess)
adversarial-attackids-ips-evasionpost-exploitation+1
5981 year ago
BlockOpenHandle preview

BlockOpenHandle

GitHubsaadahla/blockopenhandle

Block any Process to open HANDLE to your process , only SYTEM is allowed to open handle to your process ,with that you can avoid remote memory…
authentication-authorizationdefensive-toolsprivacy
1703 years ago
CVE-2026-65343 preview

CVE-2026-65343

GitHubbytev0rtex/cve-2026-65343

Proof-of-concept for CVE-2026-65343, an out-of-bounds read in AppleKeyStore that leaks kernel pointers to defeat KASLR on iOS 26.6. Includes ACM…
binary-exploitationexploitationios-security+3
7419 days ago
CredsHunter preview

CredsHunter

GitHubblacksnufkin/credshunter

PoC for CVE-2026-3609 - XIGNCODE3 xhunter1.sys handle leak enabling PPL bypass and LSASS dumping
binary-exploitationexploitationmemory-forensics+2
374 months ago
CVE-2017-9769 preview

CVE-2017-9769

GitHubkkent030315/cve-2017-9769

A specially crafted IOCTL can be issued to the rzpnk.sys driver in Razer Synapse 2.20.15.1104 that is forwarded to ZwOpenProcess allowing a handle to…

binary-exploitationexploitationprivilege-escalation+1
135 years ago
Previous123Next