
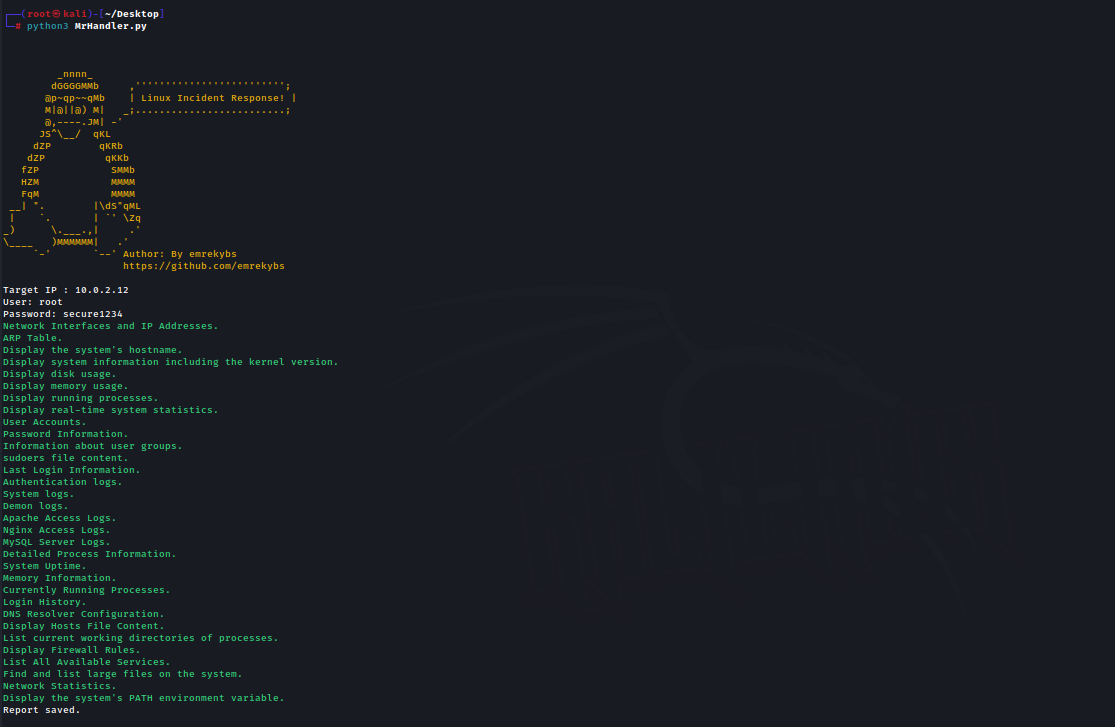
MrHandler
 emrekybs/mrhandler
SSH-based Linux incident response tool that executes diagnostic commands to collect network configs, logs, user accounts, and processes, then…
digital-forensicsforensicsincident-response+1
86
emrekybs/mrhandlerSSH-based Linux incident response tool that executes diagnostic commands to collect network configs, logs, user accounts, and processes, then…
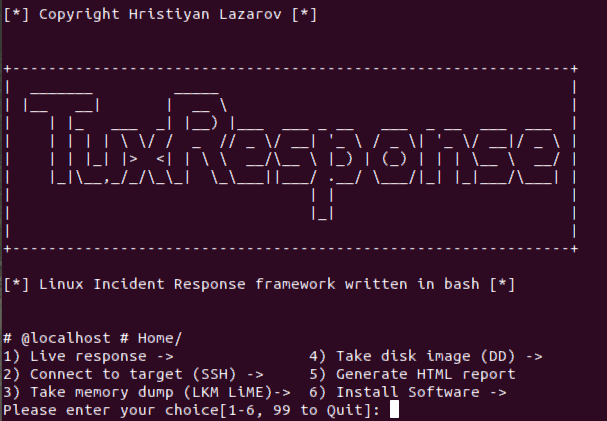 la3ar0v/tuxresponse
Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.
 sobri3195/pegasus-malware-scan
Multi-layered malware scanner combining hash-based verification, behavioral analysis, and sandbox execution for threat detection, incident response,…
 withsecurelabs/linuxcatscale
Incident Response collection and processing scripts with automated reporting scripts
 volatilityfoundation/volatility3
Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…
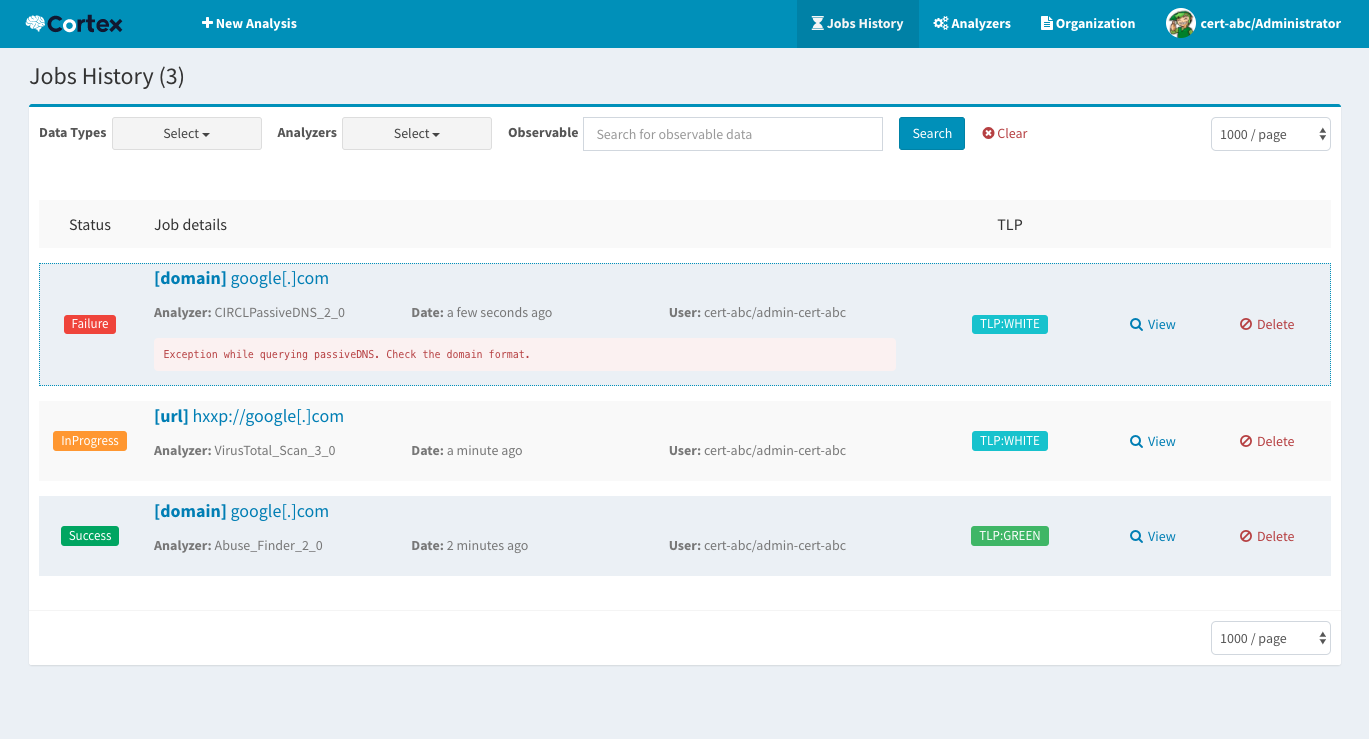 thehive-project/cortex
Cortex: a Powerful Observable Analysis and Active Response Engine
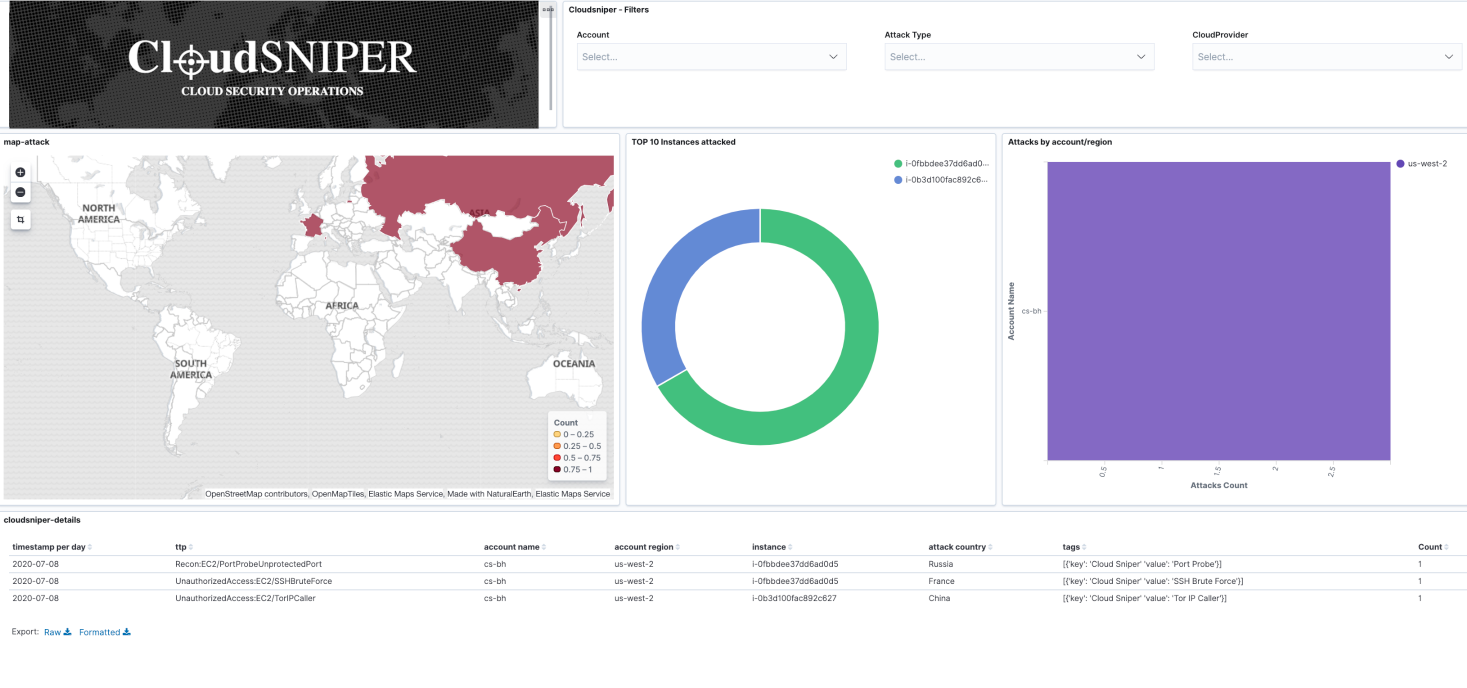 cloud-sniper/cloud-sniper
Detection-as-code platform that automates cloud security incident response by correlating artifacts, analyzing IOCs, and orchestrating…
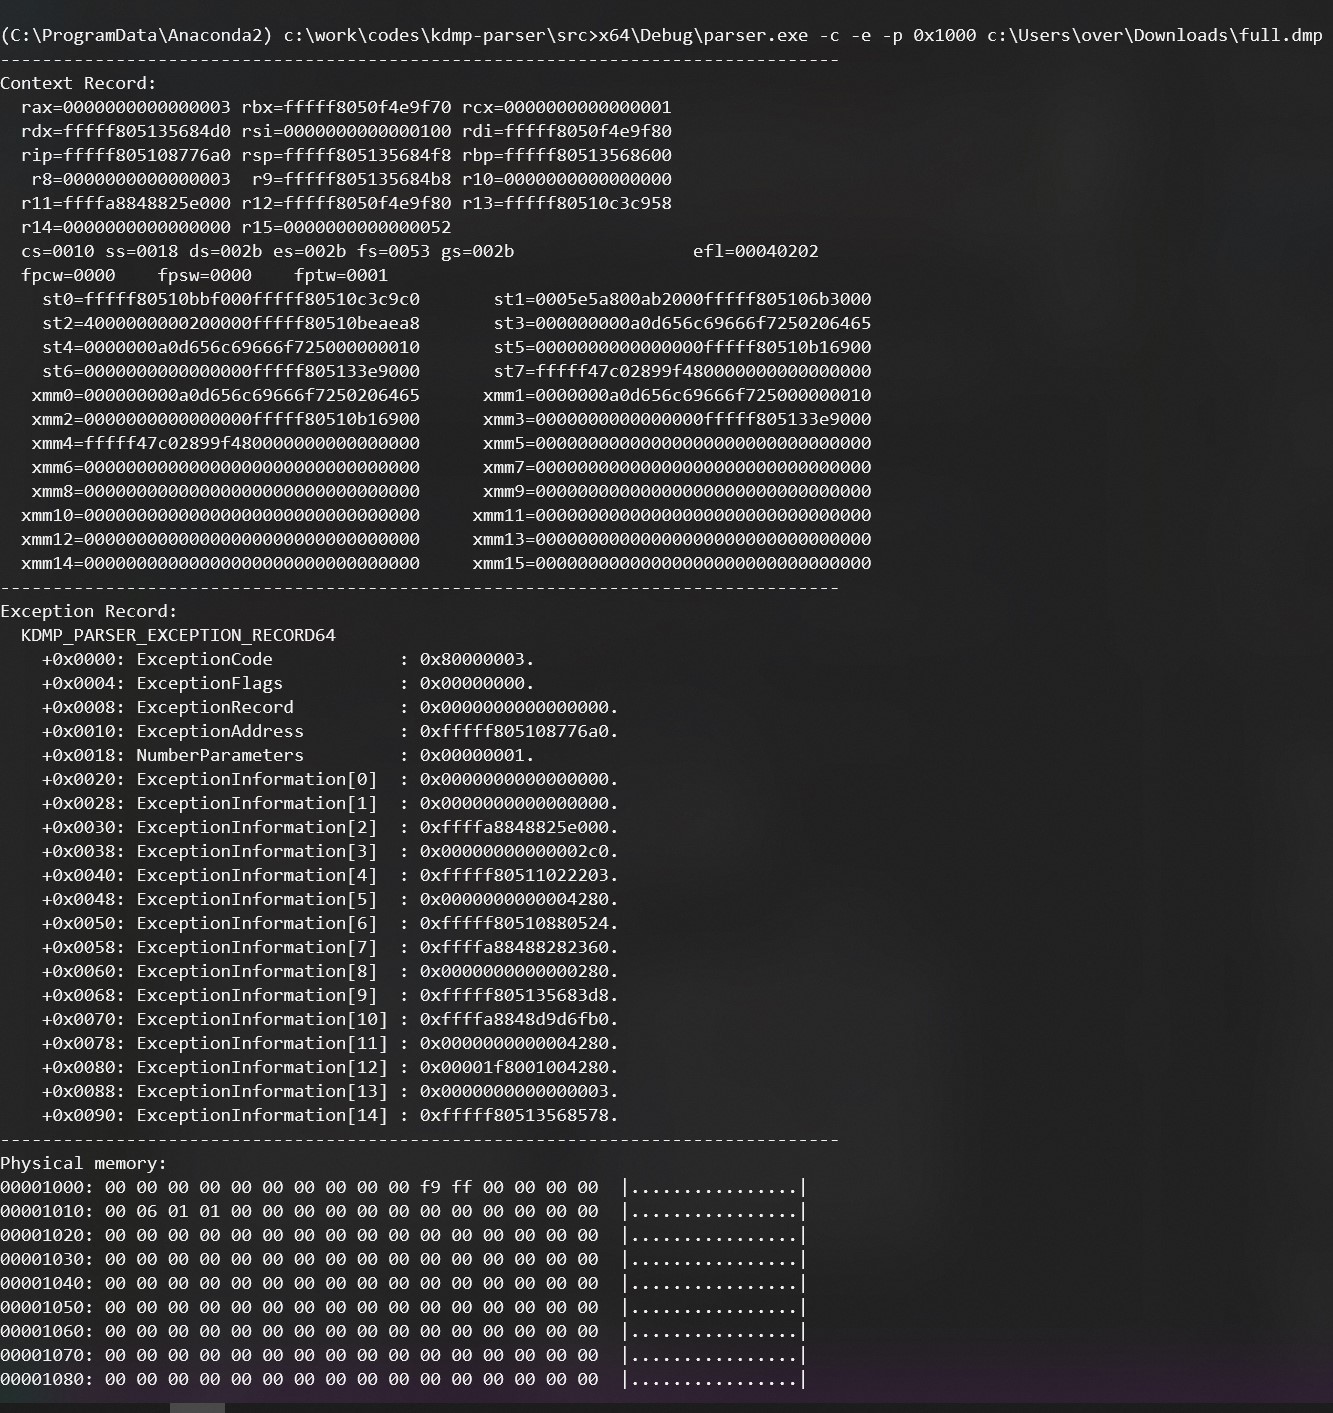 0vercl0k/kdmp-parser
A Windows kernel dump C++ parser library with Python 3 bindings.
 akefallonitis/larac2shell
Cross-platform interactive shell for Microsoft Defender for Endpoint Live Response
 sonitbahl/sshintel
Self-contained SSH honeypot for capturing attacker interactions and turning them into structured security intelligence.
 intrudify/mini-shai-hulud-scanner
Scanner for the Mini Shai-Hulud npm/PyPI supply chain worm (NHS CC-4781 · CVE-2026-45321). Detects gh-token-monitor persistence, payload artefacts,…
 techgaun/cve-2025-55182-scanner
Python-based scanner for CVE-2025-55182 indicators of compromise. Checks filesystem paths, processes, systemd services, cron persistence, and…
 intezer/linux-explorer
Easy-to-use live forensics toolbox for Linux endpoints
 msuhanov/easy_triage
Scripts to triage compromised systems (Linux, ESXi, FreeBSD/NetScaler)
 fox-it/log4j-finder
Find vulnerable Log4j2 versions on disk and also inside Java Archive Files (Log4Shell CVE-2021-44228, CVE-2021-45046, CVE-2021-45105)
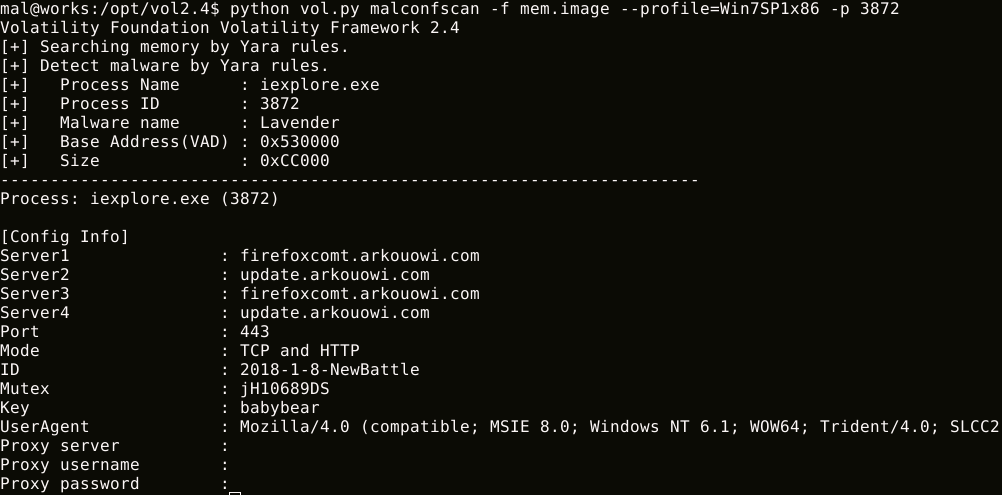 jpcertcc/malconfscan
Volatility plugin for extracts configuration data of known malware
 andreafortuna/autotimeliner
Automagically extract forensic timeline from volatile memory dump