
 liamg/dismember
🔪 Scan memory for secrets and more. Maybe eventually a full /proc toolkit.

Dismember is a command-line toolkit for Linux that can be used to scan the memory of all processes (or particular ones) for common secrets and custom regular expressions, among other things.
It will eventually become a full /proc toolkit.
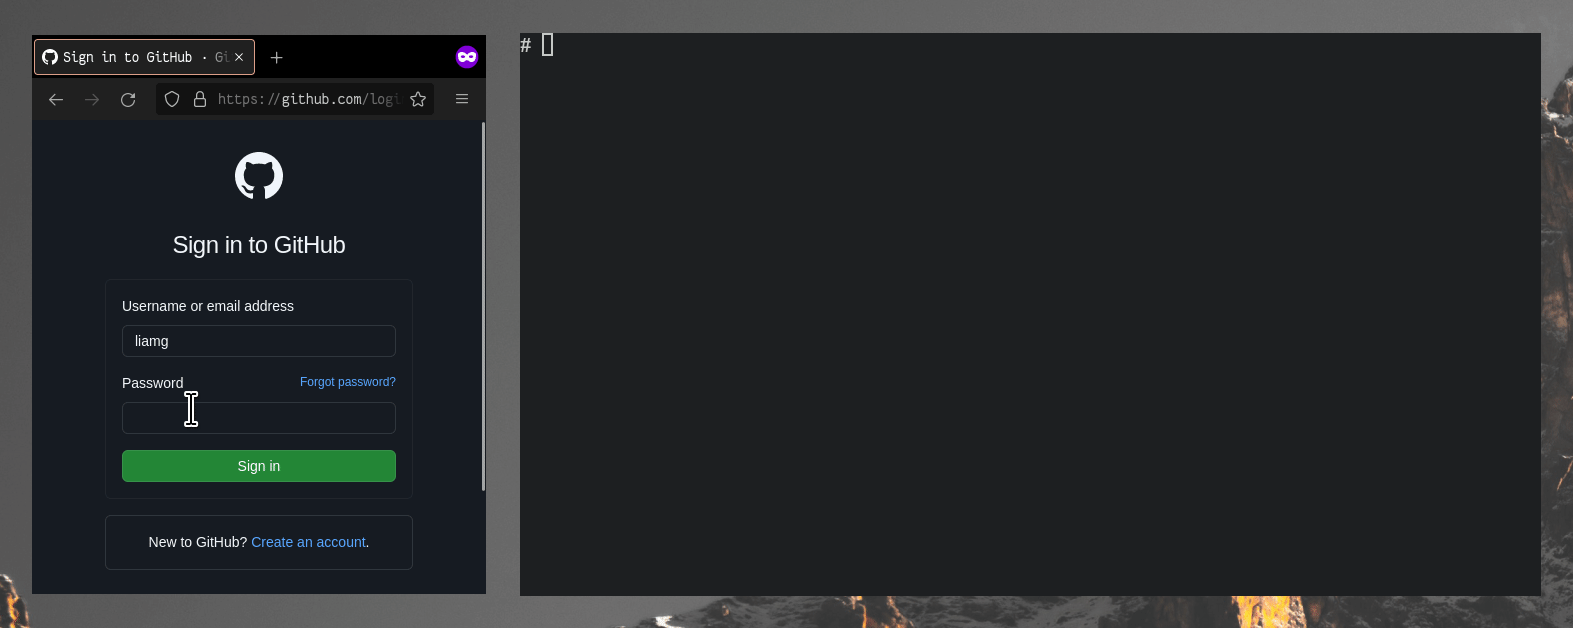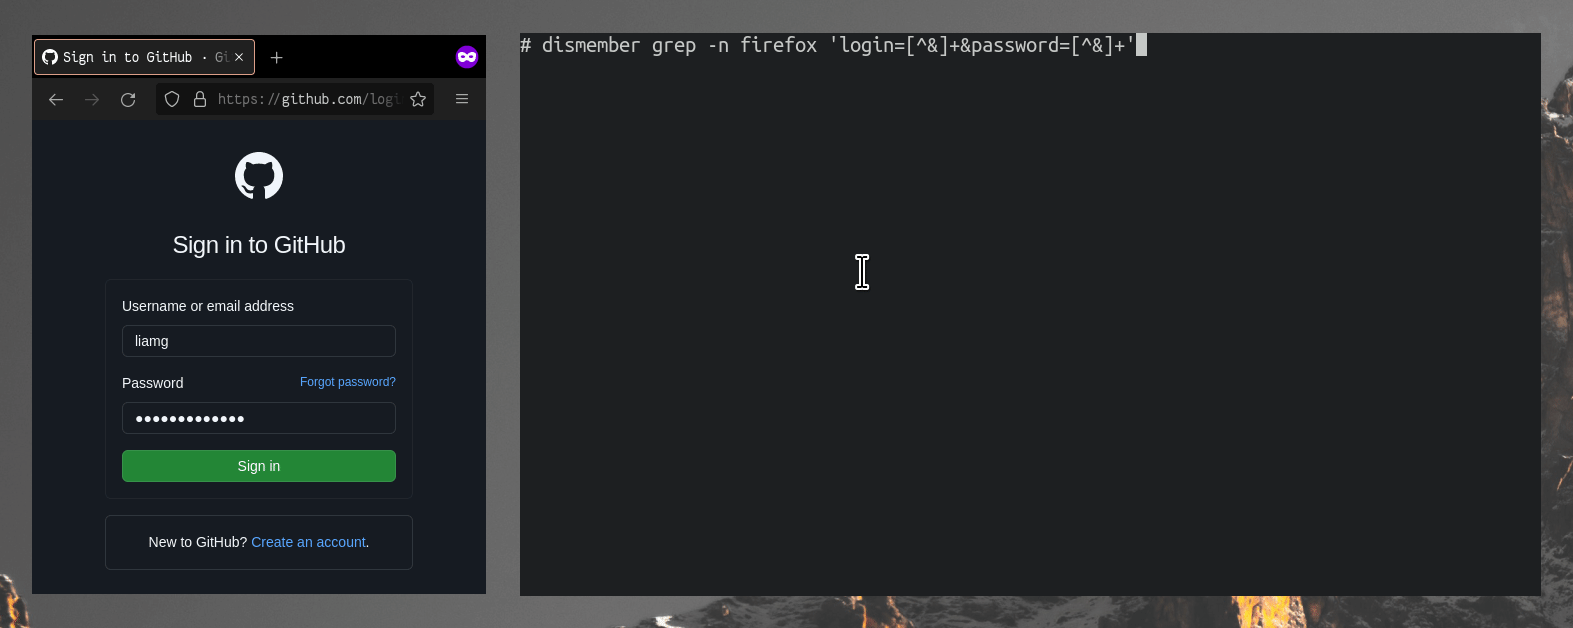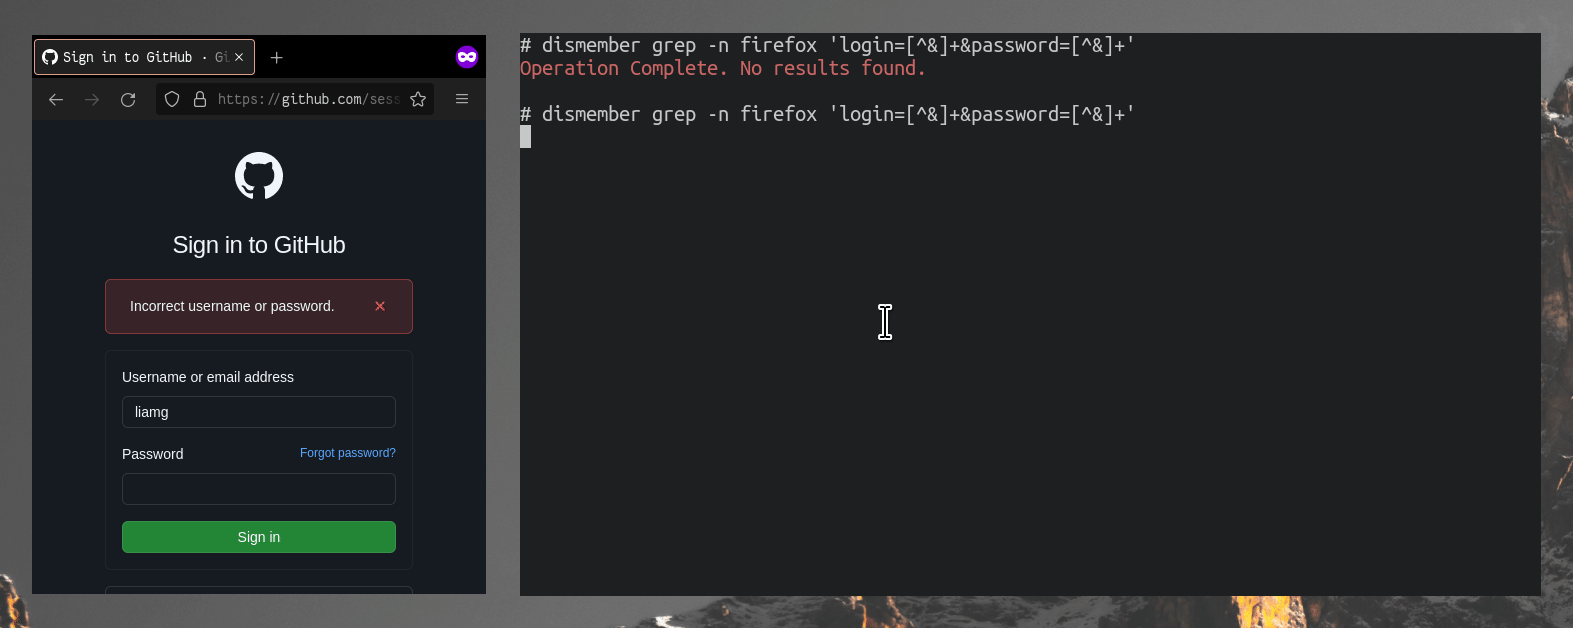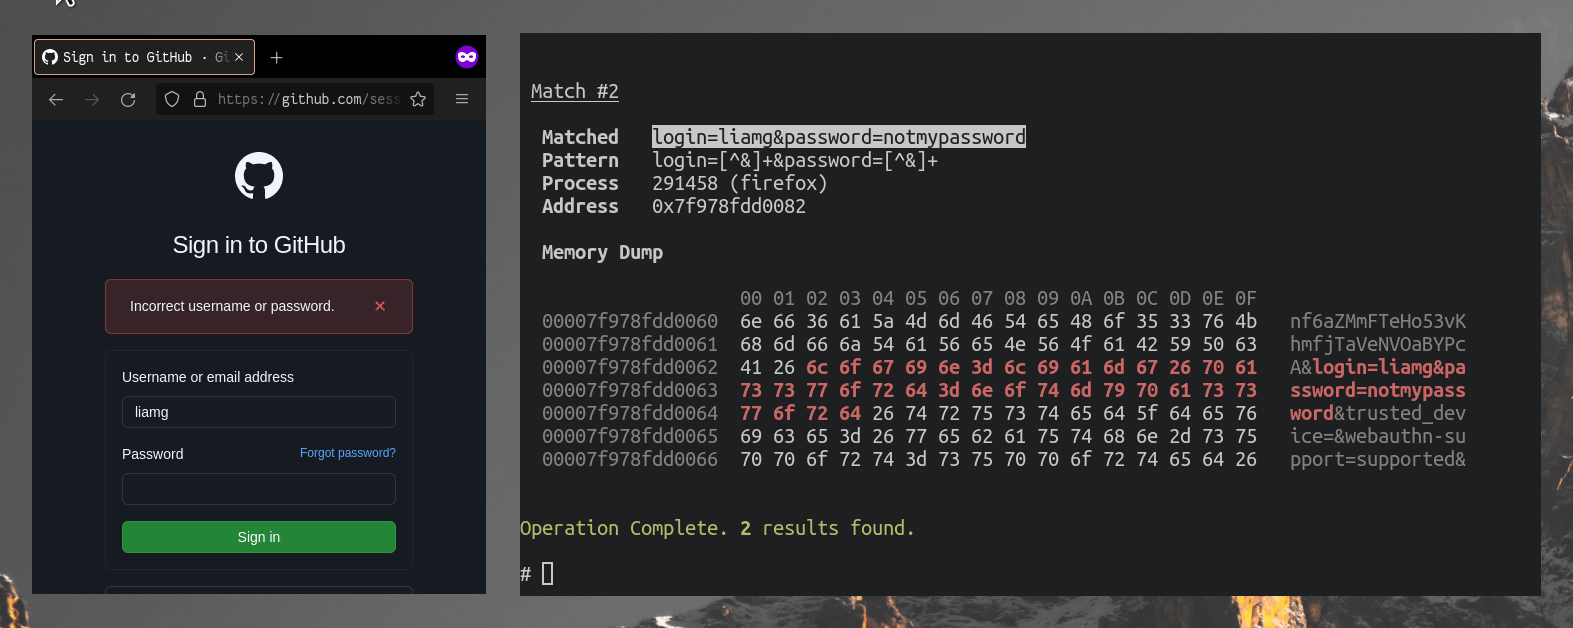
Using the grep command, it can match a regular expression across all memory for all (accessible) processes. This could be used to find sensitive data in memory, identify a process by something included in its memory, or to interrogate a processes' memory for interesting information.
There are many built-in patterns included via the scan command, which effectively works as a secret scanner against the memory on your machine.
Dismember can be used to search memory of all processes it has access to, so running it as root is the most effective method.
Commands are also included to list processes, explore process status and related information, draw process trees, and more...
| Command | Description |
|---|---|
grep | Search process memory for a given string or regex |
scan | Search process memory for a set of predefined secret patterns |
| Command | Description |
|---|---|
files | Show a list of files being accessed by a process |
find | Find a PID given a process name. If multiple processes match, the first one is returned. |
info | Show information about a process |
kernel | Show information about the kernel |
kill | Kill a process (or processes) using SIGKILL |
list | List all processes currently available on the system |
resume | Resume a suspended process using SIGCONT |
suspend | Suspend a process using SIGSTOP (use 'dismember resume' to leave suspension) |
tree | Show a tree diagram of a process and all children (defaults to PID 1). |
Grab a binary from the latest release and add it to your path.
# search memory owned by process 1234
dismember grep -p 1234 'the password is .*'
# search memory owned by processes named "nginx" for a login form submission
dismember grep -n nginx 'username=liamg&password=.*'
# find a github api token across all processes
dismember grep 'gh[pousr]_[0-9a-zA-Z]{36}'
# search all accessible memory for common secrets
dismember scan
Isn't this information all just sitting in
/proc?
Pretty much. Dismember just reads and presents it for the most part. If you can get away with grep whatever /proc/[pid]/blah then go for it! I built this as an educational experience because I couldn't sleep one night and stayed up late reading the proc man-pages (I live an extremely rock 'n' roll lifestyle). It's not a replacement for existing tools, but perhaps it can complement them.
Do you know how horrific some of these commands seem when read out of context?
Yes.






