
KittyStager
 enelg52/kittystager
KittyStager is a simple stage 0 C2. It is made of a web server to host the shellcode and an implant, called kitten. The purpose of this project is to…
command-and-controleducationencryption-decryption-tools+6
enelg52/kittystagerKittyStager is a simple stage 0 C2. It is made of a web server to host the shellcode and an implant, called kitten. The purpose of this project is to…
 kaandemir993/python-shellcode-anydesk-apc-injection-remote-ip-address-analysis
Reverse engineering write-up of Python shellcode that APC-injects into AnyDesk, exfiltrates to a C2 over HTTPS with AES/RSA, and persists via…
 oscarsantanaarias/ida-ghidra-bridge
TCP JSON bridge servers for IDA Pro and Ghidra exposing decompilation, xrefs, symbols, vtables, RTTI and memory patching to external scripts and…
 redsiege/graphstrike
Cobalt Strike HTTPS beaconing over Microsoft Graph API
 spiderlabs/dohc2
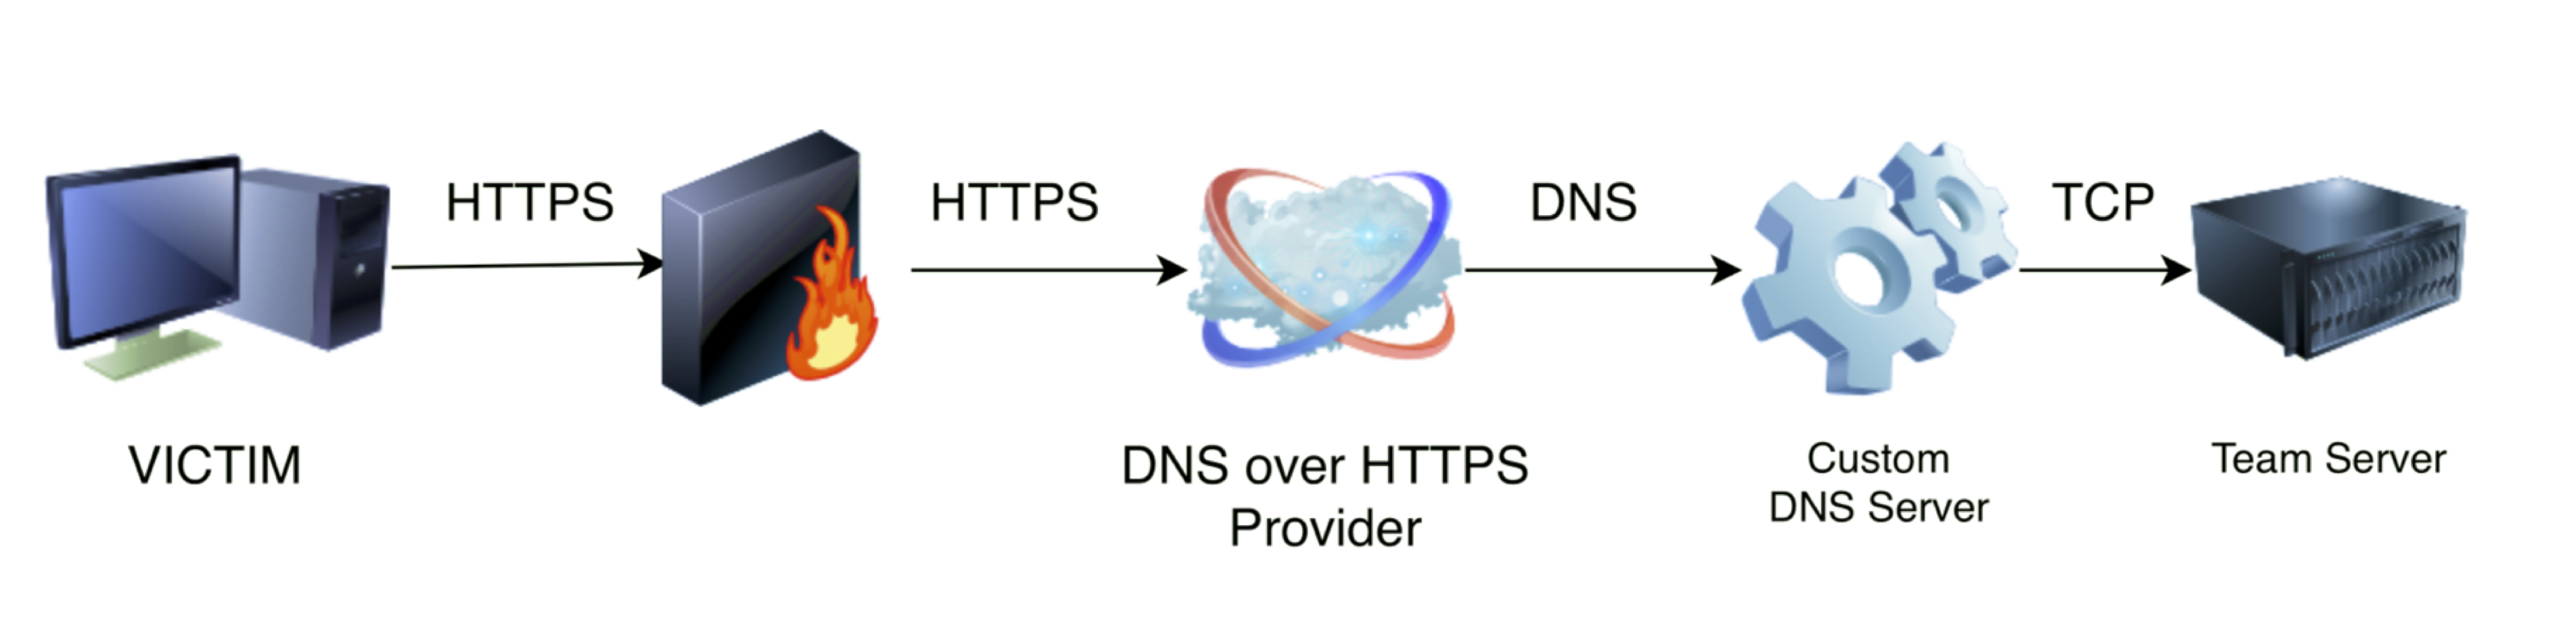
DoHC2 allows the ExternalC2 library from Ryan Hanson (https://github.com/ryhanson/ExternalC2) to be leveraged for command and control (C2) via DNS…
 impostorkeanu/bruteloops
Protocol agnostic online password guessing API.
 4g3nt47/striker
Multi-operator C2 framework with native C and Python agents, HTTP(S) channels, asynchronous tasking, and a reactive web UI for red team operations.
 mr-r00t11/cve-2024-23692
Rejetto HFS (HTTP File Server) is a simple web file server that facilitates file sharing over a network or the internet.
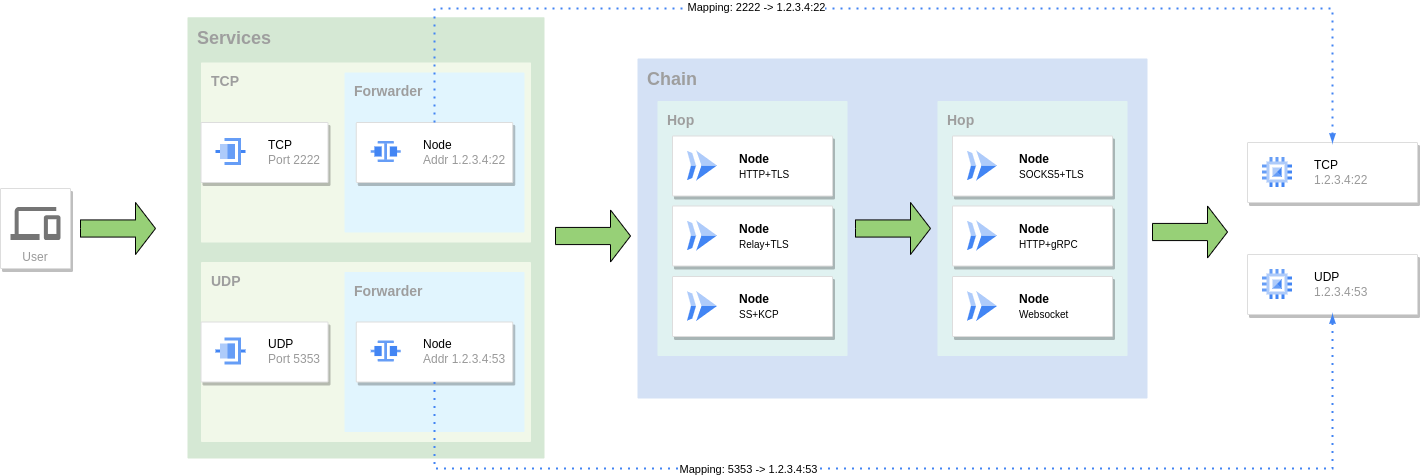 go-gost/gost
GO Simple Tunnel - a simple tunnel written in golang
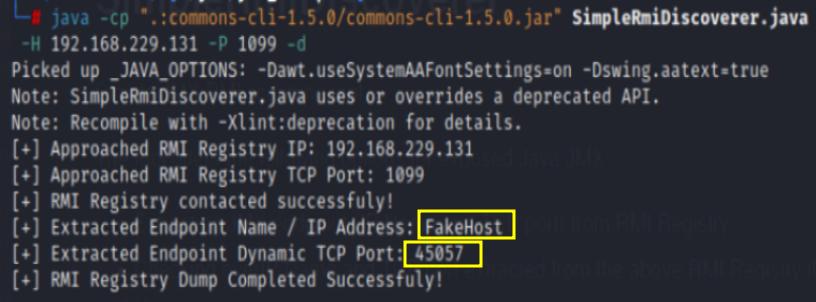 marcin-wolak/simplermidiscoverer
Simple JMX RMI scanning tool
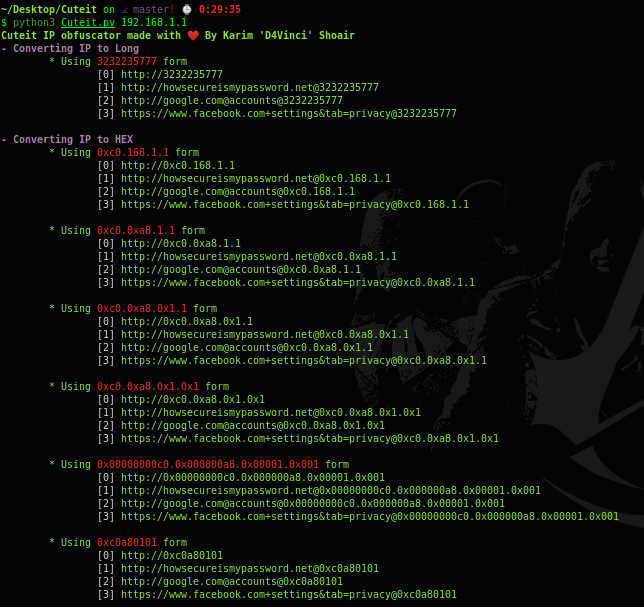 d4vinci/cuteit
IP obfuscator made to make a malicious ip a bit cuter
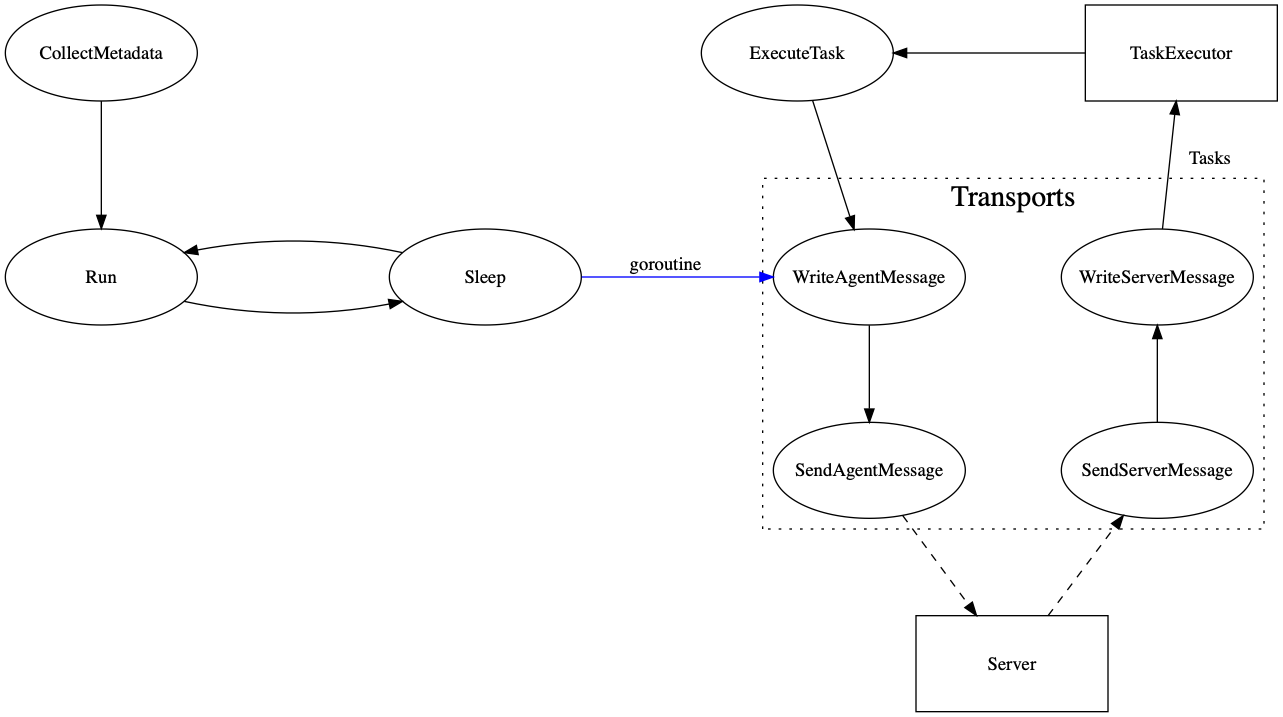 kcarretto/paragon
Red Team engagement platform with the goal of unifying offensive tools behind a simple UI
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 its-arun/cve-2022-39197
Proof-of-concept exploit for CVE-2022-39197, enabling remote code execution against CobaltStrike <= 4.7.1 via malicious SVG payload served over HTTP.
 jephthai/evilvm
Forth-based compiler deployed as position-independent x86_64 shellcode, providing a remote code execution agent with interactive REPL over TCP, HTTP,…
 persistent-security/smshell
PoC for a SMS-based shell. Send commands and receive responses over SMS from mobile broadband capable computers
 vnhacker1337/cve-2022-27925-poc
Zimbra RCE simple poc
 demon-i386/zoshrinkc2
DNS over HTTPS targeted malware (only runs once)