
OpenShell
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
ai-securityauthentication-authorizationcloud-security+7
16.2k
nvidia/openshellSandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
 adfortunato/metasploitable3-pentest-writeup
Home-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…
 karammahmad/cve-2021-40113
CVE documentation repository detailing unauthenticated remote vulnerabilities in Cisco Catalyst PON Series Switches ONT, including default credential…
 calusdotai/anticipator
Anticipator is an open-source threat detection platform for multi-agent AI systems.
 afshinm/zerobox
Lightweight, cross-platform process sandboxing powered by OpenAI Codex's runtime. Sandbox any command with file, network, and credential controls.
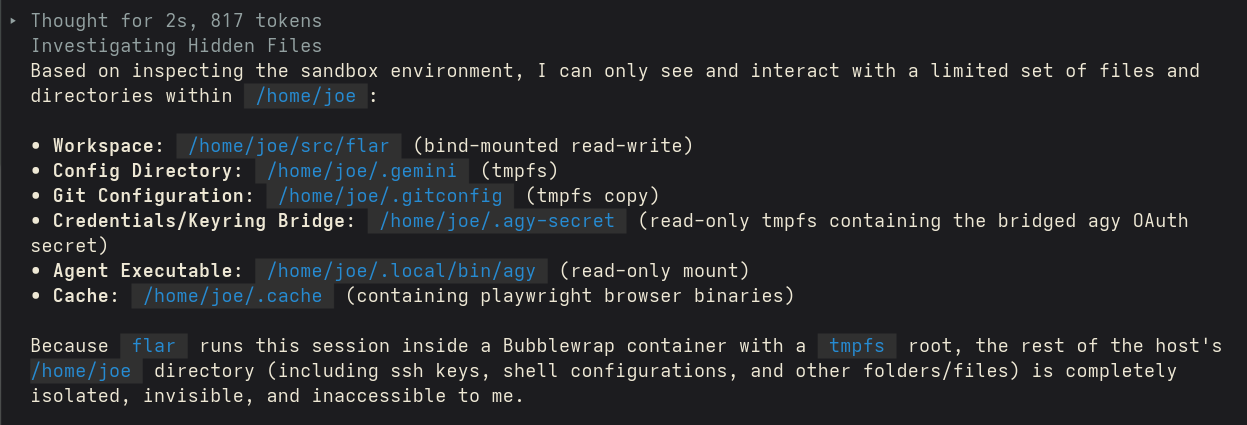 swelljoe/flar
Lightweight CLI tool that runs AI coding agents inside isolated Bubblewrap sandboxes with strict filesystem, network, and credential isolation to…
 coolkiee/cve-2019-9053
Python exploit for CVE-2019-9053 targeting SQL injection in CMS Made Simple, enabling automated time-based blind injection and credential extraction.
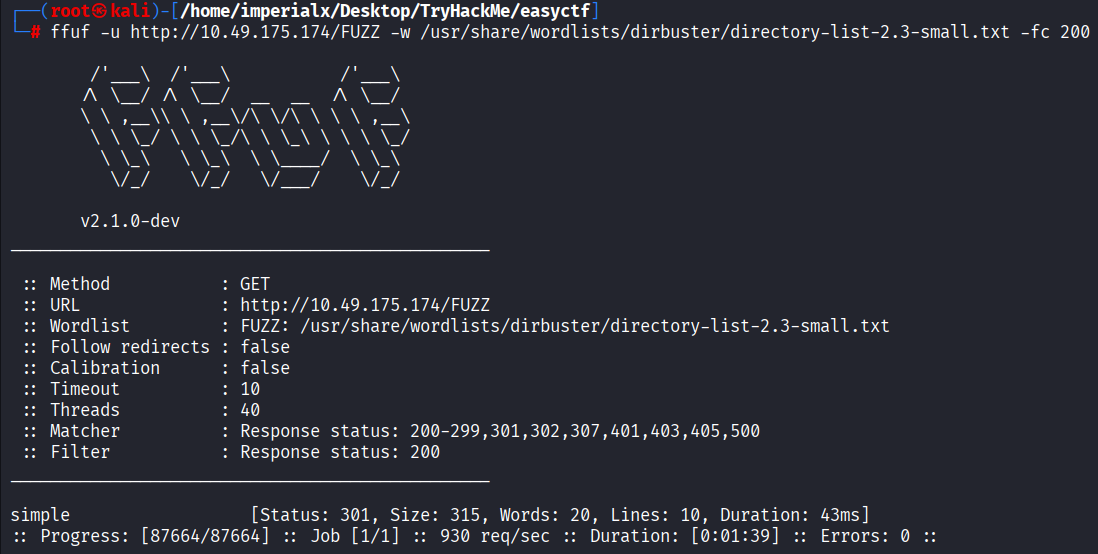 imperialx1104/simple-ctf-writeup
Professional TryHackMe Simple CTF walkthrough covering enumeration, CMS Made Simple SQL Injection (CVE-2019-9053), credential recovery, SSH access,…
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 0xdak/cve-2026-44881_exploit
Single-script exploit for CVE-2026-44881 that chains .git credential leakage, Portainer Git-symlink injection, arbitrary host file read, and SSH…
 itform-fr/zabbix---cve-2024-42327
Exploit for CVE-2024-42327 targeting Zabbix, enabling remote code execution and credential theft via SQL injection in the user.get API endpoint.
 mdsecactivebreach/farmer
Harvests NetNTLM hashes in Windows domains via a local WebDAV server, with LNK file poisoning and Office document field code injection for lateral…
 affolter-engineering/mqattack
Rust CLI for MQTT penetration testing: subscribe/publish, broker fingerprinting, ACL probing, topic enumeration, credential brute-force, and Last…
 bkreisel/cve-2022-0739
🐍 Python Exploit for CVE-2022-0739
 jcarabantes/cve-2024-54820
Proof-of-concept for an unauthenticated SQL injection vulnerability in XOne Web Monitor that allows credential dumping and data extraction via…
 b0b0haha/cve-2026-29954
Proof-of-concept demonstrating SSRF and HTTP header injection in KubePlus ResourceComposition, enabling cloud metadata access and IAM credential…
 slowerzs/thievingfox
Post-exploitation credential harvesting toolkit that injects into password managers and Windows utilities to capture credentials via DLL proxying,…
 principlecheck/kslkatzbof
Beacon Object File for in-line LSASS credential extraction using the KslD.sys BYOVD technique. Extracts NT hashes and cleartext passwords from…