Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacyΒ© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
KubeArmor β€” Runtime Security Enforcement System. Workload hardening/sandboxing and implementing least-permissive policies made easy leveraging LSMs (LSM-BPF, AppArmor). | Kitploit
Tools/GitHubGitHub/kubearmor/kubearmor
Defensive ToolsContainer SecurityCloud Security
GitHubkubearmor/kubearmor

KubeArmor

Runtime Security Enforcement System. Workload hardening/sandboxing and implementing least-permissive policies made easy leveraging LSMs (LSM-BPF, AppArmor).

View RepositoryWebsite
2.6k522426 days agoReviewed by Kitploit

Most Popular

View all β†’

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools β†’
Share

Build Status CII Best Practices CLOMonitor OpenSSF Scorecard SLSA Level 3 codecov FOSSA Status FOSSA Status Slack Discussions Docker Downloads ArtifactHub

KubeArmor is a cloud-native runtime security enforcement system that restricts the behavior (such as process execution, file access, and networking operations) of pods, containers, and nodes (VMs) at the system level.

KubeArmor leverages Linux security modules (LSMs) such as AppArmor, SELinux, or BPF-LSM to enforce the user-specified policies. KubeArmor generates rich alerts/telemetry events with container/pod/namespace identities by leveraging eBPF.

πŸ’ͺ Harden Infrastructure
⛓️ Protect critical paths such as cert bundles
πŸ“‹ MITRE, STIGs, CIS based rules
πŸ›… Restrict access to raw DB table
πŸ’ Least Permissive Access
πŸš₯ Process Whitelisting
πŸš₯ Network Whitelisting
πŸŽ›οΈ Control access to sensitive assets
πŸ”­ Application Behavior
🧬 Process execs, File System accesses
🧭 Service binds, Ingress, Egress connections
πŸ”¬ Sensitive system call profiling
❄️ Deployment Models
☸️ Kubernetes Deployment
πŸ‹ Containerized Deployment
πŸ’» VM/Bare-Metal Deployment

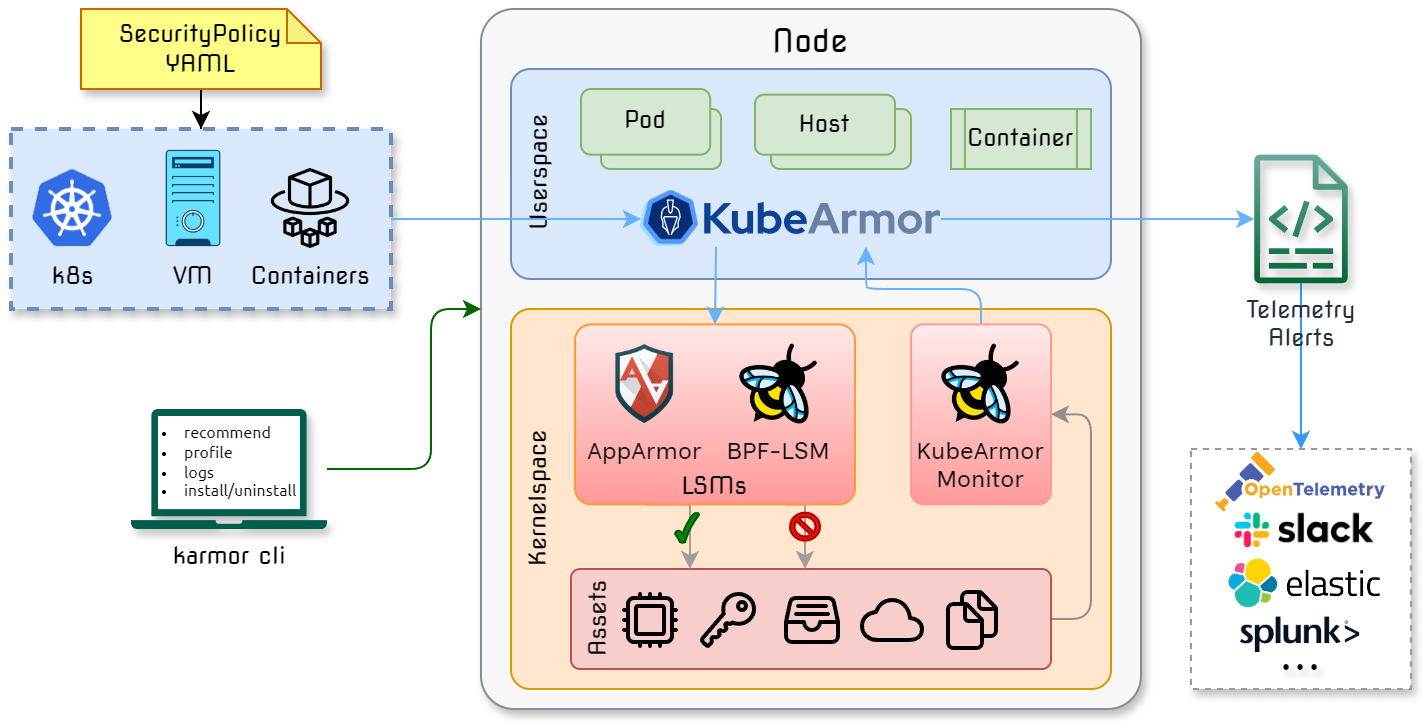
Architecture Overview

KubeArmor High Level Design

Documentation πŸ““

  • πŸ‘‰ Getting Started
  • 🎯 Use Cases
  • βœ”οΈ KubeArmor Support Matrix
  • β™ŸοΈ How is KubeArmor different?
  • πŸ“œ Security Policy for Pods/Containers [Spec] [Examples]
  • πŸ“œ Cluster level security Policy for Pods/Containers [Spec] [Examples]
  • πŸ“œ Security Policy for Hosts/Nodes [Spec] [Examples]
  • πŸ“œ Network Security Policy for Hosts/Nodes [Spec] [Examples]
    ... detailed documentation

Contributors πŸ‘₯

  • πŸ“˜ Contribution Guide
  • πŸ§‘β€πŸ’» Development Guide, Testing Guide
  • βœ‹ Join KubeArmor Slack
  • ❓ FAQs

Biweekly Meeting

  • πŸ—£οΈ Zoom Link
  • πŸ“„ Minutes: Document
  • πŸ“† Calendar invite: Google Calendar, ICS file

Community & Governance

KubeArmor is a community-governed project. The following documents describe how the project is run:

Download Tool