 apr4h/cobaltstrikescan
Scan files or process memory for CobaltStrike beacons and parse their configuration

Scan files or process memory for Cobalt Strike beacons and parse their configuration.
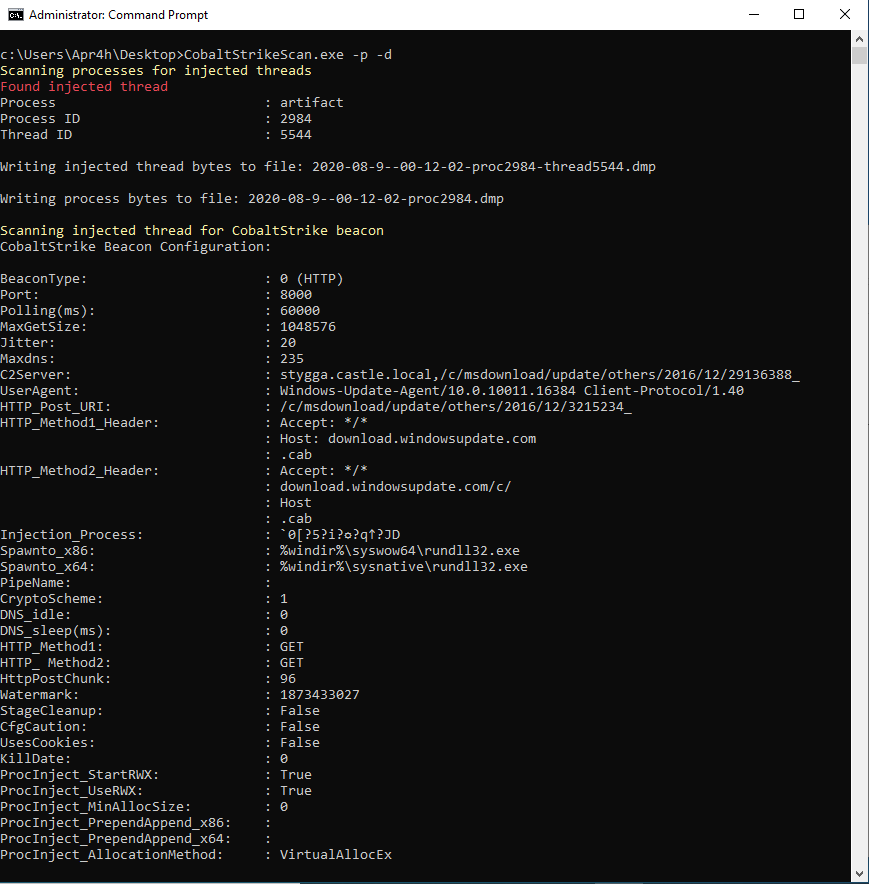
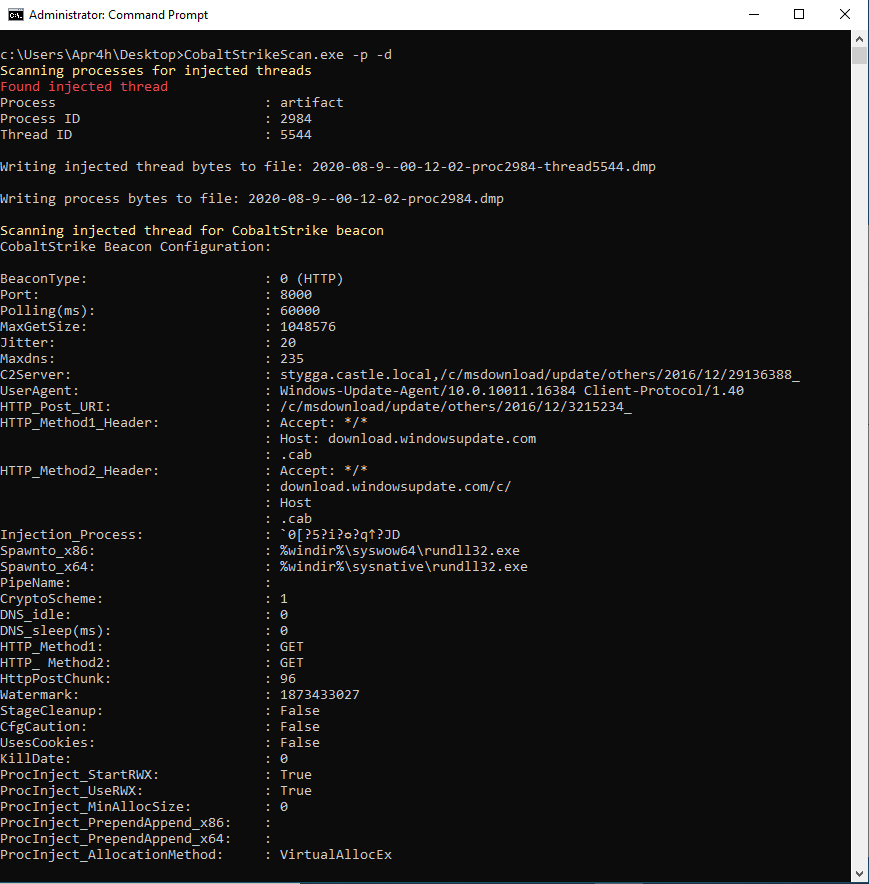
CobaltStrikeScan scans Windows process memory for evidence of DLL injection (classic or reflective injection) and/or performs a YARA scan on the target process' memory for Cobalt Strike v3 and v4 beacon signatures.
Alternatively, CobaltStrikeScan can perform the same YARA scan on a file supplied by absolute or relative path as a command-line argument.
If a Cobalt Strike beacon is detected in the file or process, the beacon's configuration will be parsed and displayed to the console.
CobaltStrikeScan contains GetInjectedThreads as a submodule. Ensure you use git clone --recursive https://github.com/Apr4h/CobaltStrikeScan.git when cloning CobaltStrikeScan so that the submodule's code is also downloaded/cloned.
Costura.Fody is configured to embed CommandLine.dll and libyara.NET.dll in the compiled CobaltStrikeScan.exe assembly. CobaltStrikeScan.exe should then serve as a static, portable version of CobaltStrikeScan. For this to occur, ensure that the "Active Solution Platform" is set to x64 when building.
This project is inspired by the following research / articles:
  -d, --directory-scan          Scan all process/memory dump files in a directory for Cobalt Strike beacons

  -f, --scan-file               Scan a process/memory dump for Cobalt Strike beacons

  -i, --injected-threads        Scan running (64-bit) processes for injected threads and Cobalt Strike beacons

  -p, --scan-processes          Scan running processes for Cobalt Strike beacons

  -v, --verbose                 Write verbose output

  -w, --write-process-memory    Write process memory to file when injected threads are detected

  -h, --help                    Display Help Message

  --help                        Display this help screen.

  --version                     Display version information.