
CVE-2017-16995
 gugronnier/cve-2017-16995
Exploit adapted for a specific PoC on Ubuntu 16.04.01
binary-exploitationexploitationpenetration-testing+2
gugronnier/cve-2017-16995Exploit adapted for a specific PoC on Ubuntu 16.04.01
 emresandikci/nextjs-cve-2026-23870-checker
Checker and fixer for all 13 vulnerabilities in the Next.js May 2026 security release (CVE-2026-23870)
 irsl/cve-2020-1967
Proof-of-concept exploit for OpenSSL CVE-2020-1967, a denial-of-service vulnerability in TLS 1.3 signature_algorithms_cert handling, with…
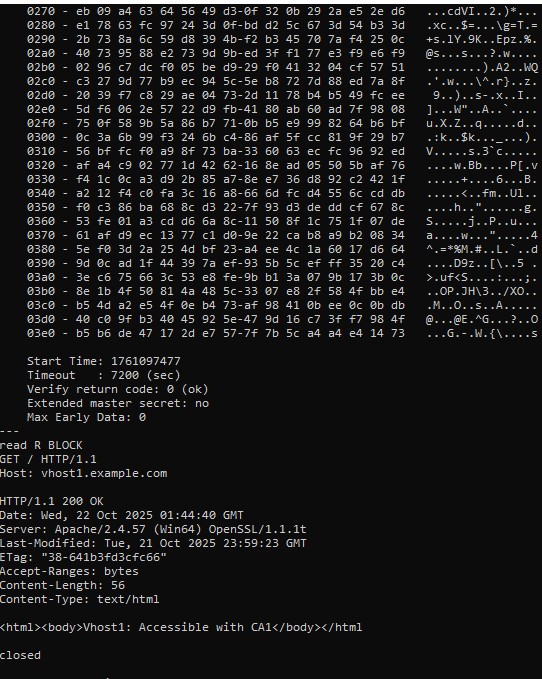 absholi7ly/cve-2025-23048-poc
Apache HTTP Server versions 2.4.35 – 2.4.63 are vulnerable to a client certificate authentication bypass when TLS 1.3 session resumption is used…
 theexploiters/cve-2024-36840-exploit
Exploit For: CVE-2024-36840: SQL Injection Vulnerability in Boelter Blue System Management (Version 1.3)
 shadowbyte1/cve-2024-48245
SQL Injection Vulnerability in Vehicle Management System 1.0 - 1.3
 shadowbyte1/cve-2024-53345
Critical 0 Day in Car Rental Management System Versions 1.0 - 1.3
 toxxxaka/cve-2019-7609
New CVE-2019-7609 which works with python 13
 randomrobbiebf/cve-2024-50507
DS.DownloadList <= 1.3 - Unauthenticated PHP Object Injection
 alt3kx/cve-2007-3831
PHP remote file inclusion in main.php in ISS Proventia Network IPS GX5108 1.3 and GX5008 1.5
 paragbagul111/cve-2024-41290
FlatPress CMS v1.3.1 1.3 was discovered to use insecure methods to > store authentication data
 paragbagul111/cve-2024-33209
FlatPress 1.3. is vulnerable to Cross Site Scripting (XSS). An attacker can inject malicious JavaScript code into the "Add New Entry" section, which…
 paragbagul111/cve-2024-33210
A cross-site scripting (XSS) vulnerability has been identified in Flatpress 1.3. This vulnerability allows an attacker to inject malicious scripts…
 advanced-threat-research/cve-2020-16898
CVE-2020-16898 (Bad Neighbor) Microsoft Windows TCP/IP Vulnerability Detection Logic and Rule
 markie-dev/desc_race_a15
CVE-2021-30955 iOS 15.1.1 POC for 6GB RAM devices (A14-A15)
 grrrdog/acedcup
Payload generator for Java Binary Deserialization attack with Commons FileUpload (CVE-2013-2186)
 hackintoanetwork/arc-browser-address-bar-spoofing-poc
Proof-of-concept exploit for CVE-2024-25733 demonstrating address bar spoofing in ARC Browser on iOS/iPadOS using JavaScript-based navigation…
 bluedragonsecurity/cve-2026-27831-poc
Poc Exploit for CVE-2026-27831 - vulnerability discovered by : Antonius