
atomic-red-team
 redcanaryco/atomic-red-team
Small and highly portable detection tests based on MITRE's ATT&CK.
educationlabs-practicepenetration-testing+1
12.7k
redcanaryco/atomic-red-teamSmall and highly portable detection tests based on MITRE's ATT&CK.
 streaak/keyhacks
Curated collection of commands to validate leaked API keys from bug bounty programs and penetration tests, covering 80+ services including AWS,…
 jonaslejon/malicious-pdf
Generate malicious PDF test files for penetration testing, bug bounty hunting, and red teaming. Tests SSRF, XSS, XXE, NTLM credential theft, and data…
 c2sp/wycheproof
Project Wycheproof tests crypto libraries against known attacks.
 open-policy-agent/conftest
Write tests against structured configuration data using the Open Policy Agent Rego query language
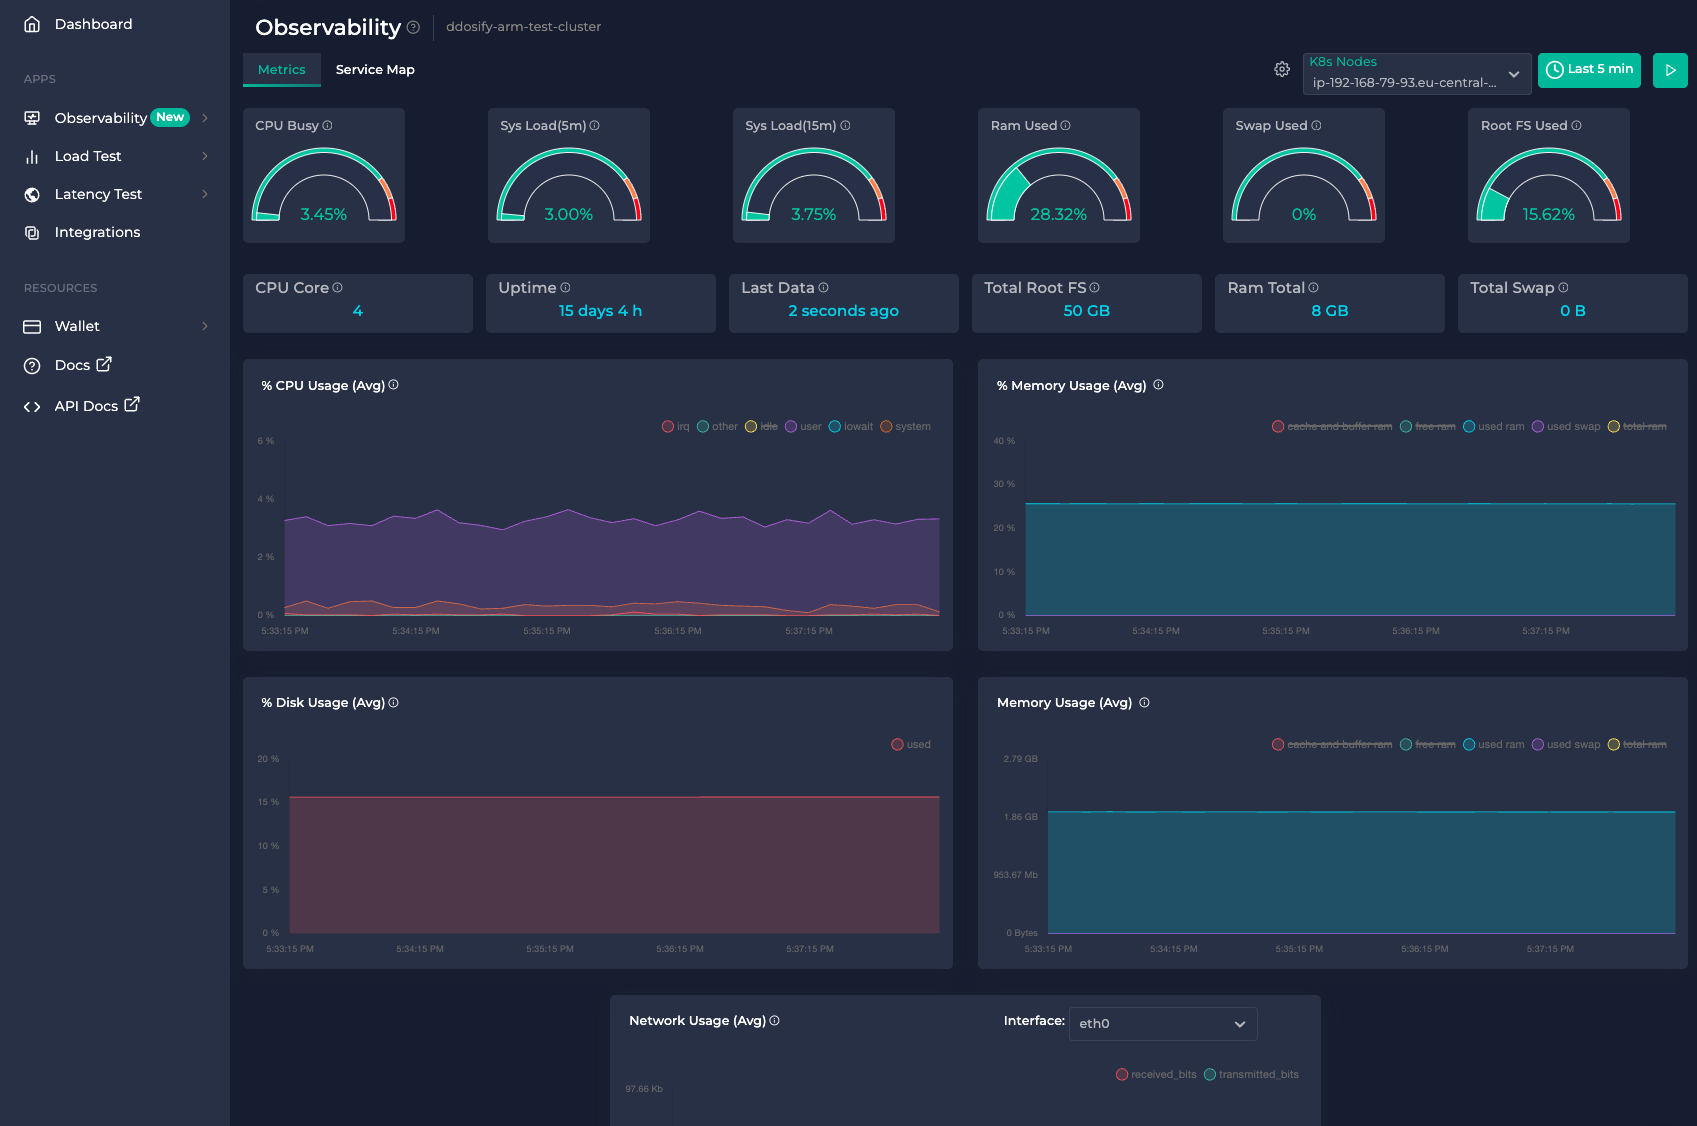 getanteon/anteon
eBPF-powered Kubernetes monitoring and performance testing platform that automatically generates service maps, tracks real-time metrics, and runs…
 voorivex/pentest-guide
Penetration tests guide based on OWASP including test cases, resources and examples.
 akto-api-security/akto
Open-source API security platform for continuous API discovery, vulnerability testing, and runtime threat detection. Integrates with CI/CD pipelines…
 bishopfox/cloudfox
Automating situational awareness for cloud penetration tests.
 0xmaximus/galaxy-bugbounty-checklist
Tips and Tutorials for Bug Bounty and also Penetration Tests.
 endava/cats
Automated REST API fuzzer and negative testing tool for OpenAPI endpoints. Generates, runs, and reports thousands of self-healing tests with no…
 unkn0wn-root/resterm
Terminal API client for HTTP, GraphQL, gRPC, WebSocket and SSE. Plain .http files you can diff and version, with scripted tests, workflows, mocks,…
 laluka/bypass-url-parser
Tests hundreds of URL bypass techniques against 40X protected pages using raw curl requests, with multi-mode scanning, header spoofing, and JSON/HTML…
 dirkjanm/mitm6
Exploits Windows IPv6 default configuration to spoof DNS via DHCPv6, redirecting victim traffic for credential relaying and man-in-the-middle attacks…
 galkan/crowbar
Crowbar is brute forcing tool that can be used during penetration tests. It is developed to support protocols that are not currently supported by…
 lukechilds/reverse-shell
On-demand reverse shell service that auto-detects target environment and executes appropriate payload for remote access during penetration tests.
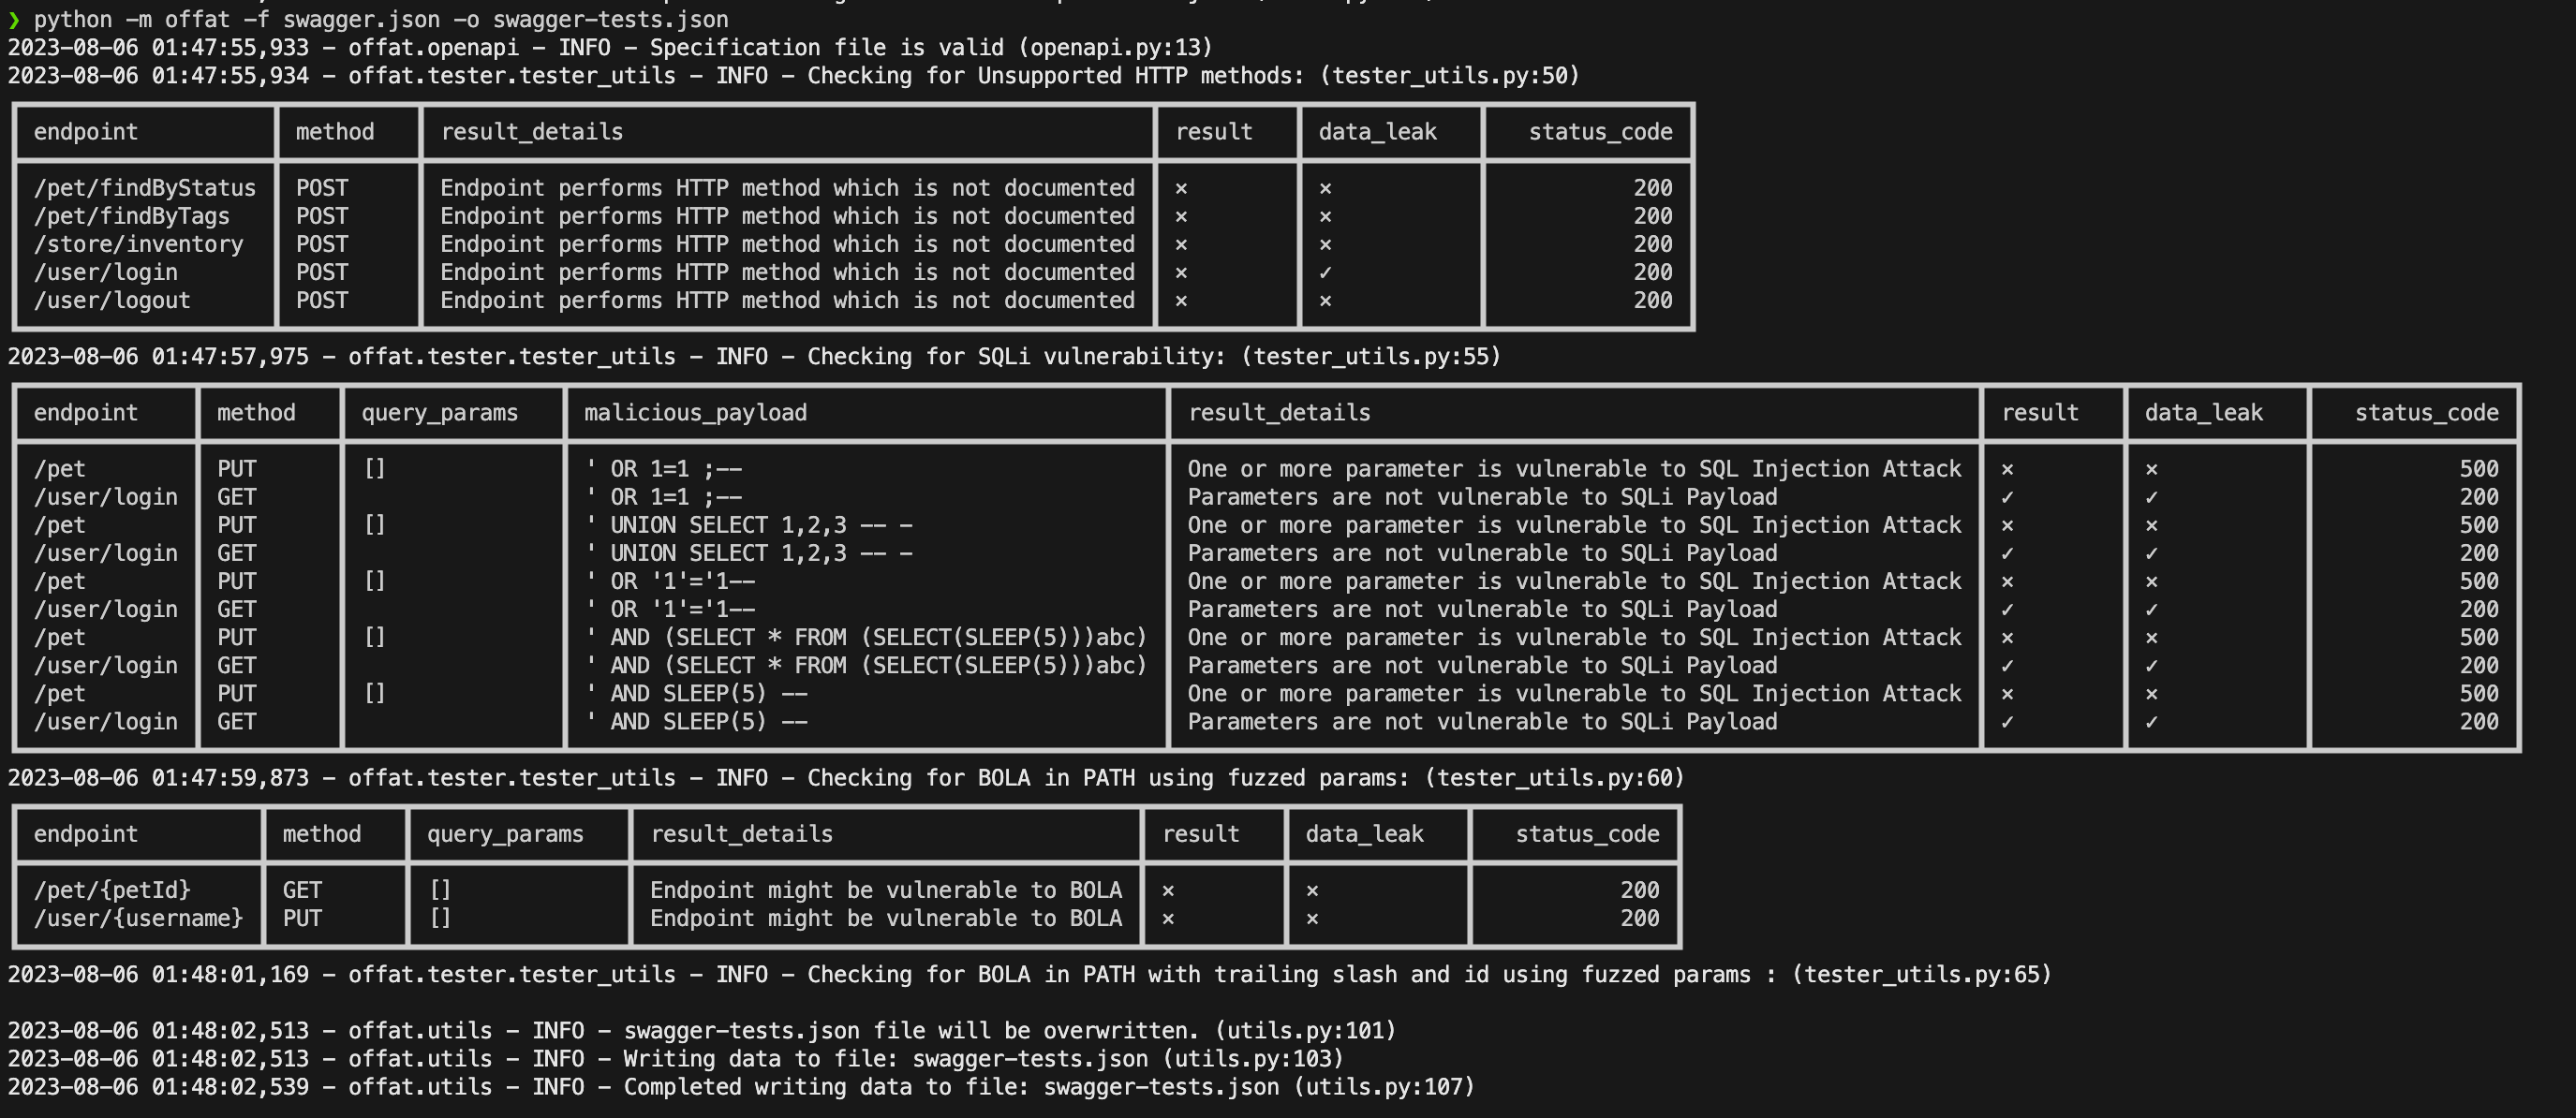 owasp/offat
Automated API security testing tool that generates tests from OpenAPI specs, fuzzes inputs, and checks for OWASP API Top 10 vulnerabilities including…
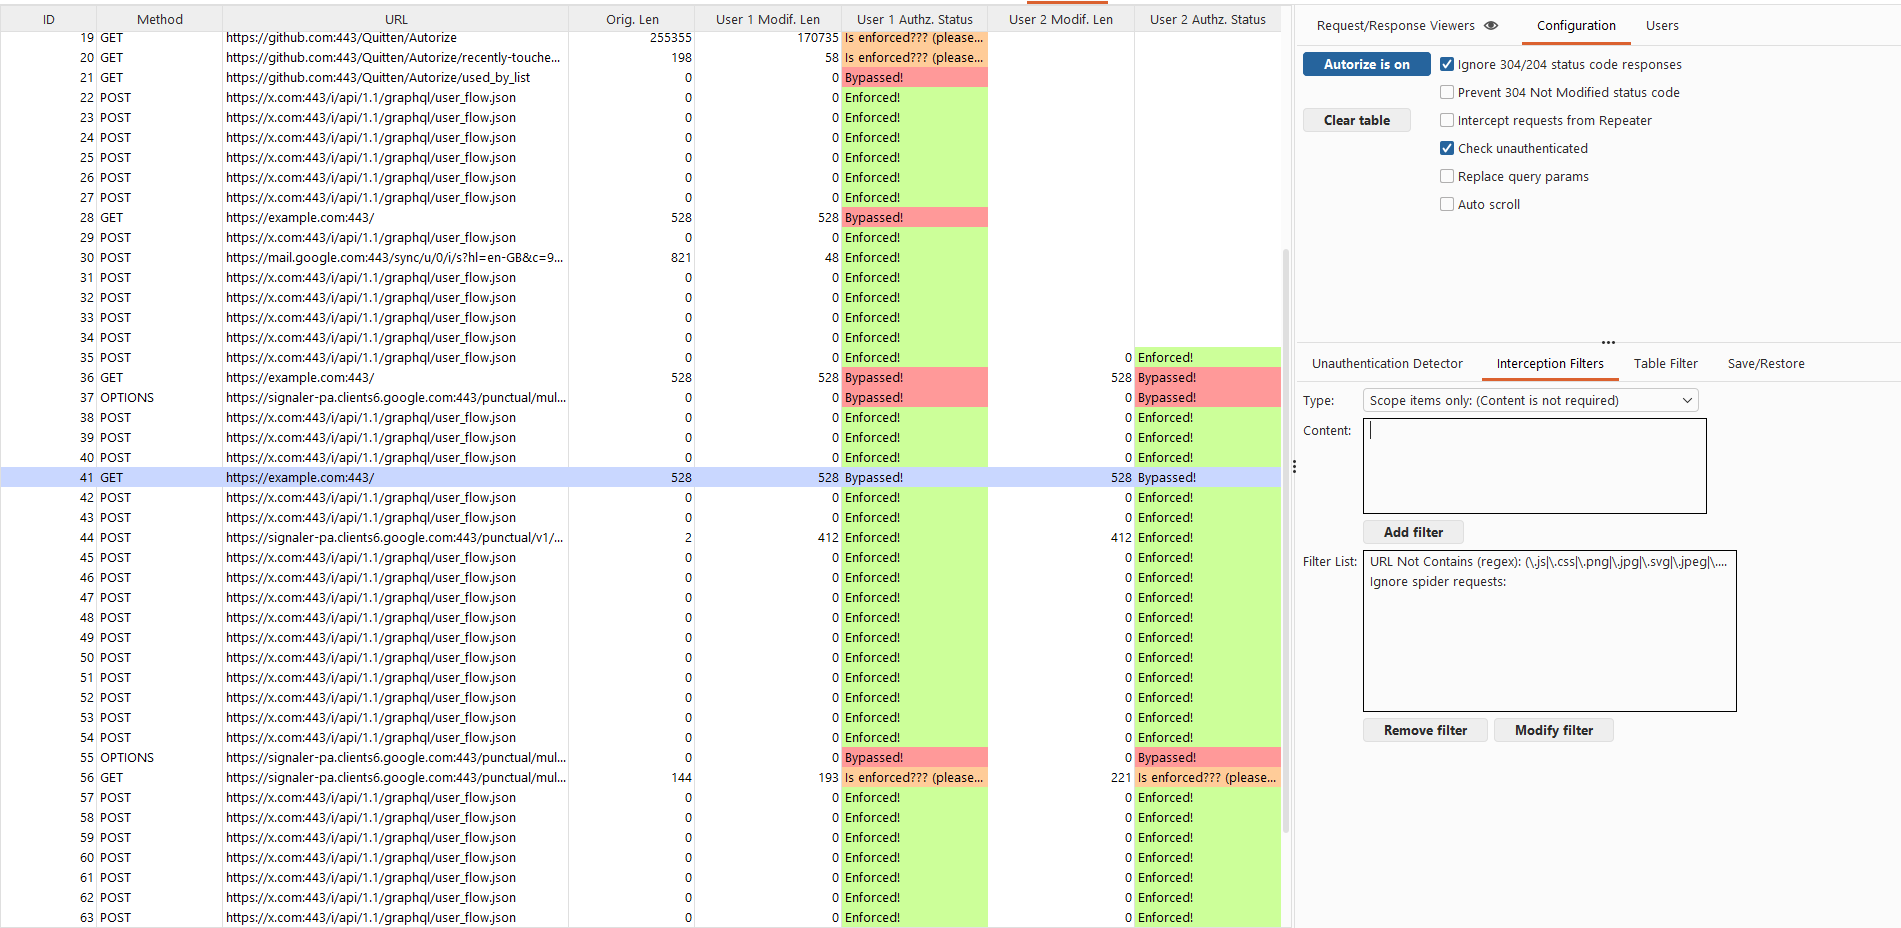 quitten/autorize
Automatic authorization enforcement detection extension for burp suite written in Jython developed by Barak Tawily in order to ease application…