

ShadowSteal
 huskyhacks/shadowsteal
Pure Nim implementation for exploiting CVE-2021-36934, the SeriousSAM local privilege escalation
exploitationpenetration-testingpost-exploitation+3
210
huskyhacks/shadowstealPure Nim implementation for exploiting CVE-2021-36934, the SeriousSAM local privilege escalation
 schierlm/javapayload
JavaPayload is a collection of pure Java payloads to be used for post-exploitation from pure Java exploits or from common misconfigurations (like not…
 citronneur/rdpy
Remote Desktop Protocol in Twisted Python
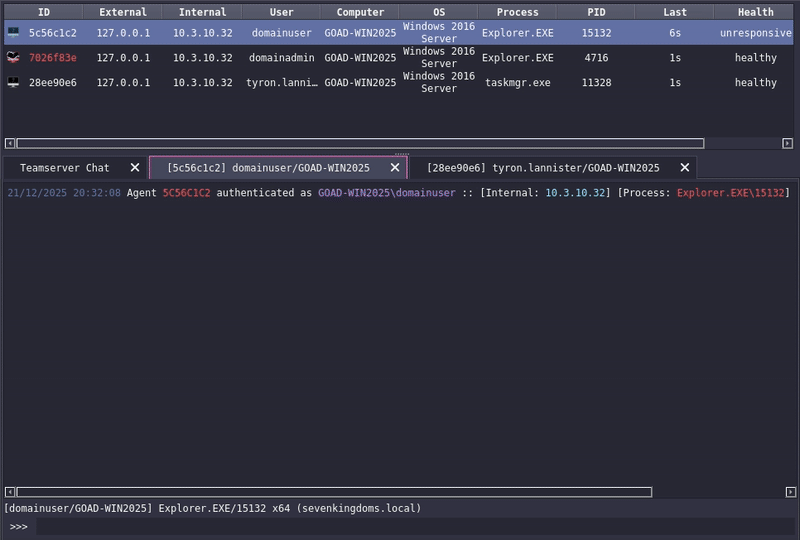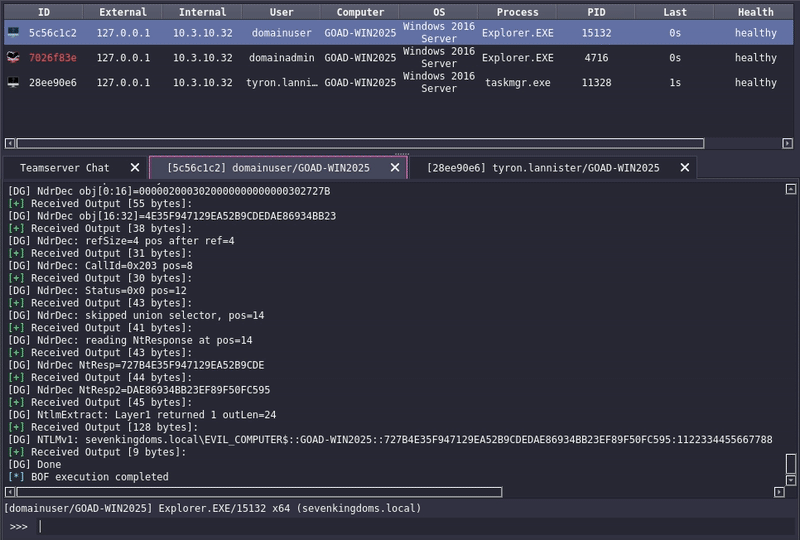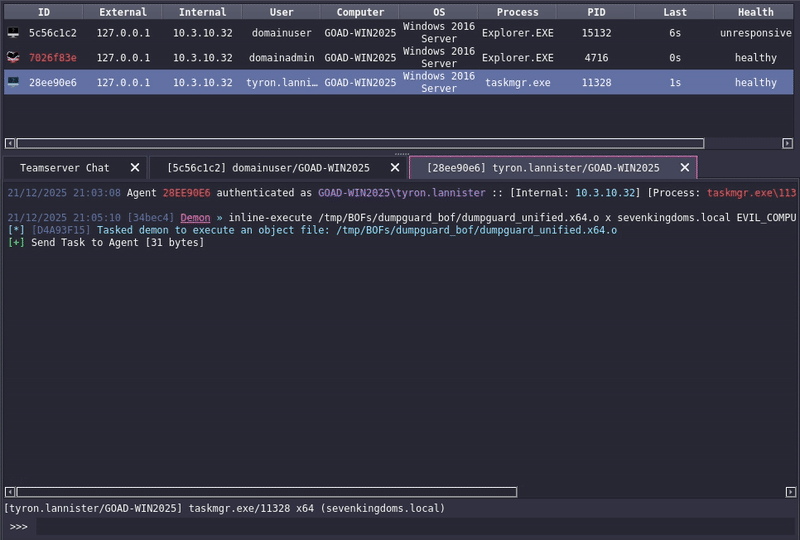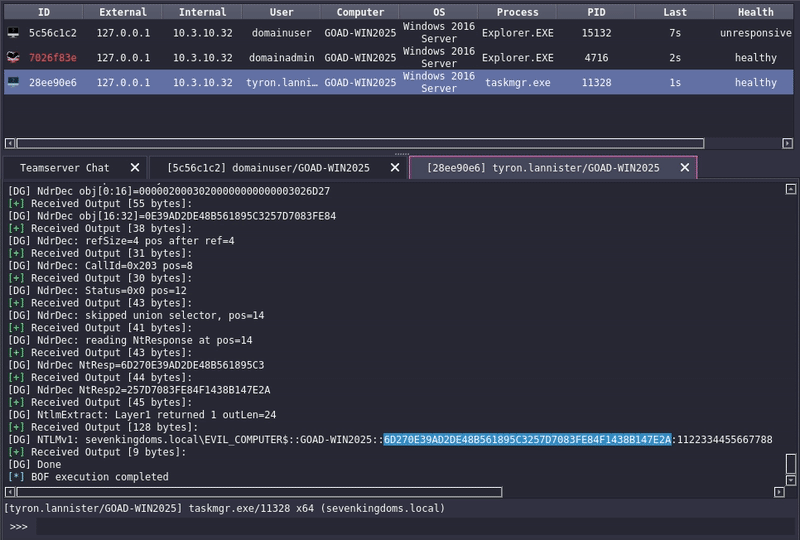 0xedh/dumpguard_bof
Beacon Object File (BOF) port of DumpGuard for extracting NTLMv1 hashes from sessions on modern Windows systems.
 unkaktus/grill
global rate-limiting in Linux (CVE-2016-5696) scanner
 rocket-panda/cve-2025-9074
Bash-based exploit script for CVE-2025-9074 that abuses the internal Docker API to mount the host C drive, execute commands inside a container, and…
 homjxi0e/cve-2017-9779
Automatic execution Payload From Windows By Path Users All Exploit Via File bashrc
 naksyn/pythonmemorymodule
pure-python implementation of MemoryModule technique to load dll and unmanaged exe entirely from memory
 oxdbxkxo/ez-pwnkit
Go implementation of the PwnKit Linux Local Privilege Escalation exploit (CVE-2021-4034)
 b3nac/injuredandroid
A vulnerable Android application that shows simple examples of vulnerabilities in a ctf style.
 vardhan0257/upb-any-recursion-audit
Audit harness testing whether the CVE-2026-0994 Any-unwrapping recursion bug class affects upb's C core in Ruby and PHP protobuf bindings, with…
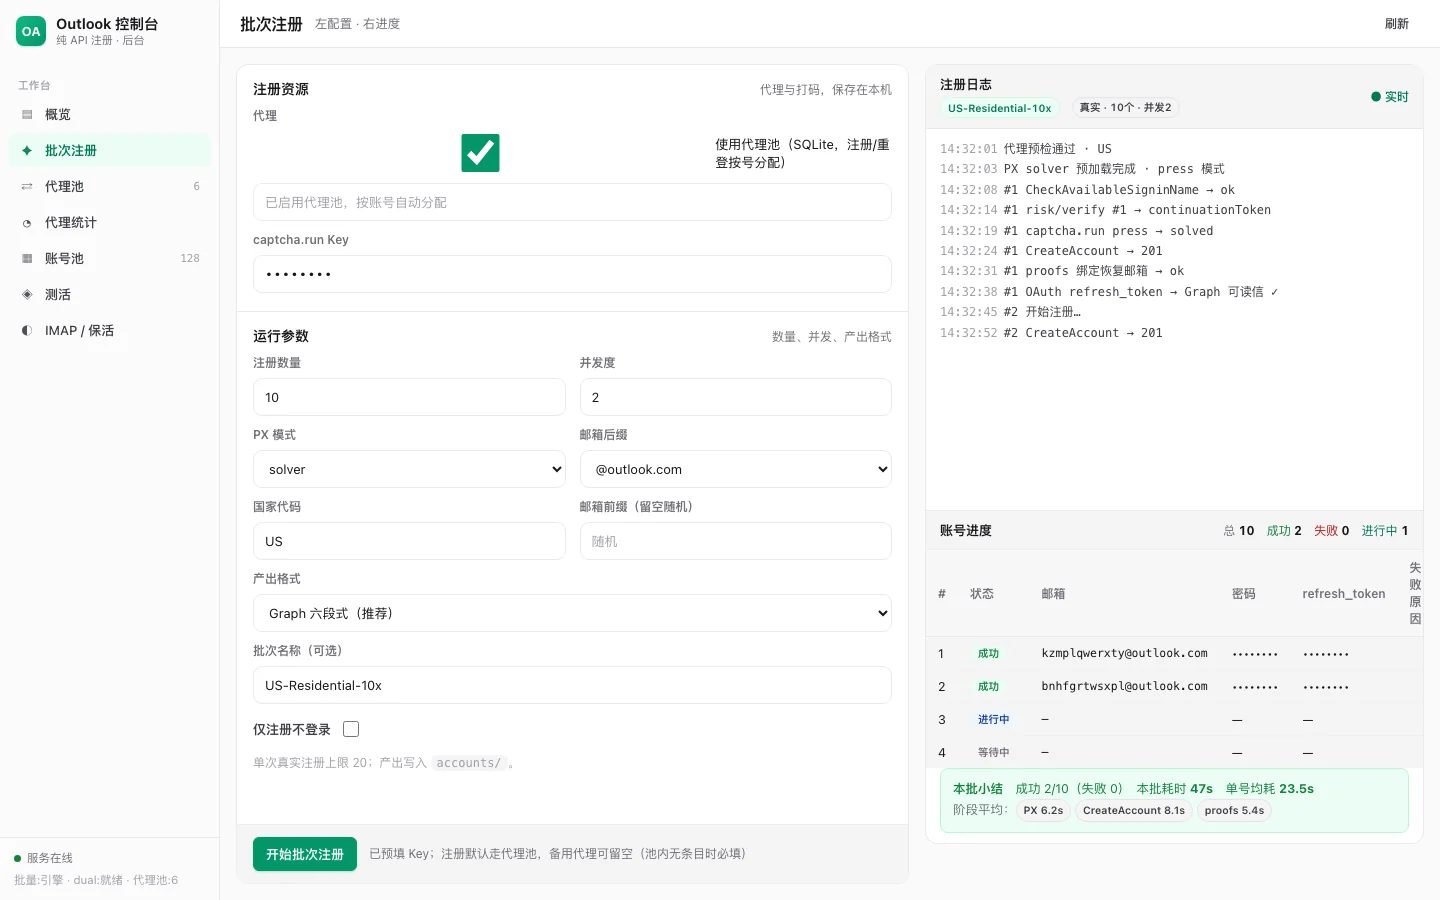 lxf746/outlook-auto-register
Automated Outlook account registration tool using pure HTTP protocol with PerimeterX captcha solving, proxy pool management, and email token…
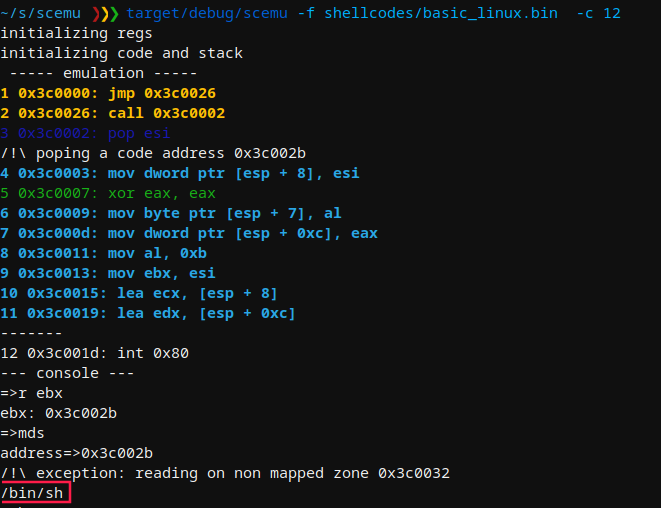 mwemuorg/mwemu
Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…
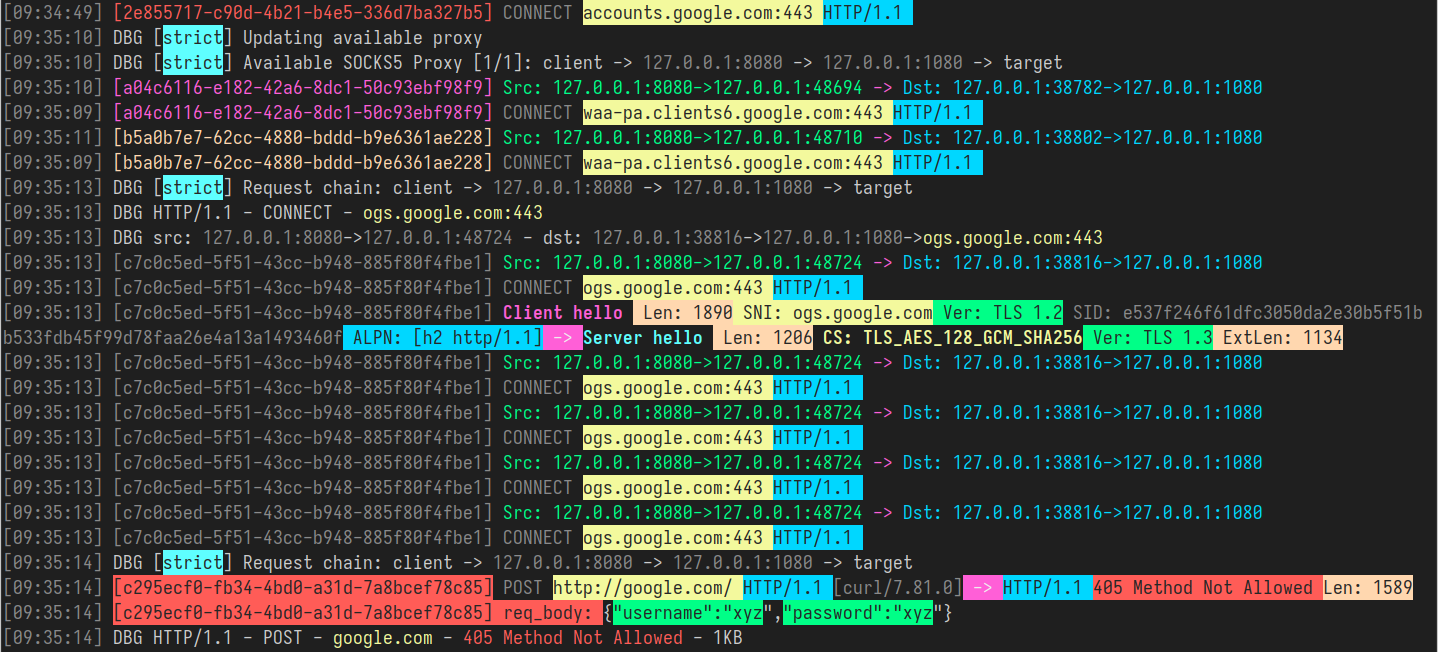 shadowy-pycoder/go-http-proxy-to-socks
CLI MITM proxy that converts SOCKS4/SOCKS5 into HTTP/HTTPS/HTTP2/HTTP3 proxy with transparent TCP/UDP redirection, ARP/NDP/DNS spoofing, traffic…
 drbloop2000/cve-2026-19745
Learn how I found my first two CVEs by pure accident.
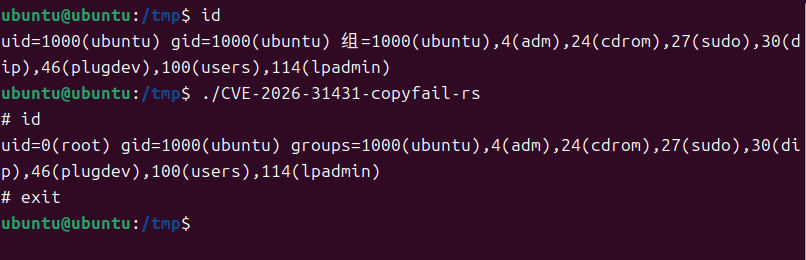 kanbaraakihito/cve-2026-31431-copyfail-rs
Pure Rust proof-of-concept for CVE-2026-31431, targeting Linux x86_64 kernels with AF_ALG AEAD support. Static musl build, no runtime dependencies,…
 mokokash/ejbca-pqc-lab
Pure PQC two-tier PKI hierarchy using ML-DSA-65 (NIST FIPS 204) on EJBCA Community Edition — Root CA + Sub CA with CRL and OCSP
 stealthcopter/deepce
Docker Enumeration, Escalation of Privileges and Container Escapes (DEEPCE)