Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
17 results
LnkMeMaybe preview

LnkMeMaybe

GitHubtrustedsec/lnkmemaybe

Lnk crafting and research tools

binary-analysisdigital-forensicsexploitation+3
1857 months ago
Shortcut-Payload-Generator preview

Shortcut-Payload-Generator

GitHub9aylas/shortcut-payload-generator

AutoIt HackTool, Shortcuts .lnk Payloads Generator As LNK-KISSER.
exploitationmalware-analysispayload-generation+1
1038 years ago
CVE-2017-8464-EXP preview

CVE-2017-8464-EXP

GitHubxssfile/cve-2017-8464-exp

Exploit for CVE-2017-8464 LNK remote code execution vulnerability. Generates malicious .lnk files for USB-based payload delivery, supporting x86 and…

exploitationlateral-movementpayload-generation+3
18 years ago
POC-CVE-2017-8464-OpenCalculator preview

POC-CVE-2017-8464-OpenCalculator

GitHubplayboisk8/poc-cve-2017-8464-opencalculator

Exploiting the .lnk vulnerability and operating system handling mechanisms regarding explorer.exe and USB drives.
binary-analysisbinary-exploitationexploitation+2
2 months ago
EpSiLoNPoInTlnk preview

EpSiLoNPoInTlnk

GitHubepsilonpointori/epsilonpointlnk

Generates obfuscated .lnk files exploiting CVE-2026-21510 with LNK stomping, encrypted payloads, and anti-forensics for authorized penetration…
anti-botexploitationmalware-analysis+4
25 months ago
CVE-2017-8464-EXP preview

CVE-2017-8464-EXP

GitHub3gstudent/cve-2017-8464-exp

Support x86 and x64
binary-exploitationexploitationpayload-generation+2
675 years ago
Peyara-FileUpload preview

Peyara-FileUpload

GitHubcapture0x/peyara-fileupload

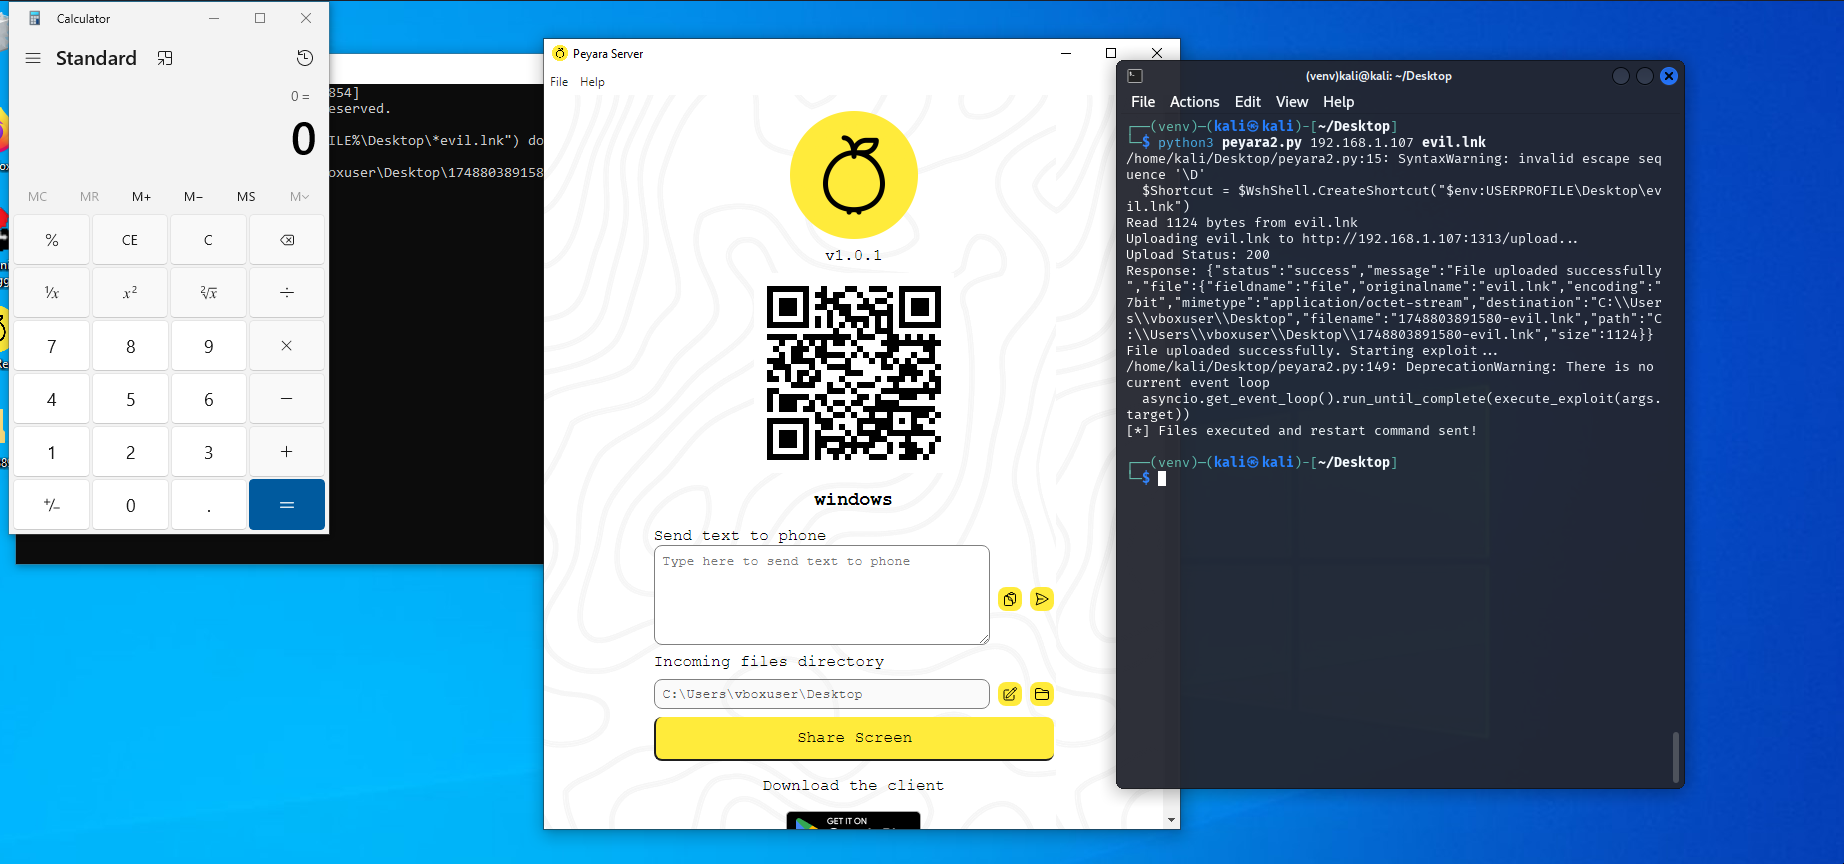
Peyara Remote Mouse Unauthenticated Arbitrary File Upload
exploitationpayload-generationremote-access-tool+1
1 year ago
SMBetray preview

SMBetray

GitHubquickbreach/smbetray

SMB MiTM tool with a focus on attacking clients through file content swapping, lnk swapping, as well as compromising any data passed over the wire in…
exploitationnetwork-securityred-teaming
3828 years ago
SharpStay preview

SharpStay

GitHub0xthirteen/sharpstay

.NET tool for installing Windows persistence via registry keys, scheduled tasks, services, WMI events, COM hijacks, and LNK backdoors, supporting…
penetration-testingpersistence-mechanismspost-exploitation+1
4992 years ago
StayKit preview

StayKit

GitHub0xthirteen/staykit

Cobalt Strike extension for post-exploitation persistence using SharpStay .NET assembly. Provides GUI-driven persistence via Registry keys, Scheduled…
exploit-frameworkspayload-generationpersistence-mechanisms+2
4906 years ago
Farmer preview

Farmer

GitHubmdsecactivebreach/farmer

Harvests NetNTLM hashes in Windows domains via a local WebDAV server, with LNK file poisoning and Office document field code injection for lateral…
information-gatheringlateral-movementpassword-attacks+4
4295 years ago
CVE-2025-9491_POC preview

CVE-2025-9491_POC

GitHubamperclock/cve-2025-9491_poc

Proof-of-Concept of the CVE-2025-9491 using invisible characters in the arguments of a Windows shortcut file (.lnk)
binary-analysiseducationexploitation+3
1811 months ago
CVE-2026-32202 preview

CVE-2026-32202

GitHubvirus-or-not/cve-2026-32202

Generates LNK files with crafted _IDCONTROLW structures to research Windows Shell spoofing vulnerabilities CVE-2026-21510 and CVE-2026-32202,…
binary-analysisexploitationpapers-research+2
85 months ago
CVE-2026-32202 preview

CVE-2026-32202

GitHubsolarlynxsqueeze/cve-2026-32202

Generates malicious LNK files to coerce Net-NTLMv2 hashes via Windows Shell UNC handling, with custom SMB listener and relay integration for…
exploitationlateral-movementpayload-generation+2
5 months ago
CVE-2026-32202 preview

CVE-2026-32202

GitHubf0xox/cve-2026-32202

Technical analysis of CVE-2026-32202, a zero-click NTLM credential coercion via crafted .lnk Control Panel applet items in Windows Explorer.
exploitationinformation-gatheringpapers-research+4
3 months ago
CVE-2025-50154-Aggressor-Script preview

CVE-2025-50154-Aggressor-Script

GitHubash1996x/cve-2025-50154-aggressor-script

Cobalt Strike Aggressor script that weaponizes LNK and Library-MS files to trigger SMB NTLMv2 hash disclosure, including CVE-2025-24054 bypass, for…

command-and-controlctfeducation+9
11 year ago
Random-Scripts preview

Random-Scripts

GitHubstar-sg/random-scripts

Collection of DFIR and OSINT Python scripts for parsing malicious LNK samples, extracting OLE objects from MHTML, and hashing favicons to hunt…

digital-forensicsforensicshash-analysis+5
23 years ago