

 brianwrf/nagascan
NagaScan is a distributed passive vulnerability scanner for Web application.
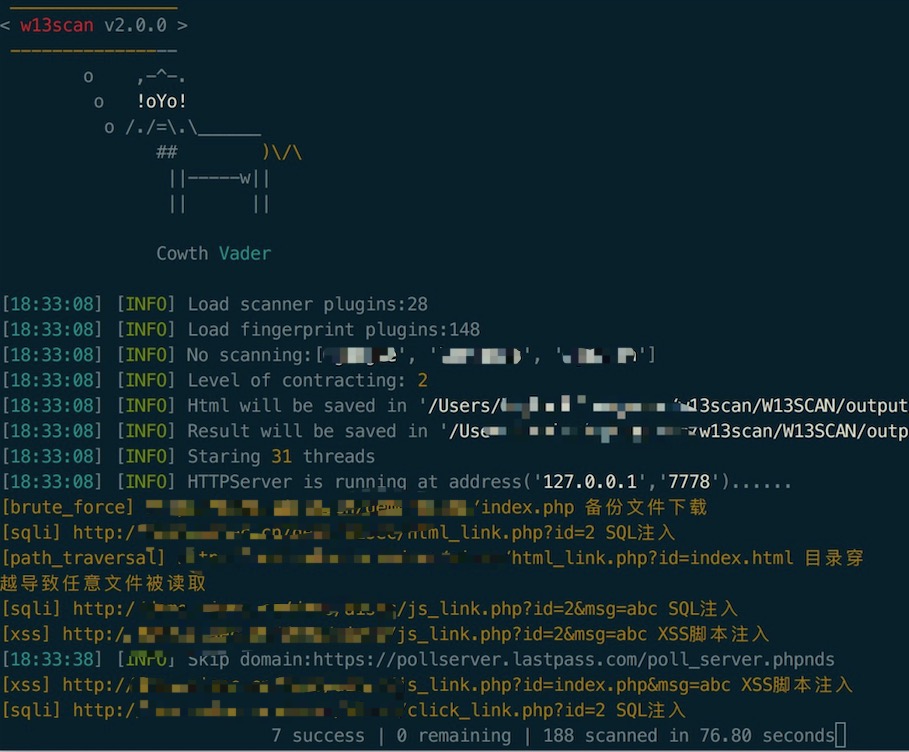 w-digital-scanner/w13scan
Passive and active web vulnerability scanner with plugin-based detection for XSS, SQL injection, command injection, and sensitive file disclosure.…
 wagiro/burpbounty
Burp Bounty (Scan Check Builder in BApp Store) is a extension of Burp Suite that allows you, in a quick and simple way, to improve the active and…
 ikkisoft/parrotng
Java-based tool to detect Adobe Flex SWF files vulnerable to CVE-2011-2461, usable as a command-line utility or Burp Suite passive scanner plugin.
 abrahamsurf/sdwan-scanner-cve-2026-20127
Cisco SD-WAN Exposure & Potential Vulnerability Scanner (Passive Fingerprinting) 2026
 sibersan/apache_audit_cve-2026-23918
Python toolkit to audit Apache HTTP Server against CVE-2026-23918 (HTTP/2 double-free RCE) and 4 related CVEs. Passive scanner with ALPN verification…
 strobelpierre/cve-2026-9082
Semi-passive scanner that detects Drupal installations vulnerable to CVE-2026-9082 (PostgreSQL SQL injection) via fingerprinting, version detection,…
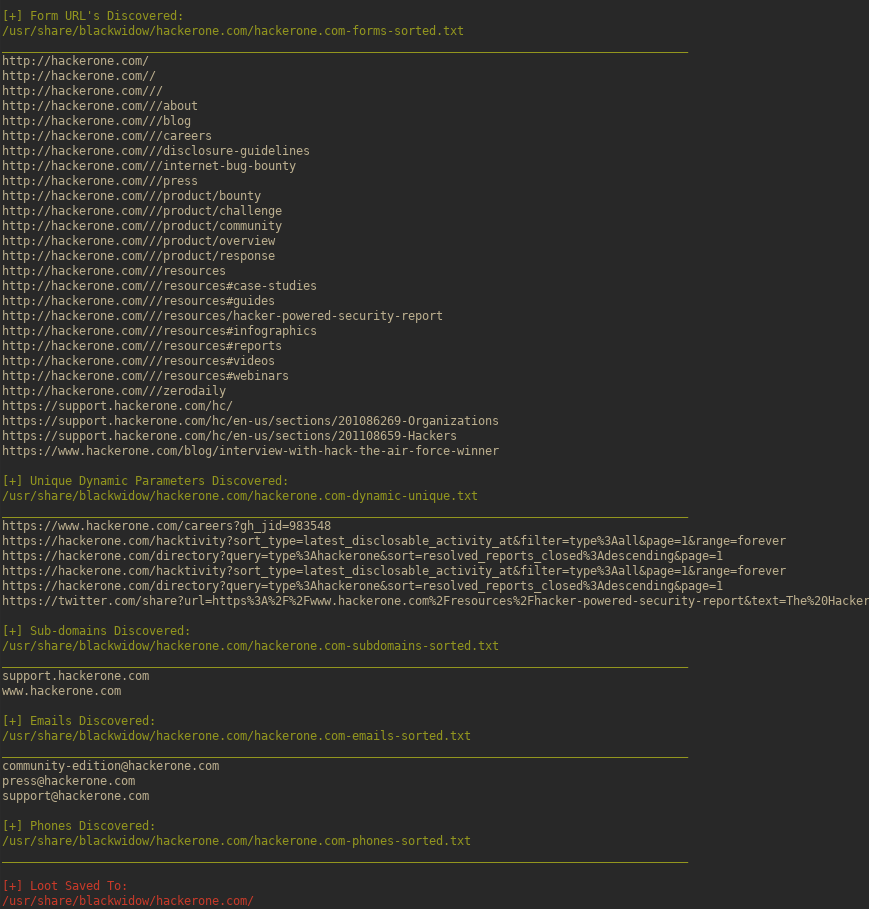 1n3/blackwidow
A Python based web application scanner to gather OSINT and fuzz for OWASP vulnerabilities on a target website.
 xkillbit/cve-2025-55182-scanner
Passive vulnerability scanner for CVE-2025-55182 and CVE-2025-66478, detecting unauthenticated RCE in React Server Components via framework…
 cybrdude/cve-2026-1731-scanner
Passive vulnerability scanner for CVE-2026-1731 — BeyondTrust RS/PRA pre-auth RCE (CVSS 9.9). Educational & defensive use only.
 anoxhunterdump-ctrl/cve-2026-103752-authorizer-privilege-escalation
Defensive analysis, patch breakdown, and passive detection scanner for CVE-2026-103752 (WordPress Authorizer Plugin <= 3.15.3).
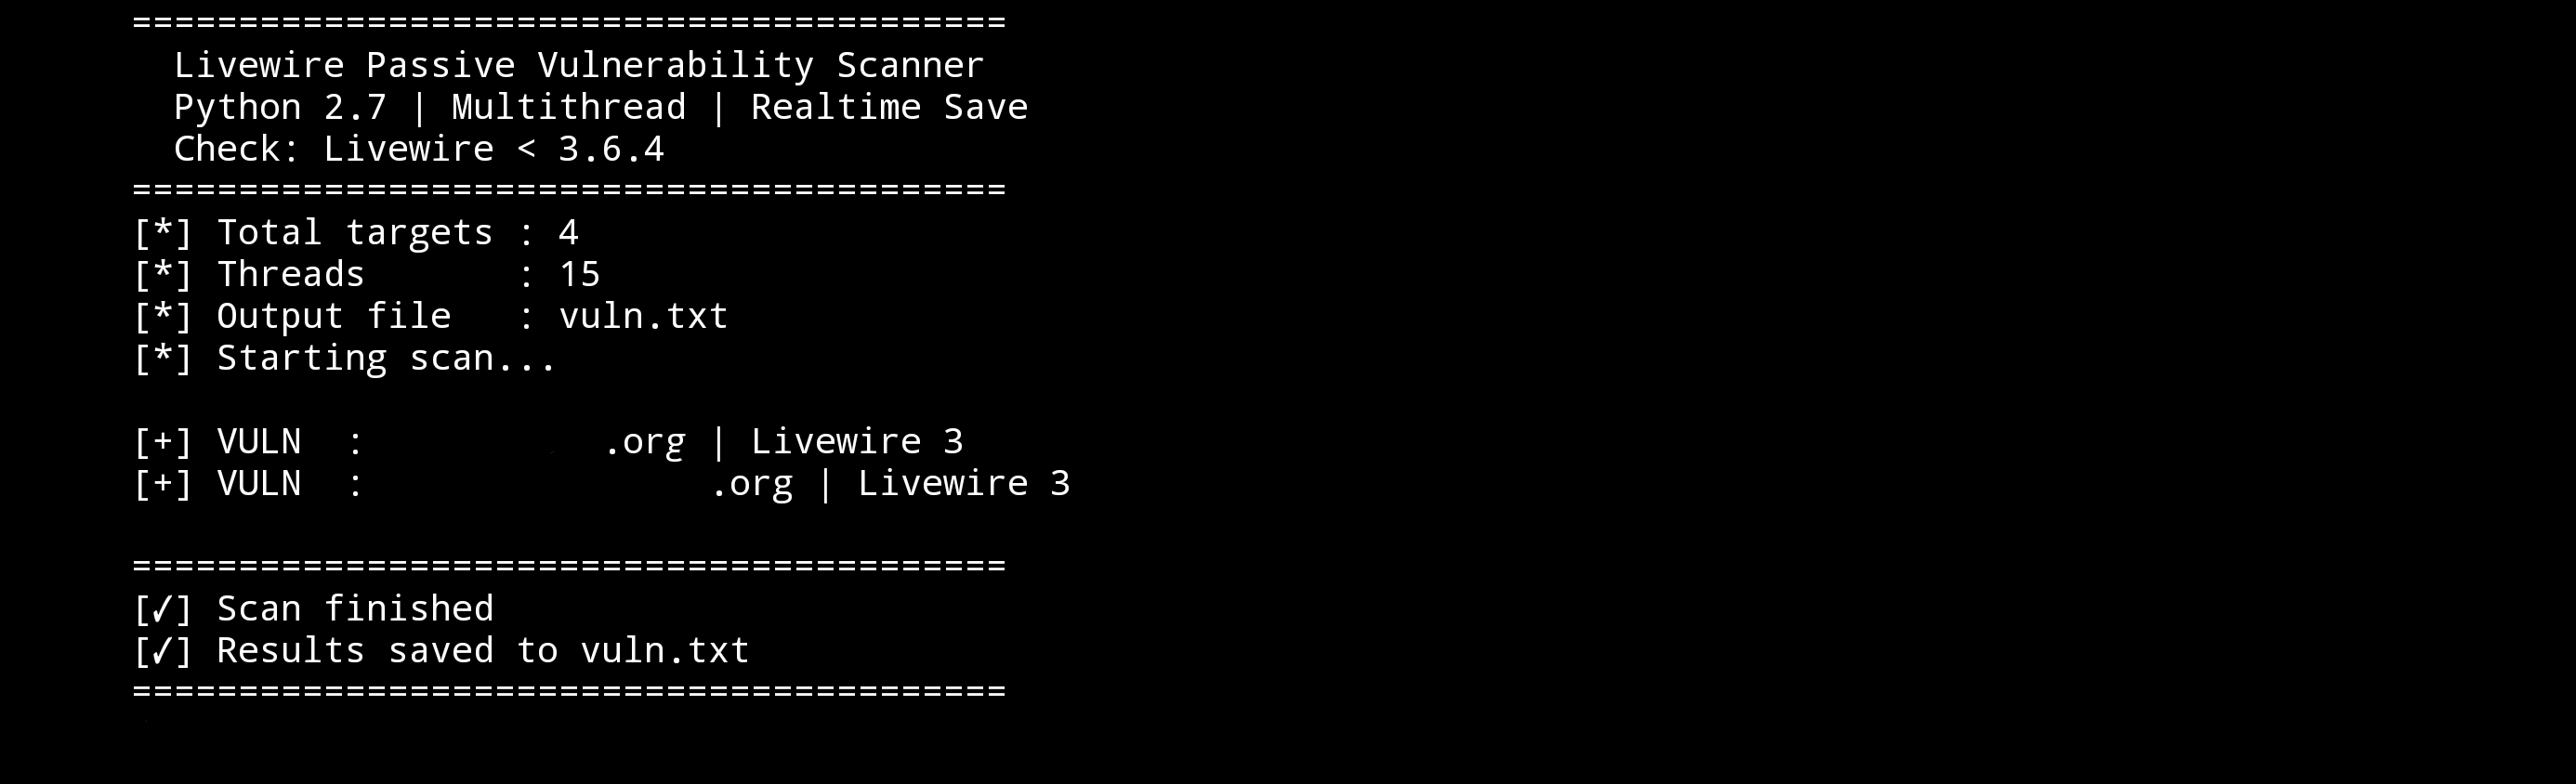 jenderal92/livewire-vuln-scanner
Simple scanner to detect vulnerable Livewire installations.
 aarocy/recon-scan
Recon-Scan: open‑source passive reconnaissance with AI‑powered security analysis. Zero‑touch, developer‑first, and privacy‑focused.
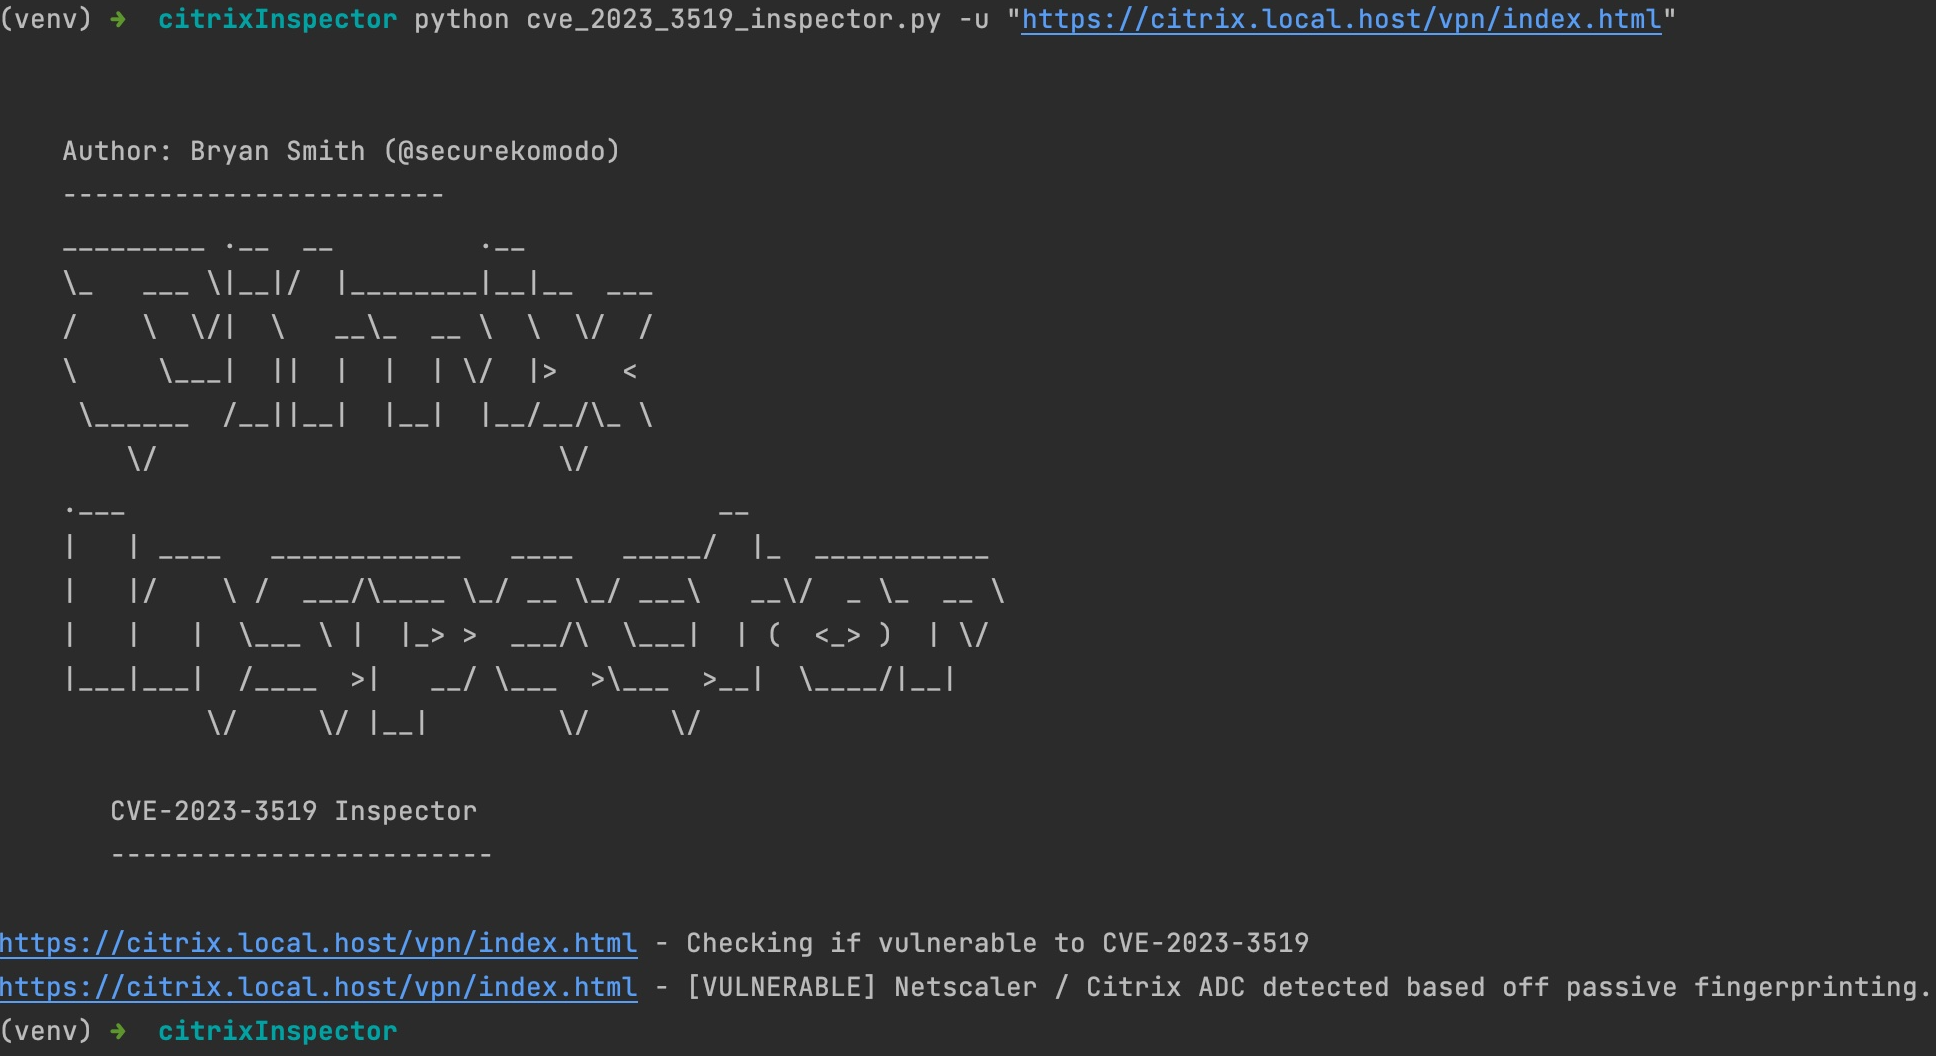 securekomodo/citrixinspector
Passively fingerprint Citrix ADC / NetScaler ADC & Gateway builds and detect known CVEs — CVE-2023-3519, CitrixBleed 2/3, CVE-2026-8452, and…
 talyx66/webfang
WEBFANG, is my first CLI, a modular OSINT & Reconnaissance toolkit curated for Ethical Hackers and Red-Teamers. Sink fangs into web targets using a…
 romanedutov/cve-2025-2294
YAML-based vulnerability scanner for CVE-2025-2294 with active and passive detection templates, enabling automated exploitation checks against Kubio…
 vighnesh91/securiscan
Standard-library Python security triage engine that scans web apps, APIs, LLMs, and mobile packages via passive header inspection, active canary…