
cve-2020-0601_poc
 gremwell/cve-2020-0601_poc
Proof-of-concept exploit for CVE-2020-0601 (Windows CryptoAPI spoofing) that generates rogue CA certificates to intercept HTTPS traffic, with…
cryptographyeducationexploitation+2
2
gremwell/cve-2020-0601_pocProof-of-concept exploit for CVE-2020-0601 (Windows CryptoAPI spoofing) that generates rogue CA certificates to intercept HTTPS traffic, with…
 parrotsec/mimikatz
Tool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…
 kevin-robertson/inveigh
.NET IPv4/IPv6 machine-in-the-middle tool for penetration testers
 funkandwagnalls/ranger
A tool for security professionals to access and interact with remote Microsoft Windows based systems.
 nettitude/sharpwsus
C# tool for lateral movement through WSUS by creating, approving, and deploying malicious updates to target Windows clients in Active Directory…
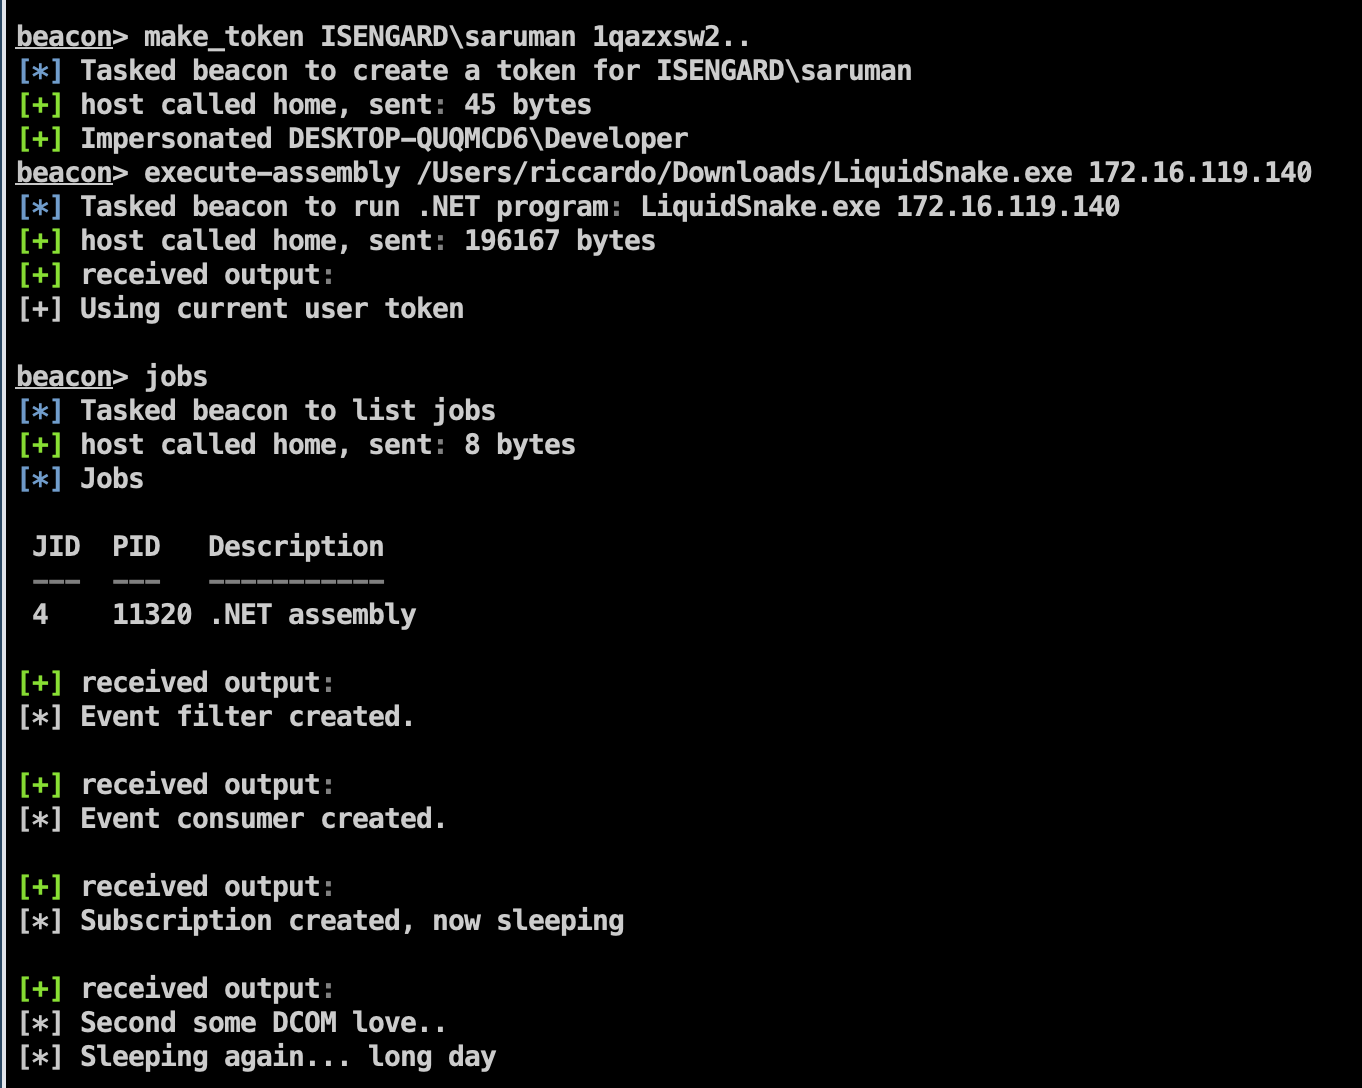 riccardoancarani/liquidsnake
Fileless lateral movement tool using WMI Event Subscriptions to execute .NET assemblies in memory, with shellcode injection via named pipes for…
 solarlynxsqueeze/cve-2026-32202
Generates malicious LNK files to coerce Net-NTLMv2 hashes via Windows Shell UNC handling, with custom SMB listener and relay integration for…
 brav0hax/smbexec
Rapid psexec-style attack tool using Samba for remote command execution, credential dumping, and lateral movement across Windows networks with hash…
 pkb1s/sharprelay
C# tool leveraging WinDivert driver to intercept and redirect Windows port 445 traffic for NTLM relay attacks via Cobalt Strike, enabling lateral…
 redteampentesting/pretender
Your MitM sidekick for relaying attacks featuring DHCPv6 DNS takeover as well as mDNS, LLMNR and NetBIOS-NS spoofing.
 decoder-it/tokenstealer
Windows token manipulation utility that lists, steals, and impersonates process or user tokens to execute commands as other users, leveraging…
 jonyfilc/printspoofer-reflectivedll
The Windows Print Spooler privilege escalation vulnerability (CVE-2019-1040/CVE-2019-1019) has been implemented as a Reflective DLL for penetration…
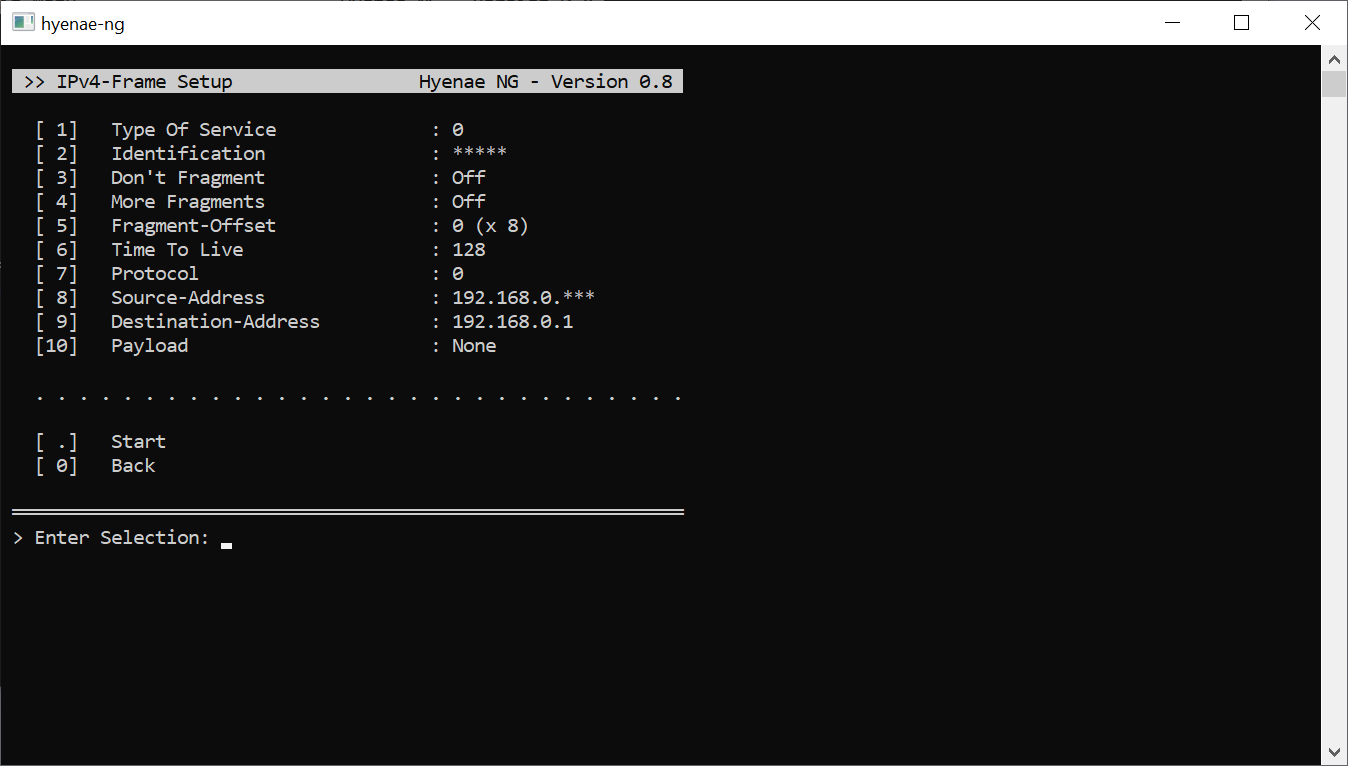 r-richter/hyenae-ng
Cross-platform network packet generator with full layer spoofing, pattern-based address randomization, and flood detection evasion for stress-testing…
 temp43487580/entrapassthecert
tool for requesting Entra ID's P2P certificate and authenticating to a remote Entra joinned devices with it
 sysdream/ligolo
Reverse Tunneling made easy for pentesters, by pentesters https://sysdream.com/
 synacktiv/prox-ez
HTTP/HTTPS interception proxy for testing Windows authentication mechanisms, supporting NTLM, Kerberos, pass-the-hash, pass-the-ticket and relay…
 glorisonlai/printnightmare
Proof-of-concept implementation of CVE-2021-34527 (PrintNightmare) for exploiting Windows Print Spooler remote code execution and privilege…
 quentinhardy/pytmipe
Python library and client for token manipulations and impersonations for privilege escalation on Windows