crlfi-scanner
CRLFISCANNER is a lightweight and powerful CLI tool designed for bug bounty hunters and penetration testers to automatically detect CRLF injection…

CRLFISCANNER is a lightweight and powerful CLI tool designed for bug bounty hunters and penetration testers to automatically detect CRLF injection…

Zeek package detecting Apache HTTP Server path traversal/RCE exploits (CVE-2021-41773, CVE-2021-42013) with payload capture and server header…

PoC exploit for CVE-2021-40346: HAProxy integer overflow enabling HTTP request smuggling and ACL bypass. Includes analysis, reproduction steps, and…

Analyzes a specific CVE in WeChat OAuth handler, identifying unbounded HTTP response reads leading to denial of service, with remediation guidance.

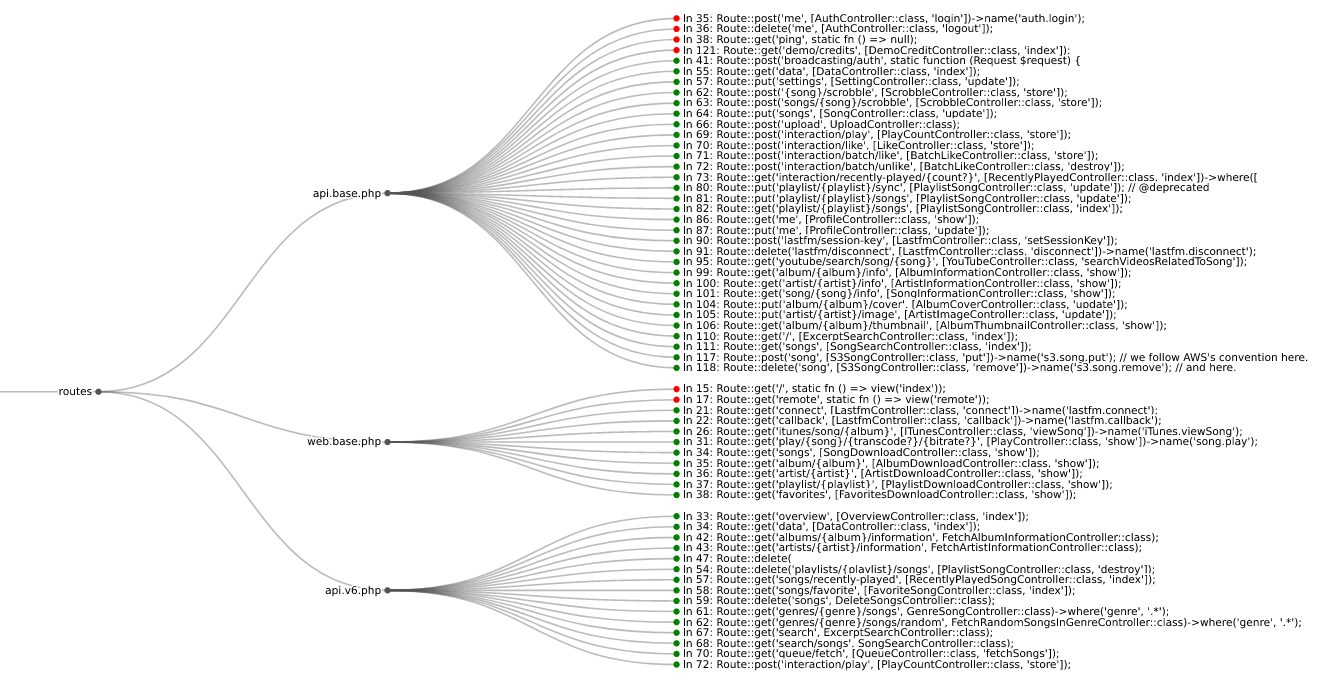
Find authentication (authn) and authorization (authz) security bugs in web application routes.

Zeek package for detecting Log4j CVE-2021-44228 exploit attempts via HTTP header payloads, LDAP Java class downloads, and second-stage Java class…

TP-Link Archer C50 V3 devices before Build 200318 Rel. 62209 allows remote attackers to cause a denial of service via a crafted HTTP Header…

PoC reproducer for CVE-2026-49099 (Apache Camel camel-salesforce): the non-Camel-prefixed sObjectQuery header escapes the HTTP header filter and…

PoC reproducer for CVE-2026-49097 (Apache Camel camel-irc): the non-Camel-prefixed irc.sendTo header escapes the HTTP header filter and overrides the…

PoC reproducer for CVE-2026-49098 (Apache Camel camel-kafka): the non-Camel-prefixed kafka.OVERRIDE_TOPIC header escapes the upstream HTTP header…

Security Advisory: HTTP Header Injection via Unvalidated CR and LF in Header Values (tiny_http)

This repository provides a PoC for CVE-2017-5638, a remote code execution vulnerability in Apache Struts 2, exploitable via a crafted Content-Type…

Proof-of-concept demonstrating SSRF and HTTP header injection in KubePlus ResourceComposition, enabling cloud metadata access and IAM credential…

A proof of concept for CVE-2025-31161, using mangled HTTP header to perform unauthenticated impersonation of any user in Crush FTP server.

Simulates CVE-2025-29927, a critical Next.js vulnerability allowing attackers to bypass middleware authorization by exploiting the internal…

Behavior-preserving fix for CVE-2025-60876 HTTP header injection in BusyBox wget, with proof-of-concept, percent-encoding patch, and upstream…

PoC and lab environment for CVE-2023-25950: HTTP request smuggling via malformed header fields in HAProxy's HTTP/3 implementation, enabling DoS and…

Reproducer for CVE-2026-46453 — Apache Camel camel-elasticsearch-rest-client unprefixed-header injection (operation/query override via inbound HTTP…