
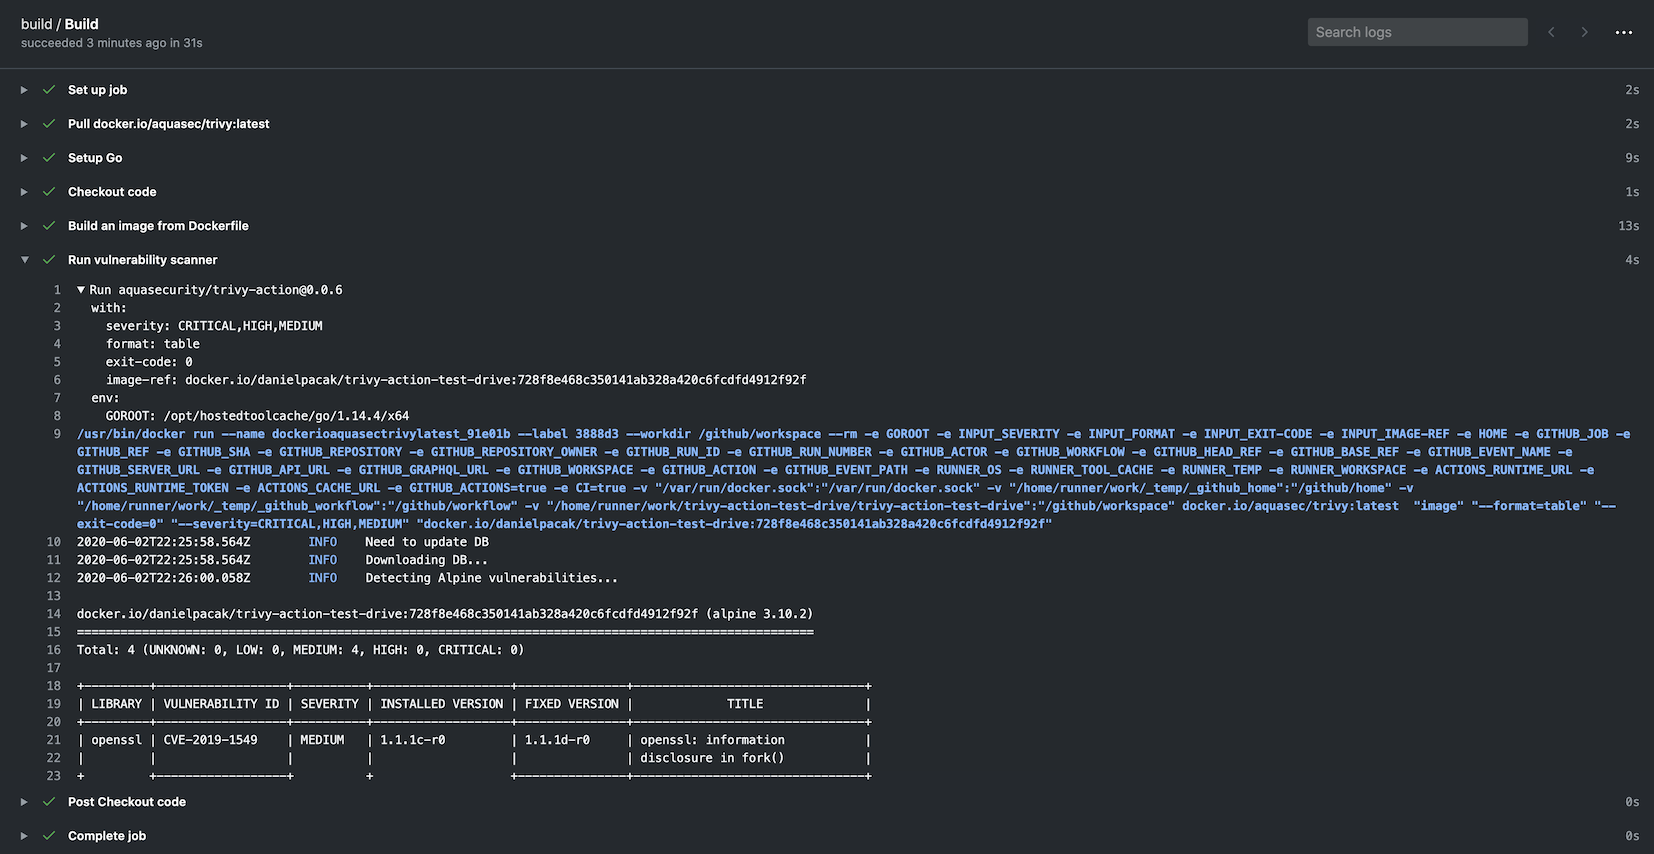
trivy-action
 aquasecurity/trivy-action
Runs Trivy as GitHub action to scan your Docker container image for vulnerabilities
cloud-securitycode-analysiscontainer-security+5
1.5k
aquasecurity/trivy-actionRuns Trivy as GitHub action to scan your Docker container image for vulnerabilities
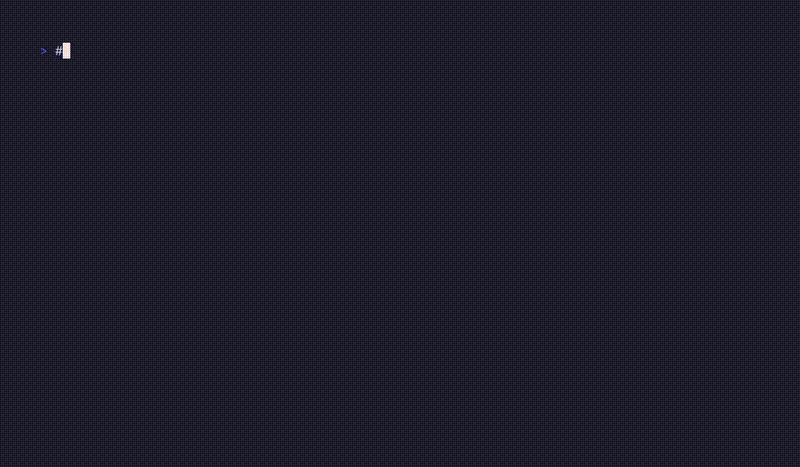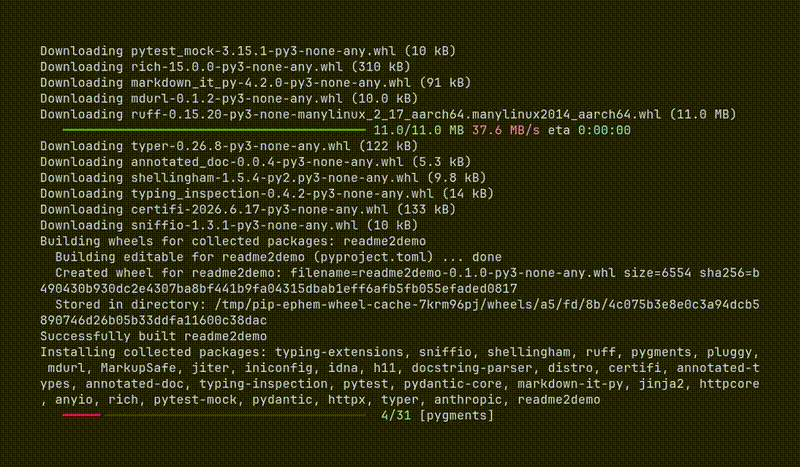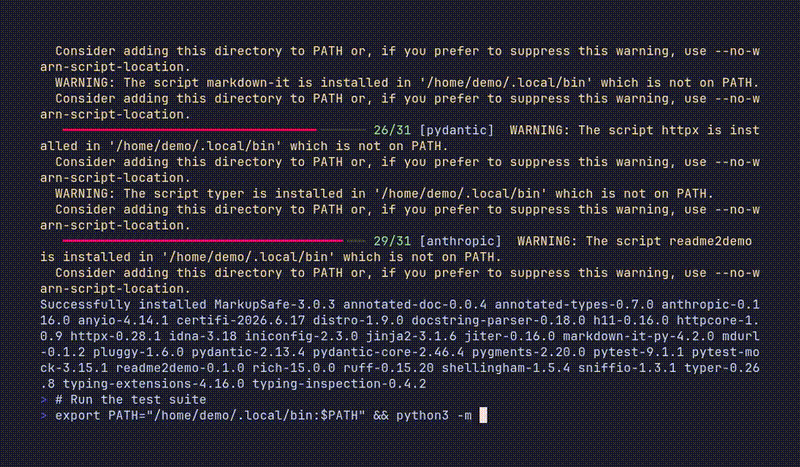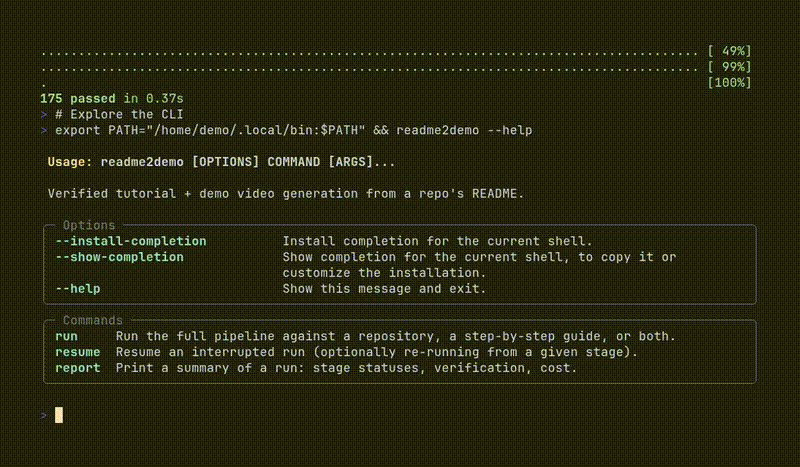 alphacrack/readme2demo
Verified tutorials and demo videos from your README. An AI agent runs it in a hardened Docker sandbox and replays it in a fresh container before…
 cdxgen/cdxgen
Creates CycloneDX Bill of Materials (BOM) for your projects from source and container images. Supports many languages and package managers. Integrate…
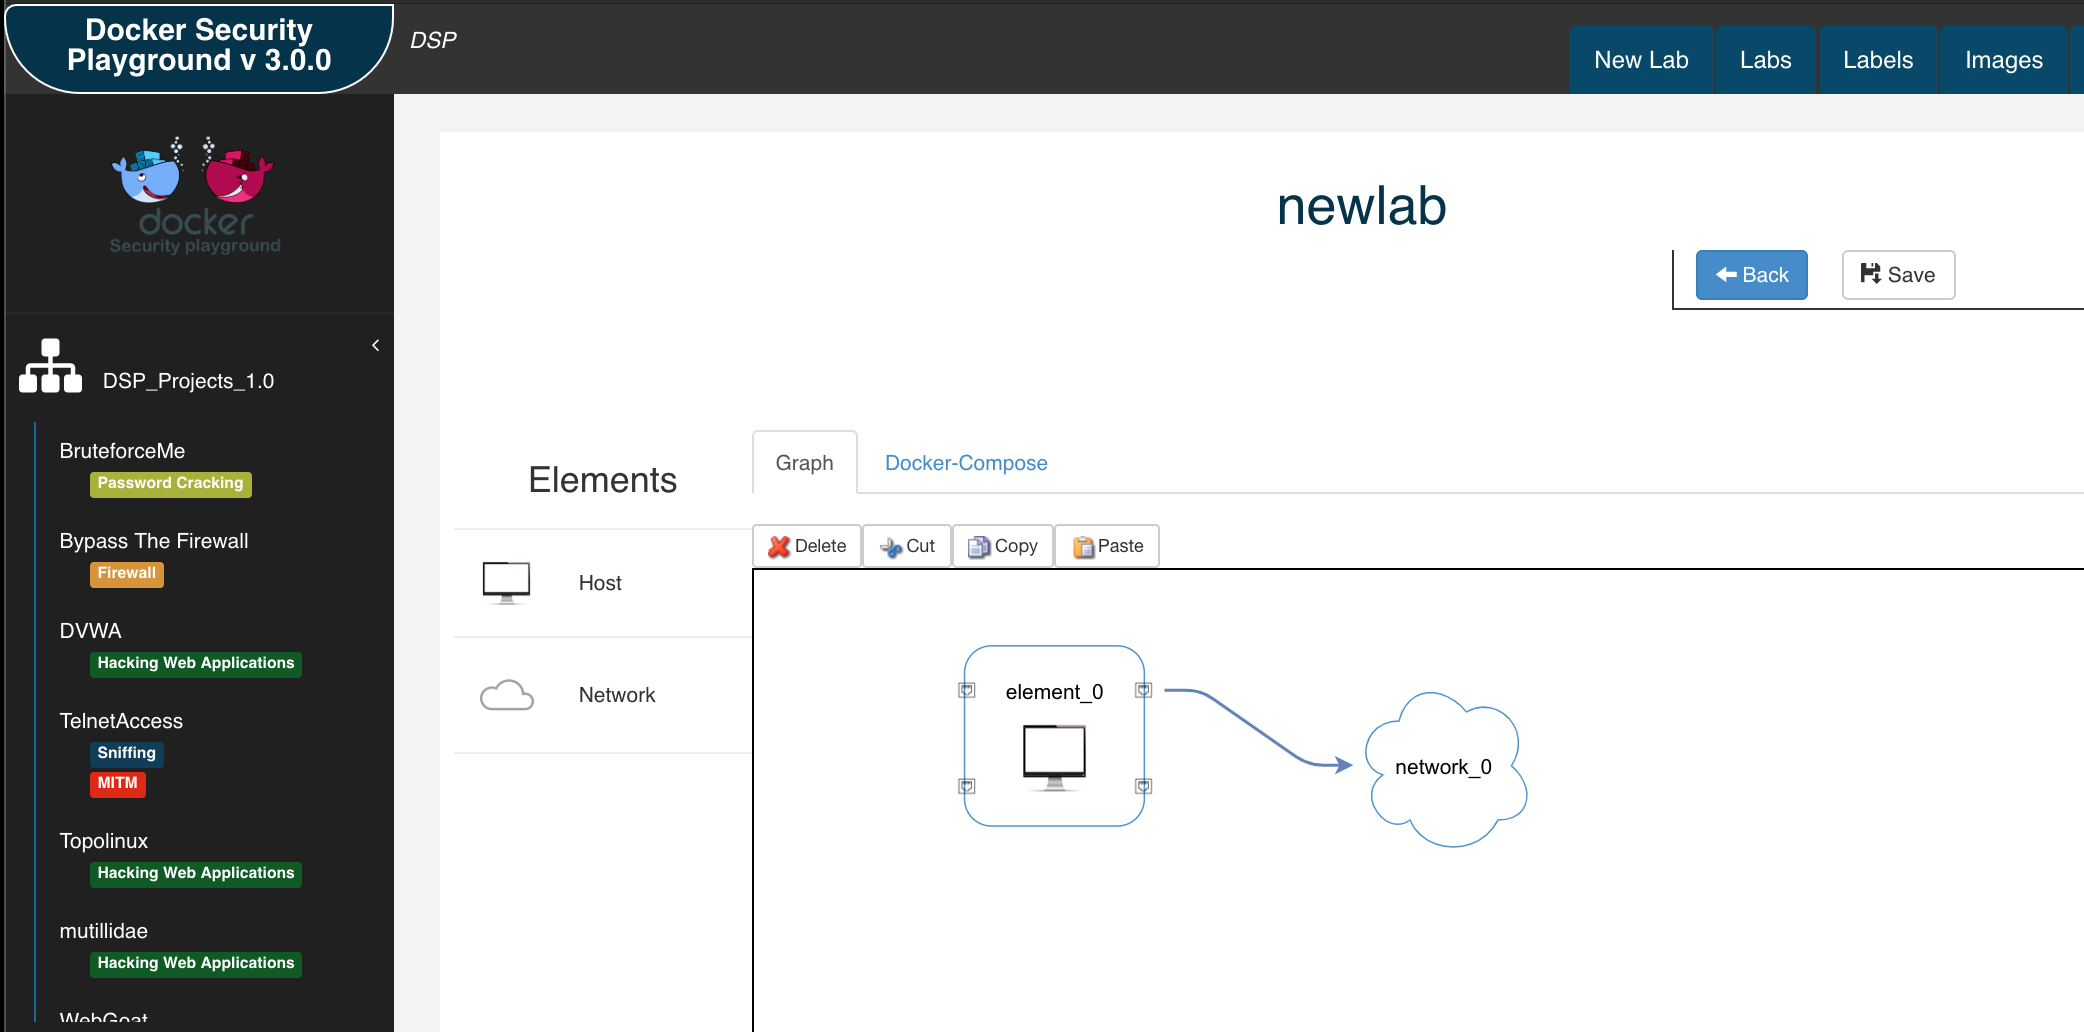 dockersecurityplayground/dsp
A Microservices-based framework for the study of Network Security and Penetration Test techniques
 alegrey91/vex8s
Suppress vulnerabilities applying Kubernetes context to scans
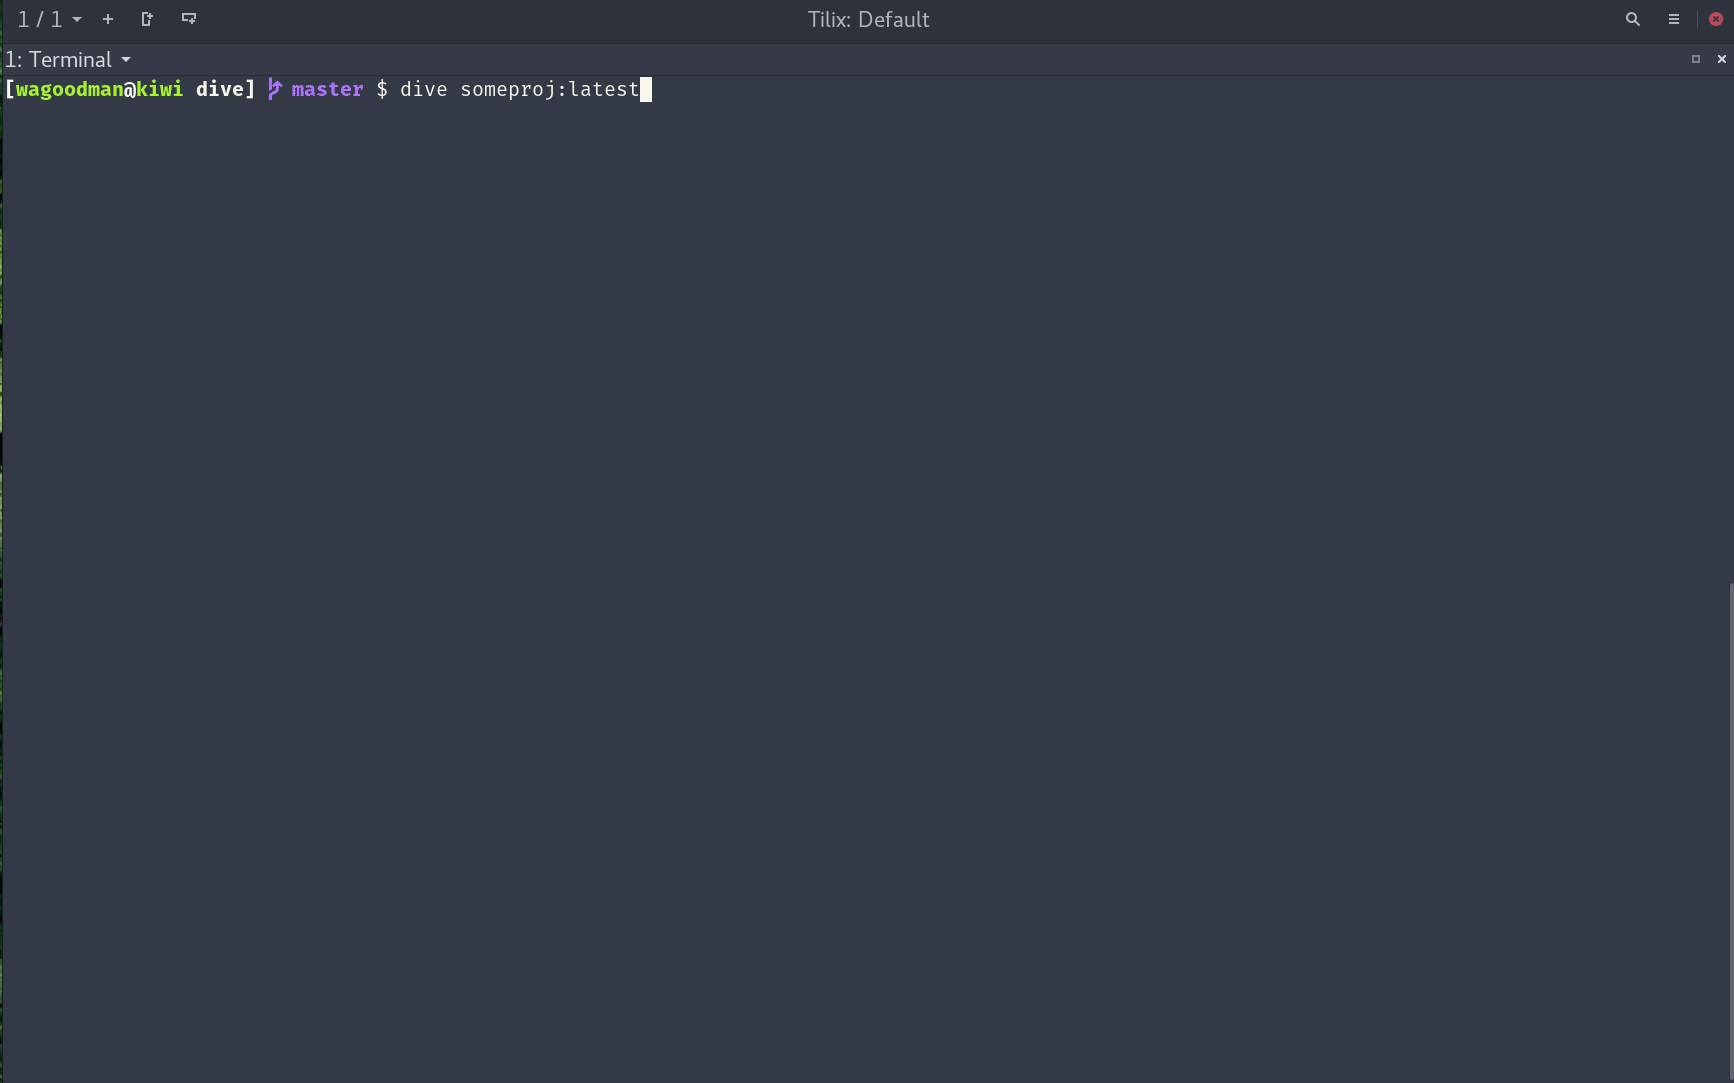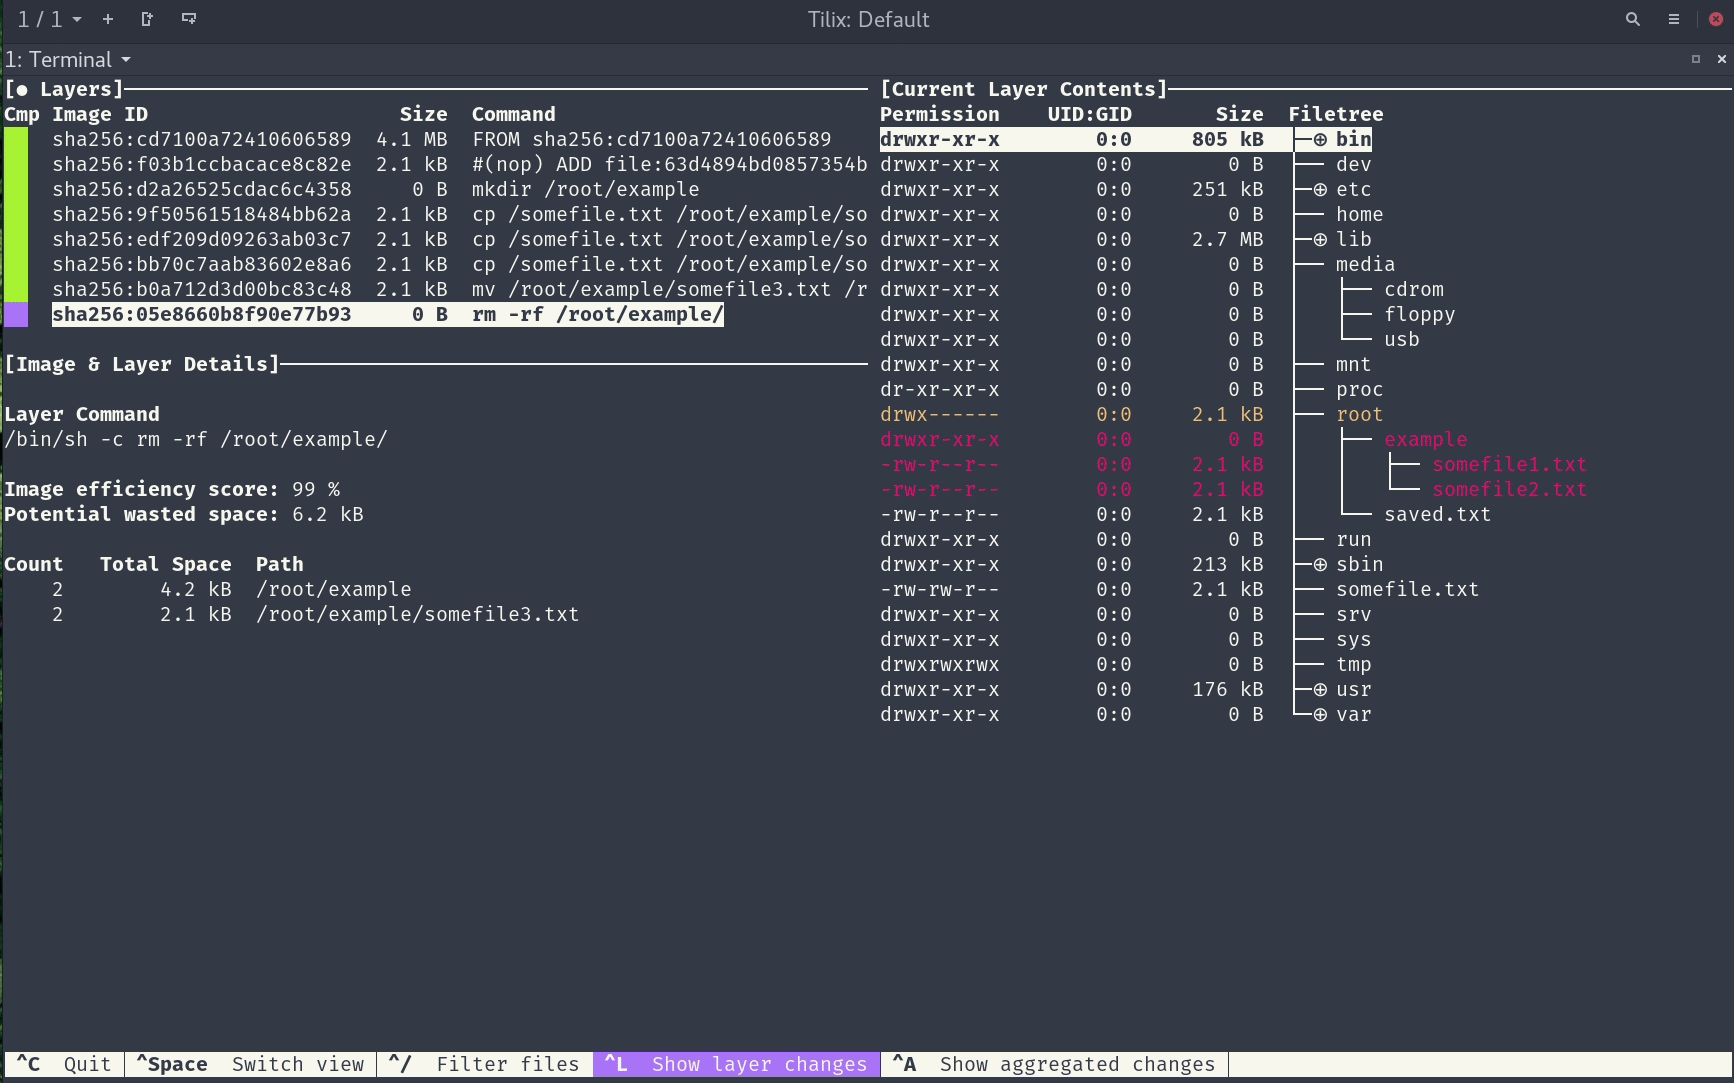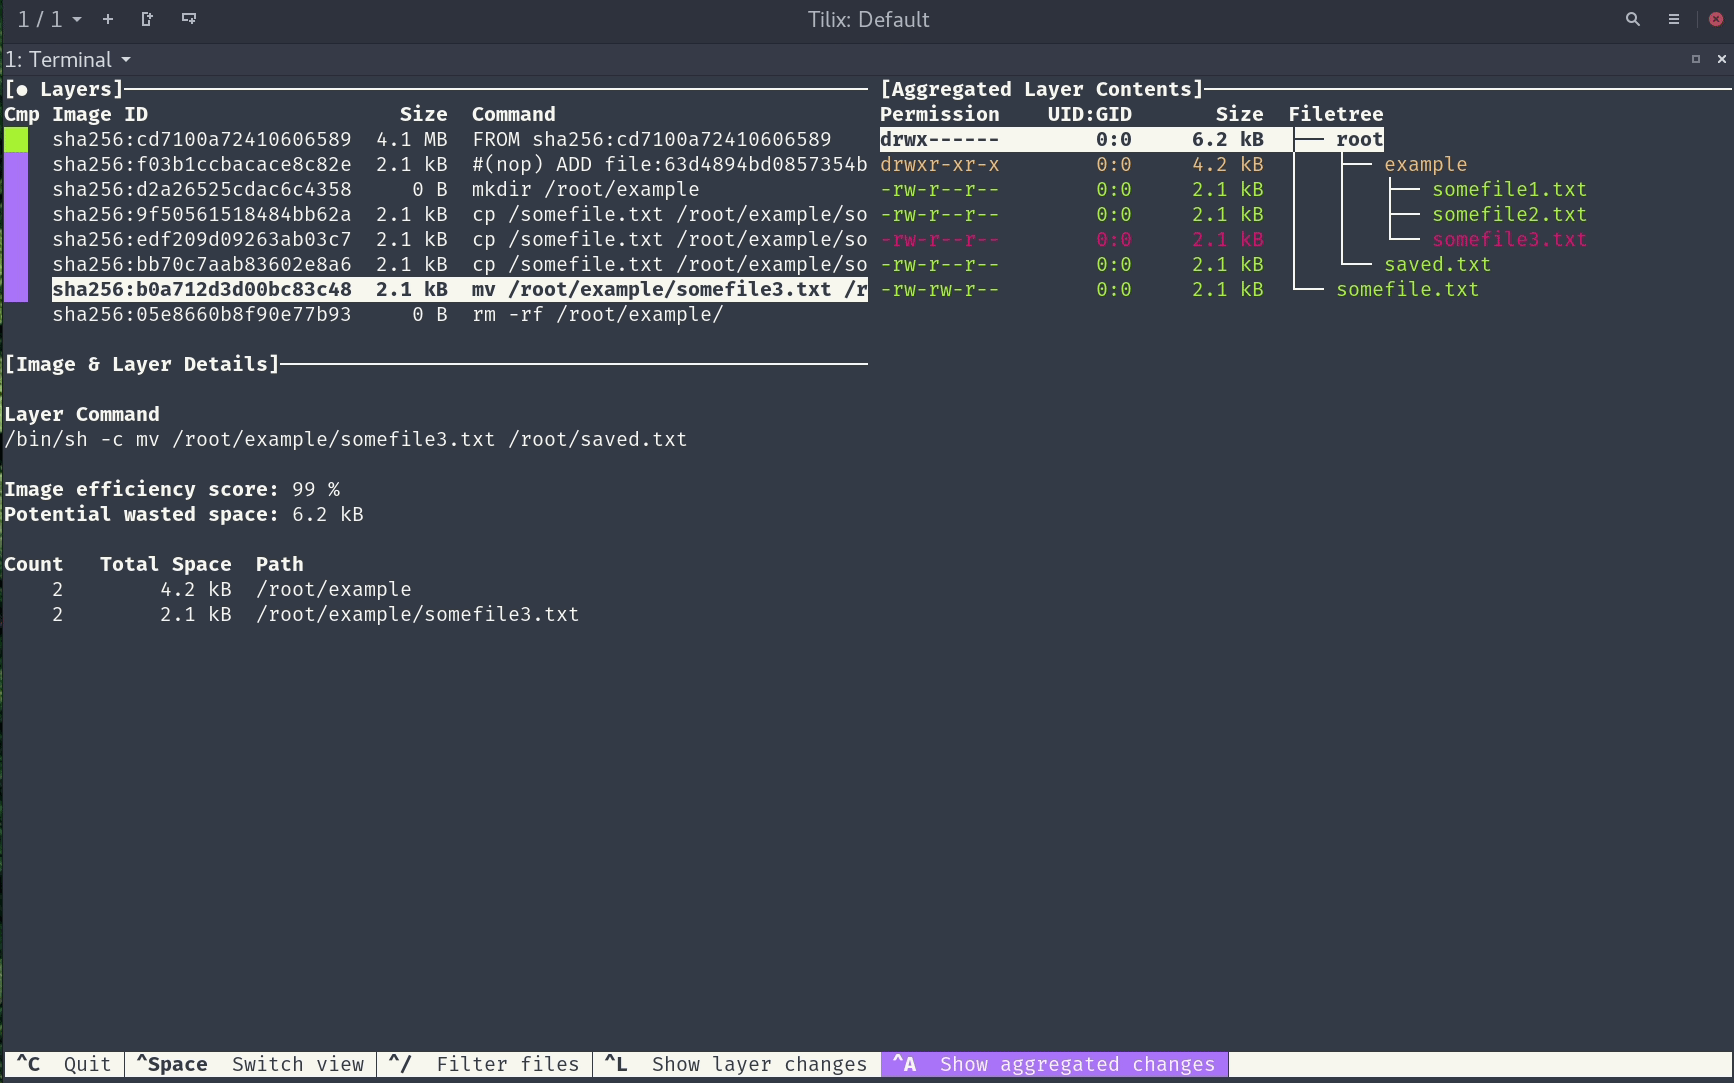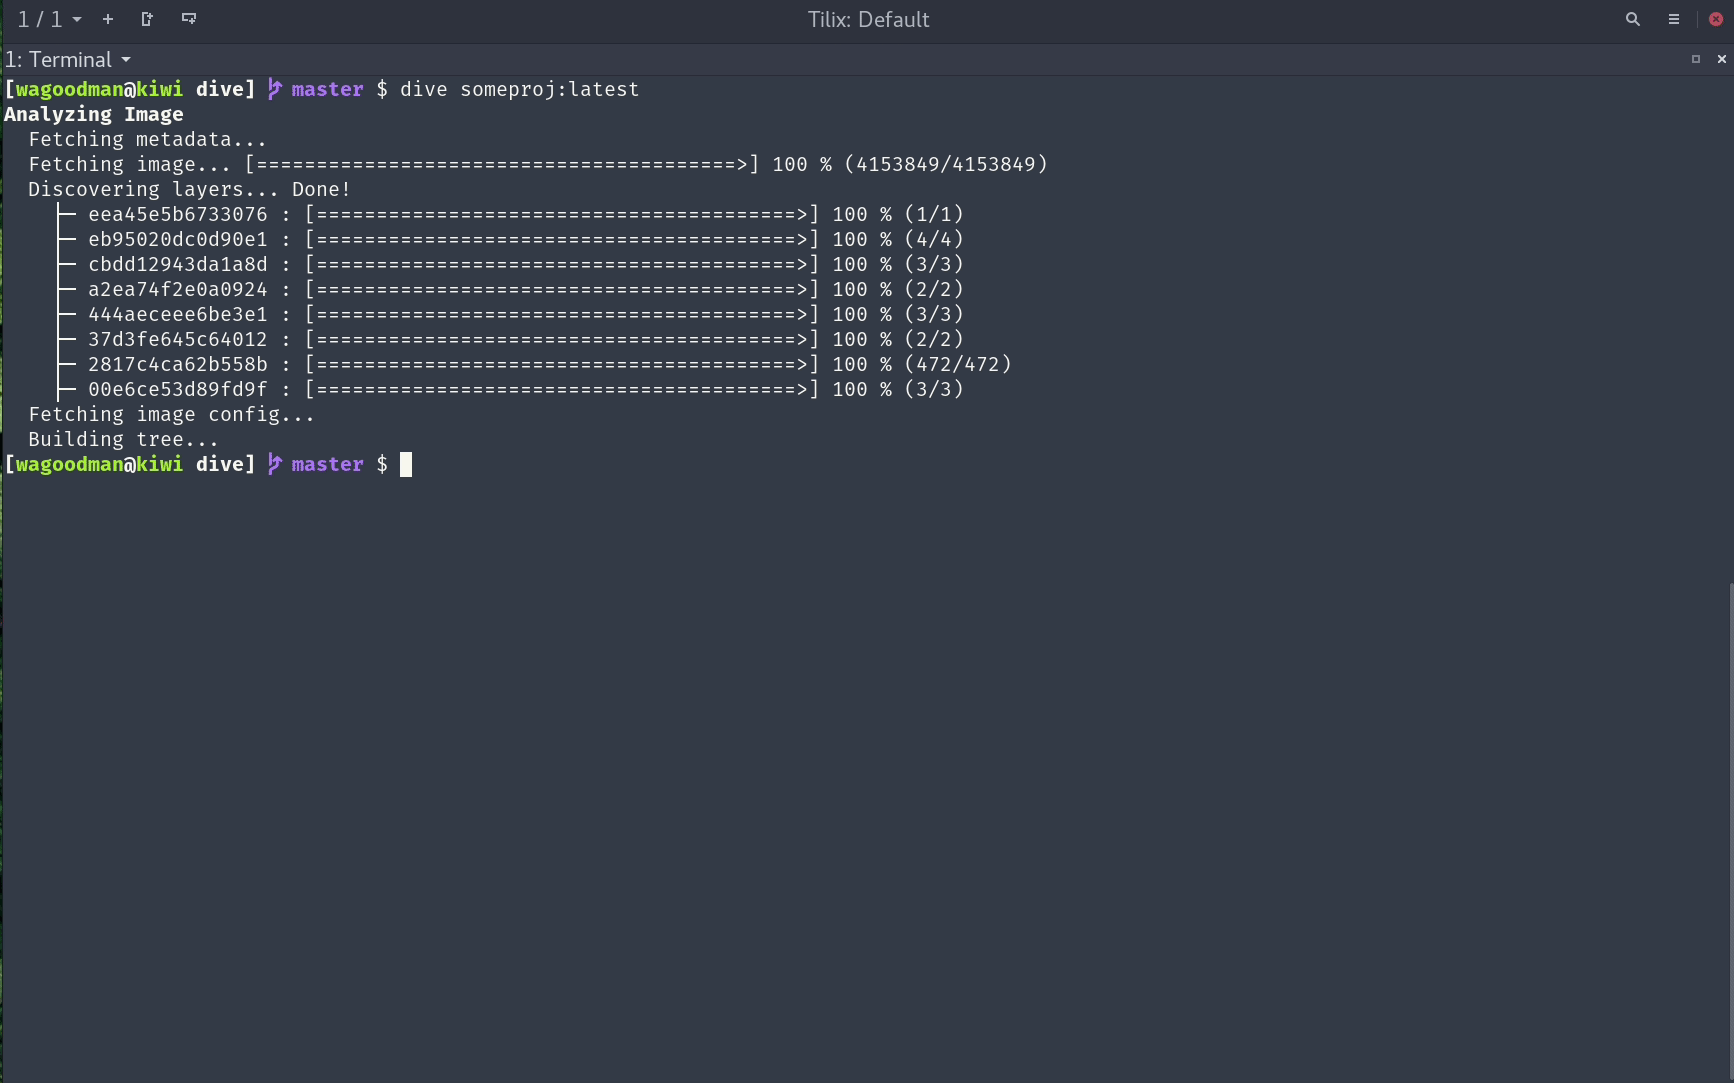 wagoodman/dive
A tool for exploring each layer in a docker image
 ivankovic/stop-bots
Automate stopping bad bots from accessing your server
 otsmane-ahmed/ci-supplychain-guard
Static analysis tool that detects malicious dependencies in CI/CD pipelines using pattern matching and AST analysis, with a traffic-light risk…
 gensecaihq/react2shell-scanner
Detects CVE-2025-55182 RCE in React Server Components by scanning npm/pnpm/yarn lockfiles, Docker images, SBOMs, and live URLs. Includes auto-fix,…
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 msaad00/agent-bom
Open-source cloud and AI security platform: scan code, dependencies, containers, cloud and AI agents/MCP into one security graph. Self-host free in…
 mathaix/openclawmachines
Manage OpenClaw in your team (Enterprise) by providing it compute infrastructure, tool integration, Authentication and security primitives
 controlplaneio/simulator
Kubernetes Security Training Platform - focusing on security mitigation
 kubeshop/testkube
☸️ The Open Testing Platform for AI-Driven Engineering Teams
 finbarr/yolobox
Let your AI go full send. Your home directory stays home.
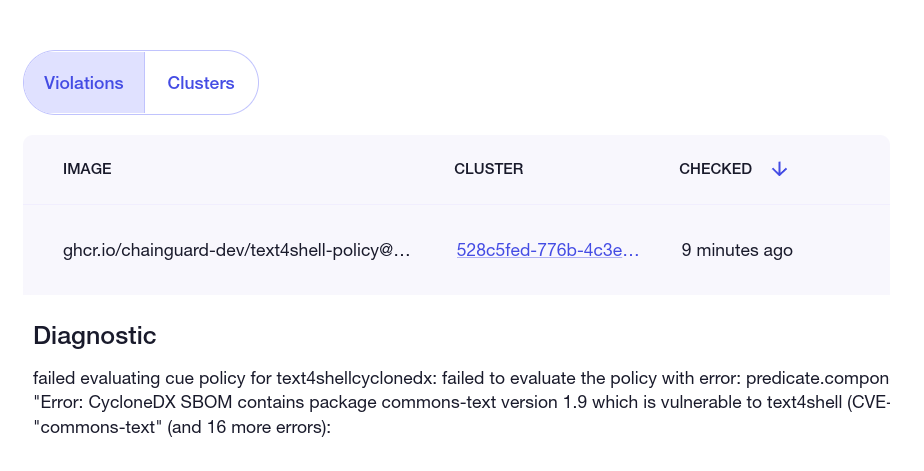 chainguard-dev/text4shell-policy
ClusterImagePolicy demo for cve-2022-42889 text4shell
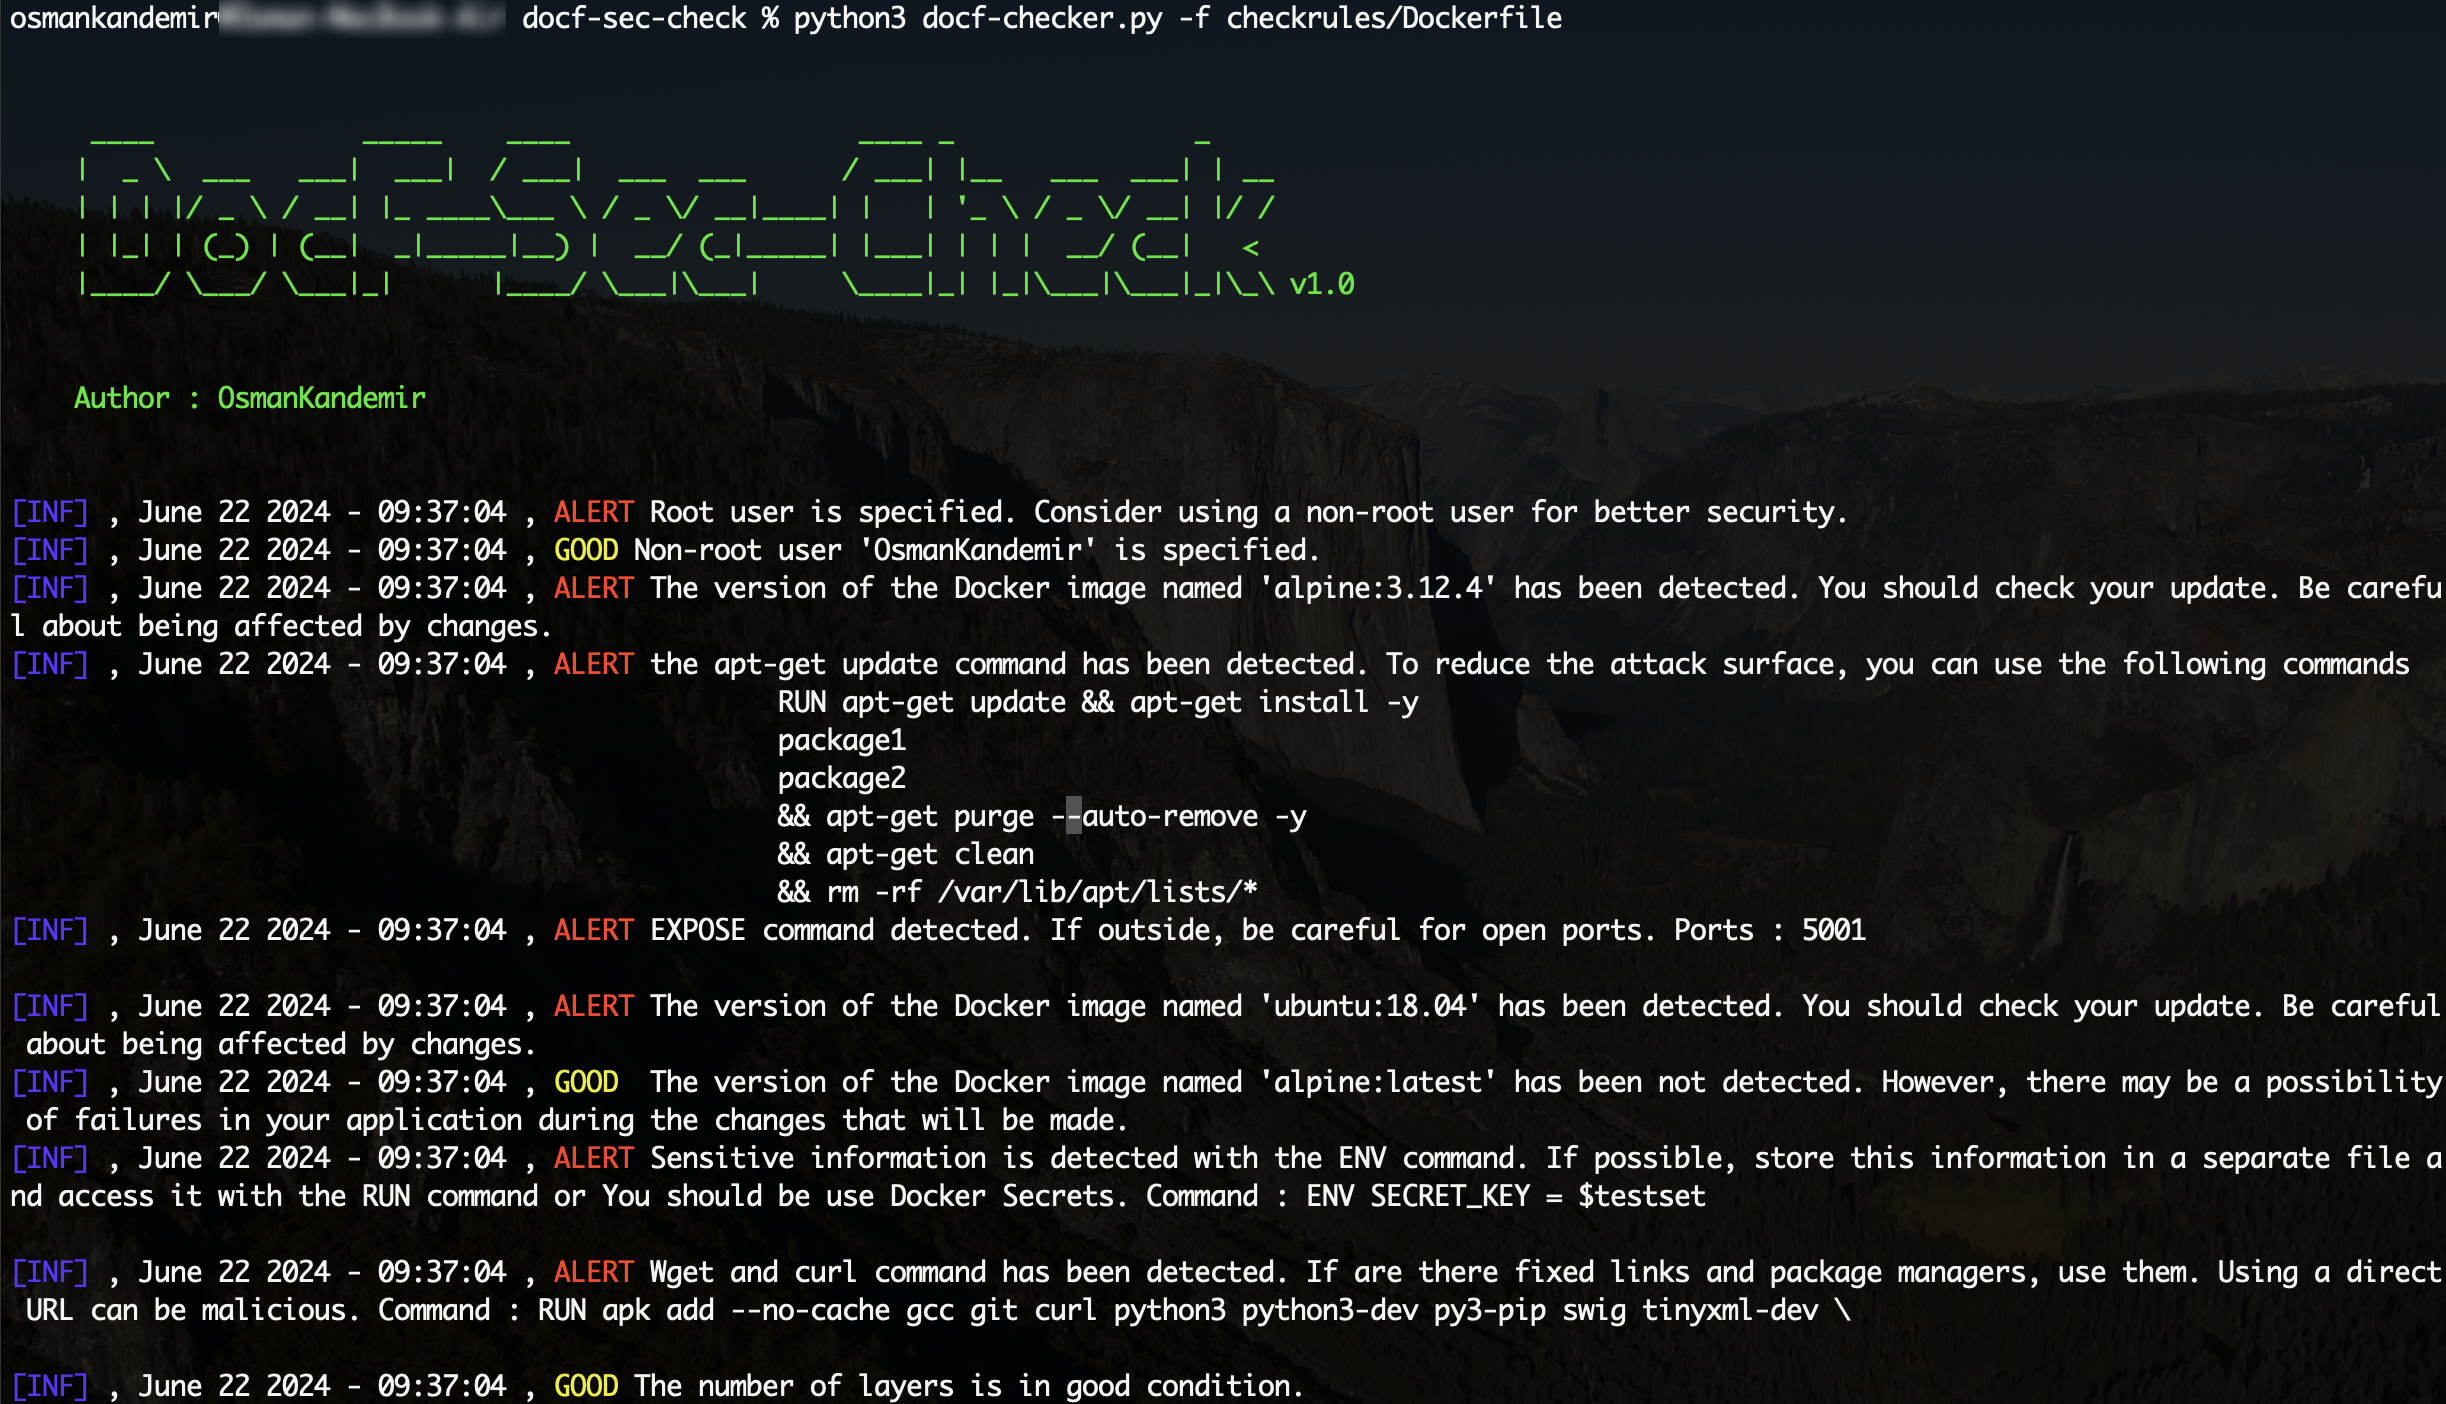 osmankandemir/docf-sec-check
Static analysis tool that scans Dockerfiles for insecure commands and configuration issues, providing actionable security notifications to harden…
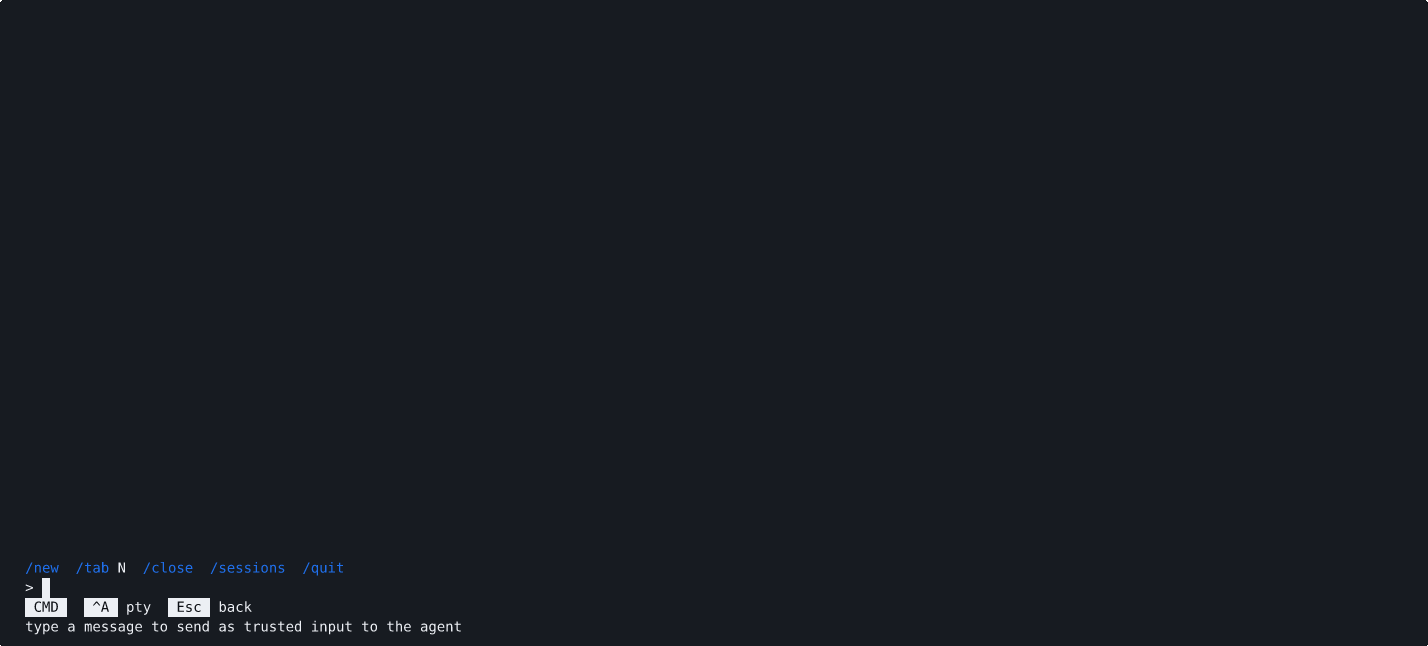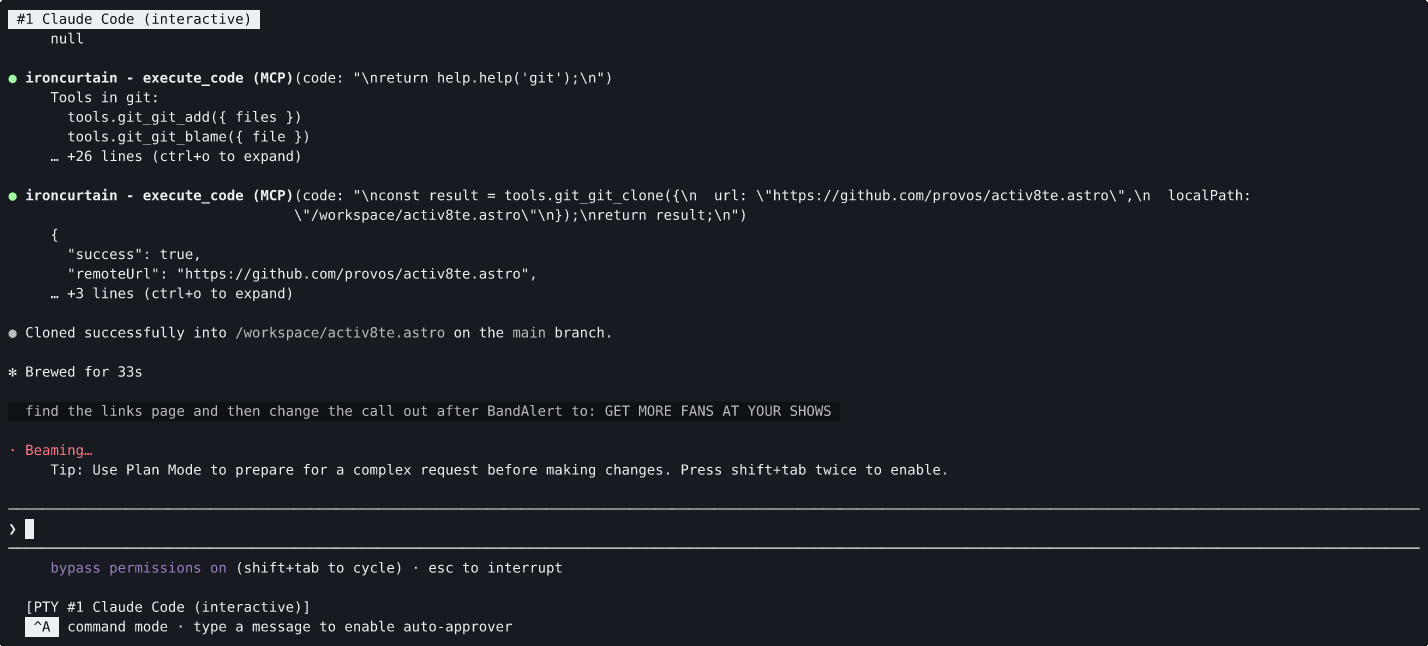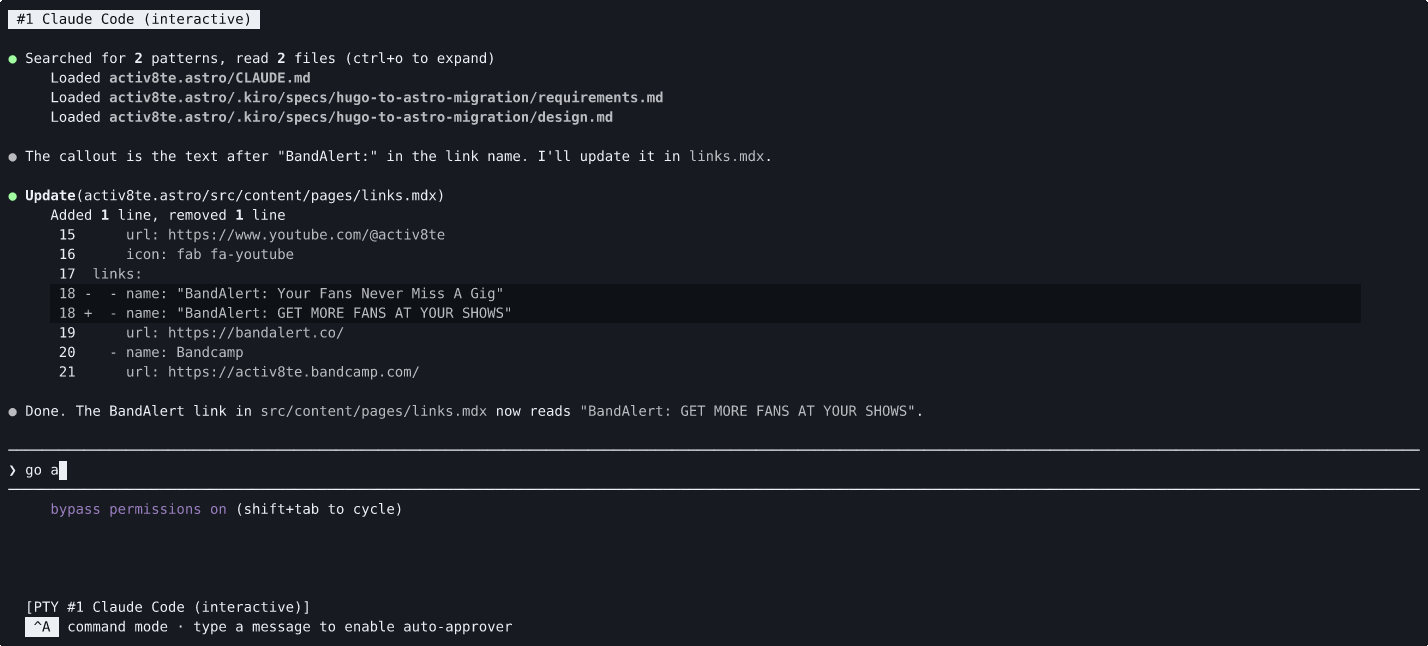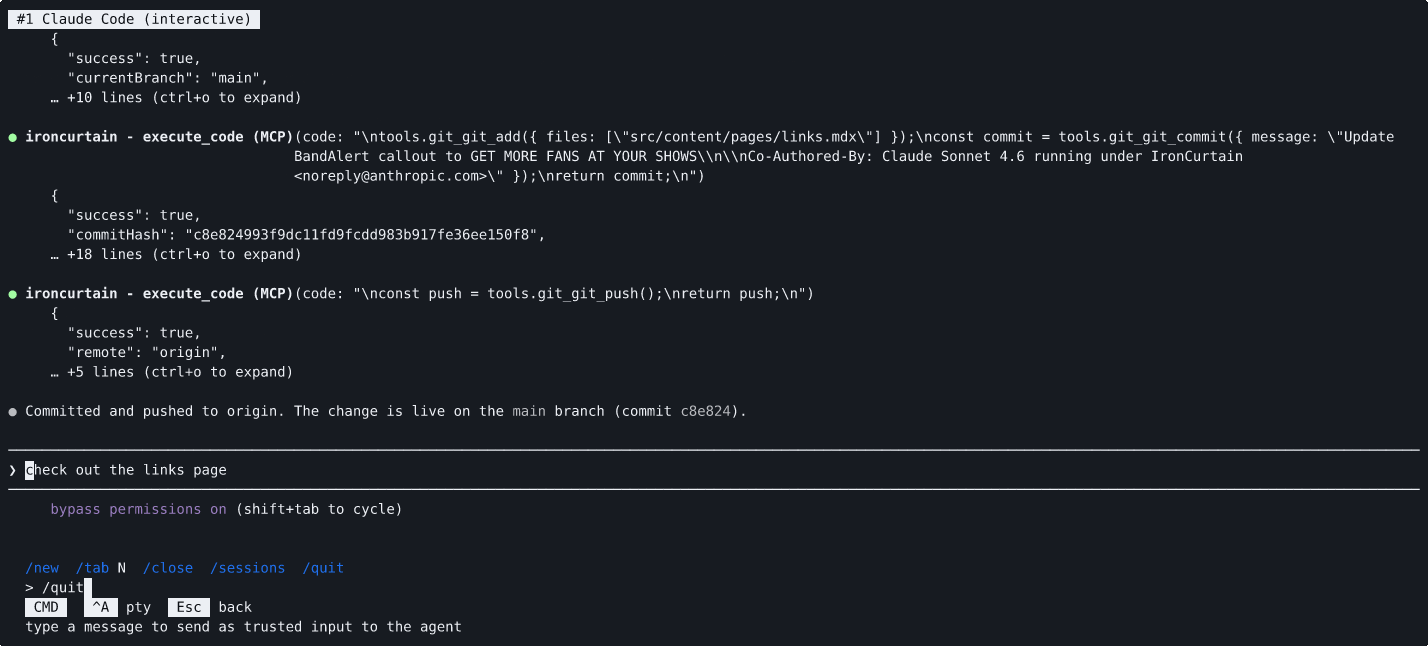 provos/ironcurtain
A secure* runtime for autonomous AI agents. Policy from plain-English constitutions. (*https://ironcurtain.dev)