
CVE-2026-1208
 snailsploit/cve-2026-1208
Friendly Functions for Welcart <= 1.2.5 - Cross-Site Request Forgery to Settings Update
educationexploitationpapers-research+3
snailsploit/cve-2026-1208Friendly Functions for Welcart <= 1.2.5 - Cross-Site Request Forgery to Settings Update
 0xdtc/prestashop-cve-2024-34716
Automates a CSRF attack against CVE-2024-34716 to deploy a PHP reverse shell on PrestaShop, with automated payload packaging and Netcat listener…
 v1n1v131r4/exploit-csrf-on-scopia-xt-desktop-version-8.3.915.4
Proof of concept demonstrating Cross-Site Request Forgery (CSRF) on Avaya SCOPIA XT Desktop, allowing admin password change without anti-CSRF token.
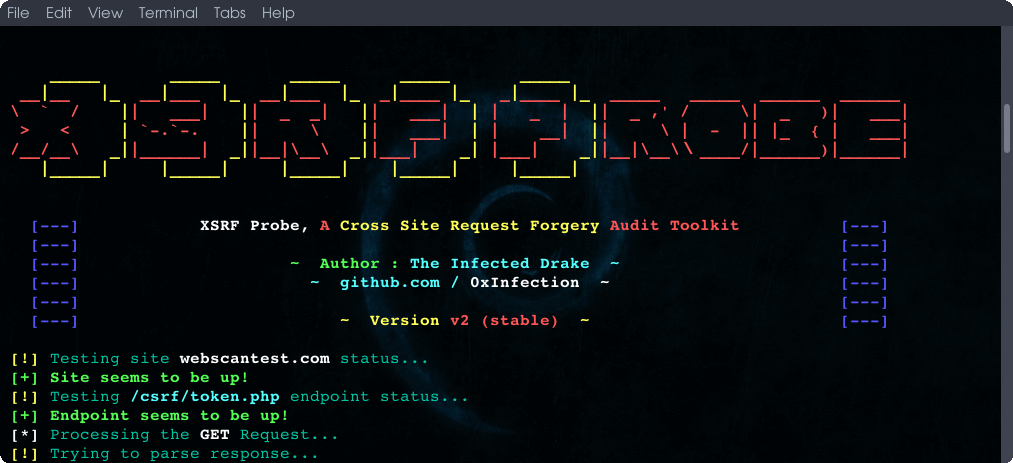 0xinfection/xsrfprobe
The Prime Cross Site Request Forgery (CSRF) Audit and Exploitation Toolkit.
 sybelle03/cve-2021-43617
This is a reproduction of PHP Laravel 8.70.1 - Cross Site Scripting (XSS) to Cross Site Request Forgery (CSRF) vulnerability
 sanupl/cve-2021-46080
CVE-2021-46080 - A Cross Site Request Forgery (CSRF) vulnerability exists in Vehicle Service Management System 1.0. An successful CSRF attacks leads…
 sanupl/vehicle-service-management-system-multiple-cross-site-request-forgery-csrf-leads-to-xss
CVE-2021-46080 - A Cross Site Request Forgery (CSRF) vulnerability exists in Vehicle Service Management System 1.0. An successful CSRF attacks leads…
 ahrixia/cve-2023-44811
mooSocial v3.1.8 is vulnerable to Cross Site Request Forgery (CSRF) which allows attacker to change admin password.
 cypherdavy/cve-2025-29722
Cross Site Request Forgery (CSRF) in Commercify v1.0
 nxploited/cve-2025-31033
WordPress Buddypress Humanity Plugin <= 1.2 is vulnerable to Cross Site Request Forgery (CSRF)
 mehdi-ben-hamou/cve-2026-30498
Educational CSRF vulnerability demonstration with a controlled lab environment, including a proof-of-concept exploit and a fixed version with proper…
 mbadanoiu/cve-2021-46366
CVE-2021-46366: Credential Bruteforce Attack via CSRF + Open Redirect in Magnolia CMS
 electronicbots/cve-2021-31762
Exploiting a Cross-site request forgery (CSRF) attack to creat a new privileged user through the Webmin's add users feature
 sahiloj/cve-2023-34839
CVE-2023-34839 is a Cross-Site Request Forgery (CSRF) vulnerability discovered in Issabel PBX version 4.0.0-6, a widely used open-source Unified…
 mesh3l911/cve-2021-31760
Exploiting a Cross-site request forgery (CSRF) attack to get a Remote Command Execution (RCE) through the Webmin's running process feature
 nixon-h/cve-2025-68434-ospos-csrf
PoC & Write-up for CVE-2025-68434: Critical CSRF in OpenSourcePOS. Exploits a disabled filter configuration to allow unauthenticated attackers to…
 electronicbots/cve-2021-31760
Exploiting a Cross-site request forgery (CSRF) attack to get a Remote Command Execution (RCE) through the Webmin's running process feature
 nxploited/cve-2025-1306
Newscrunch <= 1.8.4 - Cross-Site Request Forgery to Arbitrary File Upload