
frida-wshook
 oalabs/frida-wshook
Script analysis tool based on Frida.re
dynamic-analysis-sandboxingmalware-analysisscripting-automation
oalabs/frida-wshookScript analysis tool based on Frida.re
 aetsu/neton
Agent-based tool that collects OS, hardware, file, and hook data from internet-connected sandboxes via HTTPS exfiltration, aiding Red Team artifact…
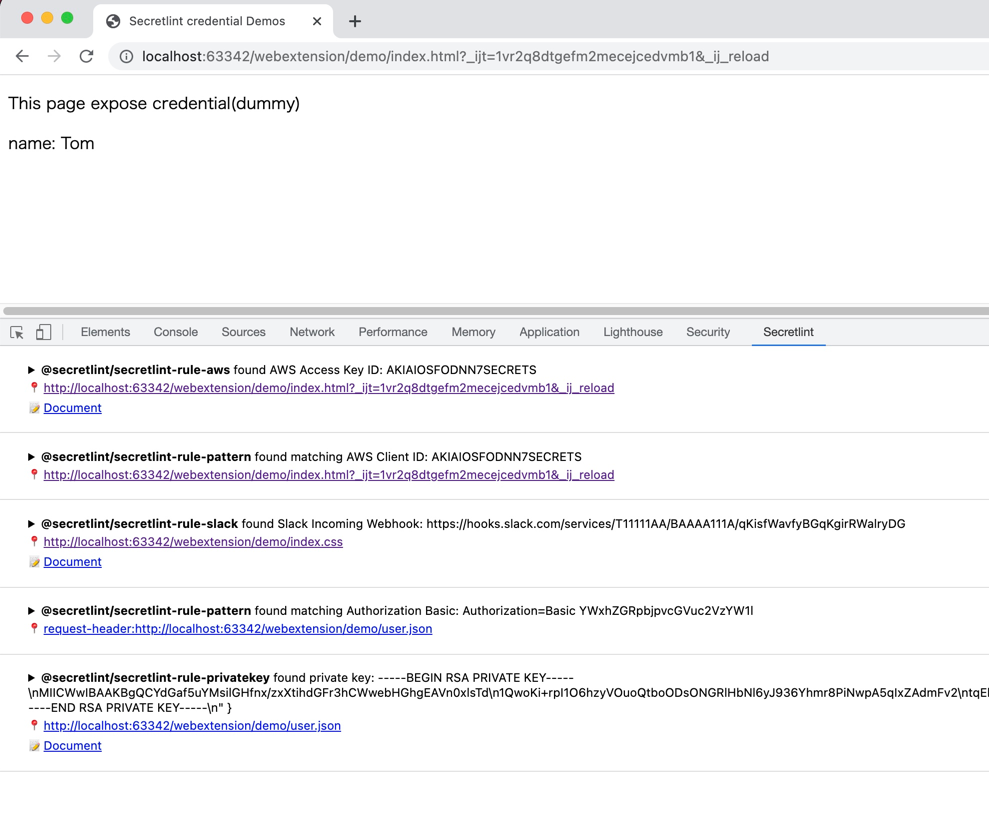 secretlint/secretlint
Pluggable linting tool to prevent committing credential.
 abhishek2512mishra/claude-code-security-audit
Security scanner auditing Claude Code environments for CVE-2026-21852 pre-trust execution, hook hijacking, and eBPF lockdown.
 reversenseorg/dexcalibur
[Official] Android reverse engineering tool focused on dynamic instrumentation automation leveraging Frida. It disassembles dex, analyzes it…
 forrest-orr/artifacts-kit
Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.
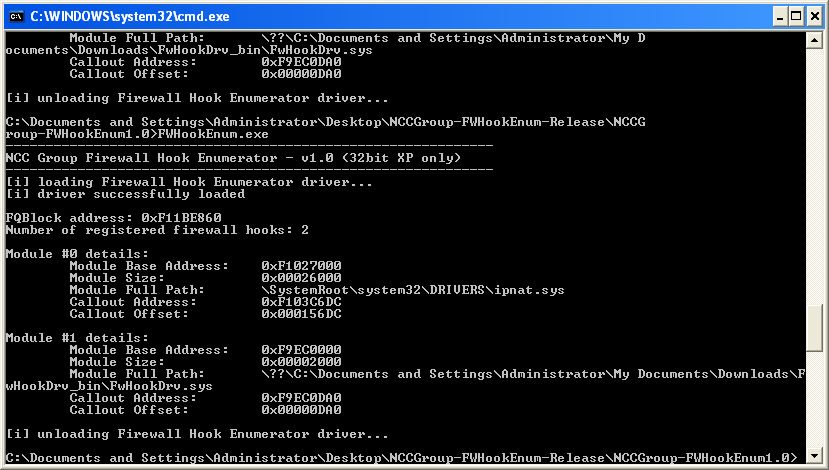 nccgroup/windowsfirewallhookdriverenumeration
Tools to enumerate Windows Firewall Hook Drivers on Windows 2000, XP and 2003
 gmh5225/iat-hook
C++ DLL that performs Import Address Table hooking by parsing PE headers and redirecting imported function addresses to a custom hook inside a target…
 nishitm/gobox
GO sandbox to run untrusted code
 pietroborrello/customprocessingunit
The first analysis framework for CPU microcode
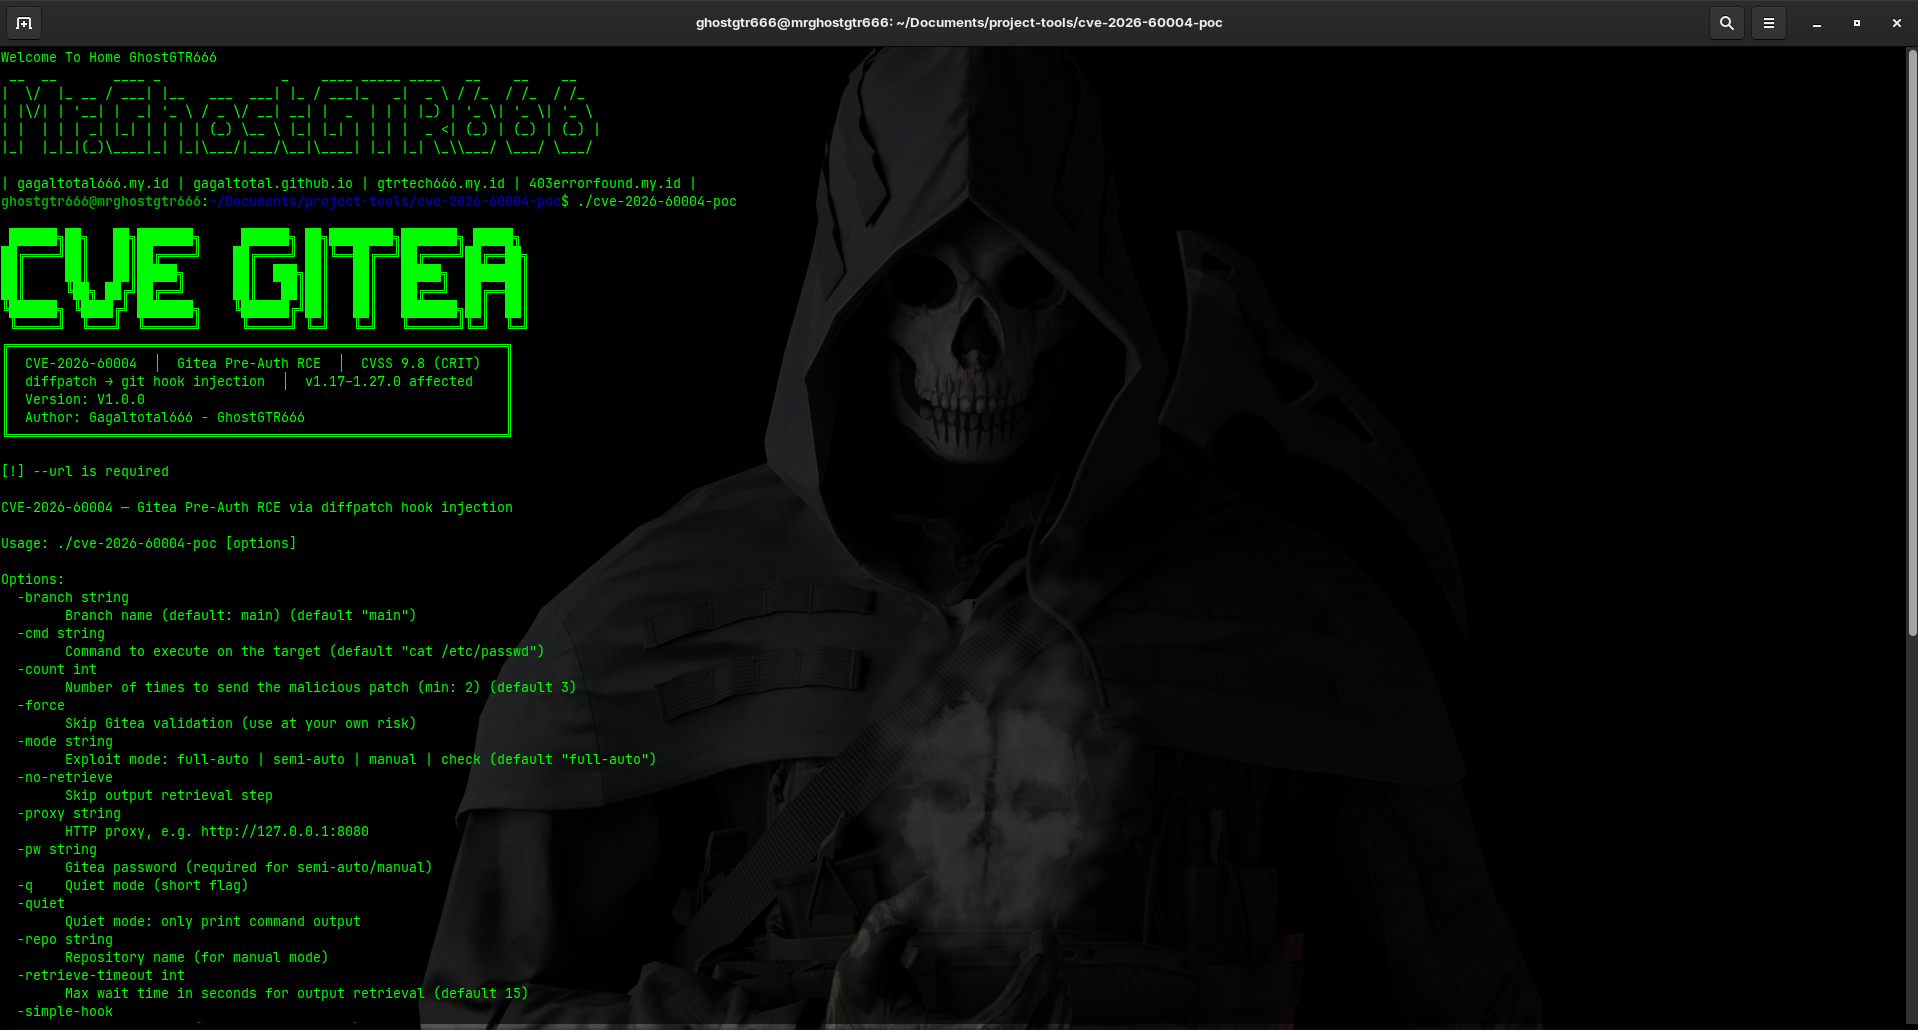 gagaltotal/cve-2026-60004-poc-gitea
CVE-2026-60004 — Gitea Pre-Auth RCE via diffpatch hook injection
 hwbp/clr-unhook
Modern security products (CrowdStrike, Bitdefender, SentinelOne, etc.) hook the nLoadImage function inside clr.dll to intercept and scan in-memory…
 kevoreilly/capev2
Malware Configuration And Payload Extraction
 nehkark/cve-2025-10230
CVE-2025-10230 PoC - Samba WINS Hook Command Injection
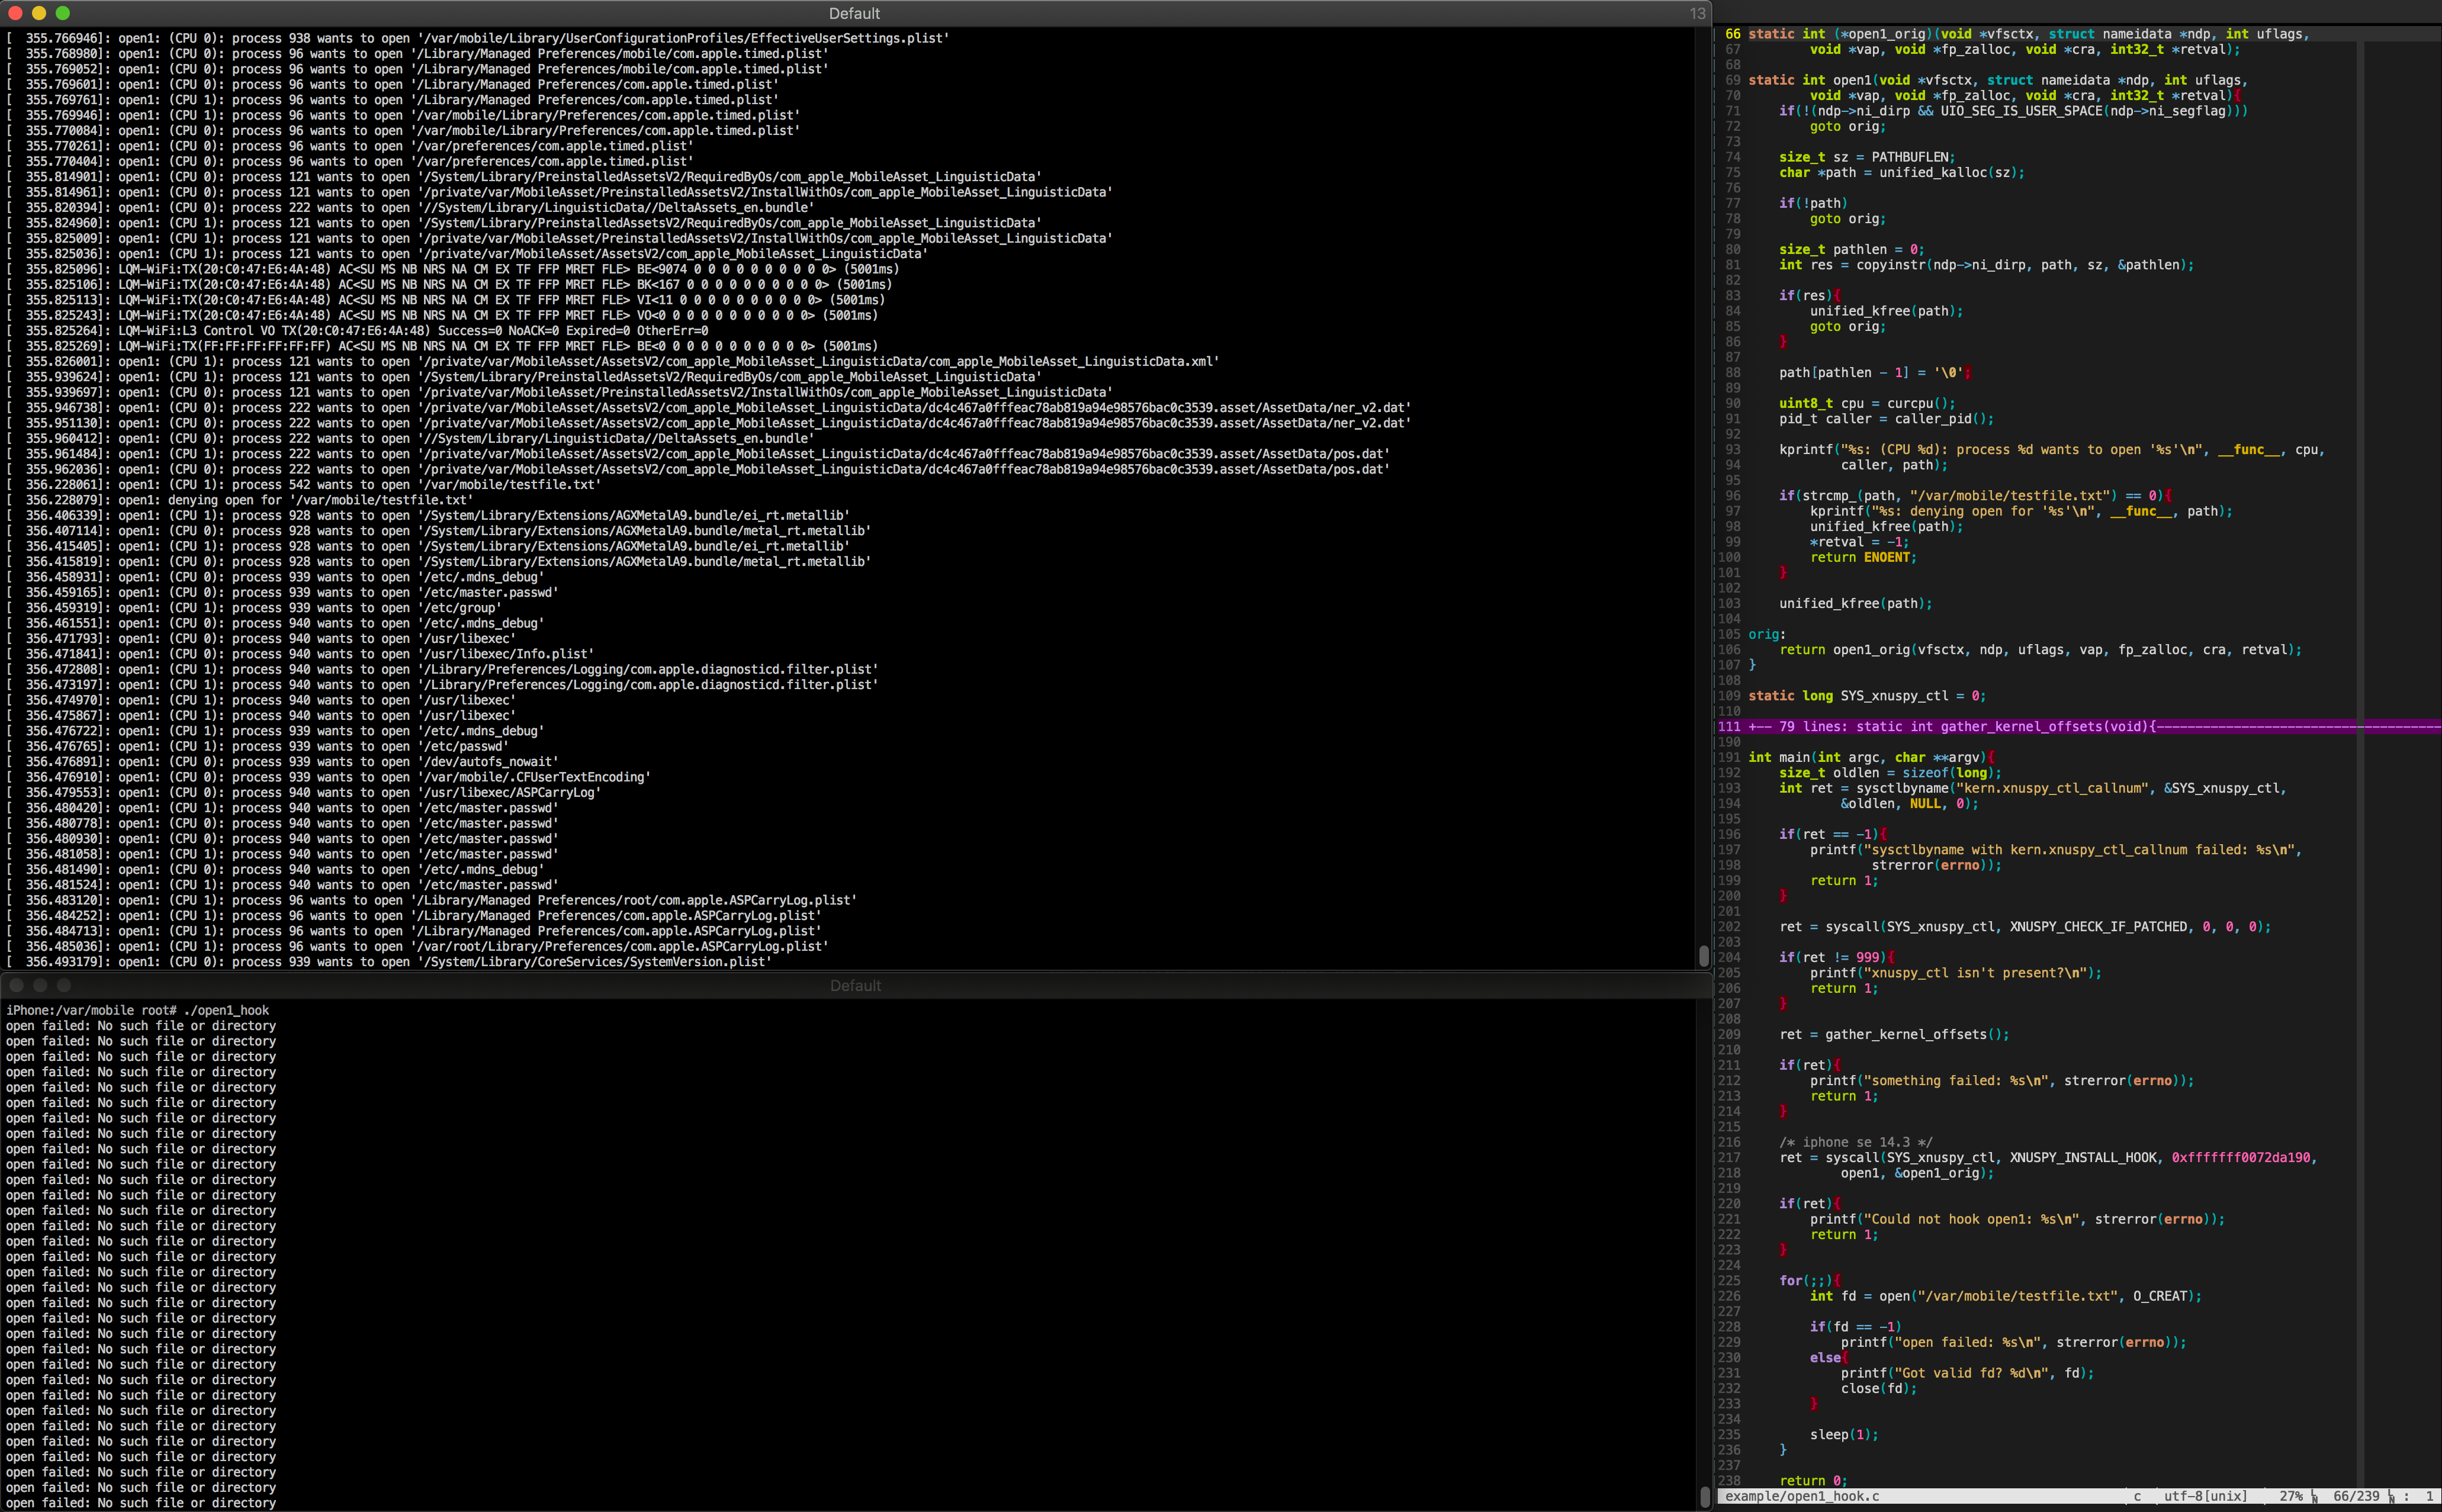 jsherman212/xnuspy
an iOS kernel function hooking framework for checkra1n'able devices
 swdunlop/andbug
Scriptable debugger for Android Dalvik VM using JDWP/DDM interfaces to hook methods, inspect process state, and modify runtime behavior without…
 do4choo/cve-2026-3227-tp-link-authenticated-rce
Proof-of-concept for authenticated OS command injection in TP-Link router firmware. Includes decryption, QEMU-based encryption hook, and 15-character…
 vichhka-git/renef-skills
Agent Skill for operating renef.io — Android ARM64 dynamic instrumentation: hook native/Java, patch memory, trace syscalls, bypass SSL pinning/root…