
chimera
 1neptune/chimera
Rust-based DLL hijacking loader for MobaXterm (CVE-2026-6421) with persistence
binary-exploitationexploitationpayload-development+4
1neptune/chimeraRust-based DLL hijacking loader for MobaXterm (CVE-2026-6421) with persistence
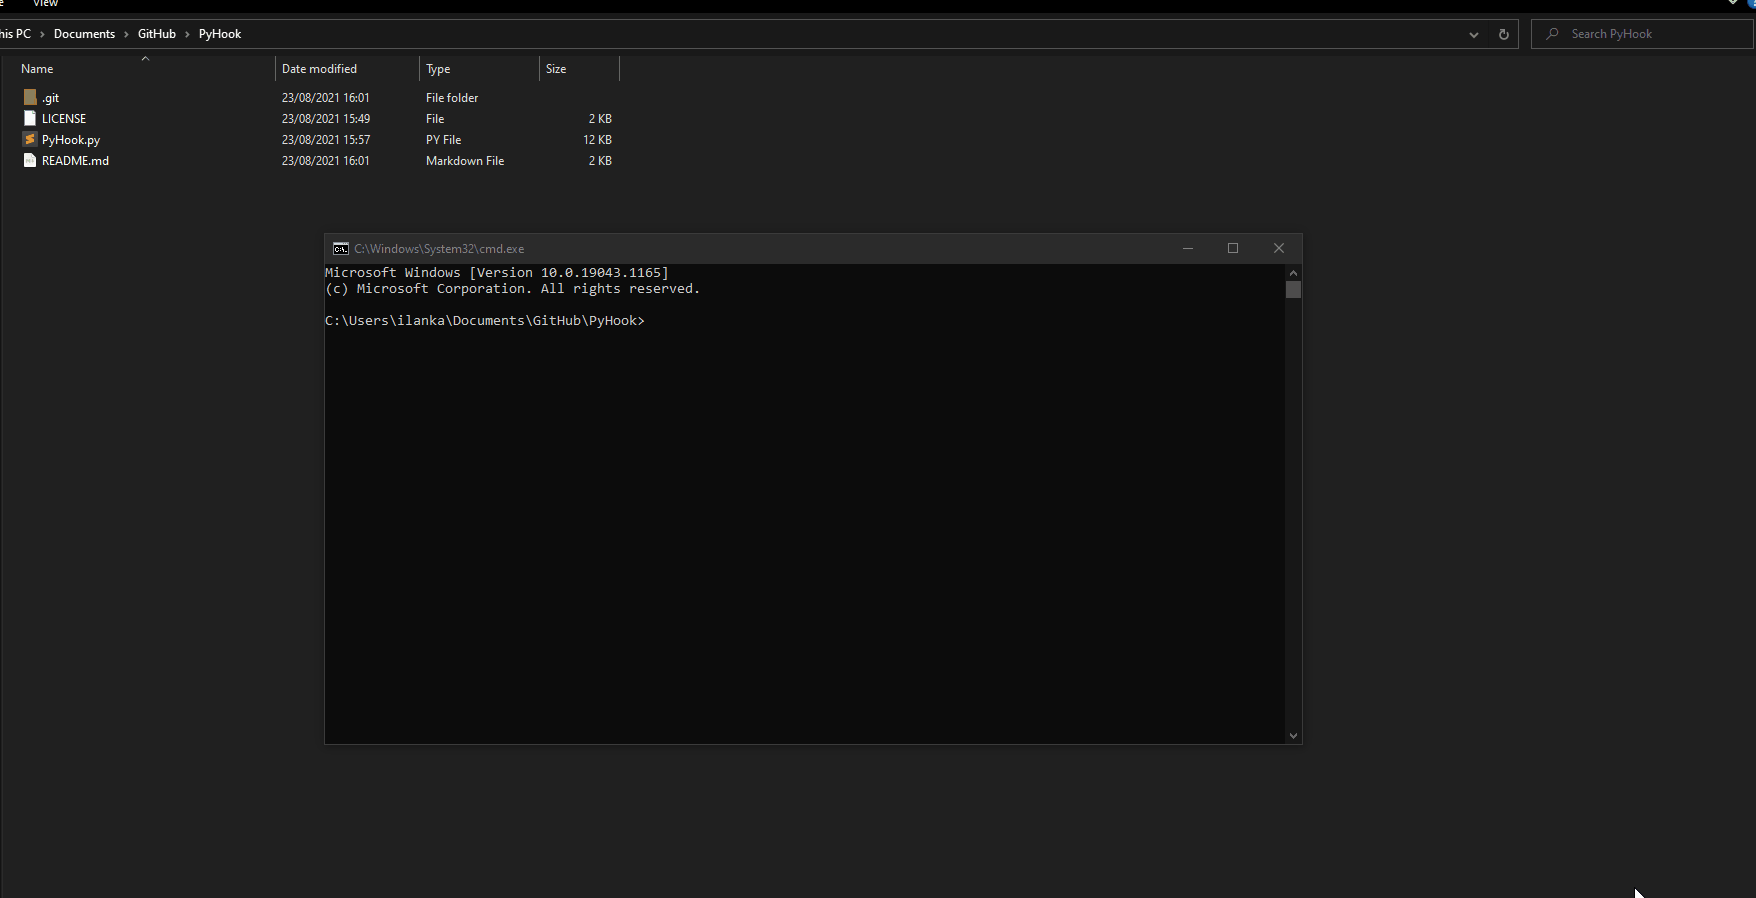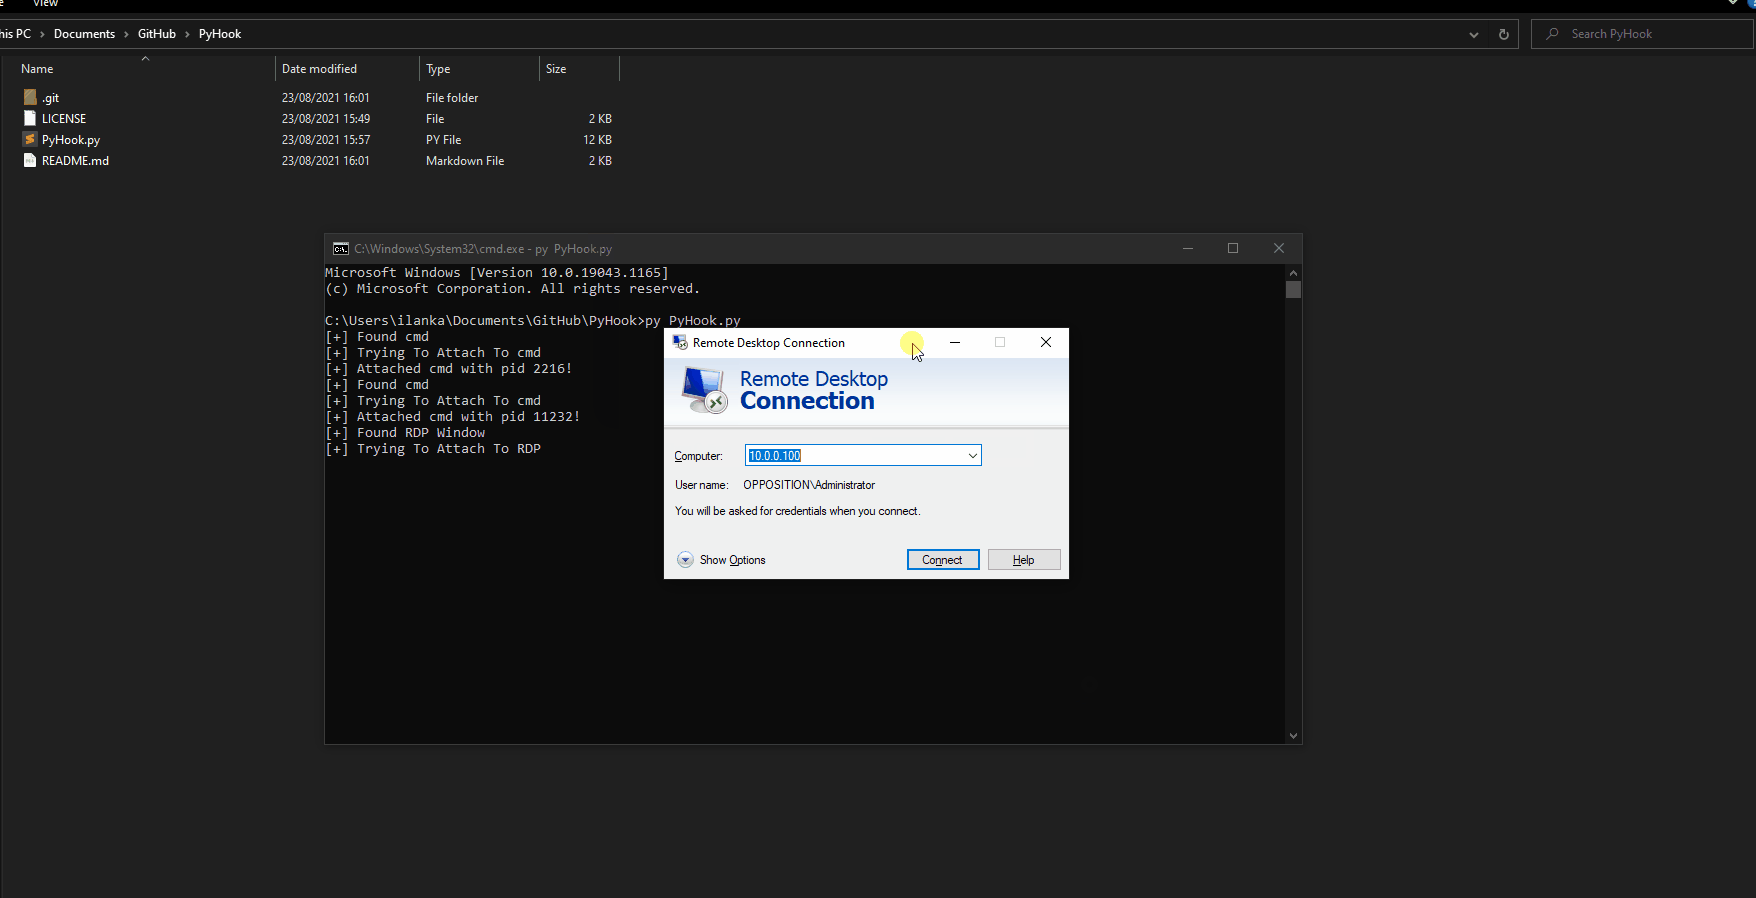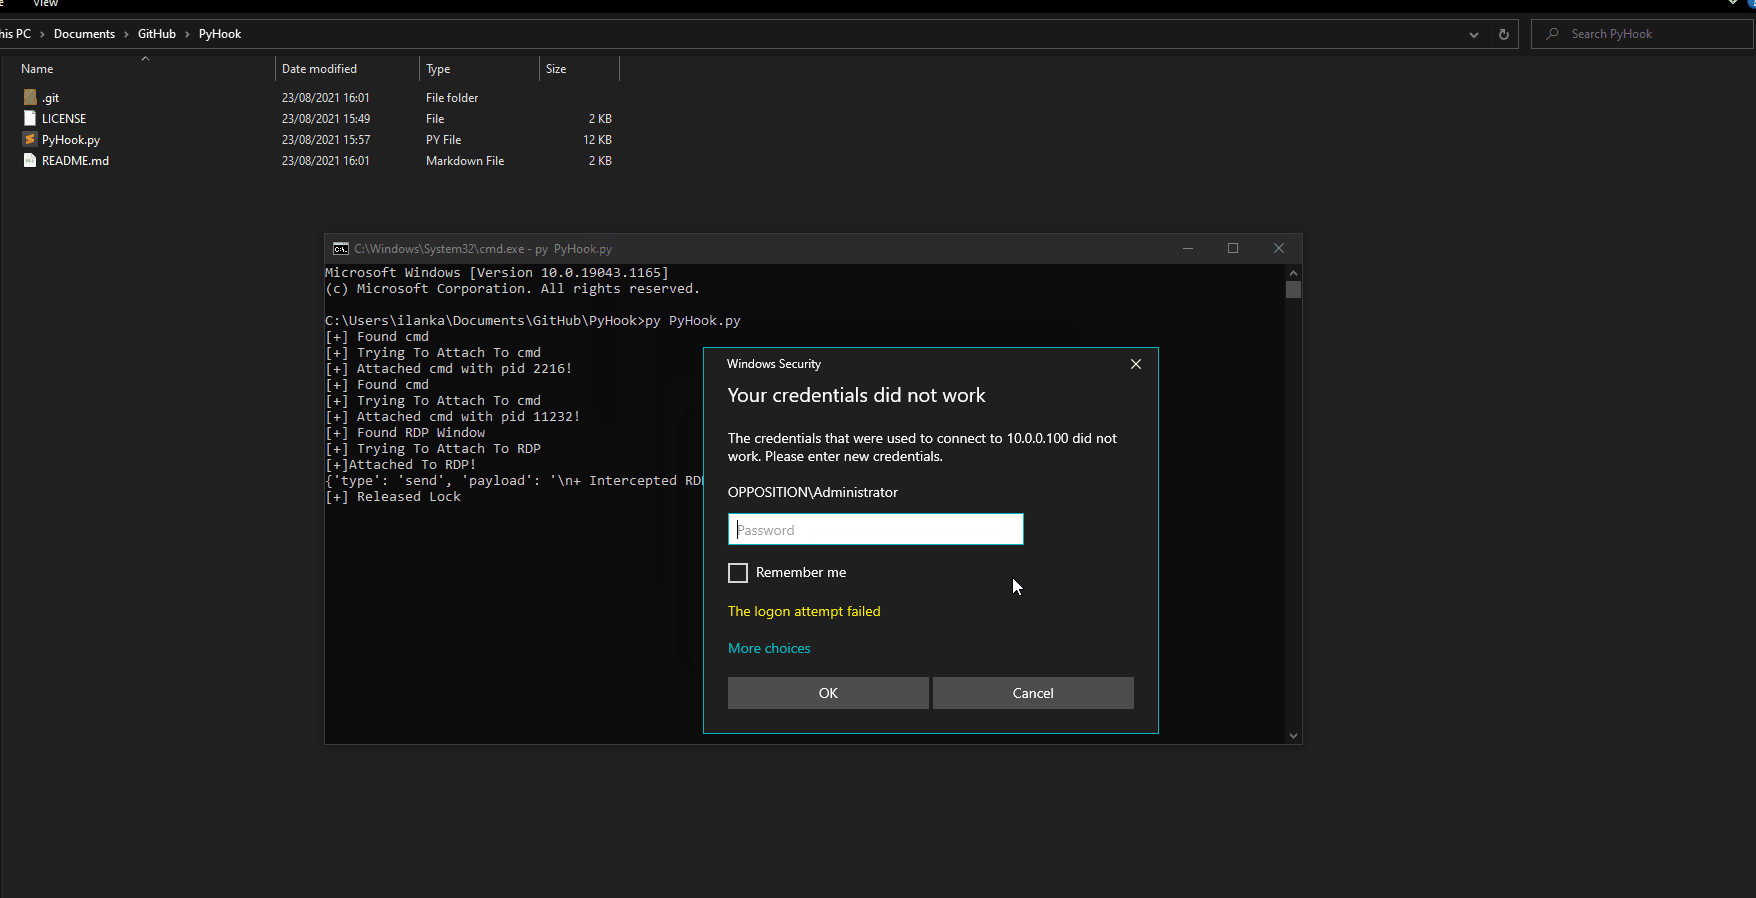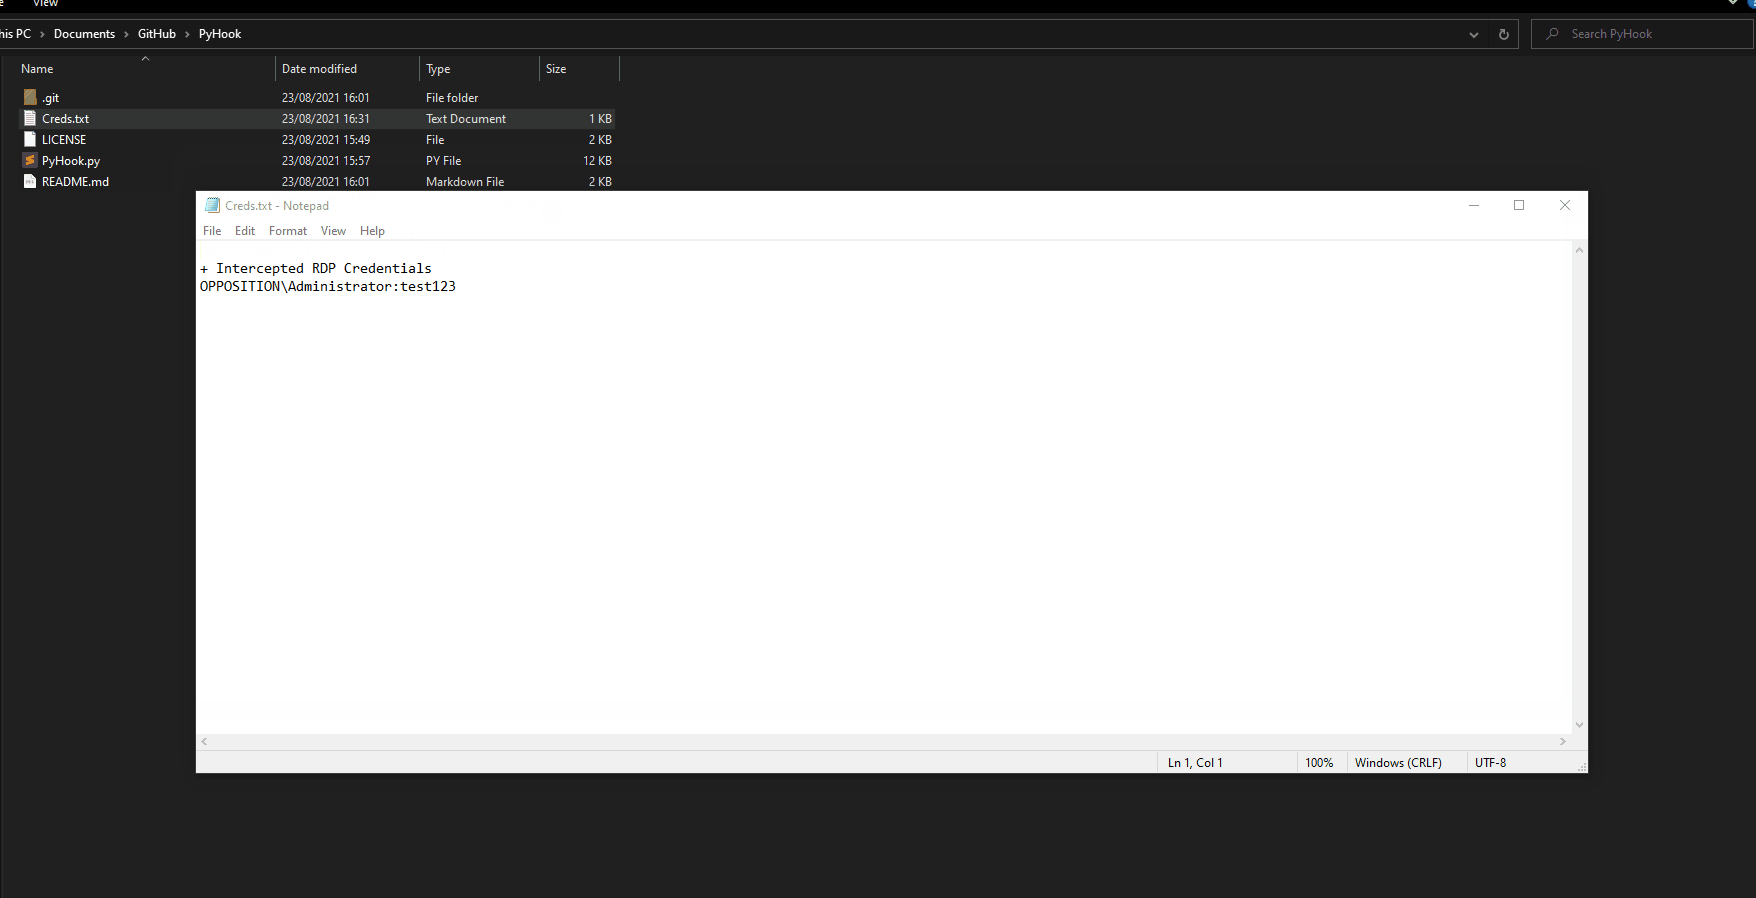 ilankalendarov/pyhook
Offensive API hooking tool using Frida to intercept Windows API calls and capture credentials from processes like mstsc, runas, PowerShell, cmd,…