Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
105 results
CVE-2024-29943 preview

CVE-2024-29943

GitHubseadragnol/cve-2024-29943

Reproducing CVE-2024-29943 for Windows, based on https://github.com/bjrjk/CVE-2024-29943
binary-exploitationeducationexploitation+2
2
11 months ago
RPCMon preview

RPCMon

GitHubcyberark/rpcmon

RPC Monitor tool based on Event Tracing for Windows

privilege-escalation
4072 years ago
Obfusk8 preview

Obfusk8

GitHubx86byte/obfusk8

Obfusk8: lightweight Obfuscation library based on C++17 / Header Only for windows binaries

cryptographyexploit-frameworkspayload-development+4
8384 months ago
evil-winrm-py preview

evil-winrm-py

GitHubadityatelange/evil-winrm-py

Execute commands interactively on remote Windows machines using the WinRM protocol (just faster)
authenticationcommand-and-controllateral-movement+7
4185 days ago
CVE-2021-34527-Scanner-Based-On-cube0x0-POC preview

CVE-2021-34527-Scanner-Based-On-cube0x0-POC

GitHubdywhoami/cve-2021-34527-scanner-based-on-cube0x0-poc

Scanner for Windows Print Spooler service vulnerability CVE-2021-34527, based on cube0x0's PoC, enabling detection of exploitable targets.
exploitationpenetration-testingvulnerability-analysis+1
35 years ago
dynmx preview

dynmx

GitHub0x534a/dynmx

Signature-based detection of malware features based on Windows API call sequences. It's like YARA for sandbox API traces!
dynamic-analysis-sandboxingmalware-analysis
843 years ago
windows-x86-shellcode-poc preview

windows-x86-shellcode-poc

GitHubnataliadiak/windows-x86-shellcode-poc

Windows x86 PoC: Stack‑based buffer overflow with custom shellcode on legacy 32-bit Windows.
binary-exploitationeducationpayload-development+3
85 months ago
exch_CVE-2021-42321 preview

exch_CVE-2021-42321

GitHub7bitsteam/exch_cve-2021-42321

Modified .NET deserialization payload for CVE-2021-42321, based on ysoserial.net, that writes files and bypasses Windows Defender to target Microsoft…

binary-exploitationexploitationpayload-development+3
104 years ago
Windows-Kernel-Exploitation preview

Windows-Kernel-Exploitation

GitHubvp777/windows-kernel-exploitation

Techniques and tools for Windows kernel exploitation, covering pool overflow exploitation, segment heap metadata abuse, and debugging scripts for…
binary-exploitationeducationexploitation+3
2691 month ago
EvilKaspersky preview

EvilKaspersky

GitHubgmh5225/evilkaspersky

Windows kernel driver experiment based on KasperskyHook that uses direct syscalls for interprocess memory copying, with support for unloading the…

defensive-toolsmalware-analysismemory-forensics+3
22 years ago
wesng preview

wesng

GitHubbitsadmin/wesng

Windows Exploit Suggester - Next Generation
exploitationinformation-gatheringprivilege-escalation+1
5.0k4 days ago
PSPKIAudit preview

PSPKIAudit

GitHubghostpack/pspkiaudit

PowerShell toolkit for AD CS auditing based on the PSPKI toolkit.
penetration-testingprivilege-escalation
9532 years ago
CVE-2009-1330 preview

CVE-2009-1330

GitHubadenkiewicz/cve-2009-1330

Simple exploit for Easy RM to MP3 Converter 2.7.3.700 on Windows 7 32b.

binary-exploitationexploitationpayload-generation+3
7 years ago
wtf preview

wtf

GitHub0vercl0k/wtf

Distributed, code-coverage guided snapshot-based fuzzer for user and kernel-mode targets on Windows and Linux, with emulator and hypervisor backends.
binary-analysisdynamic-analysis-sandboxingexploitation+2
1.8k2 months ago
cromite preview

cromite

GitHubuazo/cromite

Hardened Chromium/Bromite fork for Android, Windows and Linux with built-in ad blocking, anti-fingerprinting mitigations and privacy-focused patches.
android-securityanti-botfingerprint-spoofing+4
8.4k1 month ago
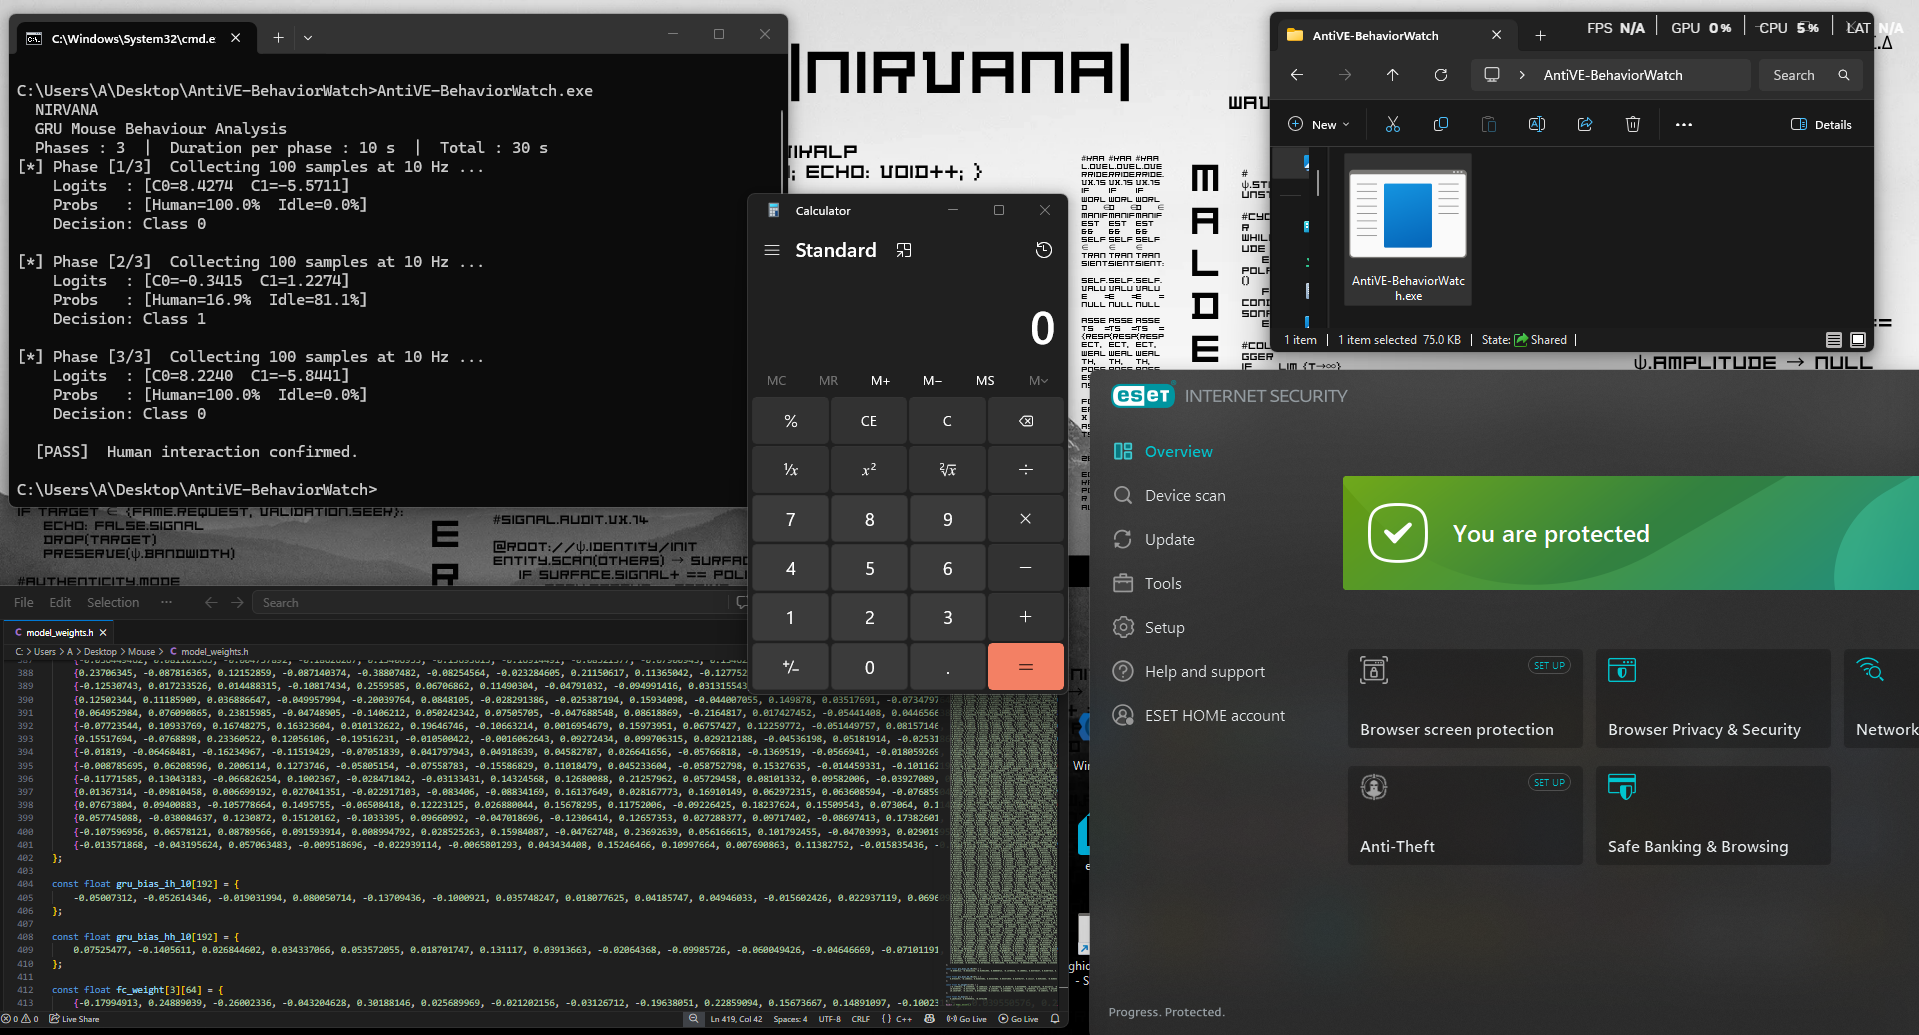
AntiVE-BehaviorWatch preview

AntiVE-BehaviorWatch

GitHubnirvanaon/antive-behaviorwatch

Embedded GRU neural network for real-time human behavior verification via mouse movement analysis, detecting automated analysis systems, sandboxes,…
anti-botdynamic-analysis-sandboxingids-ips-evasion+3
413 months ago
PacketPirate preview

PacketPirate

GitHubd0rb/packetpirate

A headless , scriptable, command-line based MITM proxy designed for network traffic interception, analysis, and modification on Windows systems.
api-security-testingeducationinformation-gathering+6
10 months ago
GodPotato preview

GodPotato

GitHubbeichendream/godpotato

DCOM-based privilege escalation tool for Windows Server 2012-2022 and Windows 8-11, elevating users with ImpersonatePrivilege to NT AUTHORITY\SYSTEM…

exploitationpenetration-testingpost-exploitation+1
2.4k2 years ago
Previous123456Next