
bifrost
 bifrost-proxy/bifrost
High-performance HTTP/HTTPS/SOCKS5 MITM proxy in Rust with TLS interception, rule-based request rewriting, traffic capture, breakpoints, script…
api-security-testingnetwork-securitypacket-sniffing-analysis+6
161
bifrost-proxy/bifrostHigh-performance HTTP/HTTPS/SOCKS5 MITM proxy in Rust with TLS interception, rule-based request rewriting, traffic capture, breakpoints, script…
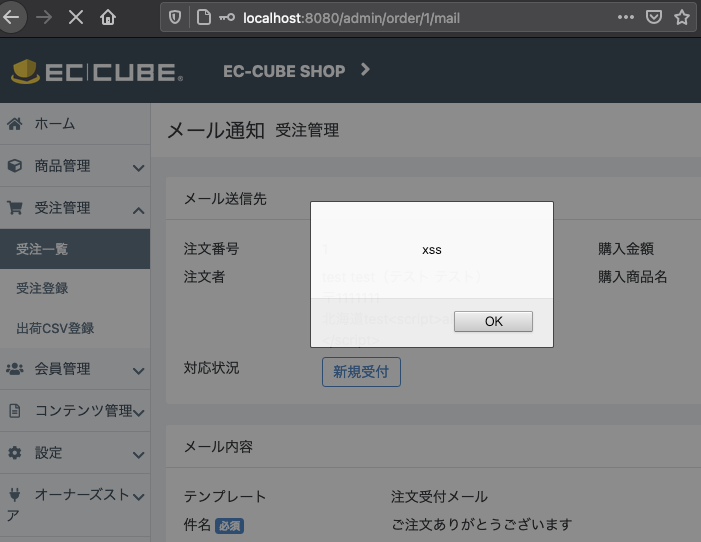 s-index/cve-2021-20717
CVE-2021-20717-EC-CUBE-XSS
 huyvo2910/cve-2525-25748-cross-site-request-forgery-csrf-vulnerability-in-hoteldruid-3.0.7
Detailed CVE-2025-25748 proof-of-concept and analysis of a CSRF vulnerability in HotelDruid 3.0.7, including exploitation flow, impact assessment,…
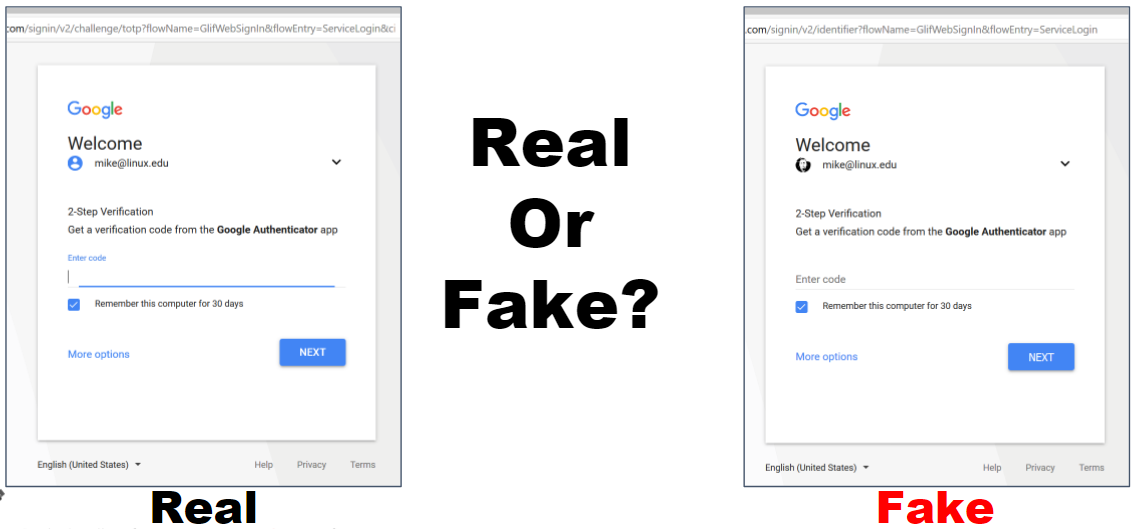 ustayready/credsniper
CredSniper is a phishing framework written with the Python micro-framework Flask and Jinja2 templating which supports capturing 2FA tokens.
 noraj/hacker-profile
Personal hacker profile page showcasing CTF achievements, cybersecurity projects, and curated resources. Built with Middleman and Gulp for static…
 cyberhawk000/cve-2022-24181
XSS via Host Header injection and Steal Password Reset Token of another user
 razielx64/cve-2025-69606-gsvoip-xss
Proof-of-concept for a reflected XSS vulnerability (CVE-2025-69606) in GSVoIP Web Panel v2.0.90, demonstrating unauthenticated arbitrary JavaScript…
 shree-chandragiri/cve-2024-51032
A Cross-site Scripting (XSS) vulnerability in manage_recipient.php of Sourcecodester Toll Tax Management System 1.0 allows remote authenticated users…
 zero-trace7/cve-2026-50229
Automated XSS scanner and proof-of-concept exploit for CVE-2026-50229 in Apache Tomcat examples. Detects and exploits reflected cross-site scripting…
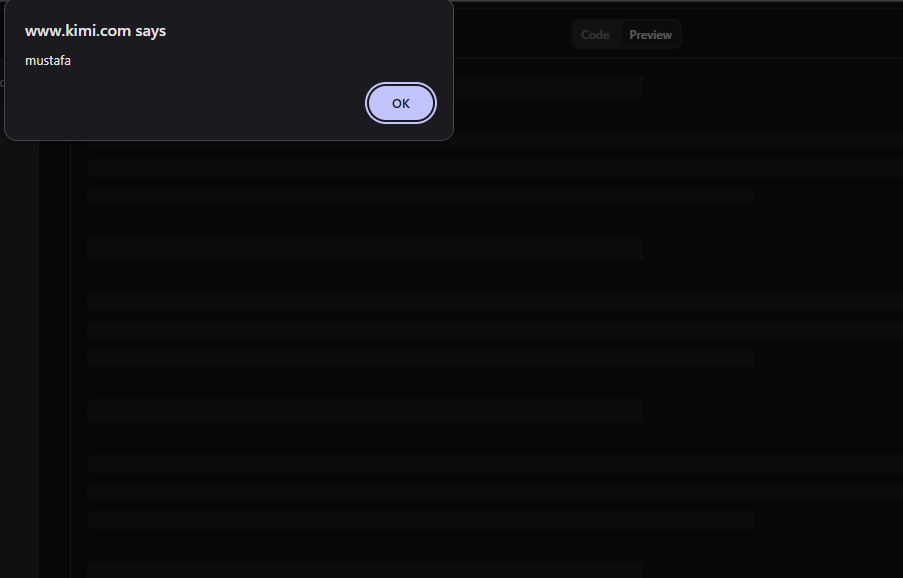 mgtx2/cve-2026-39107
Detailed disclosure of a stored XSS vulnerability in Kimi AI v1.0's Preview tab, including attack scenario, PoC, and remediation guidance for…
 ritvikb99/dark-fantasy-hack-tool
DDOS Tool: To take down small websites with HTTP FLOOD. Port scanner: To know the open ports of a site. FTP Password Cracker: To hack file system of…
 venablee/cve-2026-30252
The ZenShare Suite application is vulnerable by a Reflected Cross-Site Scripting (XSS) vulnerability, affecting web application login and recovery…
 rashidkhanpathan/cve-2022-41445
Cross Site Scripting in Teacher's Record Management System using CodeIgnitor
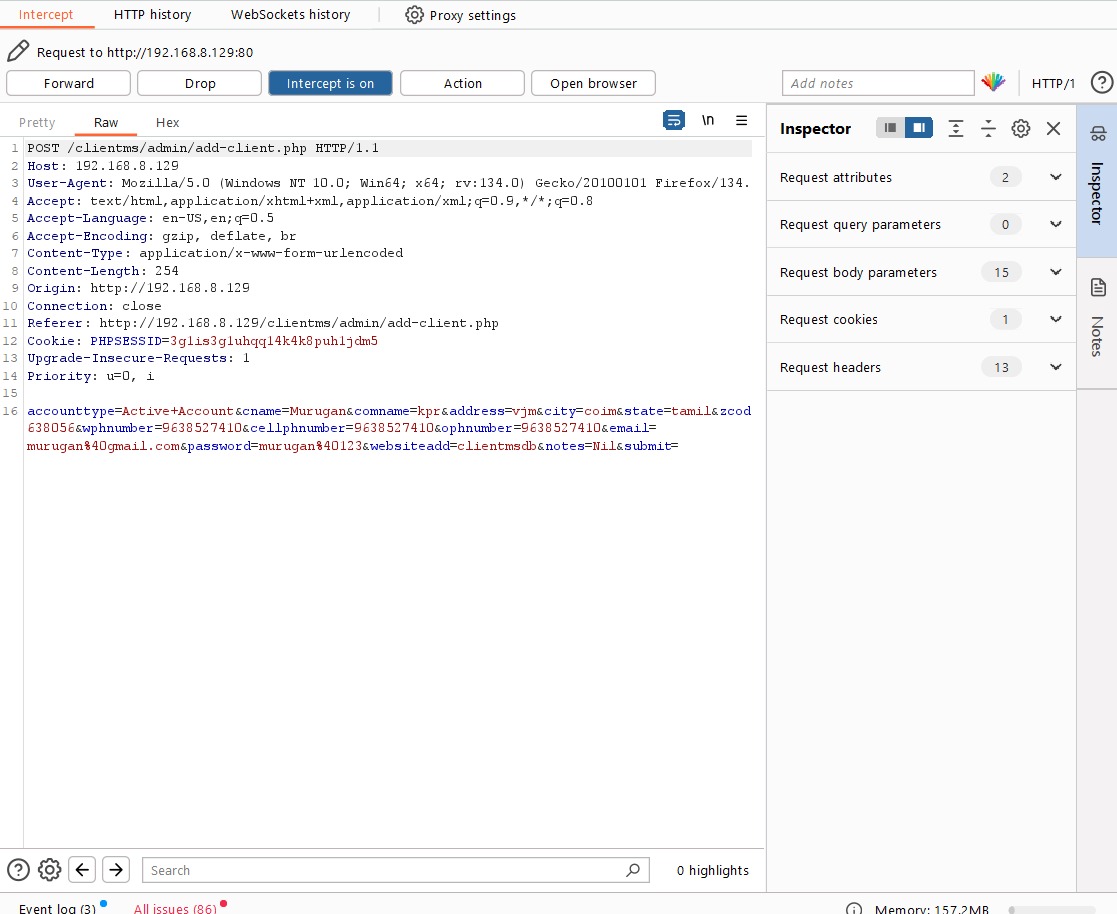 moulish2004/cve-2025-44603-csrf-leads_to_create_fakeusers
Proof-of-concept demonstrating a CSRF vulnerability in a PHP-based Client Management System, with HTML exploit code and mitigation strategies for web…
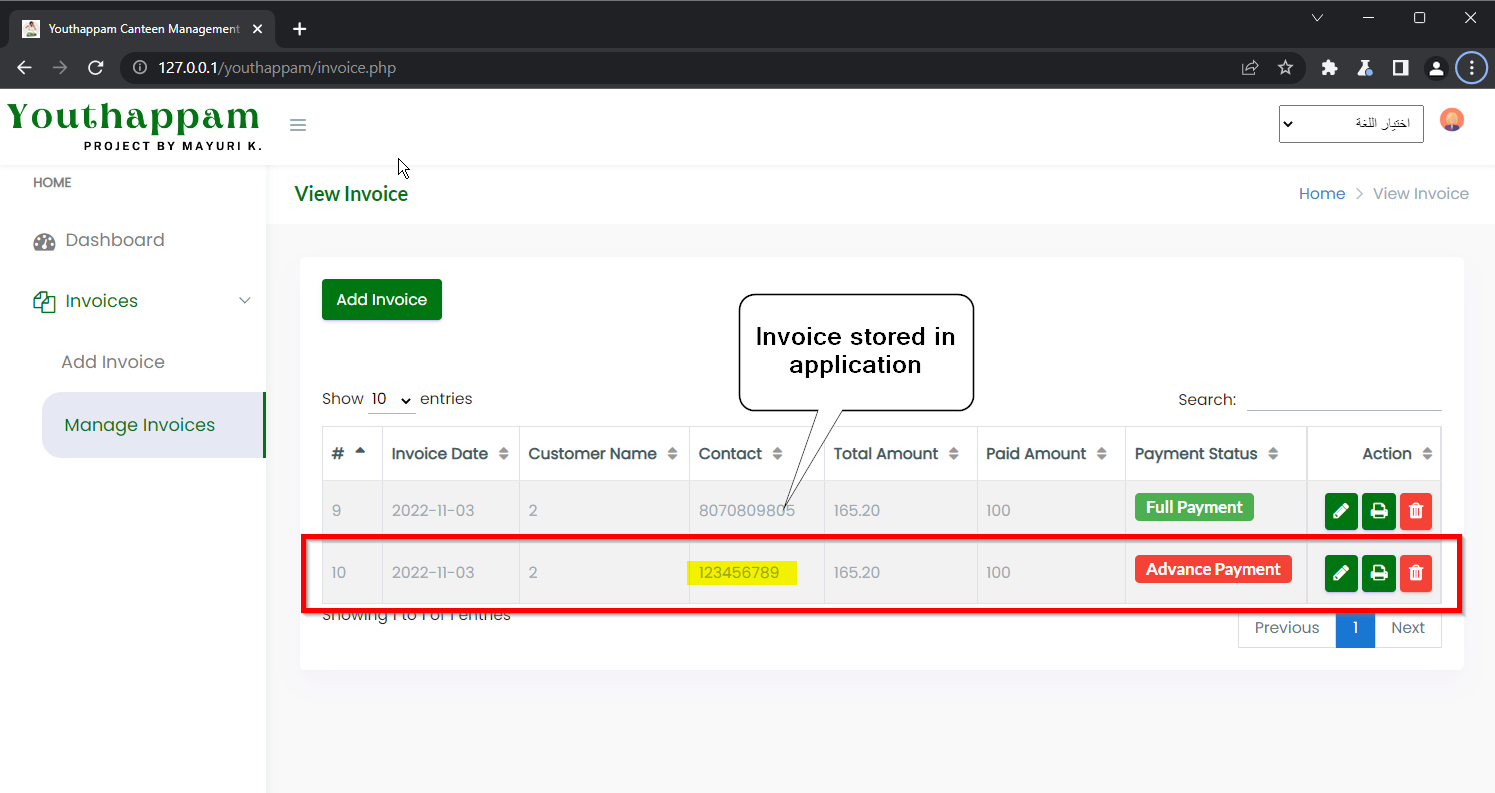 mudassiruddin/cve-2022-43144-stored-xss
PoC to exploit CVE-2022-43144
 lauleysen/cve-2024-46538
based on [EQSTLab](https://github.com/EQSTLab)