Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
38 results
CVE-2023-45182 preview

CVE-2023-45182

GitHubafine-com/cve-2023-45182

IBM i Access Client Solutions < 1.1.9.4 - Weak password encryption
cryptographyencryption-decryption-toolsexploitation+2
2 years ago
CVE-2005-2428-IBM-Lotus-Domino-R8-Password-Hash-Extraction-Exploit preview

CVE-2005-2428-IBM-Lotus-Domino-R8-Password-Hash-Extraction-Exploit

GitHubschwankner/cve-2005-2428-ibm-lotus-domino-r8-password-hash-extraction-exploit

IBM Lotus Domino <= R8 Password Hash Extraction Exploit
exploitationinformation-gatheringpassword-attacks+2
37 years ago
datapower-redis-rce-exploit preview

datapower-redis-rce-exploit

GitHubcopethomas/datapower-redis-rce-exploit

A POC for IBM Datapower Authenticated Redis RCE Exploit abusing the Test Message Function (CVE-2020-5014)
exploitationpenetration-testingred-teaming+3
24 years ago
ibmsecurity preview

ibmsecurity

GitHubibm-security/ibmsecurity

Idempotent functions for IBM Security Appliance REST APIs. Currently covering ISAM and ISDS Appliances.
api-securityconfiguration-auditingdevsecops+3
533 months ago
CVE-2023-30990 preview

CVE-2023-30990

GitHubsilentsignal/cve-2023-30990

CVE-2023-30990 exploits
command-and-controlexploitationpayload-development+3
61 year ago
CVE-2013-2977 preview

CVE-2013-2977

GitHubdefrancescojp/cve-2013-2977

Proof-of-concept exploit for CVE-2013-2977: IBM Lotus Notes PNG integer overflow leading to arbitrary code execution when a malicious email is opened…
binary-exploitationemail-securityexploitation+1
5 years ago
CVE-2026-9198 preview

CVE-2026-9198

GitHubywh-jfellus/cve-2026-9198

Proof of Concept for CVE-2026-9198 - IBM Langflow Unauthenticated RCE via Auto-Login Bypass
ctfeducationexploitation+4
3 months ago
CVE-2026-9198 preview

CVE-2026-9198

GitHubprocjevt/cve-2026-9198

Exploit script for CVE-2026-9198 targeting IBM Langflow, providing proof-of-concept code to validate vulnerabilities and support authorized security…
exploitationpenetration-testingvulnerability-analysis+1
2 months ago
langflow-CVE-2026-17633-PoC preview

langflow-CVE-2026-17633-PoC

GitHuboscar-collado/langflow-cve-2026-17633-poc

PoC for CVE-2026-17633 — Authenticated RCE in IBM Langflow OSS 1.0.0–1.10.3 via custom_component endpoint. Includes CVE-2026-17632 AST scanner bypass…
code-analysisexploitationpenetration-testing+2
11 month ago
Tivoli-Madness preview

Tivoli-Madness

GitHubvoidsec/tivoli-madness

Advisory for CVE-2020-28054 & stack based buffer overflow in IBM Tivoli Storage Manager
exploitationinformation-gatheringpenetration-testing+1
75 years ago
IBM-Langflow-CVE-2026-48519-poc preview

IBM-Langflow-CVE-2026-48519-poc

GitHublukehebe/ibm-langflow-cve-2026-48519-poc

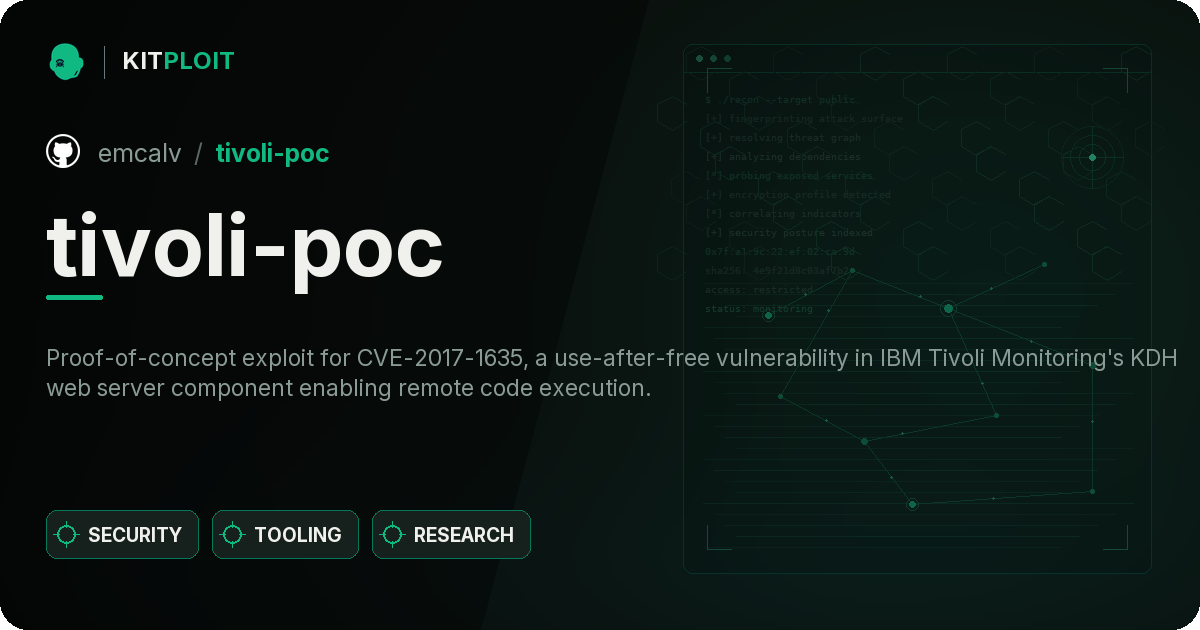
Proof-of-concept exploit for CVE-2026-48519, a pre-auth RCE in IBM Langflow <= 1.9.1 via the Shareable Playground /api/v1/build_public_tmp endpoint.
exploitationpenetration-testingremote-access-tool+3
1 month ago
tivoli-poc preview

tivoli-poc

GitHubemcalv/tivoli-poc

Proof-of-concept exploit for CVE-2017-1635, a use-after-free vulnerability in IBM Tivoli Monitoring's KDH web server component enabling remote code…
exploitationpenetration-testingremote-access-tool+2
18 years ago
EXPLOIT-CVE-2026-9198 preview

EXPLOIT-CVE-2026-9198

GitHubjoaovicdev/exploit-cve-2026-9198

Proof-of-concept exploit for CVE-2026-9198, an unauthenticated RCE in IBM Langflow OSS, chaining auto_login and validate/code endpoints. Includes a…
educationexploitationlabs-practice+4
2 months ago
CVE-2024-28784 preview

CVE-2024-28784

GitHubcainsoulless/cve-2024-28784

Technical disclosure for CVE-2024-28784 — a stored XSS vulnerability in IBM QRadar SIEM 7.5.0 UpdatePackage 7. The issue affects the Rule Wizard…
educationpapers-researchpenetration-testing+2
1 year ago
EternalLiberty preview

EternalLiberty

GitHubstrangerealintel/eternalliberty

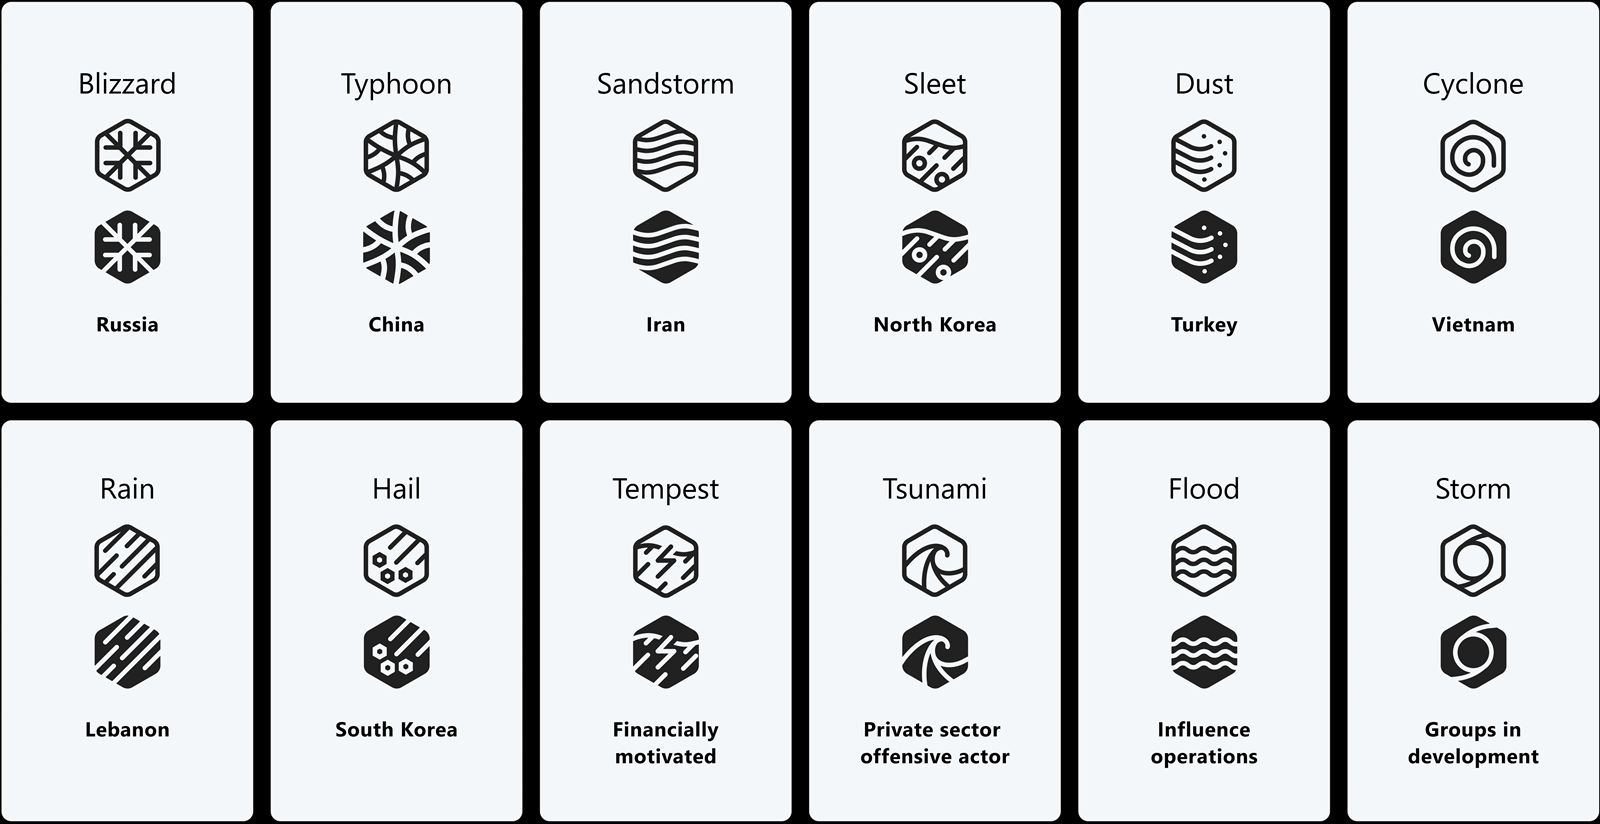
Curated repository of threat actor aliases and naming schemes used by major threat intelligence vendors, enabling cross-vendor search, attribution,…
curated-resourcesinformation-gatheringosint+1
2171 year ago
CVE-2025-36041 preview
Archived

CVE-2025-36041

GitHubbytereaper77/cve-2025-36041

Exploit (C) of the CVE-2025-36041 vulnerability in IBM MQ
exploitationnetwork-securitypenetration-testing+3
21 year ago
CVE-2015-1986 preview

CVE-2015-1986

GitHubmayaofveil/cve-2015-1986

Exploit PoC for Buffer overflow vulnerability in the server in IBM Tivoli Storage Manager FastBack 5.5.x and 6.x before 6.1.12.2 (tested in version…
binary-exploitationexploitationpayload-development+2
12 years ago
ibm-sterling-b2b-integrator-poc preview

ibm-sterling-b2b-integrator-poc

GitHubreverseclabs/ibm-sterling-b2b-integrator-poc

PoC code for the LPE and RCE (CVE-2024-31903) attacks against the IBM Sterling B2B Integrator

binary-exploitationcommand-and-controlexploitation+3
11 year ago
Previous123Next