
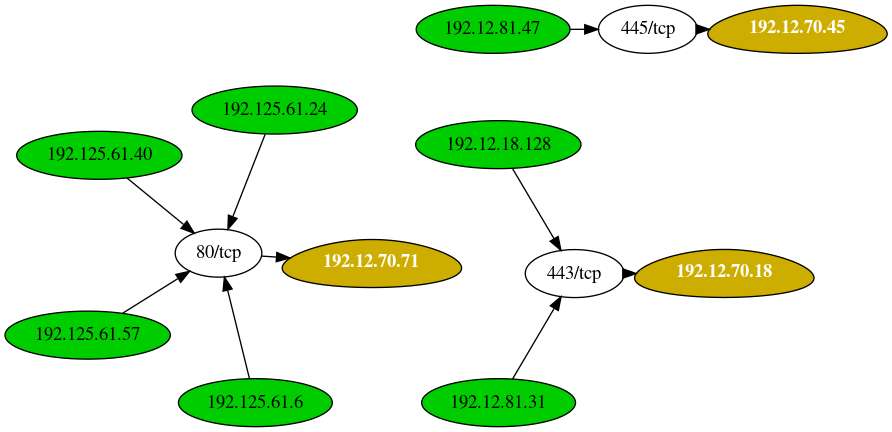
leprechaun
 vonahisec/leprechaun
This tool is used to map out the network data flow to help penetration testers identify potentially valuable targets.
network-mappingpenetration-testingpost-exploitation+1
245
vonahisec/leprechaunThis tool is used to map out the network data flow to help penetration testers identify potentially valuable targets.
 anmolksachan/waybacklister
A New Approach to Directory Bruteforce with WaybackLister v1.0
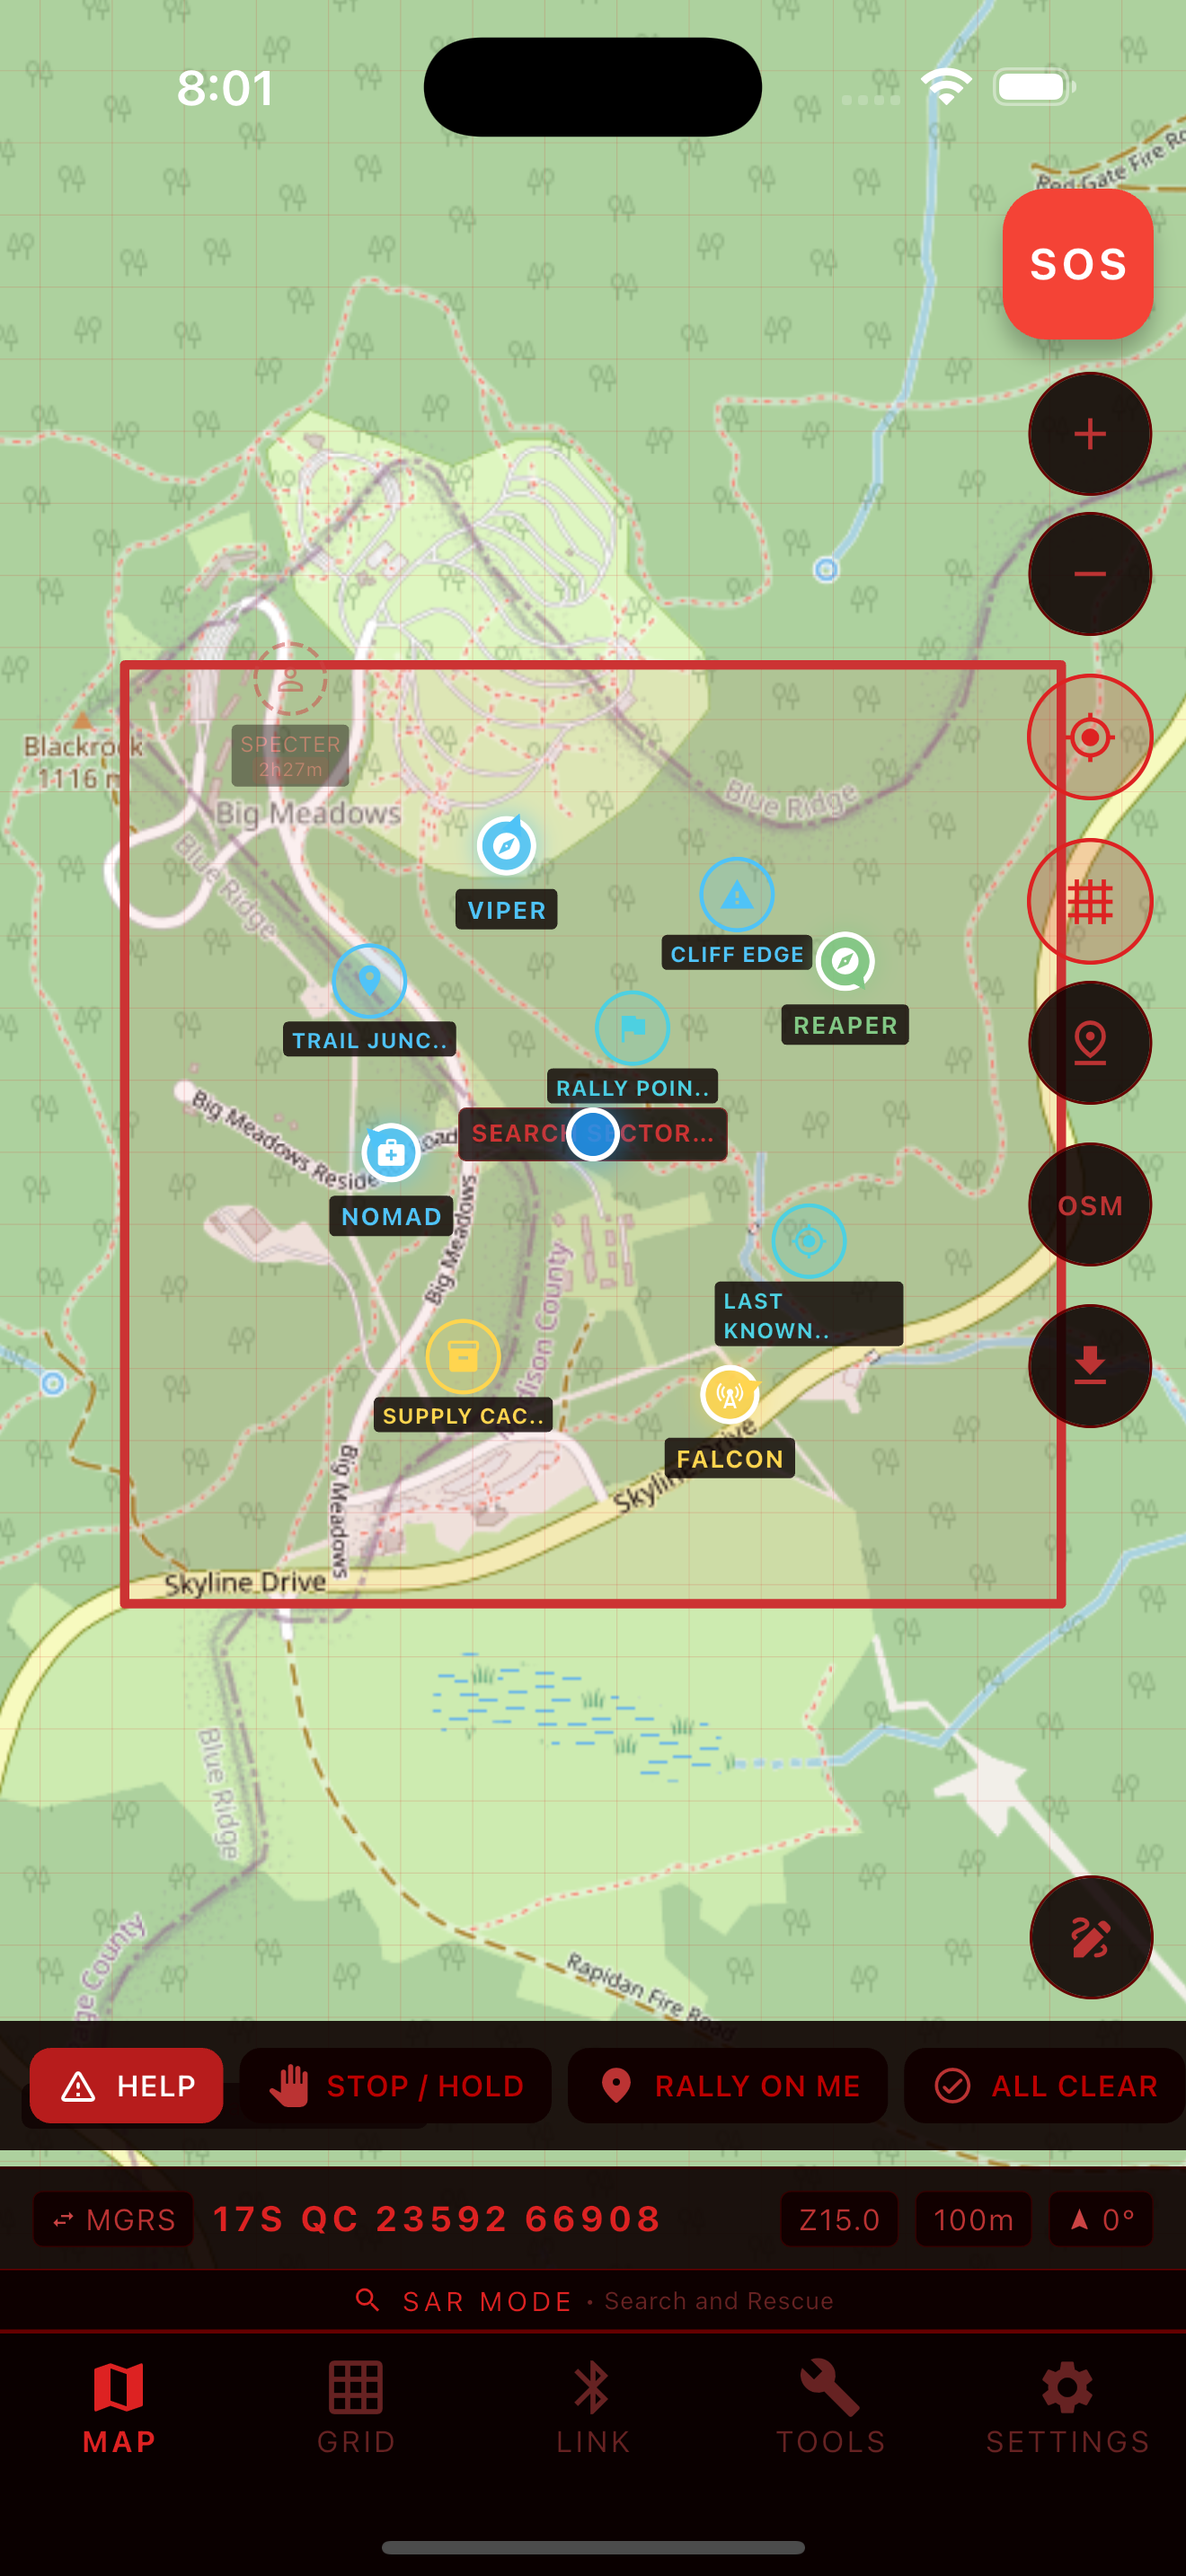 redgridtactical/redgridlink
Offline MGRS navigation + BLE proximity team sync for 2-8 people. No cell service needed. V1.0 through V4.0 roadmap in README.

 wattocyber/offensive-one-liners
110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.
 pateldhyeyit/cve-2026-37149
CVE-2026-37149 - SQL Injection vulnerability in the scost parameter of search_products.php in…
 amaansiddd787/cve-2025-65354
Technical disclosure and proof-of-concept for SQL injection in PuneethReddyHC event-management v1.0, detailing affected endpoint, payloads, and…
 maherazzouzi/cve-2022-36163
Proof-of-concept exploit for CVE-2022-36163, a format string vulnerability in pdftoroff hovacui 1.1.0 PDF reader, demonstrating local…
 erengozaydin/microfinance-management-system-v1.0-sql-injection-vulnerability-unauthenticated
Proof-of-concept exploit for an unauthenticated SQL injection vulnerability in Microfinance Management System V1.0, allowing remote data extraction…
 tuannq2299/cve-2023-23279
Proof-of-concept exploit for an unauthenticated SQL injection vulnerability (CVSS 9.8) in Canteen Management System v1.0, enabling remote data…
 geraldoalcantara/cve-2023-49989
Hotel Booking Management v1.0 - SQL Injection Vulnerability in the "id" parameter at update.php
 vighneshnair7/cve-2024-48427
Proof-of-concept for CVE-2024-48427: SQL injection in Sourcecodester Packers and Movers Management System v1.0. Exploits the id parameter to execute…
 geraldoalcantara/cve-2023-51801
Simple Student Attendance System v.1.0 - Multiple SQL injection vulnerabilities - student_form.php and class_form.php
 baroi-ai/cve-2024-42658
CVE-2024-42658 An issue in wishnet Nepstech Wifi Router NTPL-XPON1GFEVN v1.0 allows a remote attacker to obtain sensitive information via the cookies…
 baroi-ai/cve-2024-42657
CVE-2024-42657 An issue in wishnet Nepstech Wifi Router NTPL-XPON1GFEVN v1.0 allows a remote attacker to obtain sensitive information via the lack of…
 hh1f/cve-2022-27413
Proof-of-concept exploit for CVE-2022-27413, an SQL injection vulnerability in Hospital-Management-System v1.0 admin.php page. Includes payloads and…
 ersinerenler/cve-2023-46022-code-projects-blood-bank-1.0-oob-sql-injection-vulnerability
Proof-of-concept exploit for CVE-2023-46022, demonstrating Out-of-Band SQL injection in Code-Projects Blood Bank V1.0 via the 'bid' parameter,…
 geraldoalcantara/cve-2023-49979
Best Student Management System v1.0 - Incorrect Access Control - Directory Listing
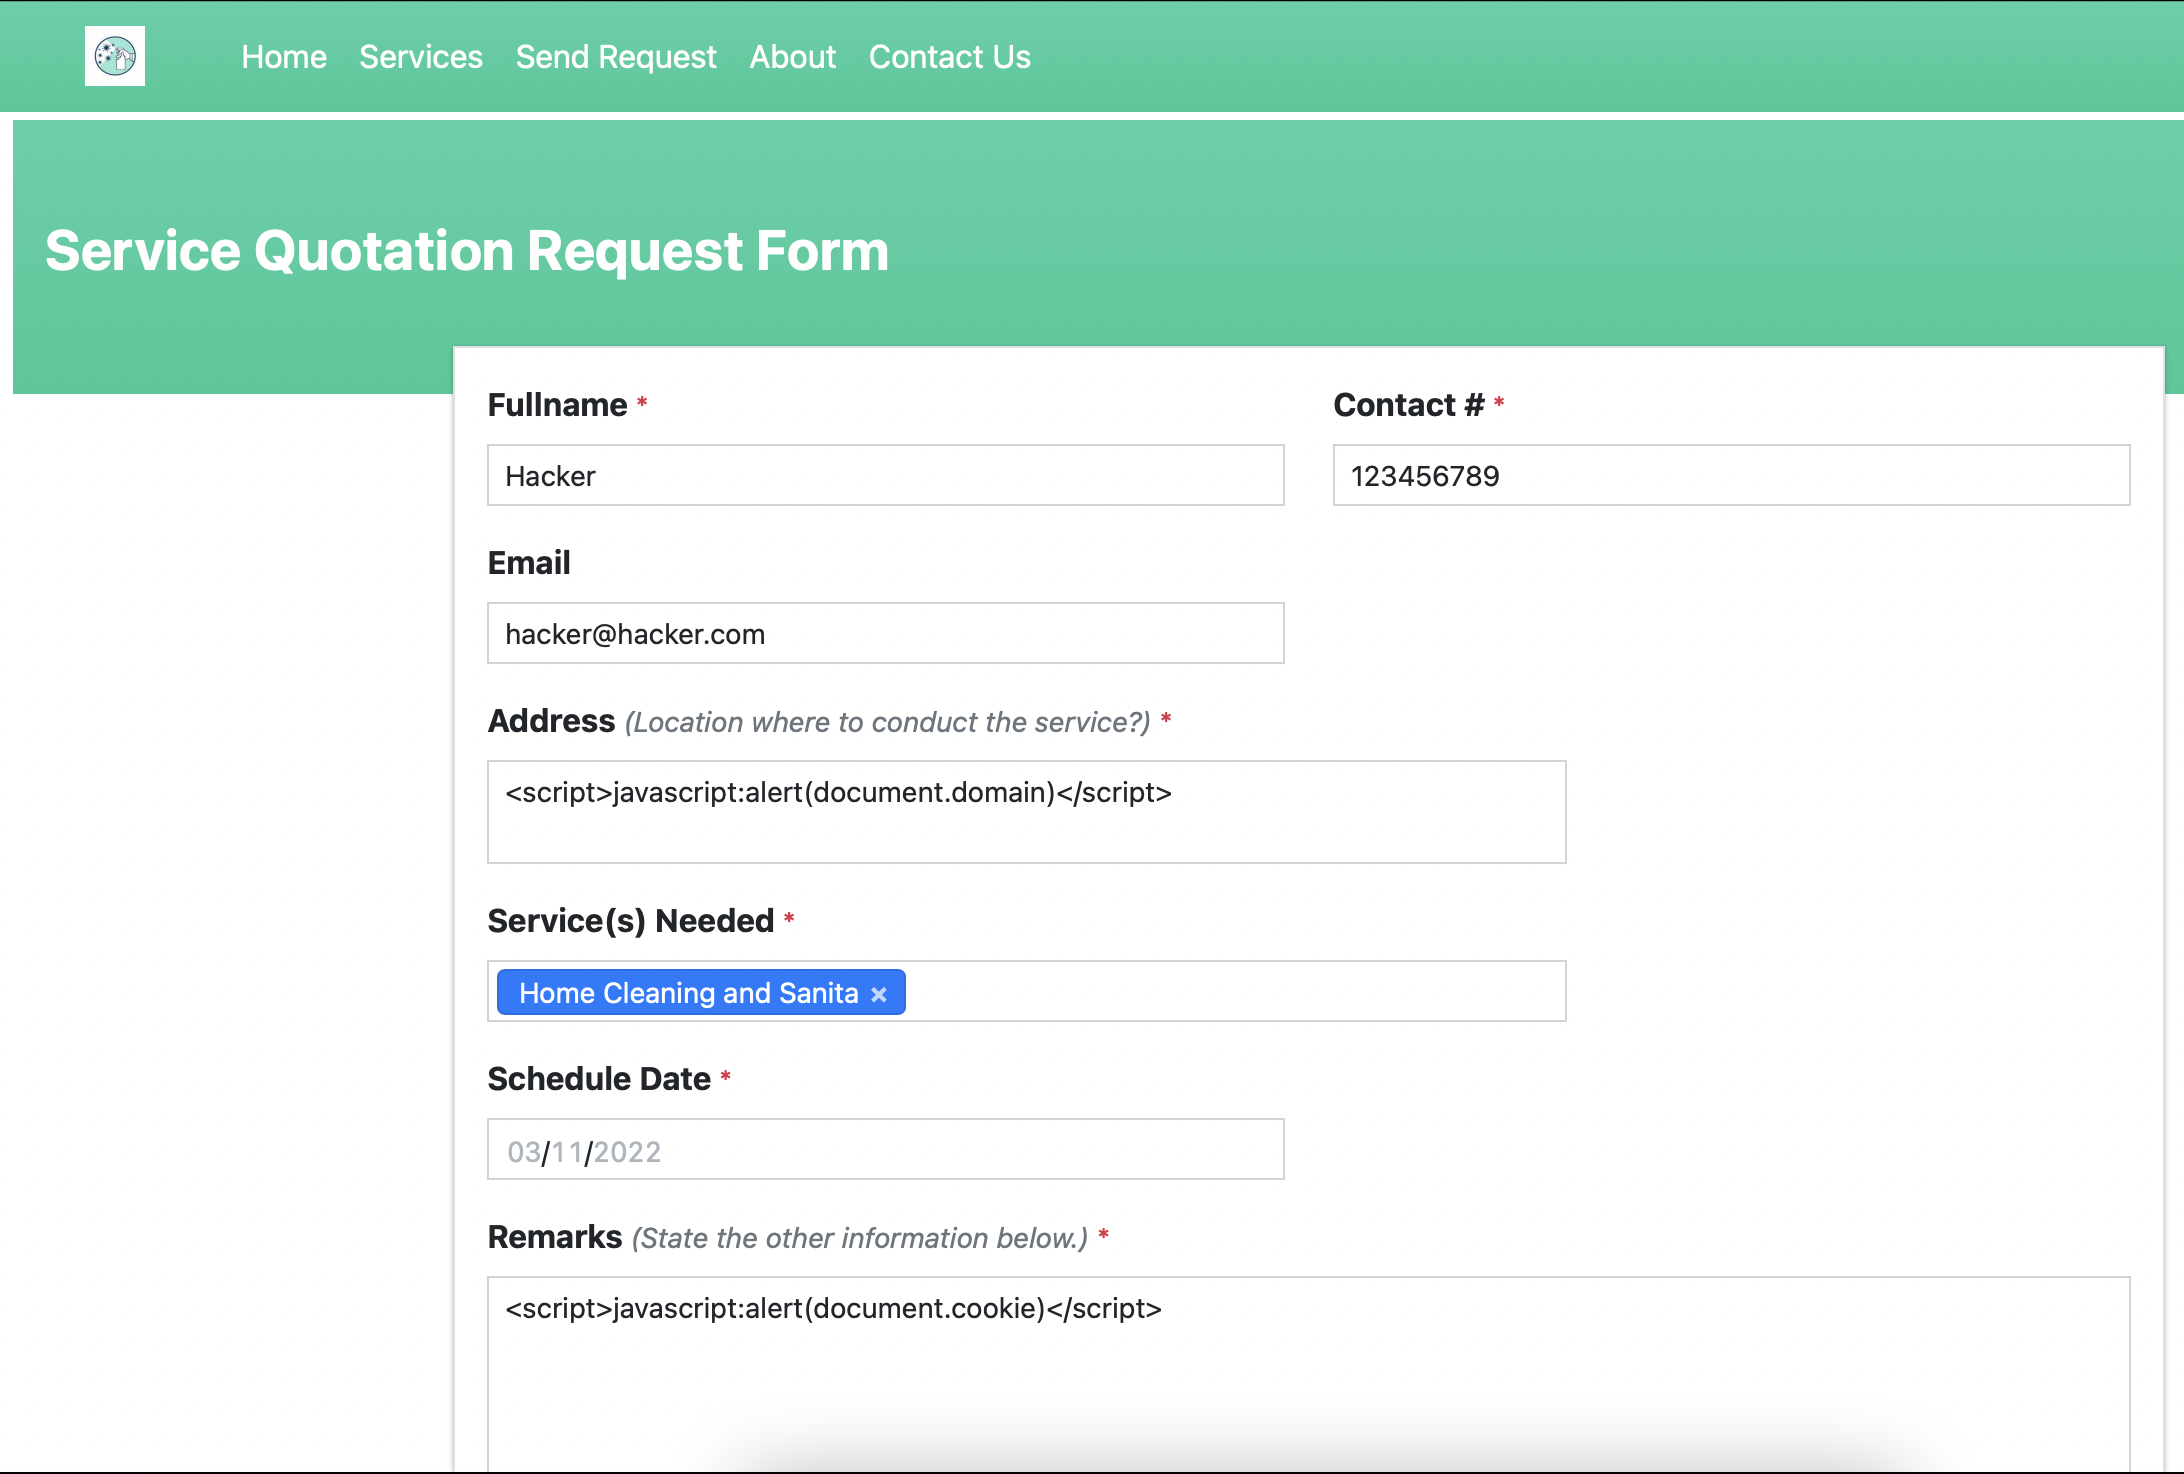 maikroservice/cve-2022-3942
Proof-of-concept for CVE-2022-3942: stored XSS in Sanitization Management System v1.0 enabling cookie theft via crafted payload in Remarks/Address…