
engine
 droidefense/engine
Droidefense: Advance Android Malware Analysis Framework
android-securitybinary-analysisdynamic-analysis-sandboxing+4
480
droidefense/engineDroidefense: Advance Android Malware Analysis Framework
 user1342/droiddetective
A machine learning malware analysis framework for Android apps.
 sumidcyber/zeroscout
🦅 ZeroScout: The Autonomous Local & Cloud Threat Hunter. Visualize attacks in a live War Room, identify APT groups via Genetic Analysis, and…
 jstrosch/subparse
Modular malware analysis artifact collection and correlation framework
 mandiant/flare-emu
Scriptable binary emulation framework integrating IDA Pro/Radare2 with Unicorn engine for automated malware analysis, string decryption, and code…
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 decaf-project/decaf
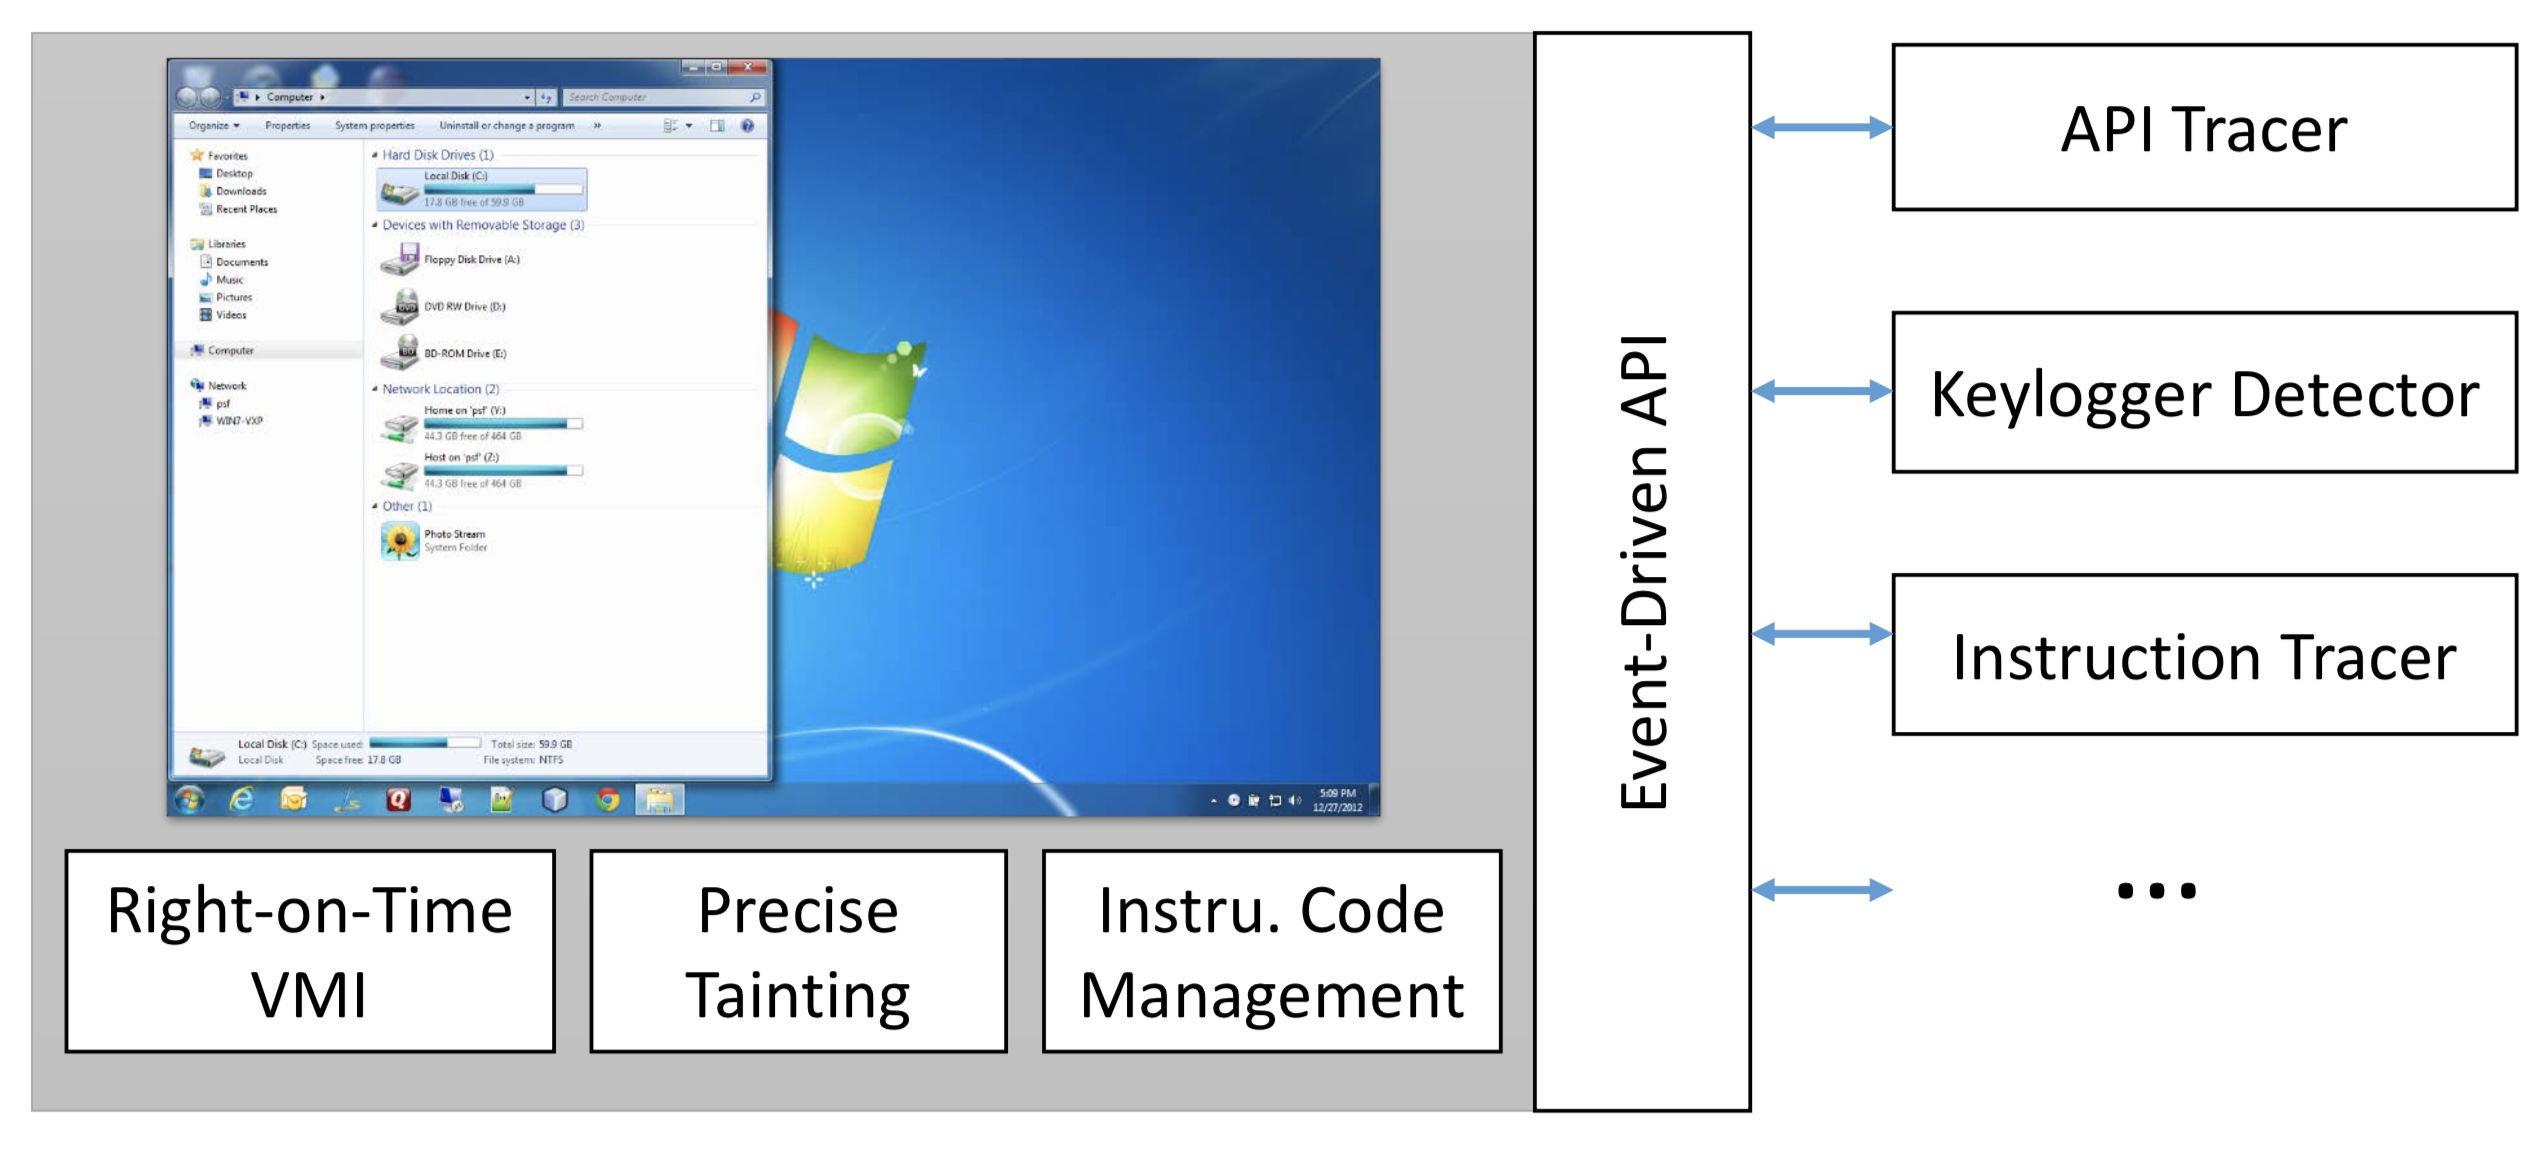
DECAF (short for Dynamic Executable Code Analysis Framework) is a binary analysis platform based on QEMU. This is also the home of the DroidScope…
 sh4hin/androl4b
A Virtual Machine For Assessing Android applications, Reverse Engineering and Malware Analysis
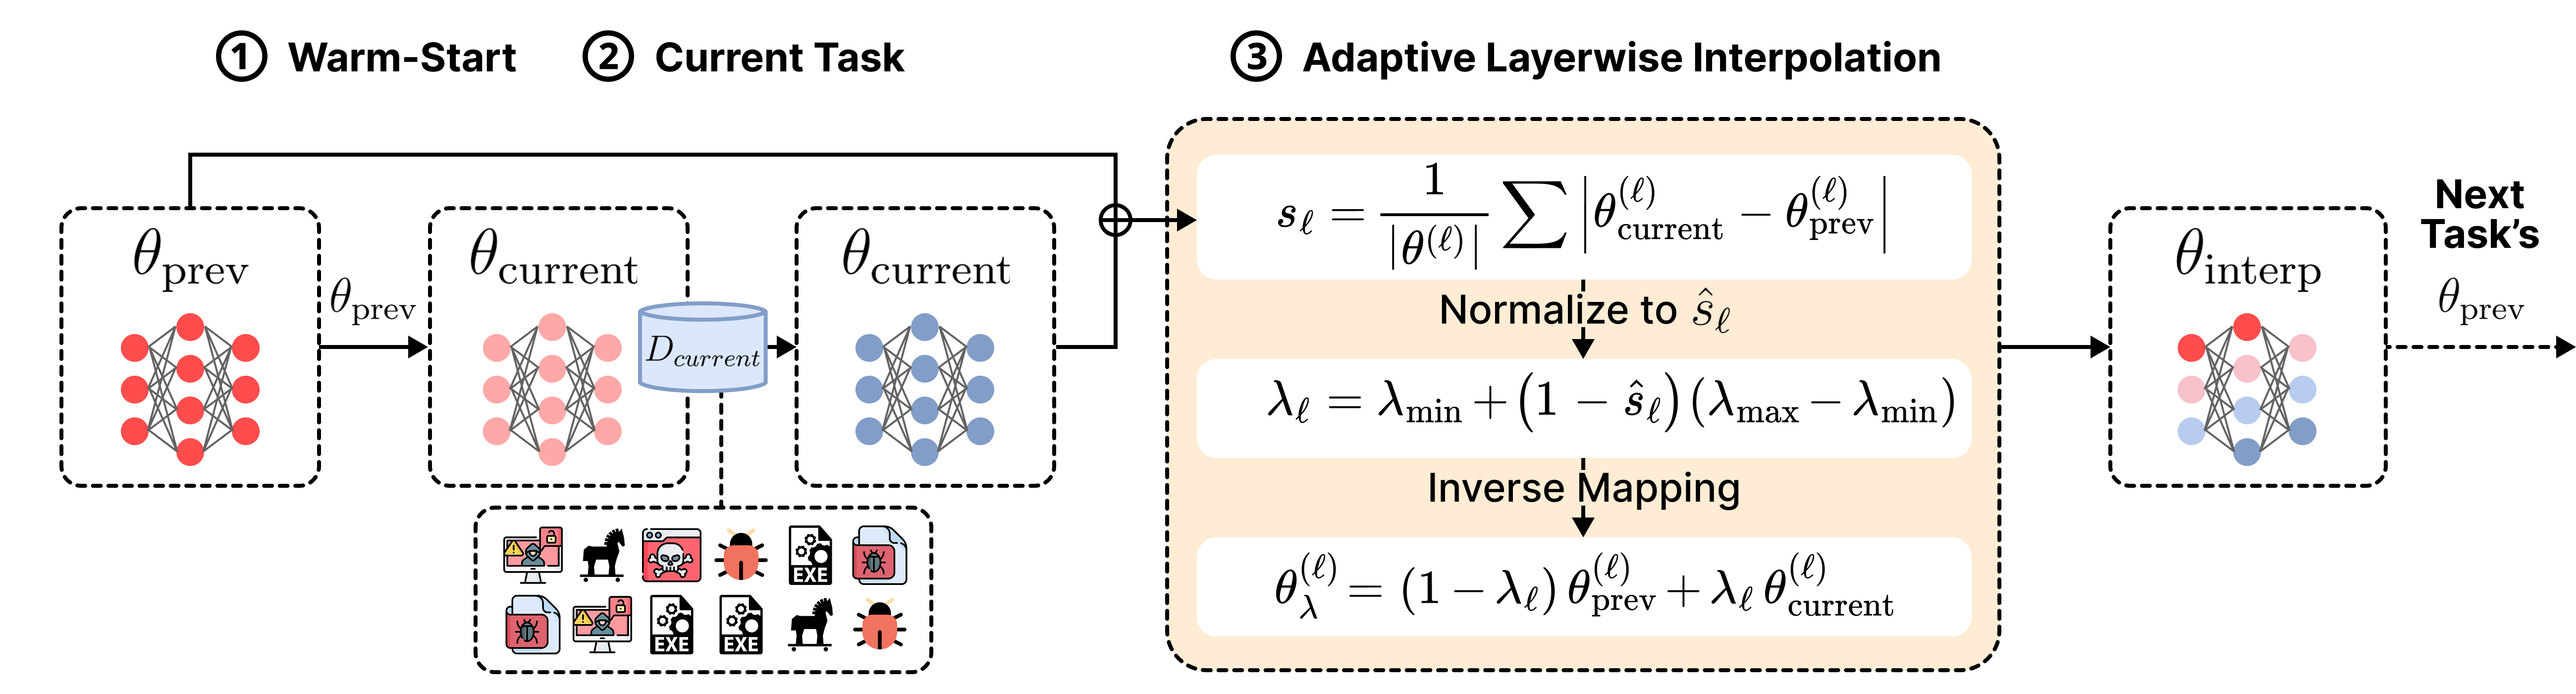 iqsec-lab/freemoca
Memory-free continual learning framework for malware classification using mode connectivity-based interpolation. Supports class-incremental and…
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 volatilityfoundation/volatility3
Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…
 punch-cyber/stoq
An open source framework for enterprise level automated analysis.
 intelbroker/endurance-wiper
a small wiper malware programmed in c#
 volatilityfoundation/volatility
An advanced memory forensics framework
 sensepost/snoopy
Snoopy: A distributed tracking and data interception framework
 cmu-sei/kaiju
CERT Kaiju is a binary analysis framework extension for the Ghidra software reverse engineering suite. This repository is a "mirror" -- please file…
 amavis/amavis
amavis is a high-performance email content filter framework written in Perl.
 splintersfury/autopiff
Semantic analysis engine for detecting vulnerability fixes in Windows kernel driver patches — 58 YAML rules, Ghidra decompilation, reachability…