
operative-framework
 graniet/operative-framework
operative framework is a rust investigation OSINT framework, you can interact with multiple targets, execute multiple modules, create links with…
forensicsinformation-gatheringosint+1
754
graniet/operative-frameworkoperative framework is a rust investigation OSINT framework, you can interact with multiple targets, execute multiple modules, create links with…
 volatilityfoundation/volatility3
Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…
 google/turbinia
Automation and Scaling of Digital Forensics Tools
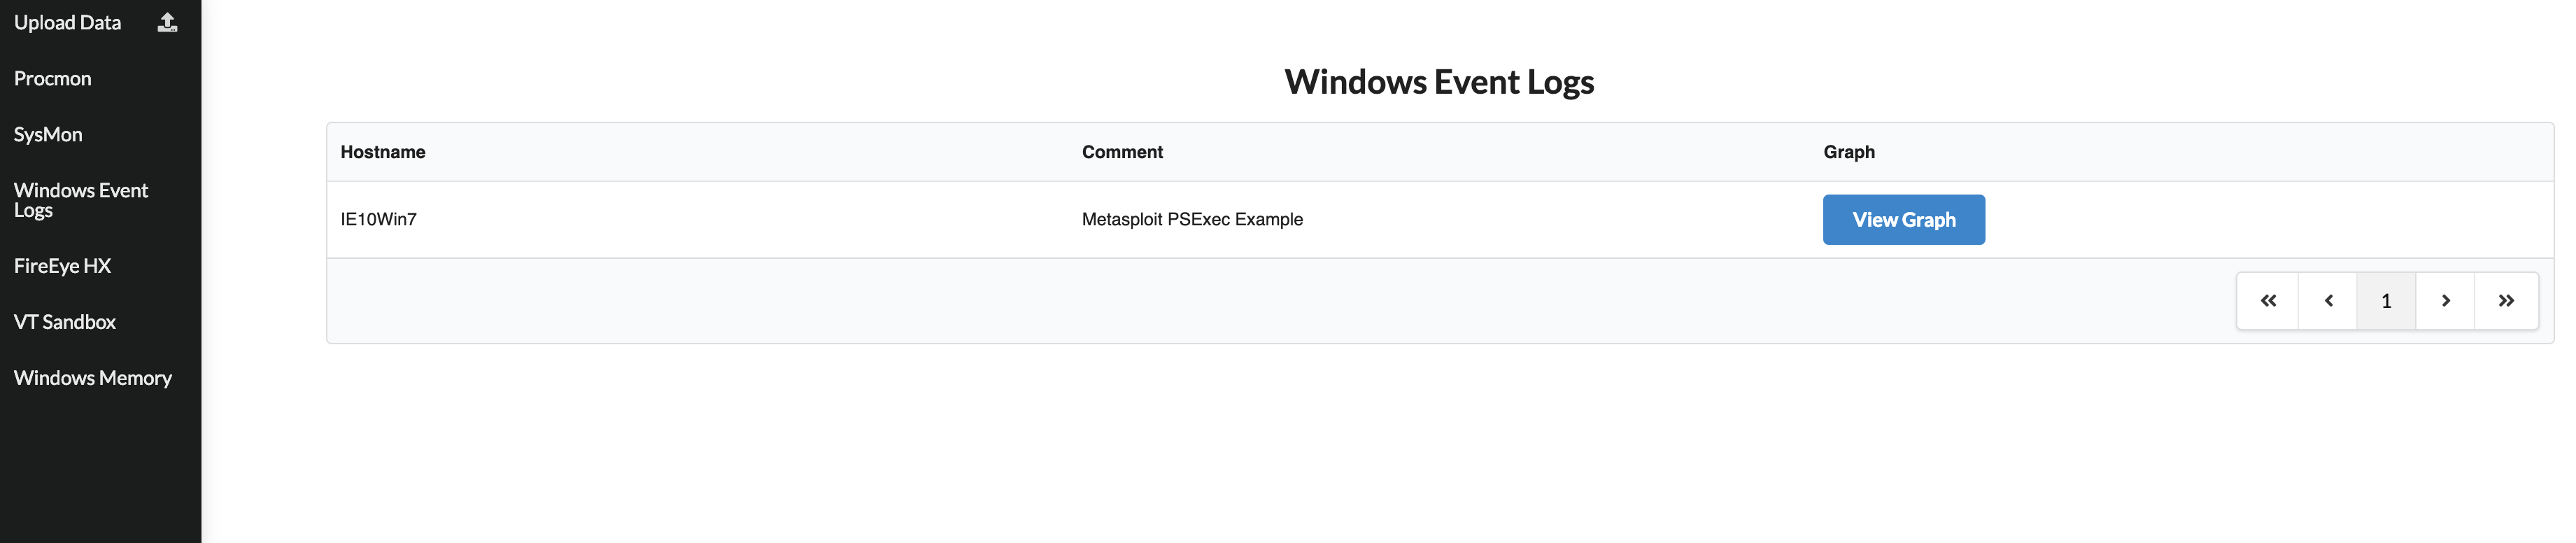 yampelo/beagle
Beagle is an incident response and digital forensics tool which transforms security logs and data into graphs.
 s0md3v/orbit
Blockchain Transactions Investigation Tool
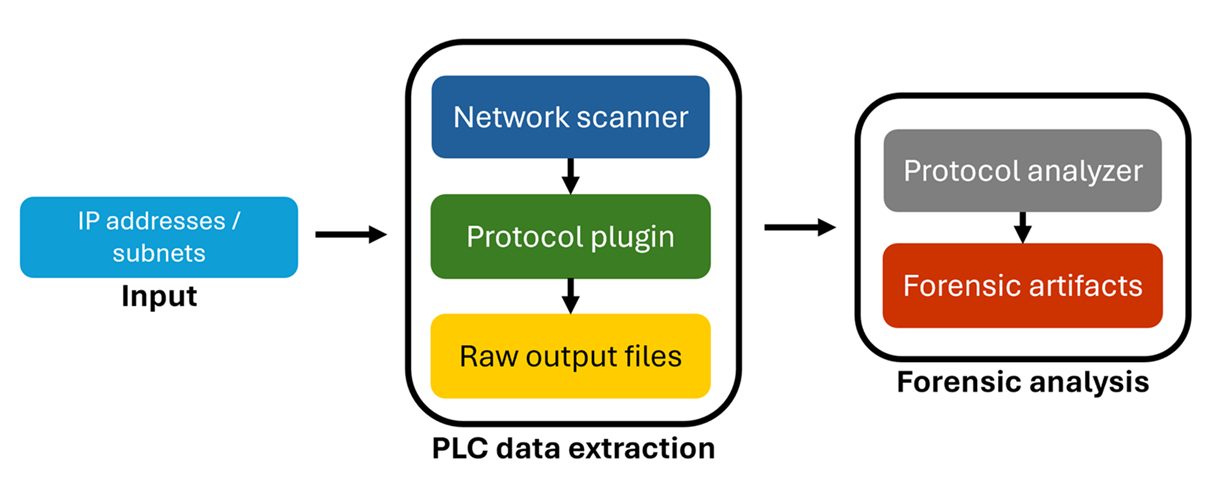 microsoft/ics-forensics-tools
Open-source forensics framework for analyzing Industrial PLC metadata and project files. Scans for suspicious artifacts in ICS environments to…
 travisfoley/dfirtriage
Digital forensic acquisition tool for Windows based incident response.
 redaelli/imago-forensics
Imago is a python tool that extract digital evidences from images.
 clausing/scripts
Collection of Python and Perl scripts for digital forensics, incident response, and network analysis, including hash signature tooling and packet…
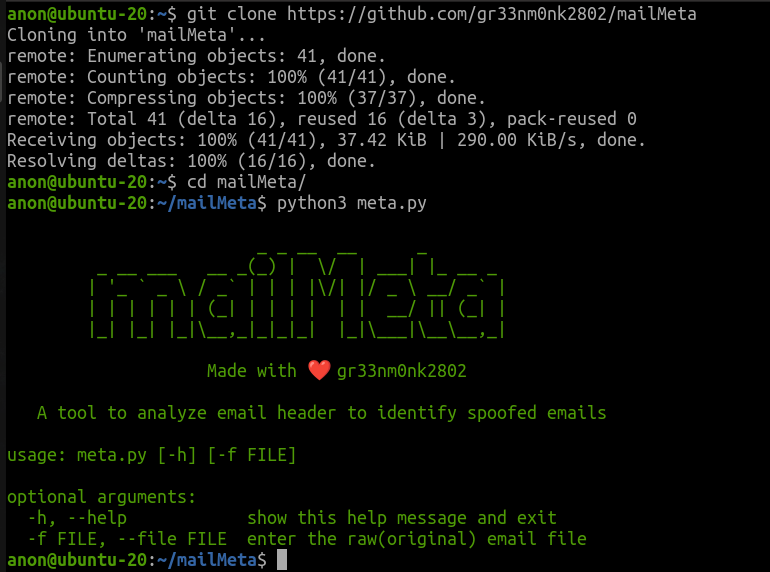 gr33nm0nk2802/mailmeta
An forensics tool to help aid in the investigation of spoofed emails based off the email headers.
 ncsc-nl/citrix-2025
Digital forensics and incident response tool using YARA rules to scan Citrix NetScaler core dumps, disk images, and live hosts for signs of…
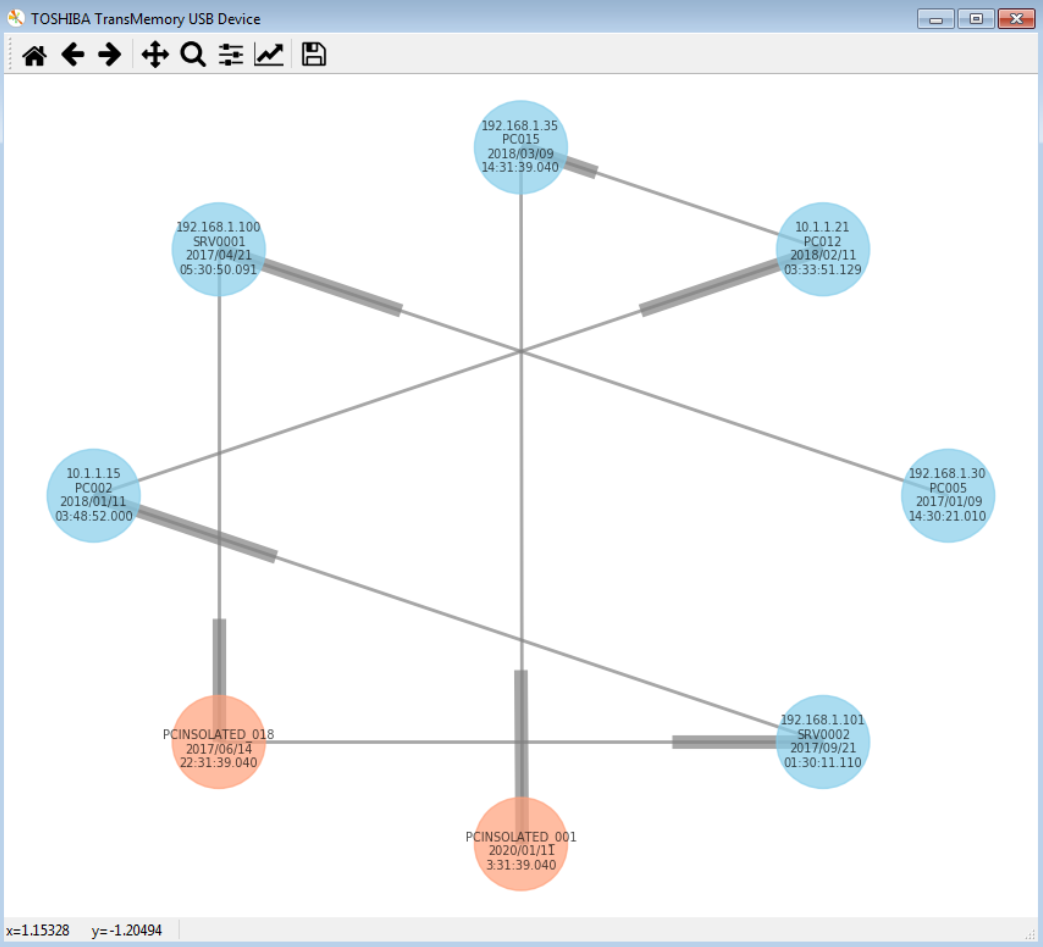 telefonica/hiddennetworks-python
USB device connection forensics tool that traces physical device-to-computer relationships across local and domain networks, generating visual graphs…
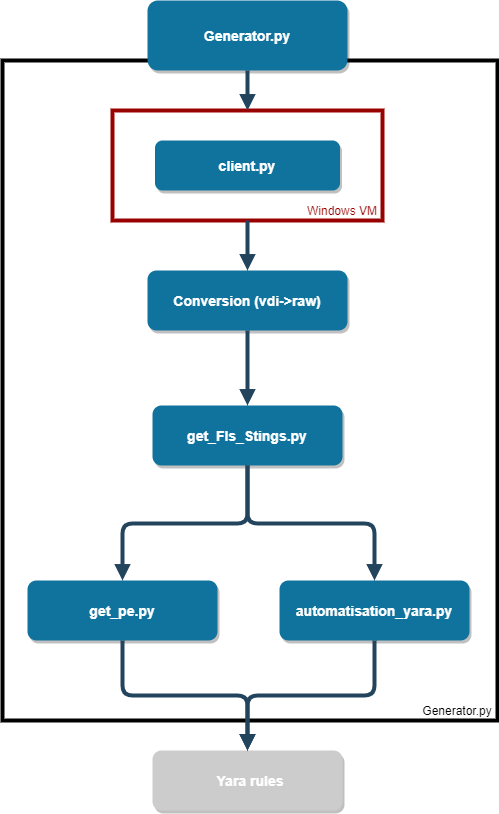 circl/factual-rules-generator
Generates YARA rules from installed software on a running OS to baseline known software and find similar installations across digital forensic…
 slaughterjames/excelpeek
Static analysis tool for investigating potentially malicious Microsoft Excel files, extracting metadata, macros, and embedded objects to aid digital…
 onapsis/cve-2020-6287_recon-scanner
Black-box vulnerability scanner and indicator-of-compromise analyzer for CVE-2020-6287 (RECON) in SAP NetWeaver Java applications, enabling rapid…
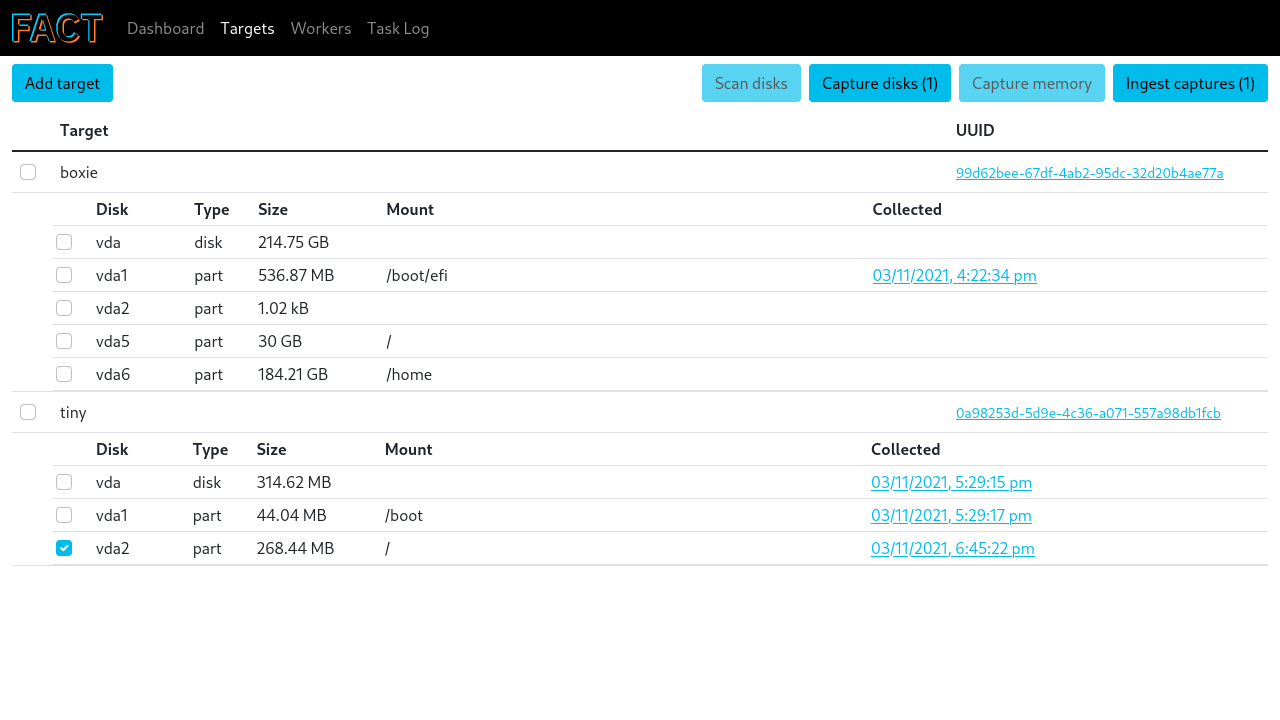 unicornunicode/fact
Collects, processes, and visualizes forensic data from cloud and on-premise machine clusters for incident response and digital investigations.
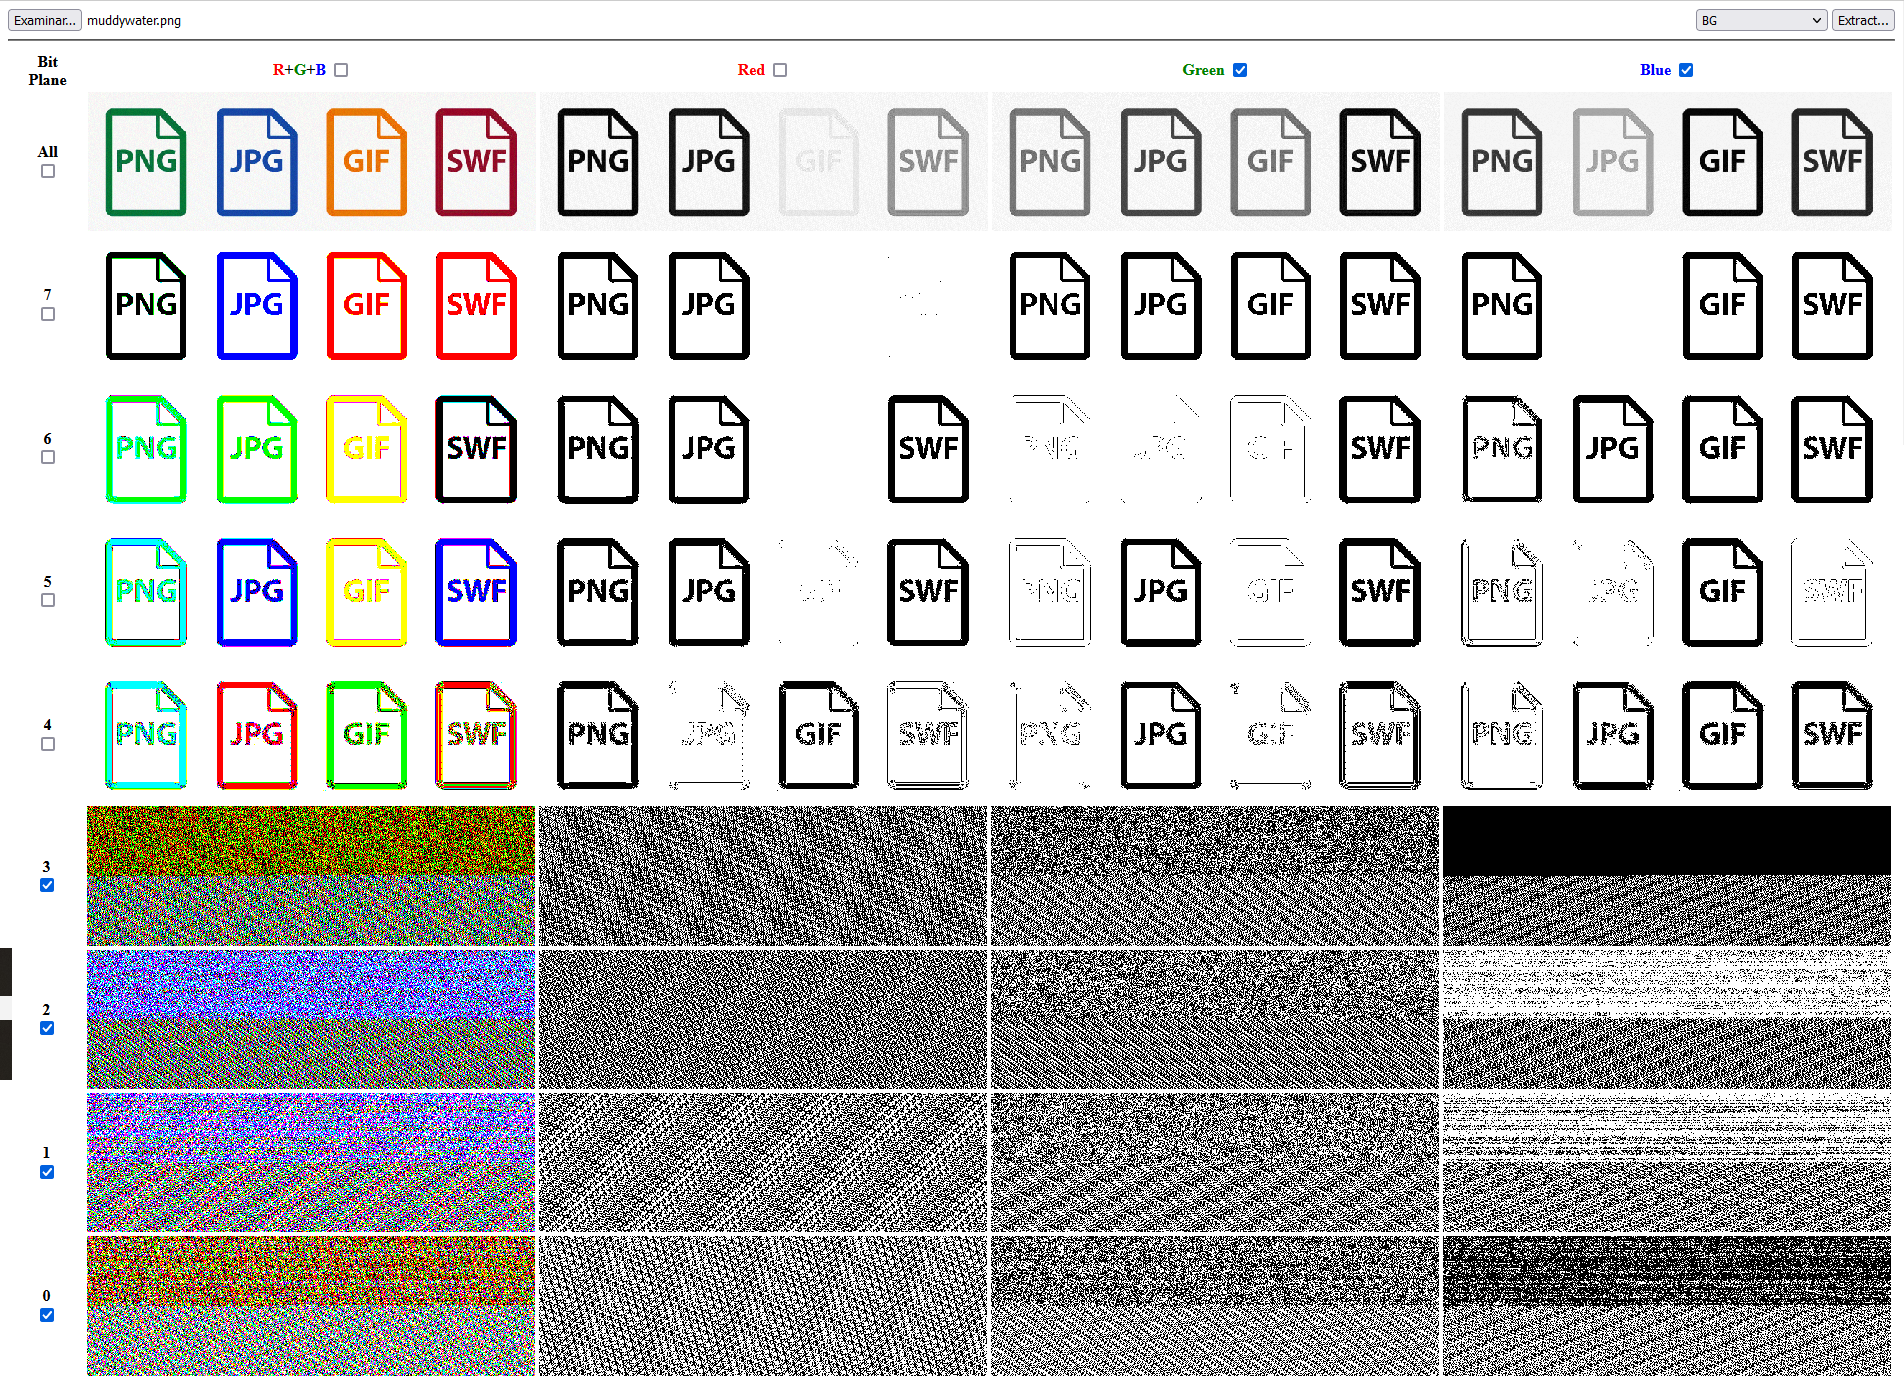 mindcrypt/visual-forensic-steganography
Browser-based tool for visual steganography detection via LSB analysis on digital images, enabling forensic examination and stegomalware…
 benadia/an-integrated-wireless-network-forensic-analysis-framework
This framework combines a set of existing open source tools into an integrated package that automates the forensics investigation process. It is able…